
ADRecon
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
defensive-toolsdigital-forensicsincident-response+6
983
adrecon/adreconPowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
 gianlucaborello/libprocesshider
LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
 malwaretech/edr-preloader
An EDR bypass that prevents EDRs from hooking or loading DLLs into our process by hijacking the AppVerifier layer
 shutdownrepo/dcshadow
Python alternative to Mimikatz lsadump::dcshadow
 yagnikkrish/metasploitable-penetration-testing-lab
Controlled penetration testing lab demonstrating CVE-2011-2523 exploitation and mitigation techniques.
 twosevenonet/edrchoker
A tool uses the QoS Policy (Pacer.sys) to throttle Endpoint Detection and Response (EDR) agents from connecting to the server.
 hlldz/reflexxion
RefleXXion is a utility designed to aid in bypassing user-mode hooks utilised by AV/EPP/EDR etc. In order to bypass the user-mode hooks, it first…
 irsl/php-bypass-disable-functions
Demo project how to bypass the disable_functions security control of PHP on Linux
 pirosap/aquos-r7-ghostlock
Device-specific Linux 5.10 kernel root exploit for Sharp AQUOS R7 (CVE-2026-43499), granting temporary UID 0 with SELinux permissive and an su daemon.
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 mr-un1k0d3r/edrs
Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.
 cisc0-gif/kitt
Python-Based Pentesting Framework
 helviojunior/hookchain
HookChain: A new perspective for Bypassing EDR Solutions
 mouseos/aquos-r6-ghostlock
Temporary root exploit for Sharp AQUOS R6 A101SH S0029 using GhostLock CVE-2026-43499
 bishopfox/sliver
Adversary Emulation Framework
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
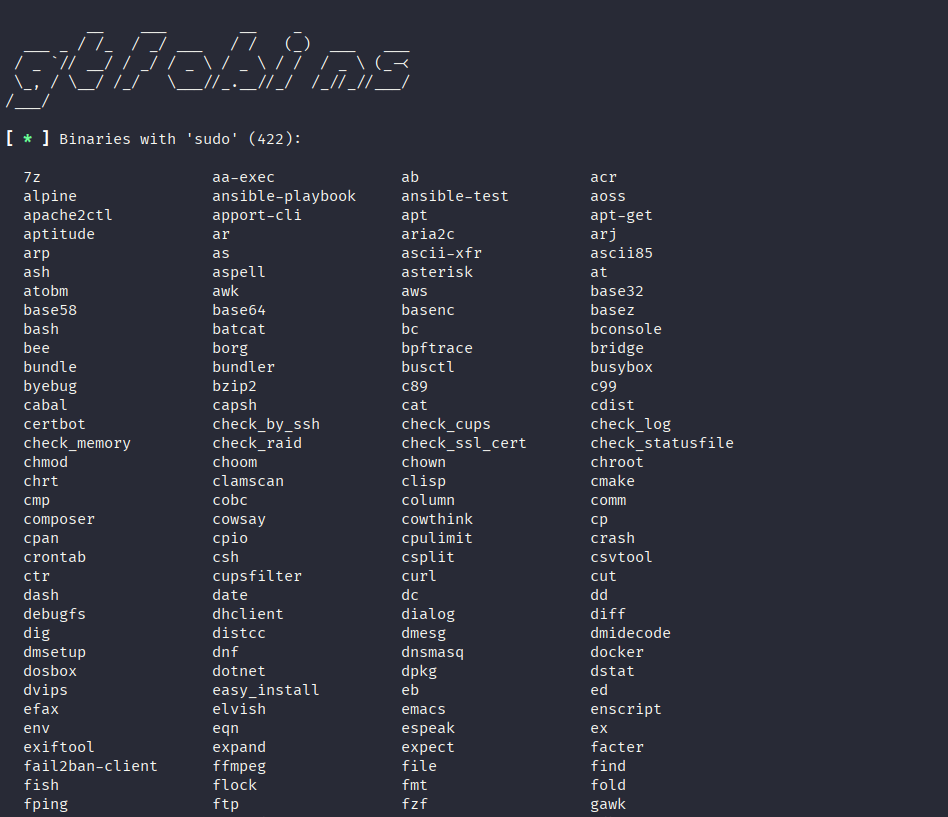 t0thkr1s/gtfobins-cli
Search for Unix binaries that can be exploited to bypass system security restrictions.