offensive-security-adversary-emulation

Simulated a real-world attack (CVE-2011-2523) against a vulnerable host, then cross-checked detection coverage against an existing…

Simulated a real-world attack (CVE-2011-2523) against a vulnerable host, then cross-checked detection coverage against an existing…

Casper@shell:~# is an enhanced, more user-friendly version of p0wny shell with many new features.

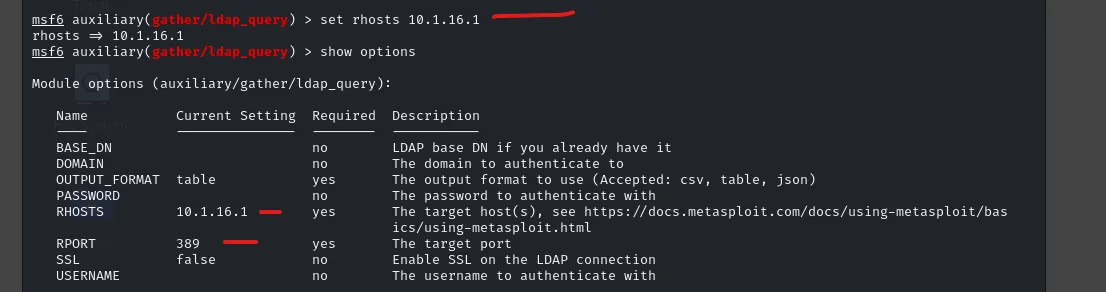
End-to-end Domain Controller exploitation using Metasploit and Impacket: discovered DC10, exploited Zerologon (CVE-2020-1472), extracted NTLM hashes,…

The objective is to conduct a full-scale security assessment of a WordPress-based web application, culminating in a complete server compromise. The…

AI-guided CTF - Break into a real server with Claude Code as your trainer

Comprehensive Penetration Testing report and exploit chain for Metasploitable 2 focusing on CVE-2011-2523.

Full-lifecycle penetration test of a legacy Linux environment (Metasploitable 2) emulated on Apple Silicon. Demonstrating network reconnaissance, RCE…

Utilize metasploit from a Kali Linux machine to exploit a well-known samba vulnerability (CVE-2007-2447). This is done in order to infiltrate a…

Explicação e demonstração da vulnerabilidade ZeroLogon (CVE-2020-1472)

Writeup of the Optimum machine from Hack The Box. This walkthrough covers the exploitation of Rejetto HttpFileServer 2.3 (CVE-2014-6287) to gain…

Audit de sécurité Black Box d'un serveur Drupal 7. Démonstration d'une Kill Chain complète : Injection SQL (CVE-2014-3704) ➔ RCE ➔ Reverse Shell ➔…

A detailed penetration testing walkthrough and exploitation report for the 'Portal' machine, focusing on CVE-2011-2523 (vsFTPd 2.3.4 Backdoor) to…

Walkthroughs for Capture the Flag challenges on the HTB Cybersecurity Platform.

Research Objective: To conduct a comprehensive analysis and successful exploitation of a Remote Code Execution (RCE) vulnerability in Webmin version…

Suite for reverse shell handling geared toward working within the native shell

Collects files and commands post-exploitation, formats them into Markdown reports, and helps find sensitive information for red team reporting.

Linux enumeration script for automated system information gathering to identify potential privilege escalation vectors during penetration testing.