

RendezvousRAT
 rvrsh3ll/rendezvousrat
Self-healing RAT utilizing libp2p
command-and-controlpost-exploitationred-teaming+1
rvrsh3ll/rendezvousratSelf-healing RAT utilizing libp2p
 w4r10ck423/envvisualizer
Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…
 p0dalirius/sharehound
A python tool to map the access rights of network shares into a BloodHound OpenGraphs easily
 blue0x1/nimux
Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…
 zimawhit3/bitmancer
Nim Library for Offensive Security Development
 cerberusmrxi/flowise-cve-2026-58057-exploit
Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…
 ayushx007/cve-2022-0847-dirtypipe-exploits
Collection of exploits and documentation for the Linux Dirty Pipe vulnerability (CVE-2022-0847), enabling arbitrary file overwrite and SUID binary…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 magisterquis/lutlol
Living Under the Land on Linux ~ Bsides Belfast/Vienna 2025
 rek7/ddoor
DDoor - cross platform backdoor using dns txt records
 nicocha30/ligolo-ng
An advanced, yet simple, tunneling/pivoting tool that uses a TUN interface.
 temp43487580/entrapassthecert
tool for requesting Entra ID's P2P certificate and authenticating to a remote Entra joinned devices with it
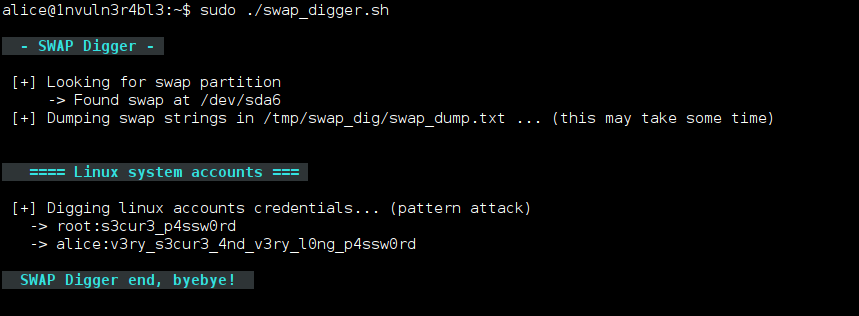 sevagas/swap_digger
Automates Linux swap analysis to extract user credentials, web form data, WiFi keys, and HTTP authentication during post-exploitation or forensic…

 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 ashemery/exploitation-course
Offensive Software Exploitation Course
 luemmelsec/pentest-tools-collection
Curated collection of offensive security tools and commands for Active Directory attacks, C2, privilege escalation, obfuscation, and web pentesting.
 yijiacloud/ghostlock-oppo-pckm00
CVE-2026-43499 GhostLock futex UAF LPE PoC for OPPO PCKM00 (SM6150) / Linux 4.14.180
 jimmypughtron/cve-2026-31431-copy-fail---minified-lpe-poc
CVE-2026-31431-CopyFail---Minified-LPE-PoC