

gopher47
 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.
command-and-controlpenetration-testingport-scanning+4
an00brektn/gopher47A third-party Gopher Assassin for the Havoc Framework.
 tomiwa-ot/telegram-c2
Control a system remotely via telegram
 codextf2/geolocation_bof
Cobalt Strike BOF that retrieves Windows geolocation coordinates via WinRT and legacy ILocation APIs, with automatic registry permission management.
 rootsecdev/secretsstalker
Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…
 keyboard-slayer/e013
VBScript tool that extracts and displays saved Wi-Fi passwords from Windows systems, outputting credentials to a text file for local access.
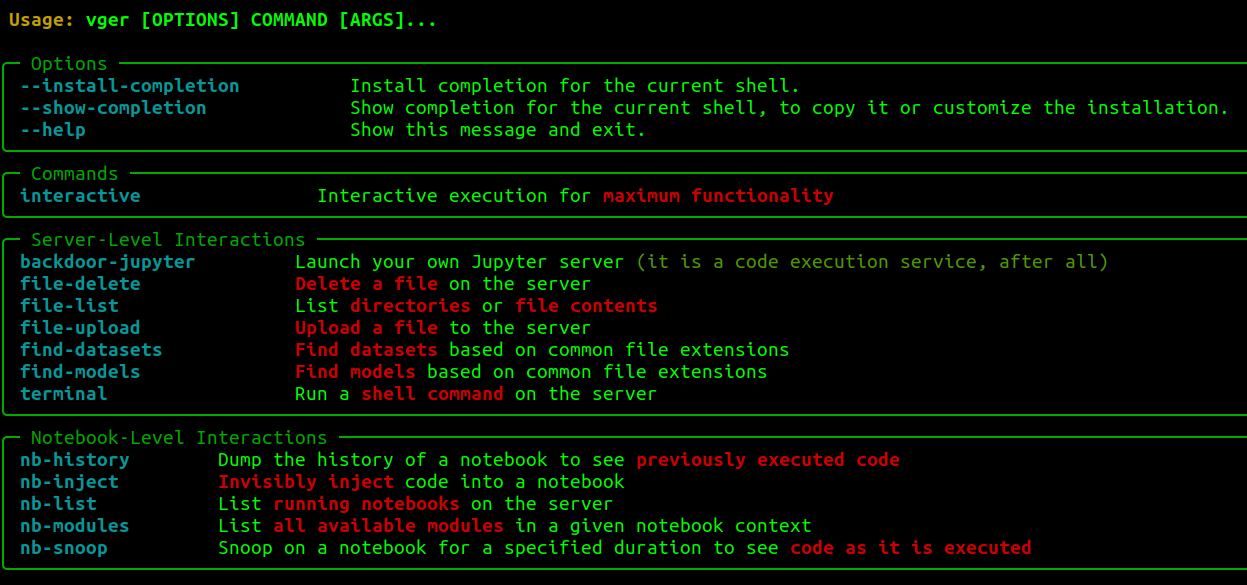 josephtlucas/vger
An interactive CLI application for interacting with authenticated Jupyter instances.
 01rabbit/pakuri-thon
PAKURI-THON is a tool that supports pentesters with various pentesting tools and C4 server (command & control and chat & communication server).…
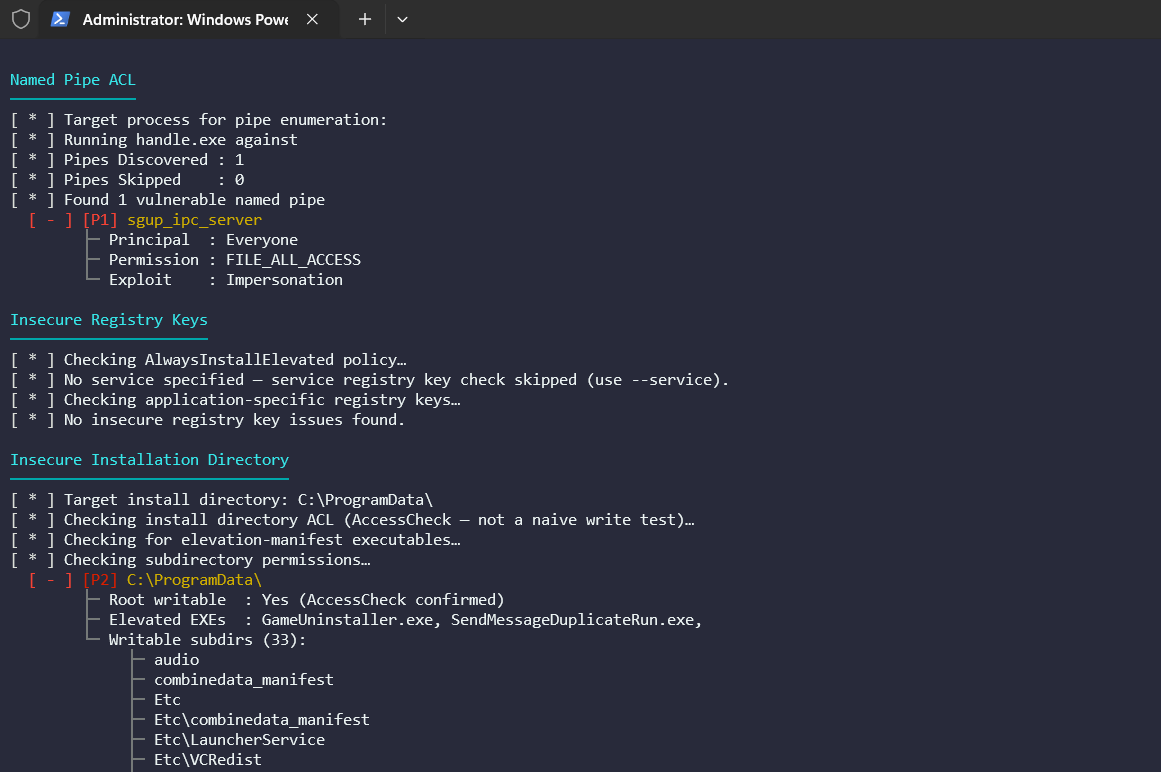 shellkraft/anvil
Anvil is a runtime-first attack surface assessment tool for Windows thick client applications, built for penetration testers and security researchers…
 horizon3ai/cyanide
Automated NTLM relay attack tool combining Responder poisoning with Impacket relay and secretsdump for credential capture, hash relaying, and lateral…
 coldfusion39/vertxploit
Exploiting HID VertX and EDGE access control systems
 preludeorg/cua-kit
Tools for attacking Computer Use Agents
 maldevel/dicerosbicornis
A fully featured Windows backdoor that uses email as a C&C server
 stra-x/outoftune
Rogue device enrollment tool for Entra ID and Intune MDM. Automates device join, token acquisition, MDM enrollment, and OMA-DM checkin to extract…
 dru1d-foofus/getlapspassword
A LAPS dumper written using the impacket library.
 al1ex/pentest-command
Pentest-Command
 behzadmagzer/auto-postxploit
Windows Auto Post Exploitation - For ReD Team