
CVE-2026-5027-Langflow
 layer-6/cve-2026-5027-langflow
Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
command-and-controlexploitationpayload-development+8
layer-6/cve-2026-5027-langflowMulti-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
 gagaltotal/cve-2026-48908-sp-page-builder-joomla
CVE-2026-48908 - SP Page Builder Joomla Unauthenticated RCE

 nu11secur1ty/0
Exploit for a Windows Defender race condition that escalates to SYSTEM via use-after-free, crashes MsMpEng.exe, spawns a hidden shell, and persists…
 gmh5225/cs-dropspawn_bof
CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking
 lierbushiwo/rasa-cve-exp
CVE-2024-49375、CVE-2021-42556、CVE-2021-41127
 al1ex/powershell-c2
Powershell-C2
 0xgunrunner/cve-2024-26229-bof
CVE-2024-26229 Beacon Object File version
 kagantua/pintheft-go
A Go implementation of PinTheft (CVE-2026-43494)
 epsilonpoint88-glitch/epsilonpoint-
Modular exploit framework targeting CVE-2026-23550 in WordPress, featuring mass exploitation, obfuscation, post-exploitation, and Docker-based C2…
 1872892142/jboss-autopwn-1
JBoss Autopwn as featured at BlackHat Europe 2010 - this version incorporates CVE-2010-0738 the JBoss authentication bypass VERB manipulation…
 newcomrade12211/cve-2025-56383
DLL hijacking to rev shell
 gitcollect/jboss-autopwn
Automated JBoss exploitation script deploying JSP shells with bind/reverse shell, Meterpreter, and VNC support for penetration testing.
 h3x0v3rl0rd/nim-reverse-shell
nim-reverse-shell
 thejoyofhacking/dirkjanm-cve-2020-1472
Exploit for CVE-2020-1472 (Zerologon) that resets the domain controller account password, enabling DCSync, with restoration steps to revert changes.
 cyglegit/cve-2025-24813
Automated exploitation toolkit for CVE-2025-24813 targeting Apache Tomcat insecure session deserialization. Features multi-target scanning, gadget…
 bgutowski/cve-2025-4517-poc-sudoers
Exploit for CVE-2024-6232 - Python Tarfile Realpath Overflow
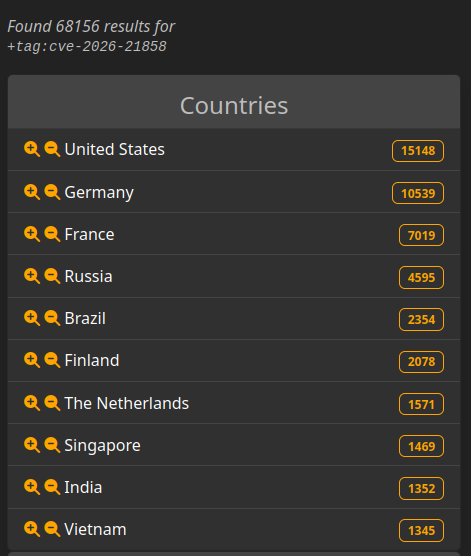 alhakim88/cve-2026-21858
Automated exploit chain for n8n combining arbitrary file read, admin token forgery, and sandbox bypass to achieve unauthenticated remote code…