
Archived
Modules
 havocframework/modules
Modules used by the Havoc Framework
authenticationcommand-and-controlinformation-gathering+5
havocframework/modulesModules used by the Havoc Framework
 mitre/caldera-crater
C# remote access trojan (RAT) implant for the Caldera adversary emulation framework, enabling post-exploitation command and control on Windows…
 optiv/ivy
Ivy is a payload creation framework for the execution of arbitrary VBA (macro) source code directly in memory. Ivy’s loader does this by utilizing…
 dobin/antnium
A C2 framework for initial access in Go
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 zux0x3a/0xsp-mongoose
a unique framework for cybersecurity simulation and red teaming operations, windows auditing for newer vulnerabilities, misconfigurations and…
 praetorian-inc/pentestly
Python and Powershell internal penetration testing framework
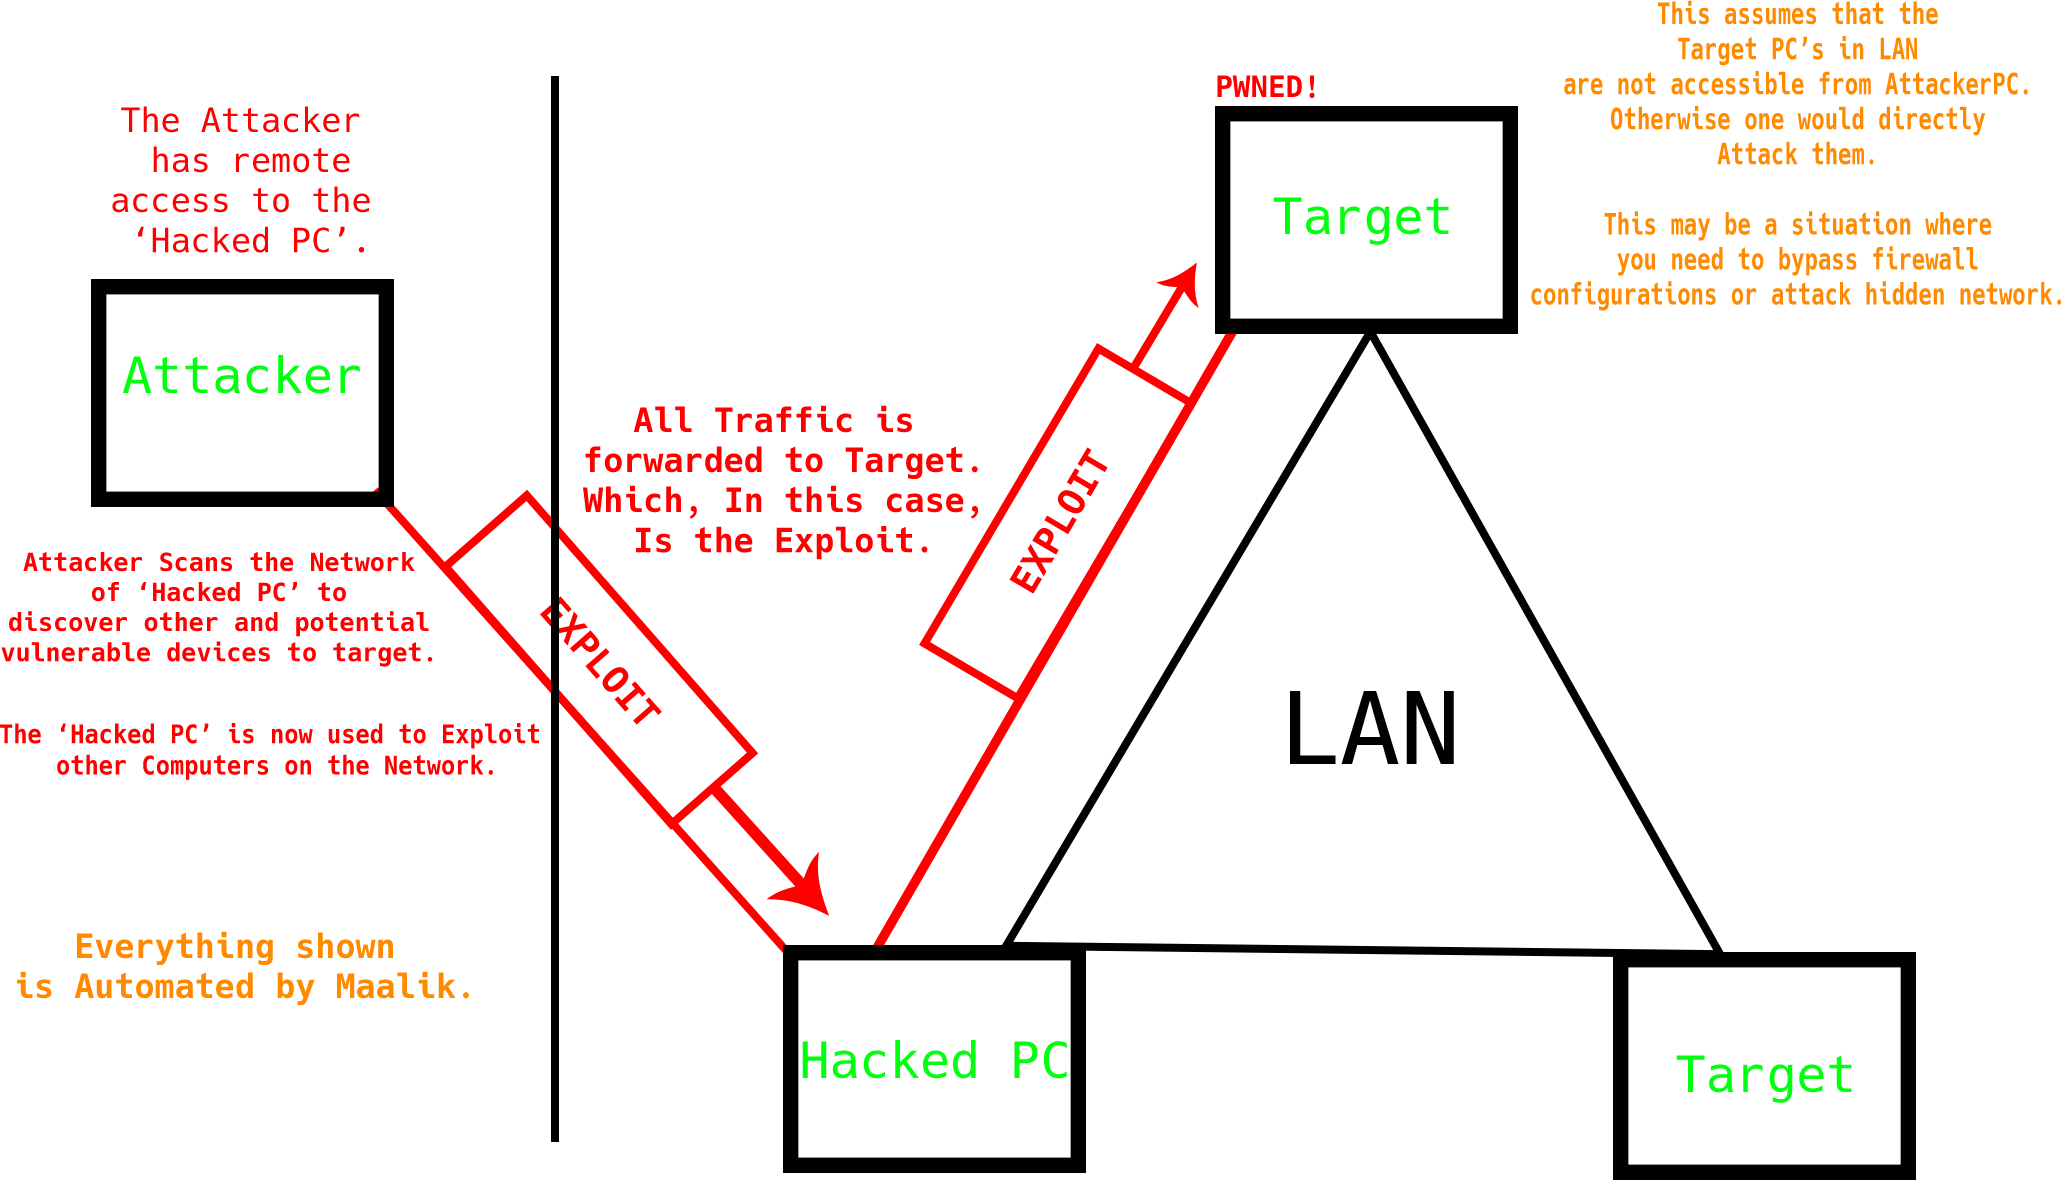 quantumcore/maalik
Feature-rich Post Exploitation Framework with Network Pivoting capabilities.
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
 aegrah/panix
Customizable Linux Persistence Tool for Security Research and Detection Engineering.
 lepotekil/msfmania
Python AV Evasion Tools
 mr-in4inci3le/sliver-gui
A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
 mncoppola/rpef
Abstracts and expedites the process of backdooring stock firmware images for consumer/SOHO routers

 mr-wolf-gb/d-rat_vb.net_mysql_php
D-RAT [VB.NET]+[MySQL]+[PHP]
 sobri3195/-pegasus-suite
A comprehensive security toolkit with 1000+ penetration testing and security assessment tools.
 hackersatyamrastogi/n8n-exploit-cve-2025-68613-n8n-god-mode-ultimate
n8n God Mode Ultimate - CVE-2025-68613 Scanner v1.0.0 ║ ║ Workflow Automation Remote Code Execution