
CVE-2010-2075
 rushikesh-a-bhujbal/cve-2010-2075
UnrealIRCd 3.2.8.1 backdoor exploit — reverse shell via AB; trigger, built from scratch in Python using raw sockets. No Metasploit.
educationexploitationlabs-practice+7
rushikesh-a-bhujbal/cve-2010-2075UnrealIRCd 3.2.8.1 backdoor exploit — reverse shell via AB; trigger, built from scratch in Python using raw sockets. No Metasploit.
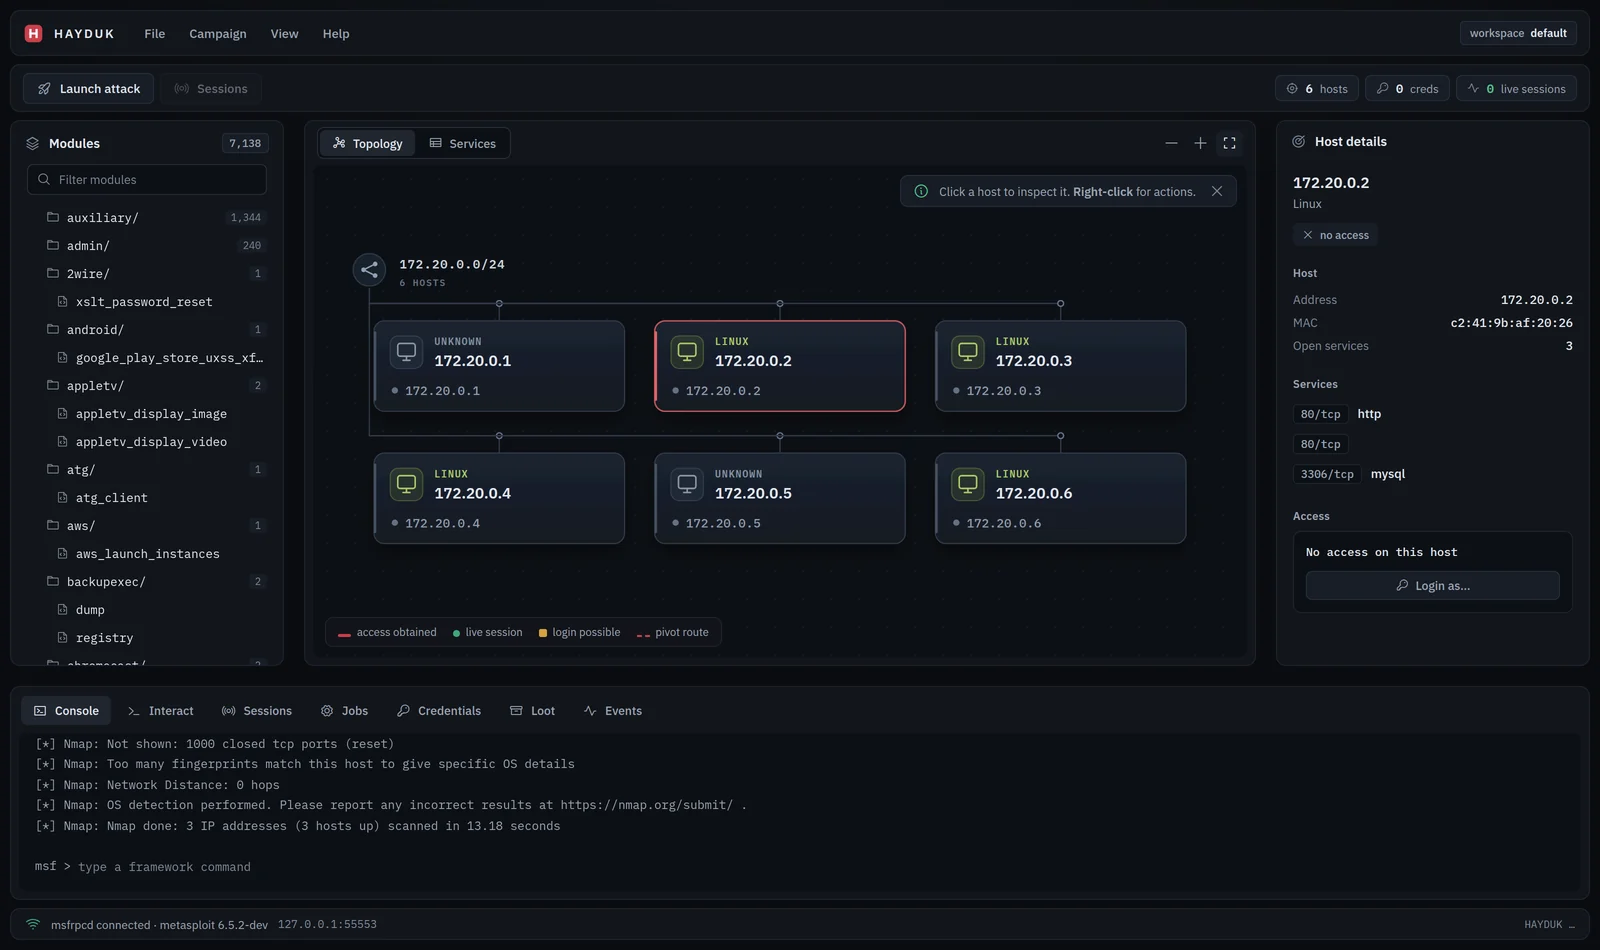 jolovicdev/hayduk
Graphical attack management console for Metasploit: the lineage of Armitage as a single Go binary with a browser UI. Live network topology, campaign…
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
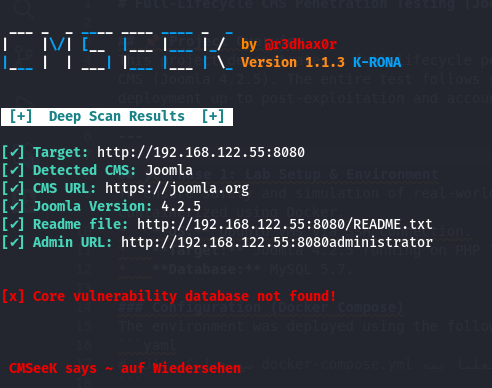 marwan651/joomla-cms-full-lifecycle-pentest
A comprehensive full-lifecycle penetration testing project on Joomla 4.2.5 exploiting CVE-2023-23752 inside a Dockerized lab environment
 infosecn1nja/red-teaming-toolkit
This repository contains cutting-edge open-source security tools (OST) for a red teamer and threat hunter.
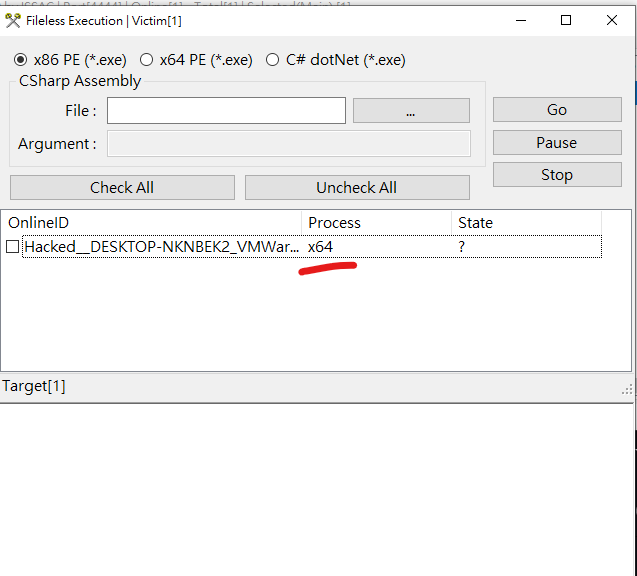 iss4cf0ng/duplexspycs
An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…
 tennc/webshell
This is a webshell open source project
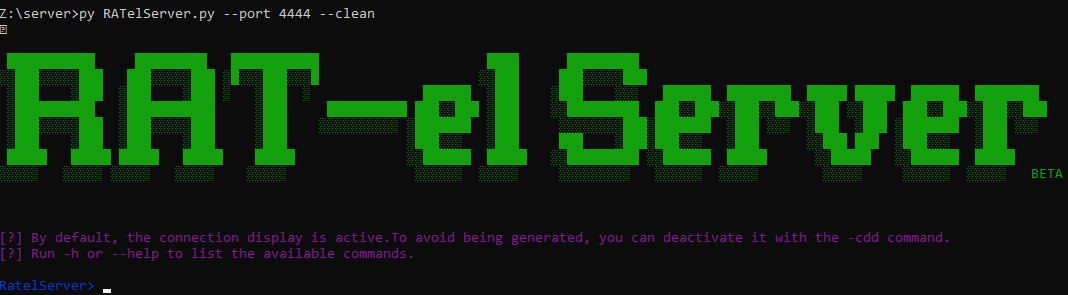 frenchcisco/ratel
RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
 alphaseclab/awesome-rat
RAT And C&C Resources. 250+ Open Source Projects, 1200+ RAT/C&C blog/video.
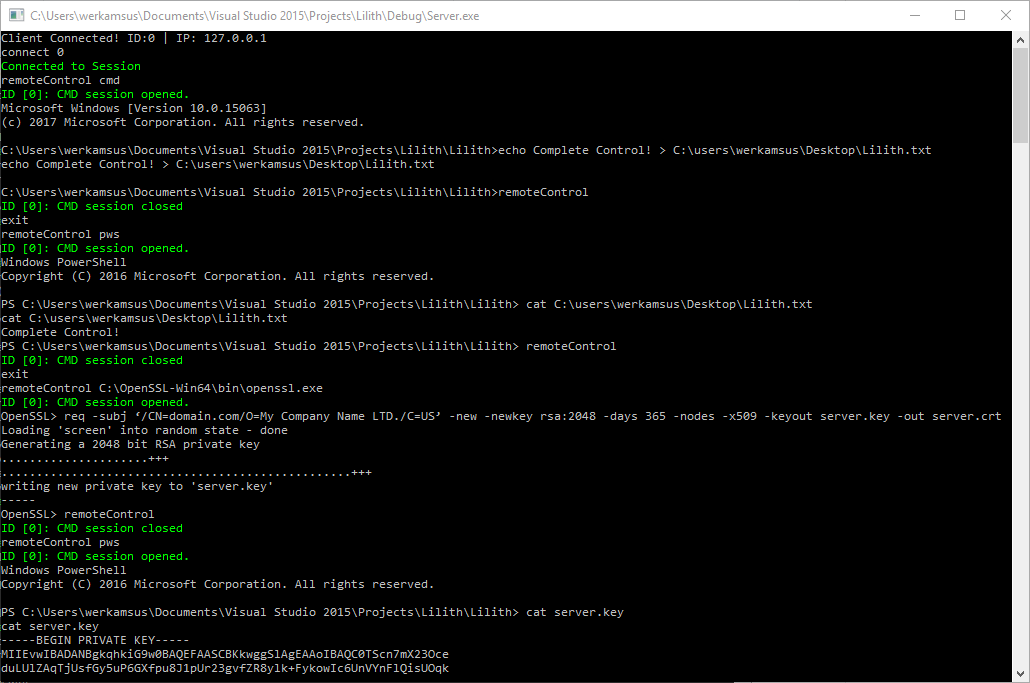 werkamsus/lilith
Lilith - Foundational reverse engineering resource for cybersecurity entrepreneurs in C++