
lsassy
 login-securite/lsassy
Extract credentials from lsass remotely
information-gatheringpenetration-testingpost-exploitation+1
login-securite/lsassyExtract credentials from lsass remotely
 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 twosevenonet/edrchoker
A tool uses the QoS Policy (Pacer.sys) to throttle Endpoint Detection and Response (EDR) agents from connecting to the server.
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
 safebreach-labs/poolparty
A set of fully-undetectable process injection techniques abusing Windows Thread Pools
 matthieu-hackwitharts/win32_offensive_cheatsheet
Win32 and Kernel abusing techniques for pentesters
 mwr-cybersec/pxethief
PXEThief is a set of tooling that can extract passwords from the Operating System Deployment functionality in Microsoft Endpoint Configuration Manager
 thomasareed/pict
Modular incident response toolkit for collecting forensic data from potentially infected macOS endpoints, capturing browser artifacts, persistence…
 dr4g0n23/cve-2020-1472
Exploit script for CVE-2020-1472 (ZeroLogon) with automated privilege escalation, credential dumping via secretsdump, and lateral movement using…
 rad9800/tamperingsyscalls
C++ library that retrieves and spoofs Windows syscall arguments using hardware breakpoints and exception handlers to subvert EDR telemetry.
 t43wiu6/cve-2019-0887
exp for CVE-2019-0887
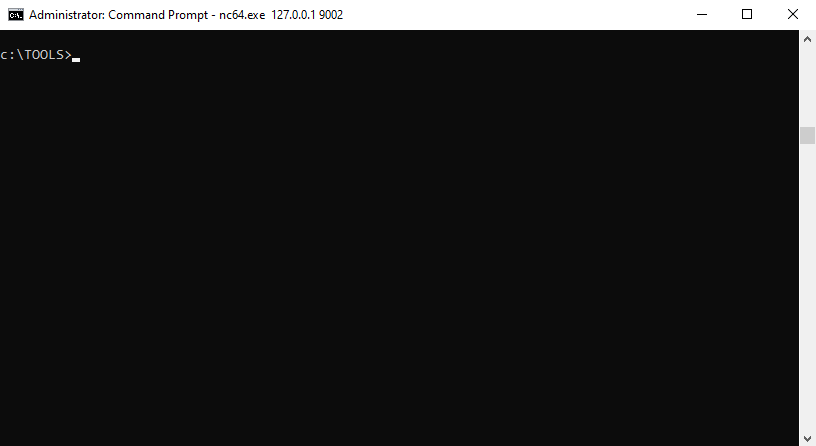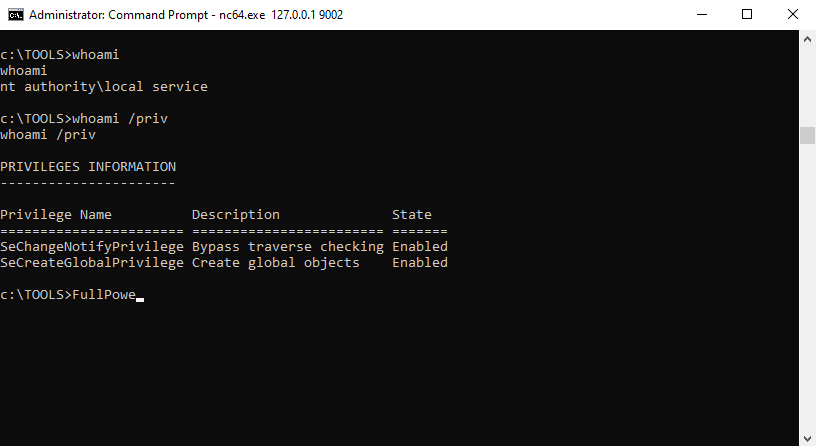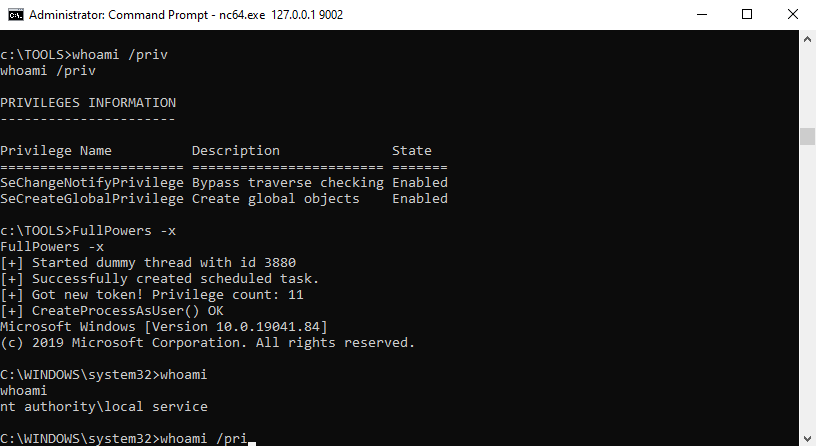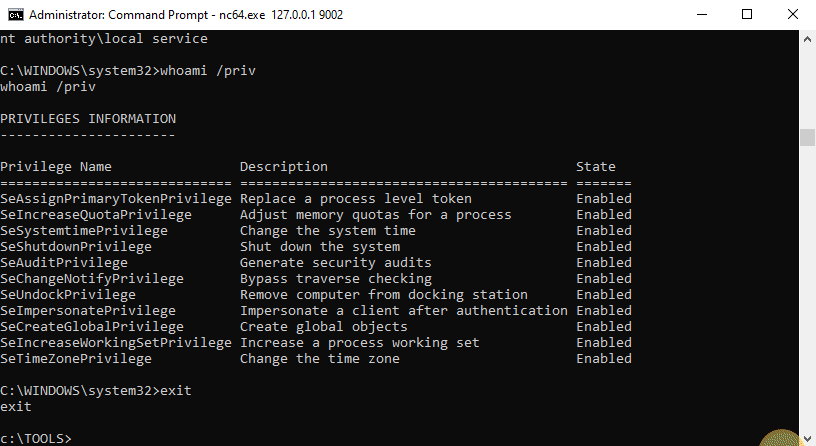 itm4n/fullpowers
Recover the default privilege set of a LOCAL/NETWORK SERVICE account
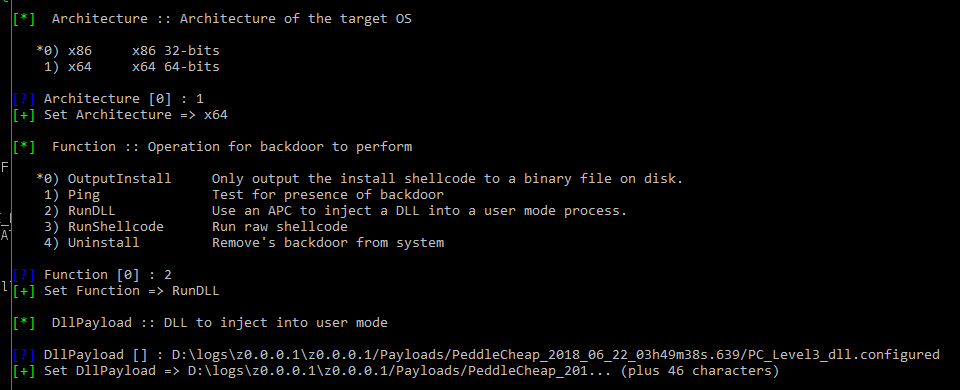 francisck/danderspritz_lab
A fully functional DanderSpritz lab in 2 commands