Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
15 results
VMkatz preview

VMkatz

GitHubnikaiw/vmkatz

Extract Windows credentials directly from VM memory snapshots and virtual disks
digital-forensicsexploitationforensics+7
1.6k1 day ago
Credential-Hunting preview

Credential-Hunting

GitHubnecr00/credential-hunting

CredsHunter - Credential Hunting scripts for Windows and Linux OS
forensicsincident-responseinformation-gathering+7
1892 months ago
LogHound preview

LogHound

GitHubrnb-team/loghound

Post-Exploitation EVTX Analyzer for BloodHound Mapping
authenticationdigital-forensicsforensics+6
155 months ago
syd preview

syd

GitHubsydsec/syd

Offline AI Security Assistant for Air-Gapped Pentesting
ai-securityexploitationforensics+8
876 months ago
FarsightAD preview

FarsightAD

GitHubqazeer/farsightad

PowerShell script that aim to help uncovering (eventual) persistence mechanisms deployed by a threat actor following an Active Directory domain…

forensicsincident-responseinformation-gathering+5
989 months ago
DeadMatter preview

DeadMatter

GitHubqsecure-labs/deadmatter

Offset Independent Credential Extraction Tool
data-recoverydigital-forensicsforensics+7
711 year ago
HiddenDesktop preview

HiddenDesktop

GitHubmalwaretech/hiddendesktop

Create and enumerate hidden desktops.
defensive-toolsforensicsincident-response+3
942 years ago
MrKaplan preview

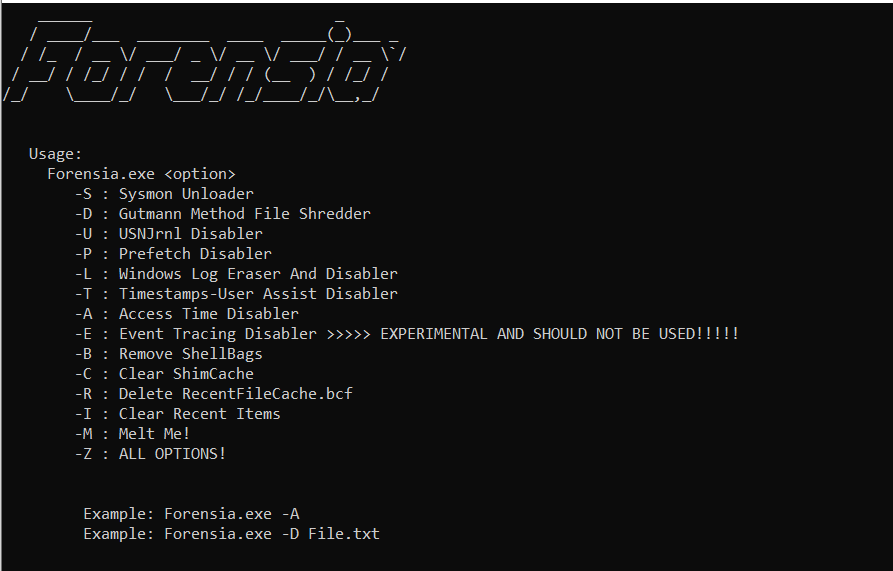
MrKaplan

GitHubidov31/mrkaplan

PowerShell tool for red teamers that clears execution evidence by stopping event logging, removing file and registry artifacts, and saving timestamps…
defensive-toolsforensicsids-ips-evasion+3
2763 years ago
Forensia preview

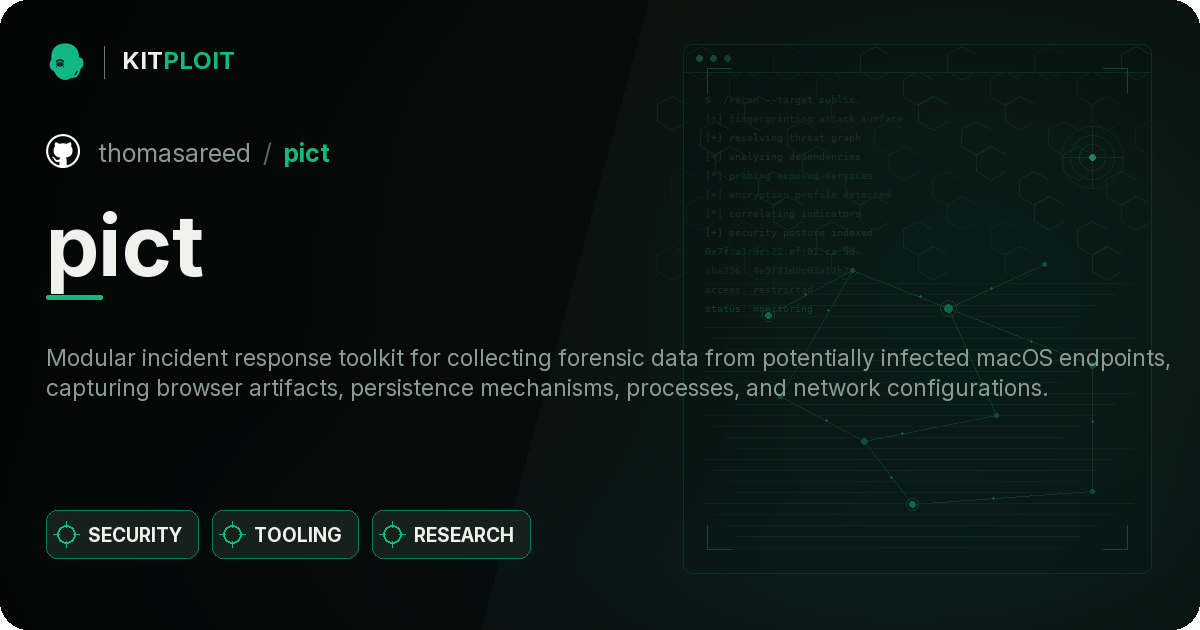
Forensia

GitHubpaulnorman01/forensia

Anti Forensics Tool For Red Teamers, Used For Erasing Footprints In The Post Exploitation Phase.
defensive-toolsforensicspost-exploitation+1
7903 years ago
pict preview

pict

GitHubthomasareed/pict

Modular incident response toolkit for collecting forensic data from potentially infected macOS endpoints, capturing browser artifacts, persistence…
digital-forensicsforensicsincident-response+2
963 years ago
moonwalk preview

moonwalk

GitHubmufeedvh/moonwalk

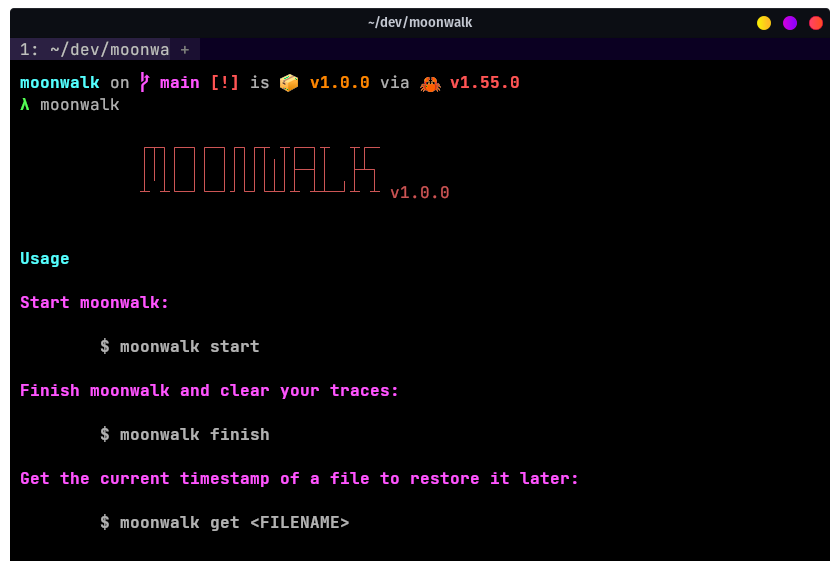
Cover your tracks during Linux Exploitation by leaving zero traces on system logs and filesystem timestamps.
forensicspenetration-testingpost-exploitation+2
1.5k4 years ago
Network-Filesystem-Forensics preview

Network-Filesystem-Forensics

GitHubgilberto47831/network-filesystem-forensics

Reports on post-exploitation on honeypot exploiting vulnerable wu-ftpd (CVE-2001-0550)
digital-forensicsforensicsnetwork-forensics+2
4 years ago
RDPLinkEnum preview

RDPLinkEnum

GitHubal1ex/rdplinkenum

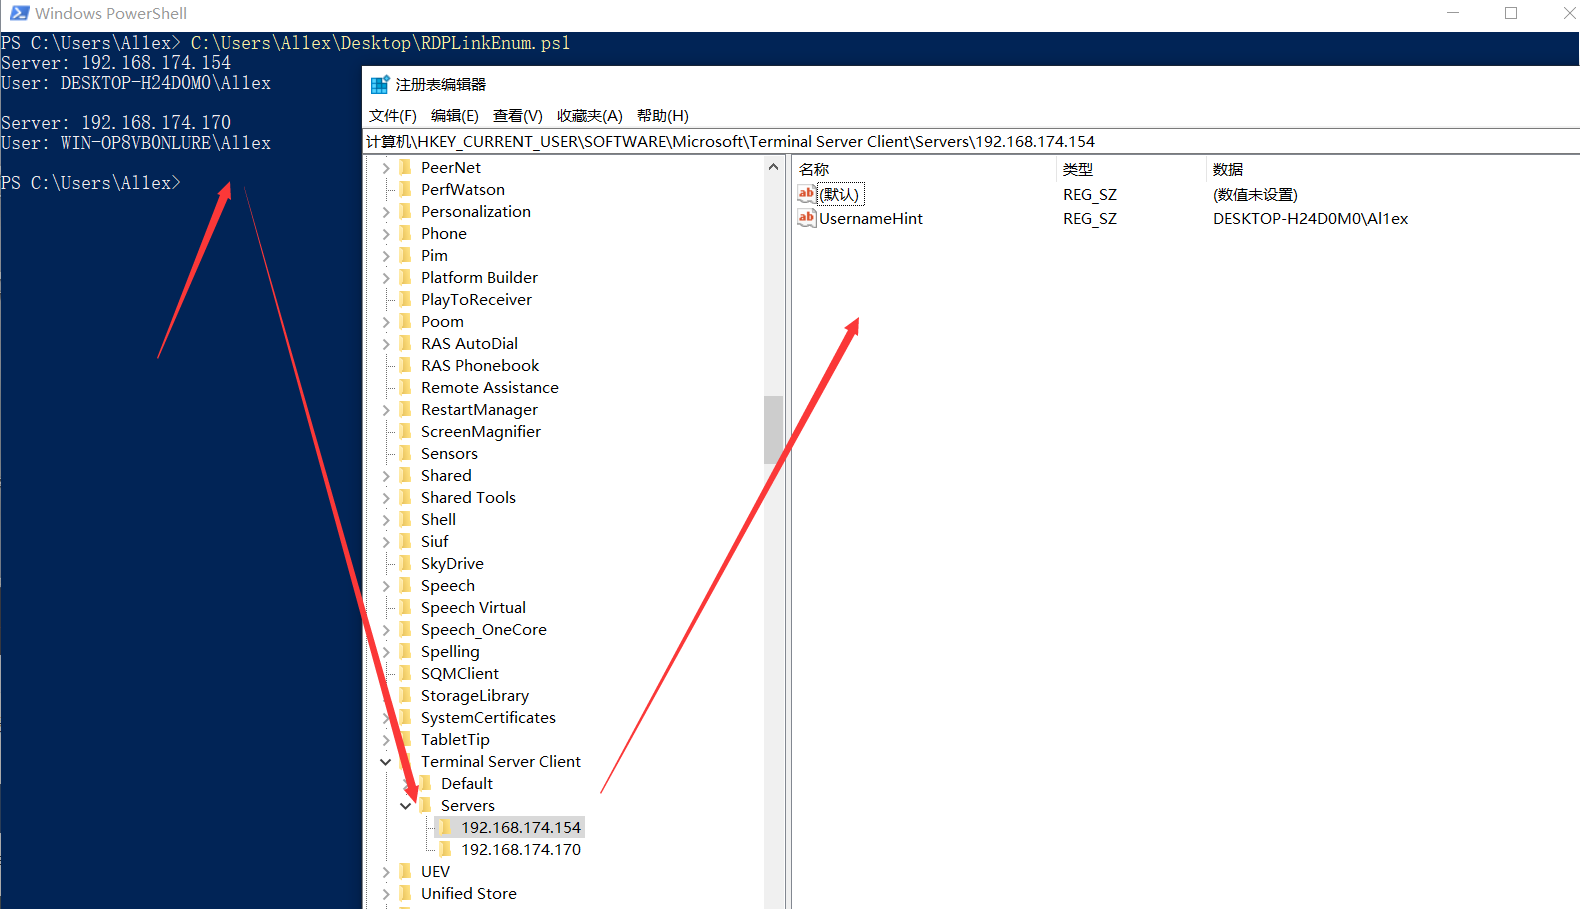
RDPLinkEnum

digital-forensicsforensicsincident-response+3
55 years ago
swap_digger preview

swap_digger

GitHubsevagas/swap_digger

Automates Linux swap analysis to extract user credentials, web form data, WiFi keys, and HTTP authentication during post-exploitation or forensic…
digital-forensicsforensicsinformation-gathering+2
5355 years ago
NorkNork preview

NorkNork

GitHubn00py/norknork

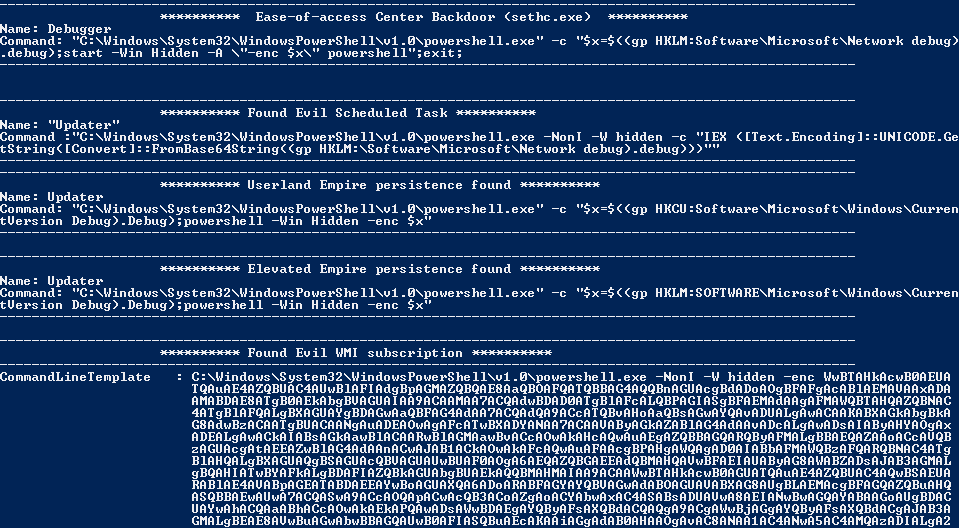
Powershell Empire Persistence finder

defensive-toolsforensicsincident-response+2
1189 years ago