

Lab-RATS-v1.6
 k4n3co/lab-rats-v1.6
Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
android-securitycommand-and-controldata-exfiltration+8
80
k4n3co/lab-rats-v1.6Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
 gentilkiwi/mimikatz
A little tool to play with Windows security
 inguardians/peirates
Peirates - Kubernetes Penetration Testing tool
 garrettfoster13/sccmhunter
Post-exploitation tool for identifying, profiling, and attacking Microsoft SCCM assets within Active Directory domains, streamlining credential…
 61106960/adpeas
Powershell tool to automate Active Directory enumeration.
 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
 tracyliving606/regpwn
Exploit Windows local privilege escalation on clients and servers using tested code for CVE-2026-24291 across multiple Windows versions
 tc4dy/cve-2026-6875-poc-exploit
CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…
 nikopmpm/fsociety-cve-2024-0670-checkmk-lpe
🔍 Exploit CVE-2024-0670 in CheckMK agents for local privilege escalation using a robust C++ tool designed for security professionals.
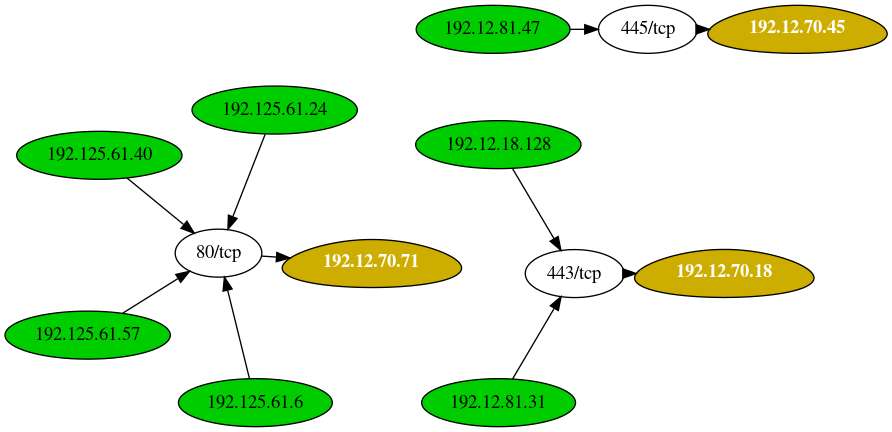 vonahisec/leprechaun
This tool is used to map out the network data flow to help penetration testers identify potentially valuable targets.
 hitechcloud-vietnam/cve-2026-41940-poc
Exploits CVE-2026-41940, a cPanel & WHM authentication bypass, to gain root WHM access and run post-exploitation commands, file reads, and account…
 mayyhem/sharpsccm
C# post-exploitation tool for abusing Microsoft Configuration Manager (SCCM) to perform lateral movement, credential gathering, and NTLM…
 a2333c/dfroot
Android root tool for Samsung Galaxy S25 Ultra (SM-S938B) that chains DirtyFrag CVE-2026-43284 and CVE-2026-43499 to gain root automatically at boot…
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
 trustedsec/cs-remote-ops-bof
Remote operations commands implemented using Beacon Object Files
 davidcarliez/mythic_telegram_profile
Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…
 rurixis/msrkit
A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
 darabium/couchdb-exploit
Exploits CouchDB CVE-2017-12635/12636 for privilege escalation and RCE, then provides an interactive shell with command execution, database browsing,…