

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
44 results
redamon preview

redamon

GitHubsamugit83/redamon

An AI-powered agentic red team framework that automates offensive security operations, from reconnaissance to exploitation to post-exploitation, with…
ai-securityexploit-frameworkslateral-movement+8
2.6k
1 day ago
CouchPotato preview

CouchPotato

GitHubaaron-kidwell/couchpotato

Windows privilege escalation tool that abuses SeImpersonatePrivilege via indirect syscalls, patching ETW and AMSI to elevate from service account or…
exploitationpayload-developmentpost-exploitation+2
11218 days ago
pentestcode preview

pentestcode

GitHubs0ld13rr/pentestcode

Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…
ai-securitycloud-securityctf+9
70921 days ago
NoiseHound preview

NoiseHound

GitHubwarpedatom/noisehound

Detection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…
adversarial-attackdefensive-toolslateral-movement+4
661 month ago
ransomwhere preview

ransomwhere

GitHubhazcod/ransomwhere

A PoC ransomware sample to test out your ransomware response strategy.
adversarial-attackencryption-decryption-toolsincident-response+3
2181 month ago
PyADRecon preview

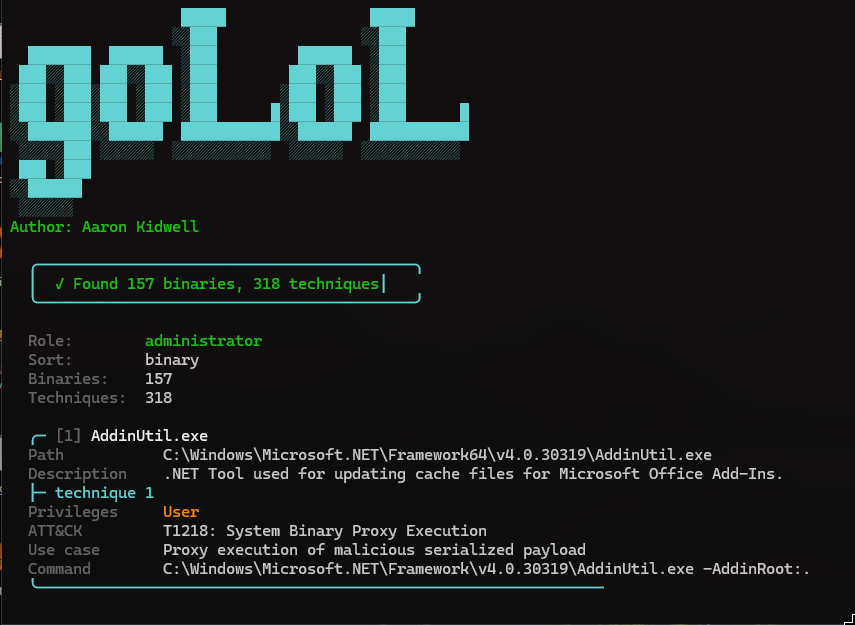
PyADRecon

GitHubl4rm4nd/pyadrecon

Python3 implementation of ADRecon with support for NTLM and Kerberos authentication querying LDAP. Generates individual CSV files and a single XSLX +…
authenticationinformation-gatheringpenetration-testing+4
682 months ago
goLoL preview

goLoL

GitHubaaron-kidwell/golol

goLoL is a Windows host scanner with dual support for LOLBAS binaries and LOLDrivers. It lists LOLBAS techniques runnable at your current privilege…
binary-analysiseducationinformation-gathering+6
692 months ago
pyGPOAbuse preview

pyGPOAbuse

GitHubhackndo/pygpoabuse

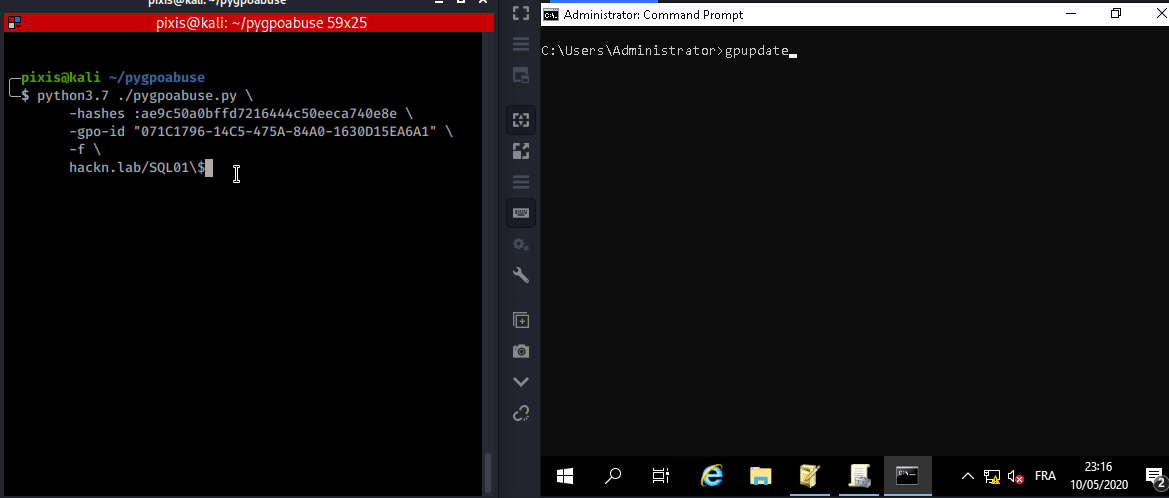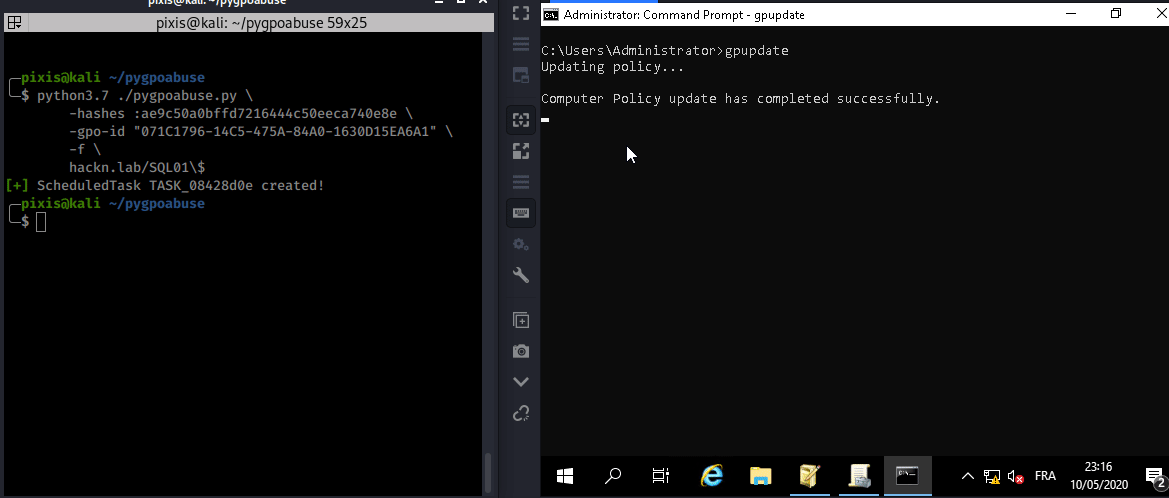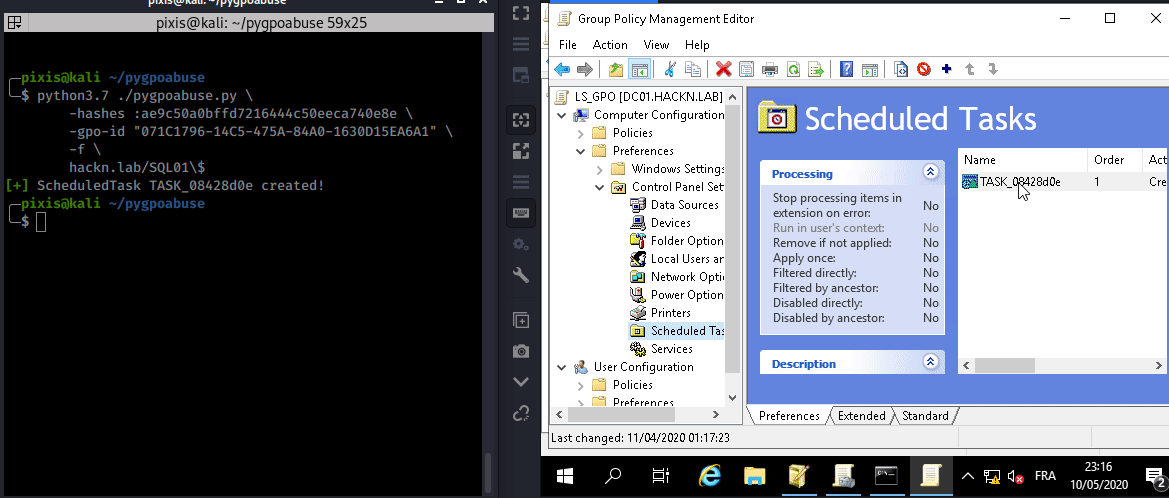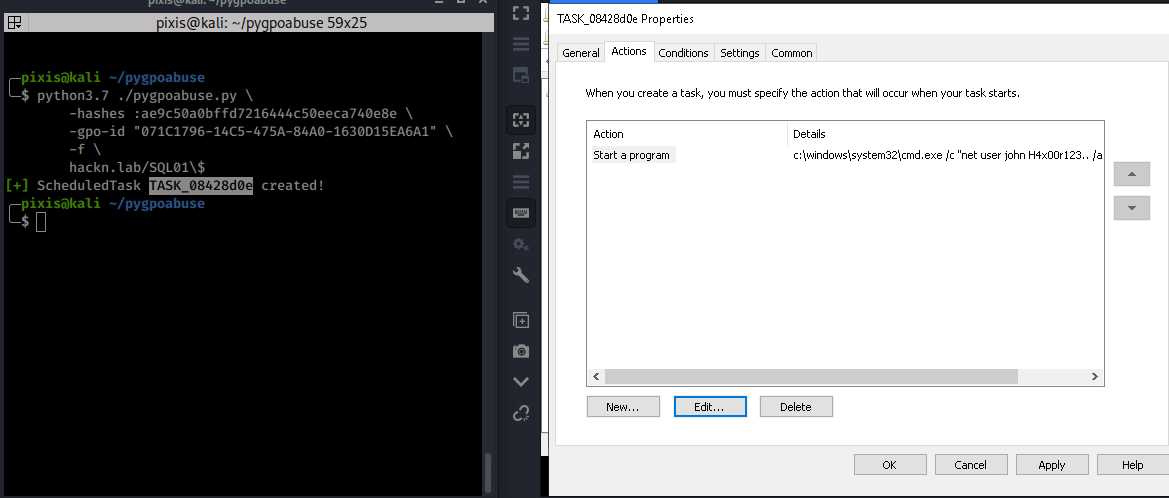
Partial python implementation of SharpGPOAbuse
exploitationlateral-movementpenetration-testing+2
5953 months ago
Prox-Ez preview

Prox-Ez

GitHubsynacktiv/prox-ez

HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…
authenticationimpersonation-toolslateral-movement+4
1133 months ago
EDR-Freeze preview

EDR-Freeze

GitHubtwosevenonet/edr-freeze

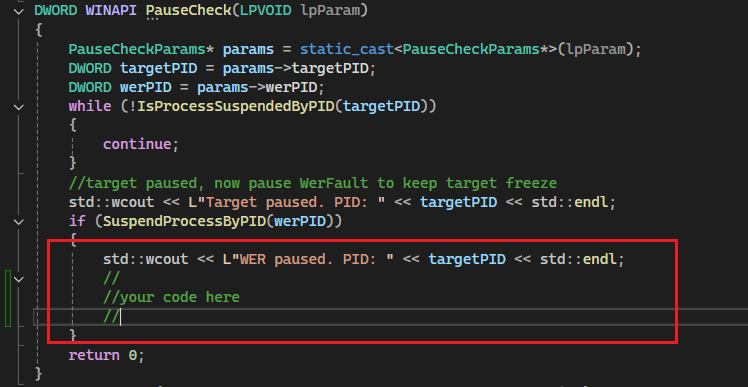
EDR-Freeze is a tool that puts a process of EDR, AntiMalware into a coma state.
exploitationids-ips-evasionpost-exploitation+1
8664 months ago
TotalRecall preview

TotalRecall

GitHubxaitax/totalrecall

This tool extracts and displays data from the Recall feature in Windows 11, providing an easy way to access information about your PC's activity…
data-exfiltrationexploitationinformation-gathering+5
1655 months ago
SNet preview

SNet

GitHubhrmtz/snet

AI-guided CTF - Break into a real server with Claude Code as your trainer
ctfeducationexploitation+8
5 months ago
specula preview

specula

GitHubtrustedsec/specula

Modular command-and-control framework abusing Microsoft Outlook's Home Page feature for stealthy persistence, remote access, and post-exploitation.
command-and-controlpenetration-testing-frameworkspersistence-mechanisms+2
2371 year ago
nimvoke preview

nimvoke

GitHubnbaertsch/nimvoke

Indirect syscalls + DInvoke made simple.
ids-ips-evasionpayload-developmentpost-exploitation+2
951 year ago
BlueDoor preview

BlueDoor

GitHubsethwhy/bluedoor

Can you exploit the EternalBlue vulnerability (CVE-2017-0144) on a Windows 7 system and retrieve the hidden flag? Your goal is to gain administrative…

ctfeducationexploitation+7
21 year ago
LdrLockLiberator preview

LdrLockLiberator

GitHubelliotkillick/ldrlockliberator

For when DLLMain is the only way

exploitationpayload-developmentpersistence-mechanisms+2
4381 year ago
Python-Rootkit preview

Python-Rootkit

GitHub0xislamtaha/python-rootkit

Python Remote Administration Tool (RAT) to gain meterpreter session
command-and-controleducationexploitation+3
6391 year ago
airstrike preview

airstrike

GitHubsmokeme/airstrike

Customizable Stage0 C2 framework with C and Rust agent templates, a Flask backend, and a React dashboard for building and operating your own C2…

command-and-controleducationpayload-development+2
1742 years ago
Previous123Next