

WHFB-PinCapture
 ivancabrera02/whfb-pincapture
Captures Windows Hello PINs at entry by injecting a DLL into LogonUI.exe that sets a CPU hardware breakpoint on NgcSerializeConvenienceCredential,…
debuggersinformation-gatheringmemory-forensics+5
6
ivancabrera02/whfb-pincaptureCaptures Windows Hello PINs at entry by injecting a DLL into LogonUI.exe that sets a CPU hardware breakpoint on NgcSerializeConvenienceCredential,…
 cypherhippie/cve-2026-66804
Local Windows privilege escalation PoC for CVE-2026-66804: plants a COM DLL in a missing path to abuse Camera FrameServer and impersonate SYSTEM.
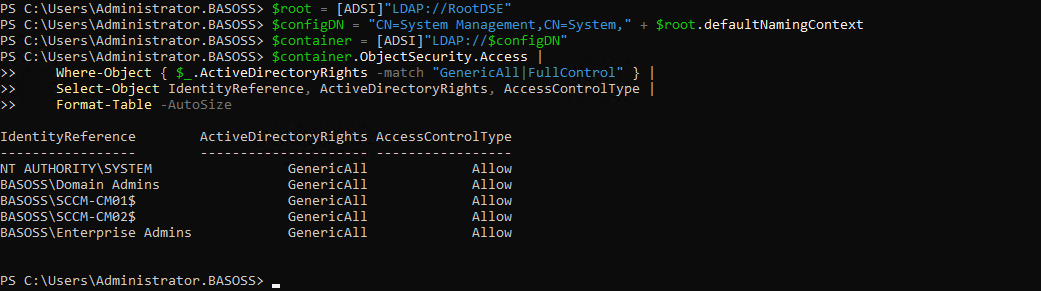 omribaso/sccm-cve-2026-47301-remote-code-execution-exploit
Proof-of-concept exploit chain (CVE-2026-47301) for Microsoft Configuration Manager (SCCM), combining a broken access, CAB arbitrary-write path…
 jonyfilc/printspoofer-reflectivedll
The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…
 r41n3rzuf477/quickassist_uac_bypass
UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…
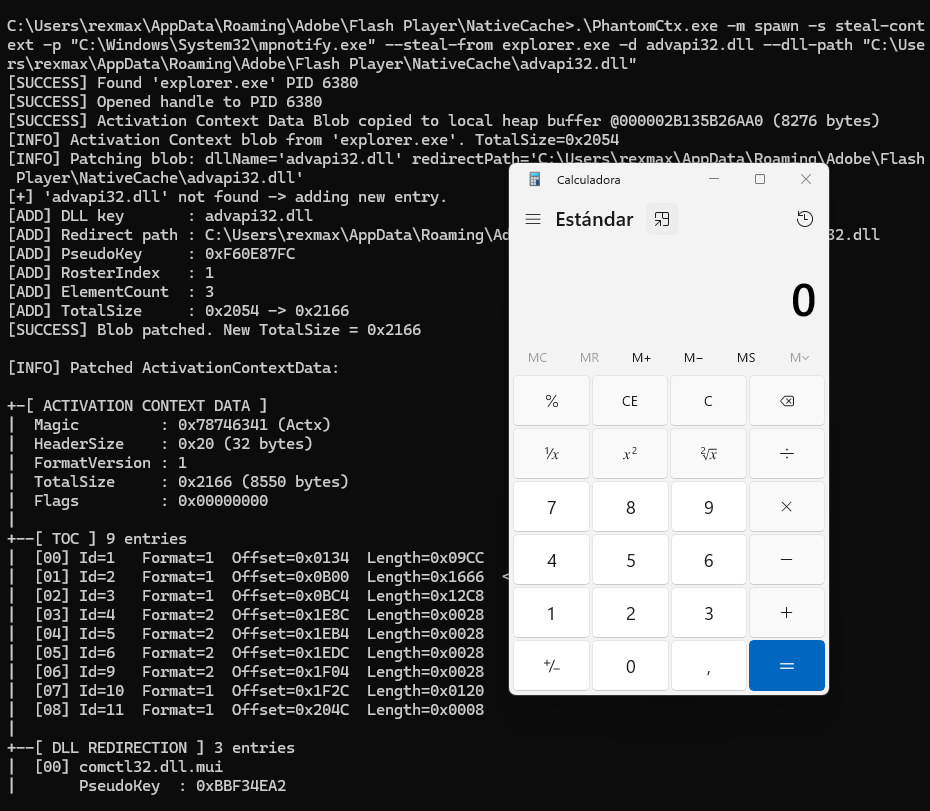 r3xmax/phantomctx
Activation Context Hijacking Evasion Tool
 johnswiftc/rustdllproxy
Generate Proxy DLLs in Rust
 s12cybersecurity/rdpcredentialstealer
Windows implant that steals RDP credentials via API hooking (Detours) and DLL injection, capturing usernames and passwords to a file for red-team…
 hackerhouse-opensource/compmgmtlauncher_dll_uacbypass
CompMgmtLauncher & Sharepoint DLL Search Order hijacking UAC/persist via OneDrive
 hackerhouse-opensource/nofaxgiven
Code Execution & Persistence in NETWORK SERVICE FAX Service
 hackerhouse-opensource/iscsicpl_bypassuac
UAC bypass for x64 Windows 7 - 11
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
 hwbp/clr-unhook
Modern security products (CrowdStrike, Bitdefender, SentinelOne, etc.) hook the nLoadImage function inside clr.dll to intercept and scan in-memory…
 newcomrade12211/cve-2025-56383
DLL hijacking to rev shell
 dll00p/cve-2021-1675
Proof-of-concept exploit for CVE-2021-1675 (PrintNightmare) targeting Windows Print Spooler. Uses msfvenom-generated malicious DLL delivered via SMB…
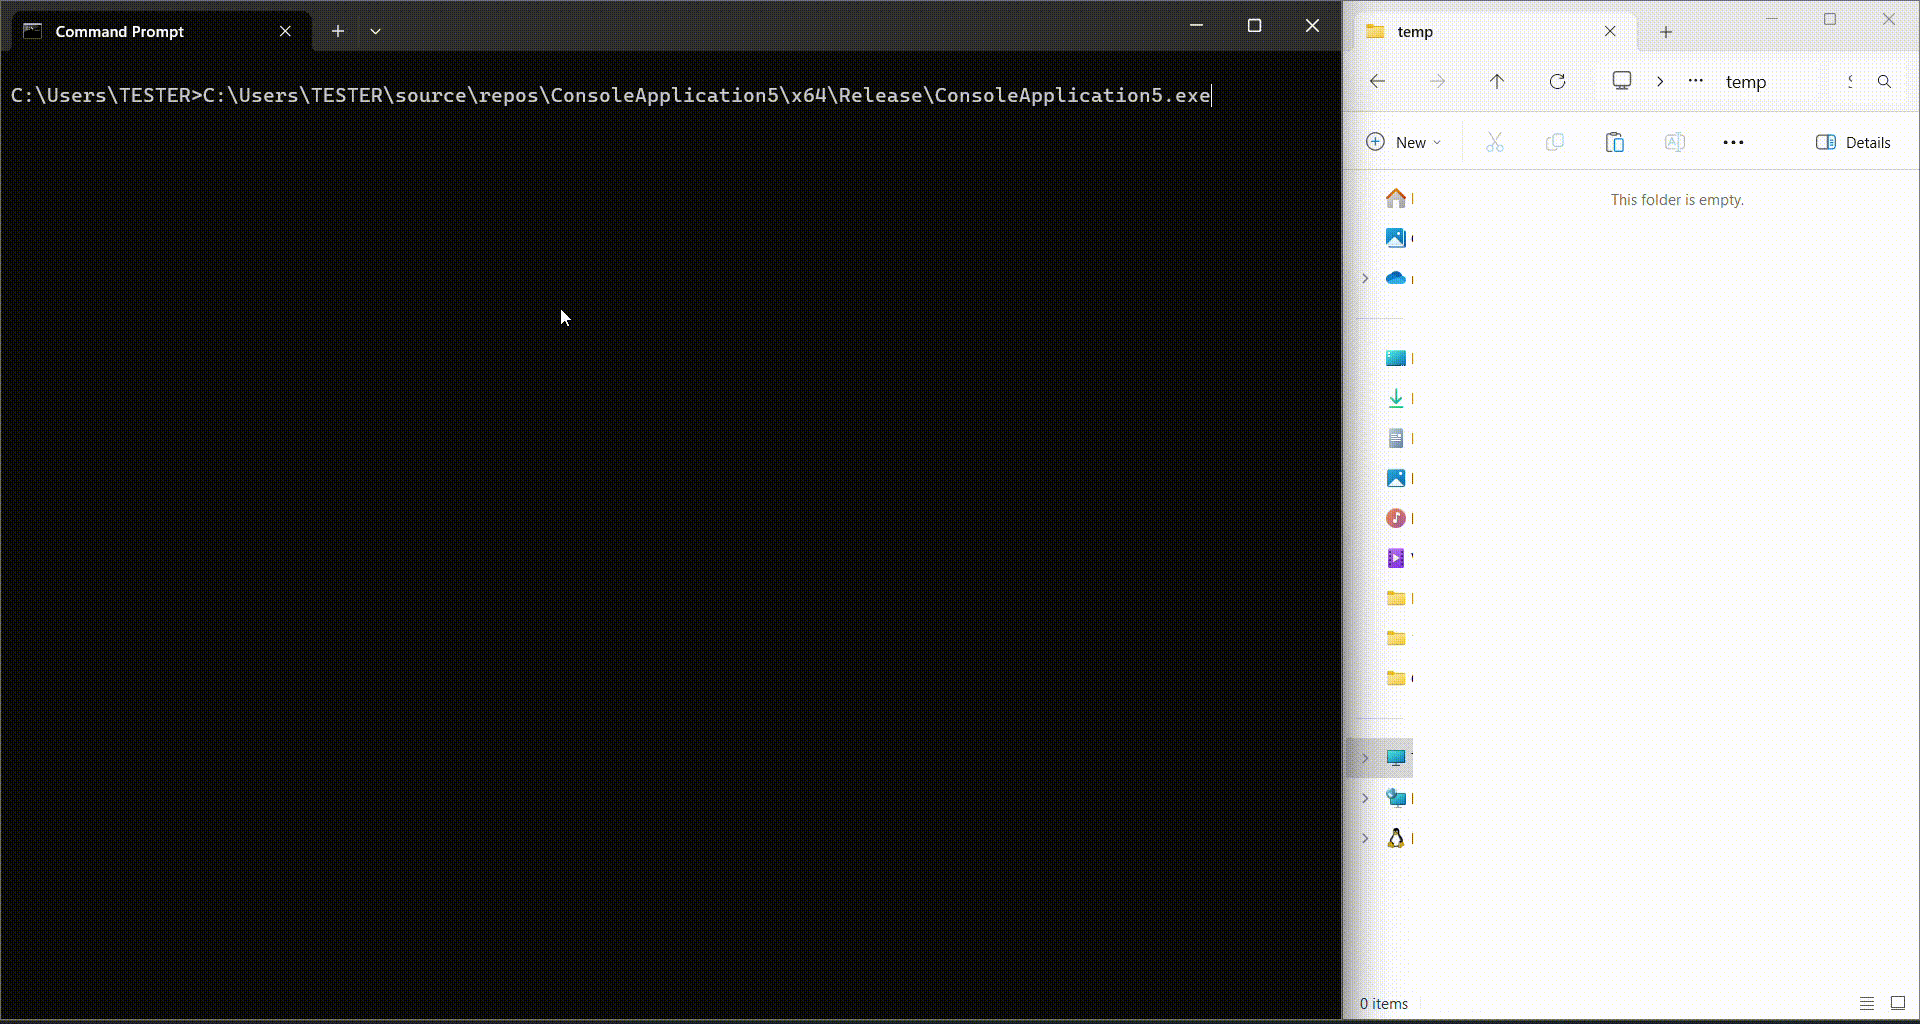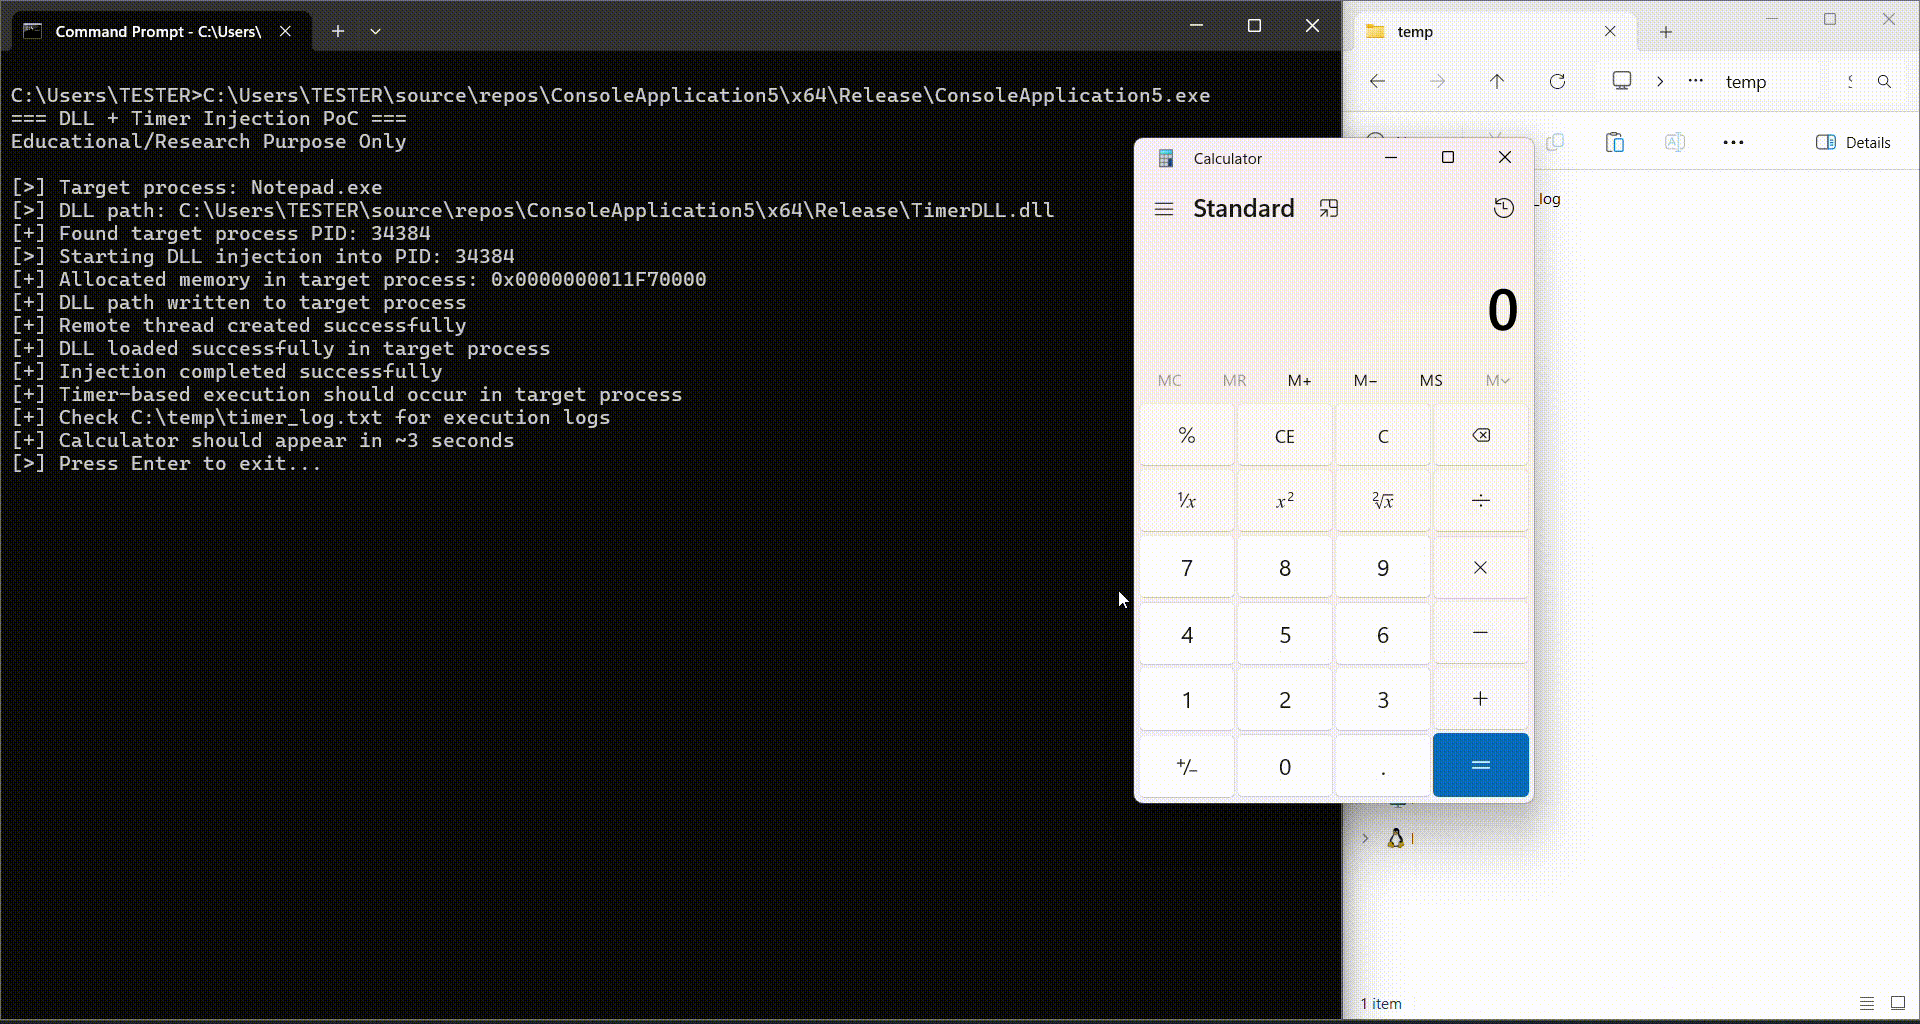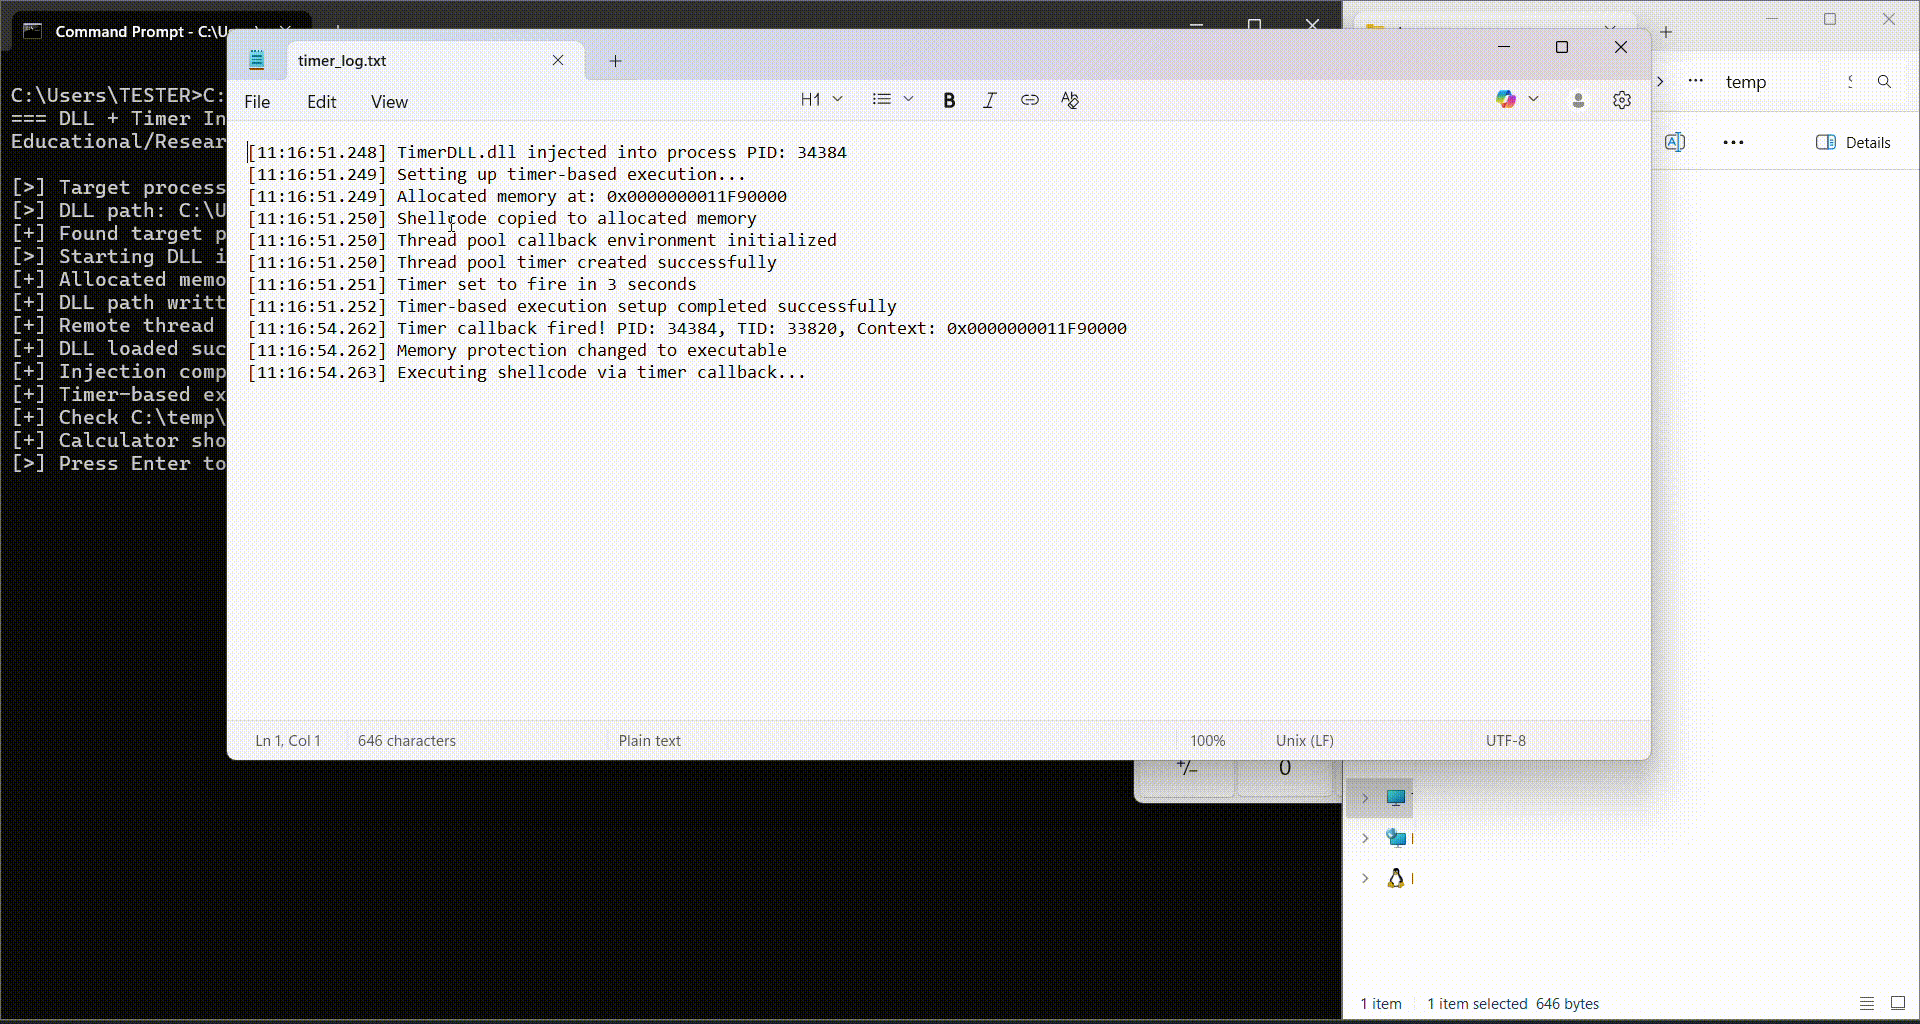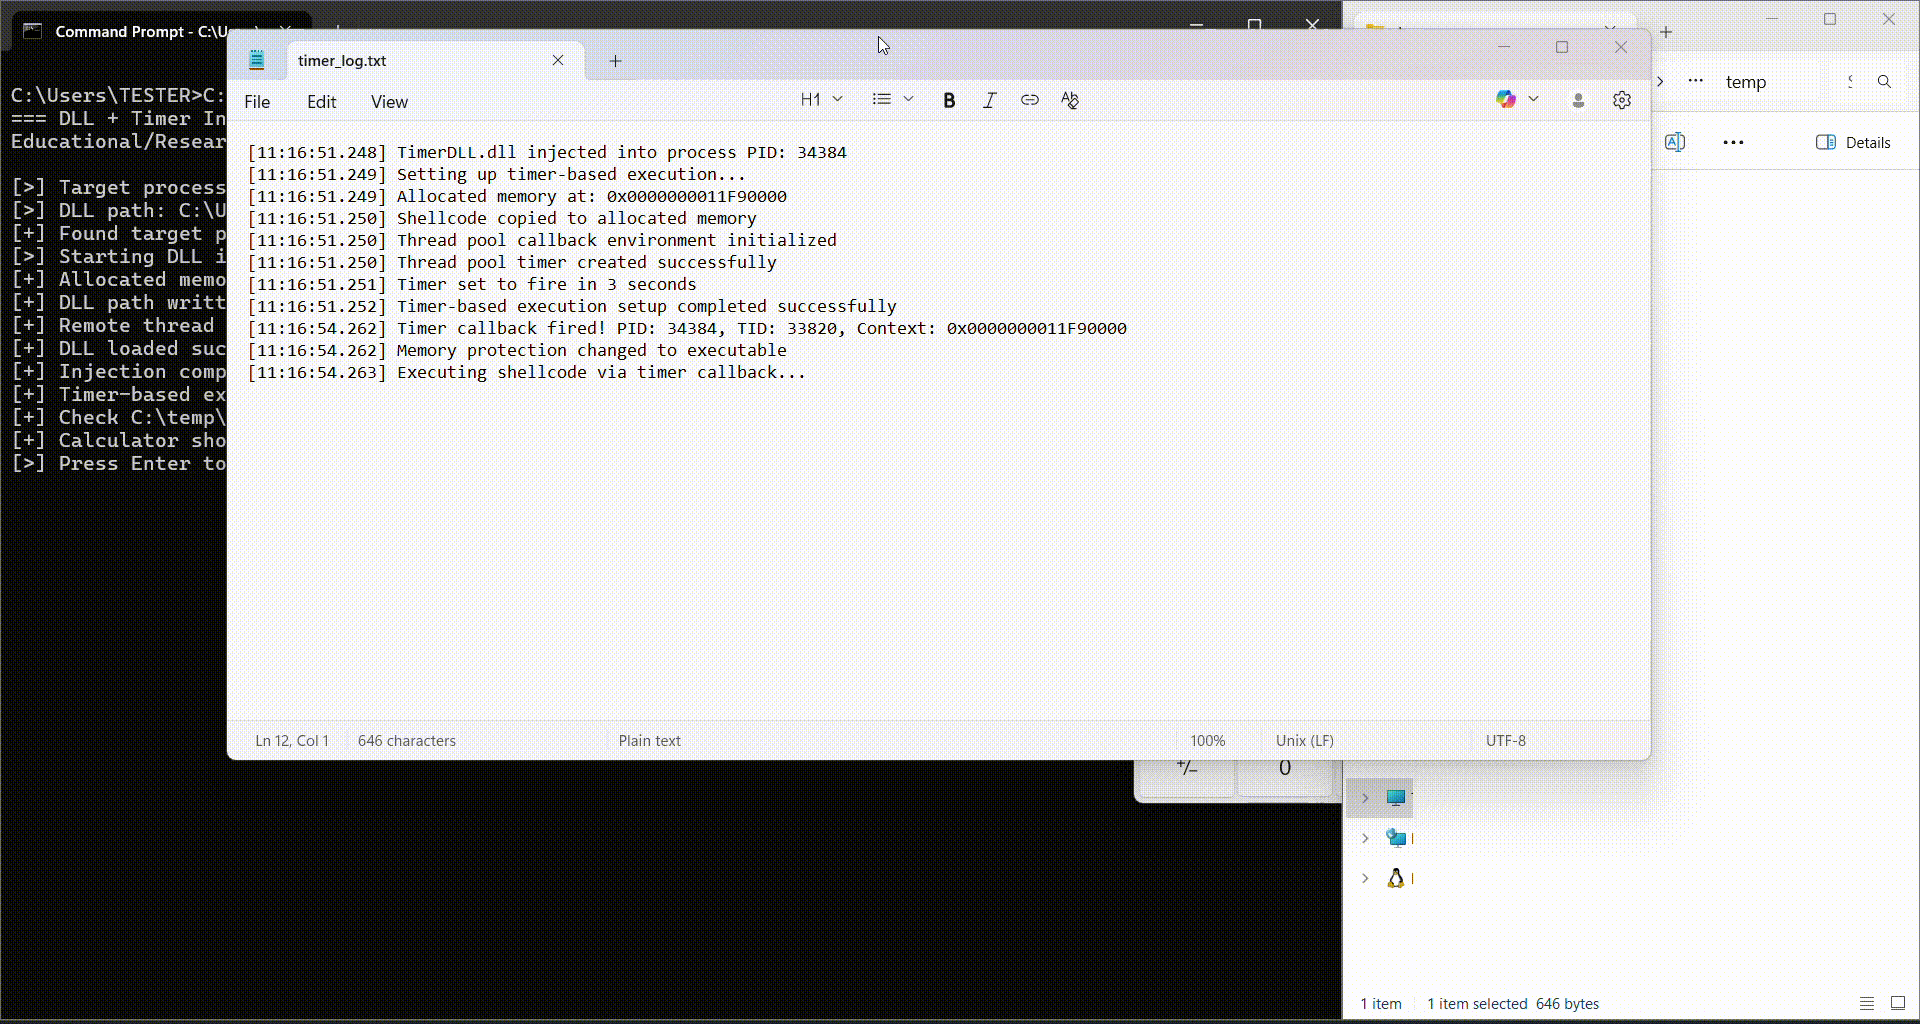 andreisss/remote-dll-injection-with-timer-based-shellcode-execution
Remote DLL Injection with Timer-based Shellcode Execution
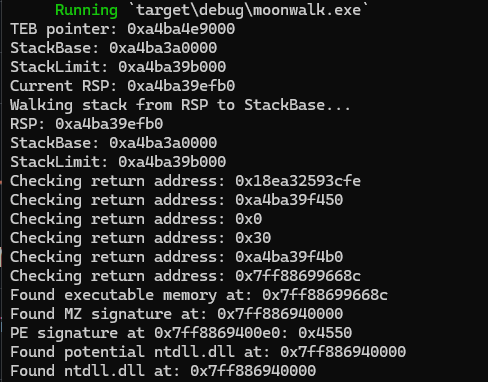 teach2breach/moonwalk
find dll base addresses without PEB WALK
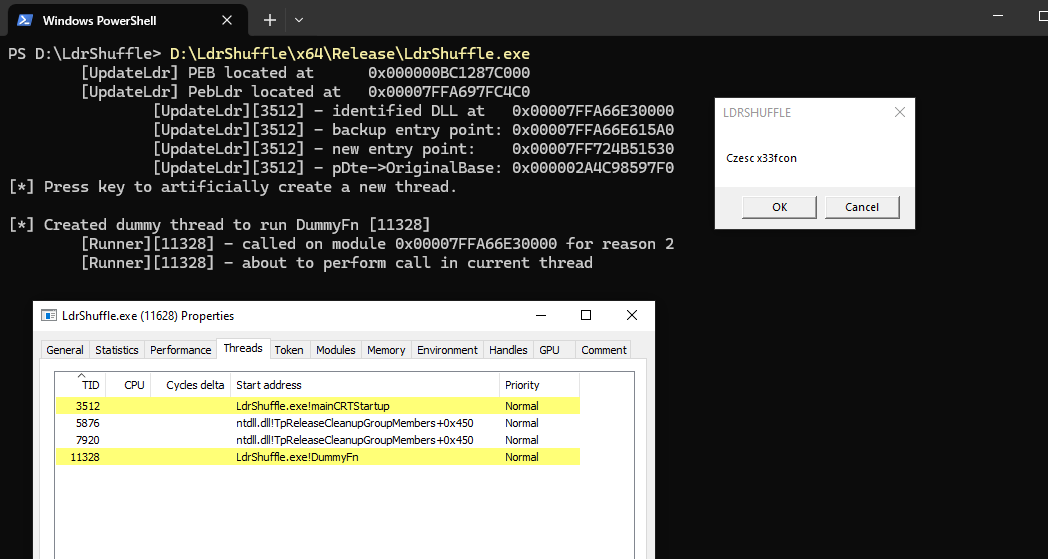 rwxstoned/ldrshuffle
Code execution/injection technique using DLL PEB module structure manipulation