
-CVE-2021-4034
 usmansec/-cve-2021-4034
Controlled proof-of-concept assessment and exploitation report for CVE-2021-4034 (PwnKit) local privilege escalation in pkexec/polkit, with forensic…
exploitationpenetration-testingpost-exploitation+3
1
usmansec/-cve-2021-4034Controlled proof-of-concept assessment and exploitation report for CVE-2021-4034 (PwnKit) local privilege escalation in pkexec/polkit, with forensic…
 jacobtaylor3/c2-and-post-exploitation-framework
CVE-2021-21220 Exploitation infrastructure
 saru1718/thm---solar-exploiting-log-4j
This room is based on exploiting the notorious Log4j vulnerability ( CVE-2021-44228), also referred to as the Log4Shell. The weakness enables…
 simoesctt/ctt-proxylogon-rce-v1.0---convergent-time-theory-enhanced-microsoft-exchange-exploit
An advanced exploit for Microsoft Exchange Server (CVE-2021-26855, CVE-2021-27065) enhanced with Convergent Time Theory principles, achieving…
 ramahmdr/pwnkit
Self-contained exploit for CVE-2021-4034 - Pkexec Local Privilege Escalation
 george-yanni/deeproot
CVE-2021-3493 OverlayFS privilege escalation exploit framework with advanced red team features. Includes persistence mechanisms, post-exploitation…
 withinonestem/poc-bash-cve-2021-3560
Script Bash -- CVE-2021-3560
 p1rat3r00t/why-so-serious-sam
PoC malware that uses exploit CVE-2021-36934 (improper ACLs on shadow copies) using a fileless red team method on Windows 10/11 with LOLBins,…
 ausk1ll9/cve-2021-34527
CVE-2021-34527 is a critical remote code execution and local privilege escalation vulnerability dubbed "PrintNightmare."
 tadash10/exploiting-cve-2021-44228-log4shell-in-a-banking-environment
Objective: Demonstrate the exploitation of the Log4Shell vulnerability (CVE-2021-44228) within a simulated banking application environment.
 artemis-mike/cve-2021-4034
PoC for cve-2021-4034
 koztkozt/cve-2021-1366
Proof-of-concept for Cisco AnyConnect HostScan local privilege escalation via DLL hijacking and IPC command injection, demonstrating DLL proxying to…
 muhammad-ali007/log4j_cve-2021-44228
Hands-on lab exercise for exploiting Log4Shell (CVE-2021-44228) with JNDI injection, LDAP referral servers, and reverse shell payloads. Includes…
 deeexcee-io/cve-2021-44731-snap-confine-suid
Local privilege escalation exploit for CVE-2021-44731 targeting snap-confine versions 2.54.2 and lower. Automatically detects vulnerable binaries and…
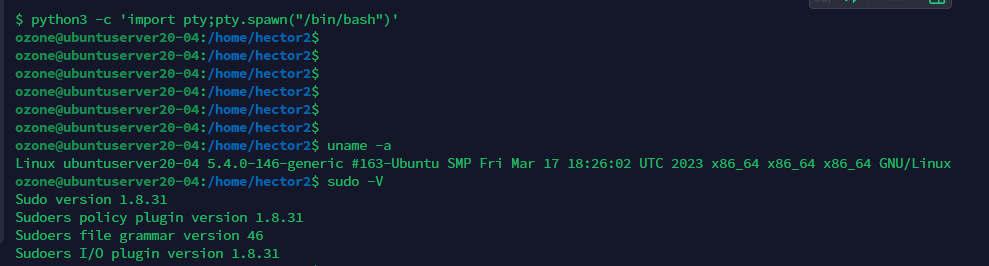 purpleozone/pe_cve-cve-2021-3156
Exploit for Ubuntu 20.04 using CVE-2021-3156 enhanced with post-exploitation scripts
 phuketisland/cve-2021-3156-centos7
利用sudo提权,只针对cnetos7
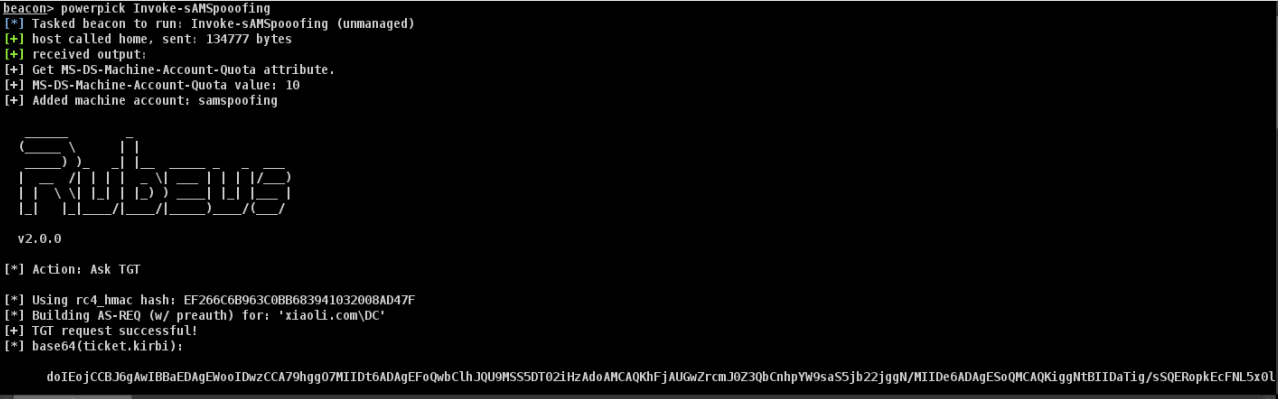 xiaolichan/invoke-samspoofing
CVE-2021-42287/CVE-2021-42278 exploits in powershell
 jbaines-r7/blankspace
Proof of Concept for EFSRPC Arbitrary File Upload (CVE-2021-43893)