injection-2
 gmh5225/injection-2
Curated collection of Windows process injection techniques, linking write-ups on Conhost, PROPagate, KernelCallbackTable, KnownDlls poisoning and…
curated-resourcesdefensive-toolsexploitation+4
7
gmh5225/injection-2Curated collection of Windows process injection techniques, linking write-ups on Conhost, PROPagate, KernelCallbackTable, KnownDlls poisoning and…
 spiralbl0ck/mallicious-ios-shortcut-keylogger-
iOS Shortcut-based keylogger designed to capture keystrokes and exfiltrate data from compromised devices.
 jailbreaks/empty_list
empty_list - exploit for p0 issue 1564 (CVE-2018-4243) iOS 11.0 - 11.3.1 kernel r/w

 bazad/blanket
CVE-2018-4280: Mach port replacement vulnerability in launchd on iOS 11.2.6 leading to sandbox escape, privilege escalation, and codesigning bypass.
 tr00jan99/pwntilldawn-portal-walkthrough
A detailed penetration testing walkthrough and exploitation report for the 'Portal' machine, focusing on CVE-2011-2523 (vsFTPd 2.3.4 Backdoor) to…
 mwr-cybersec/pxethief
PXEThief is a set of tooling that can extract passwords from the Operating System Deployment functionality in Microsoft Endpoint Configuration Manager
 brows3r/ipwn
A Framework meant for the exploitation of iOS devices.
 3nailsinfosec/dcvc2
Discord voice channel C2 framework for covert command and control operations. Transmits all data via RTP packets over voice channels, leaving no…
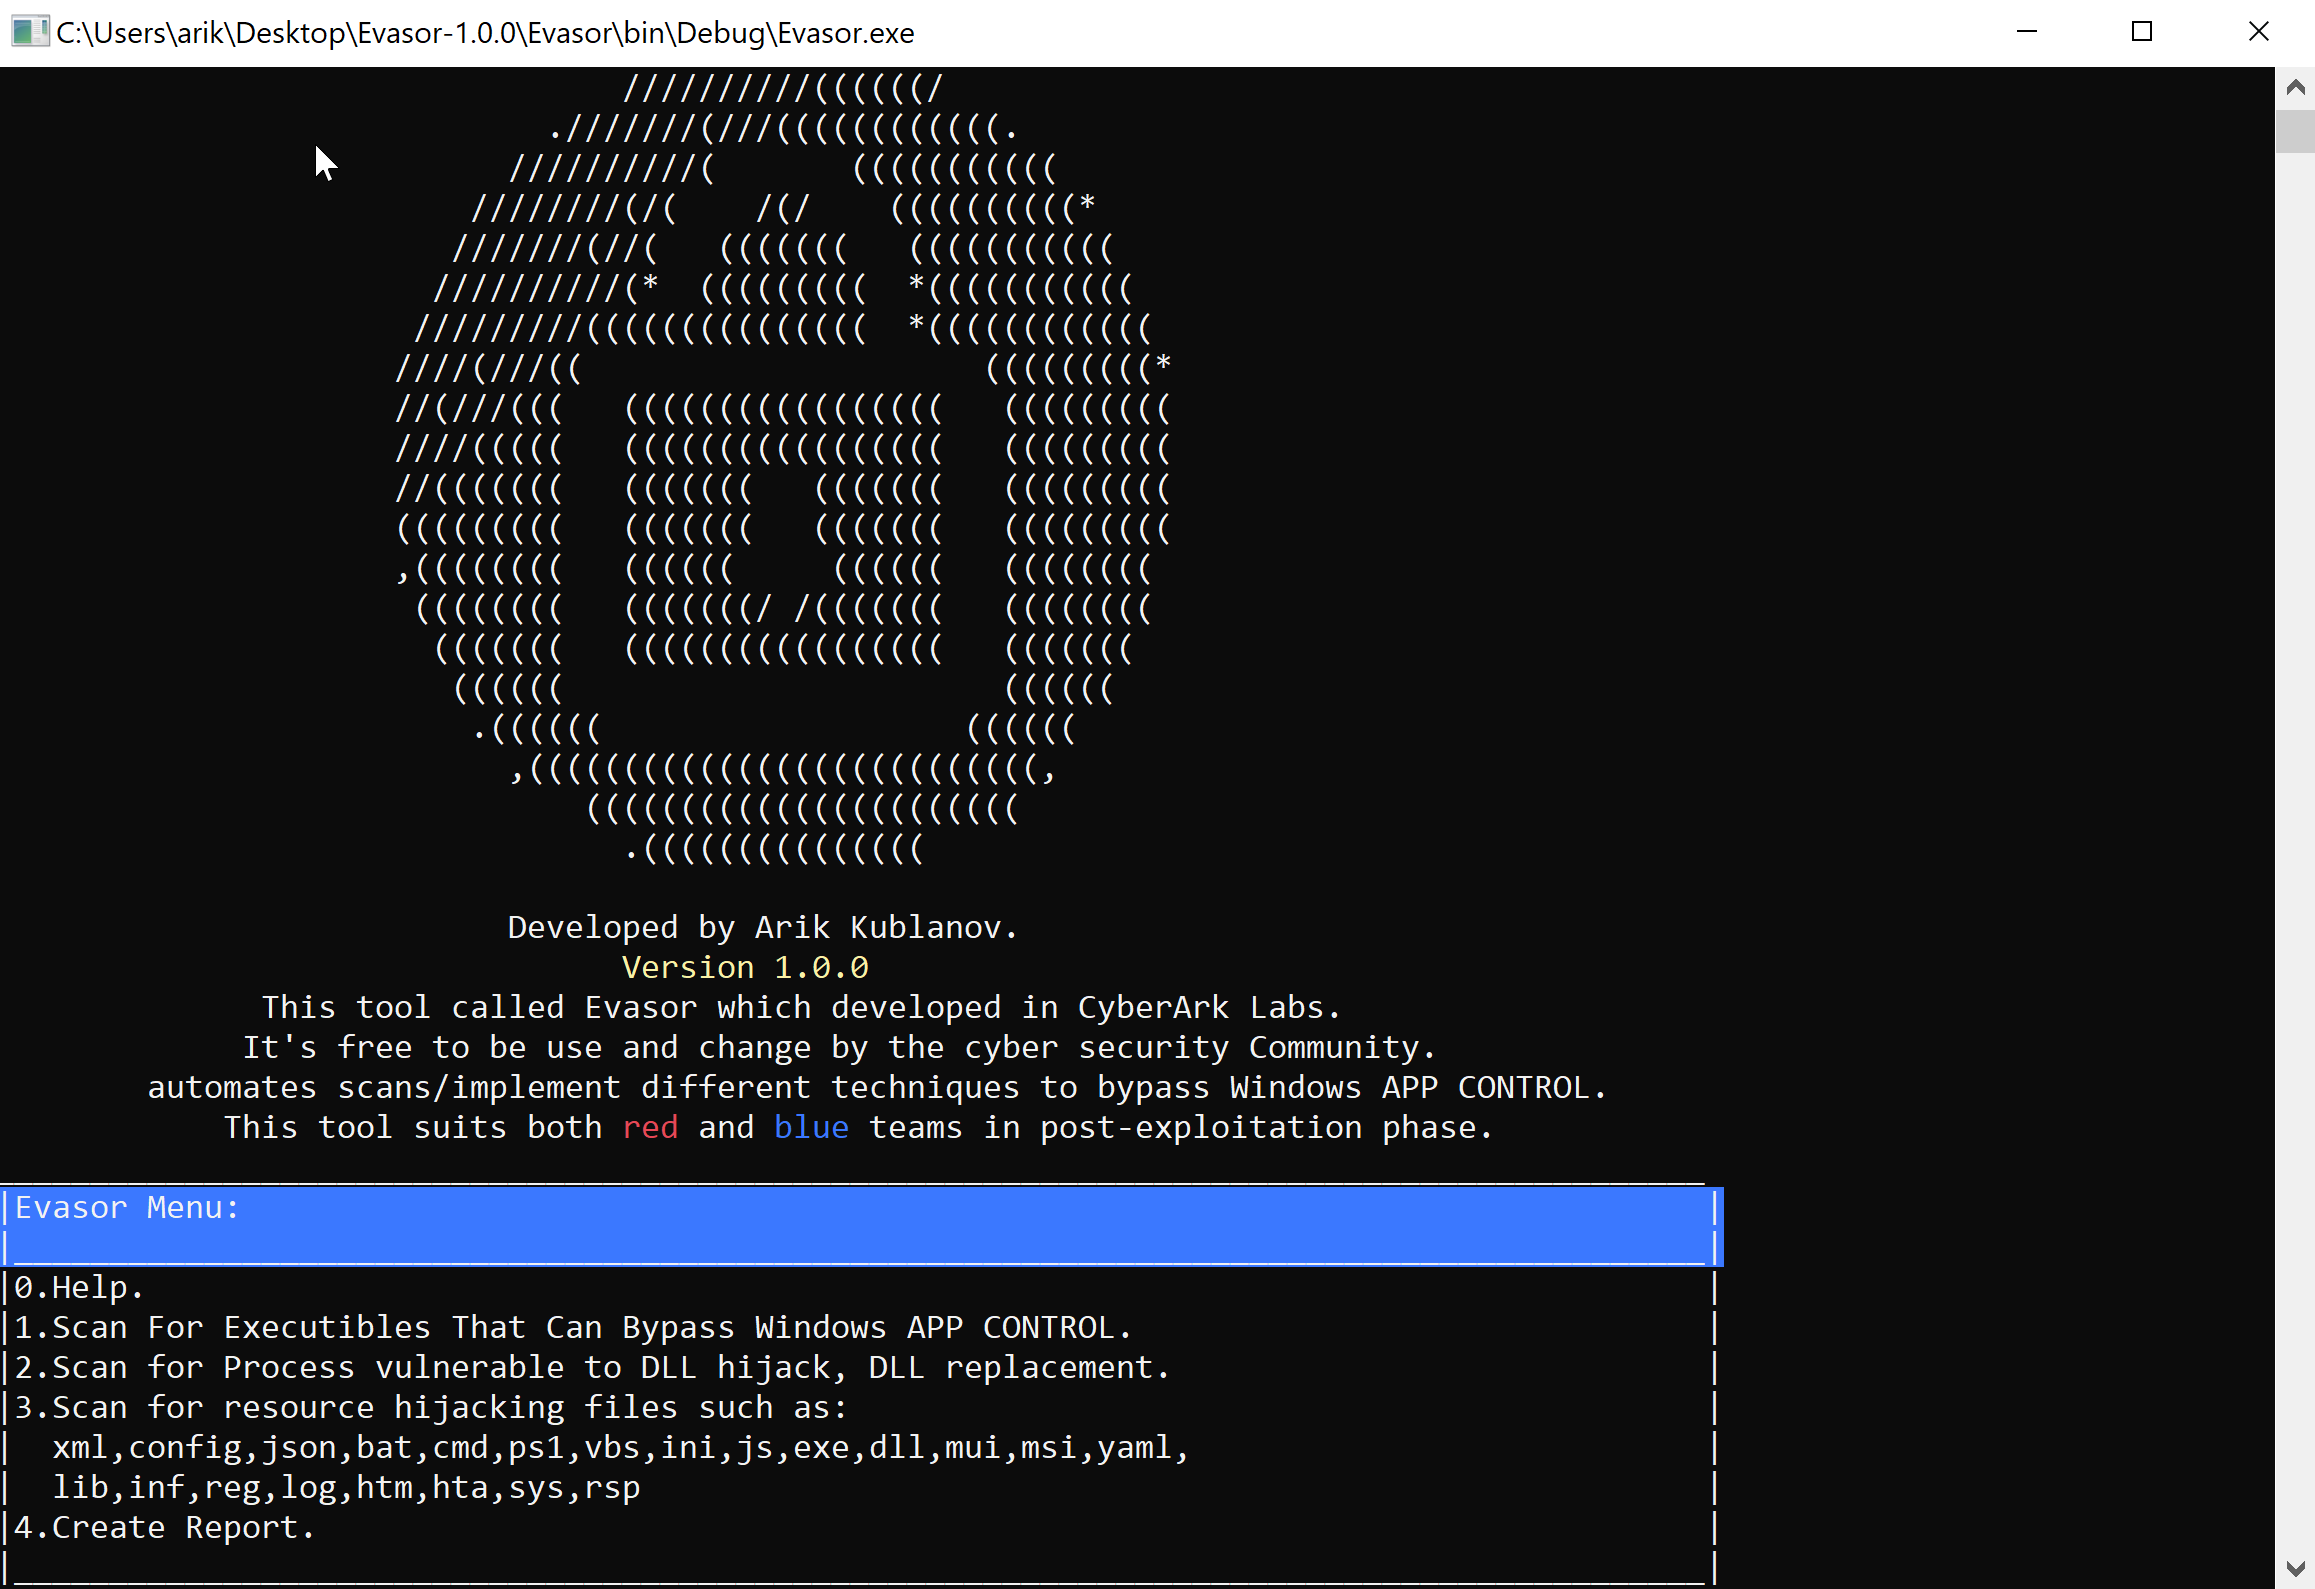 cyberark/evasor
A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies