
CVE-2010-2075
 rushikesh-a-bhujbal/cve-2010-2075
UnrealIRCd 3.2.8.1 backdoor exploit — reverse shell via AB; trigger, built from scratch in Python using raw sockets. No Metasploit.
educationexploitationlabs-practice+7
rushikesh-a-bhujbal/cve-2010-2075UnrealIRCd 3.2.8.1 backdoor exploit — reverse shell via AB; trigger, built from scratch in Python using raw sockets. No Metasploit.
 theandersmadsen/humane-aipin-ghostlock
Guarded, source-only Humane AI Pin root PoC for CVE-2026-43499
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 jolovicdev/hayduk
Graphical attack management console for Metasploit: the lineage of Armitage as a single Go binary with a browser UI. Live network topology, campaign…
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 rasta-mouse/ost-c2-spec
Open Source C&C Specification
 tennc/webshell
This is a webshell open source project
 bridgeralderson/cve-2026-58424
A flaw in Gitea Open Source Git Server’s approval‑gate logic allows a pull request that originates from a permanent fork to merge without satisfying…
 cr4sh/smmbackdoor
First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
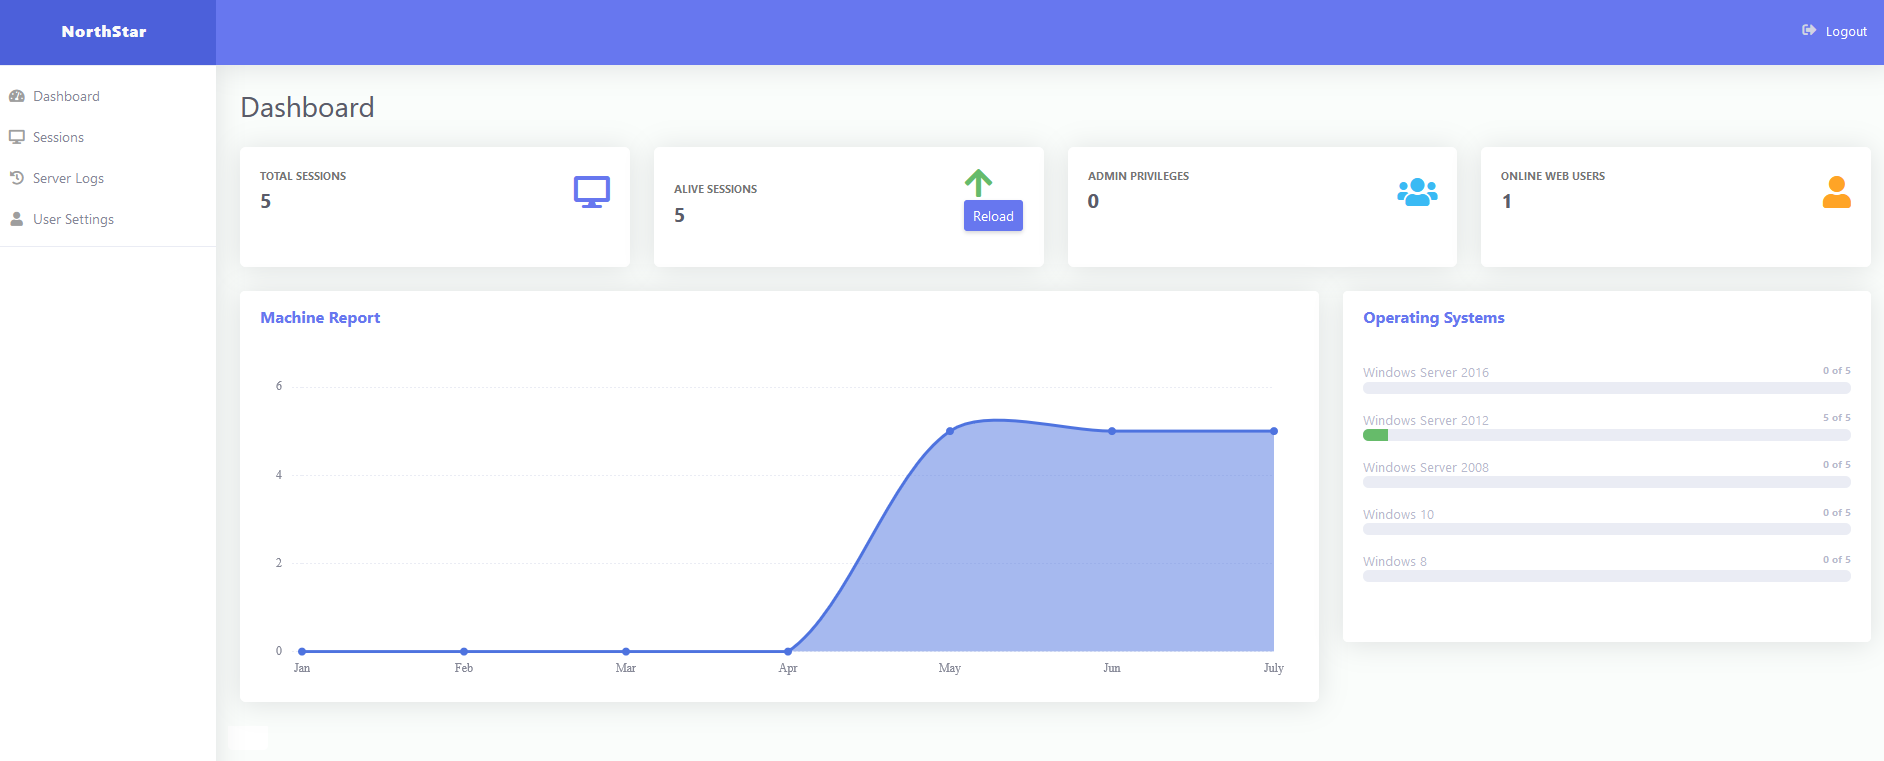 eng1ndes/northstarc2
Web Based Command Control Framework (C2) #C2 #PostExploitation #CommandControl #RedTeam #C2Framework #PHPC2 #.NETMalware #Malware #PHPMalware #CnC…
 nccgroup/fenrir
PoC to tunnel the Meterpreter reverse HTTP shell over RDP Virtual Channels
 nccgroup/loki
LOKI (Limited Obstructive Keyboard Impersonator) is a RDP File Transfer Tool Using Keypresses
 nccgroup/scomdecrypt
SCOMDecrypt is a tool to decrypt stored RunAs credentials from SCOM servers
 infodox/tsh-sctp
TinySHell port to SCTP
 nu11secur1ty/metasploit-framework-nu11secur1ty
Extending of metasploit-framework
 sin5678/gh0st
a open source remote administrator tool
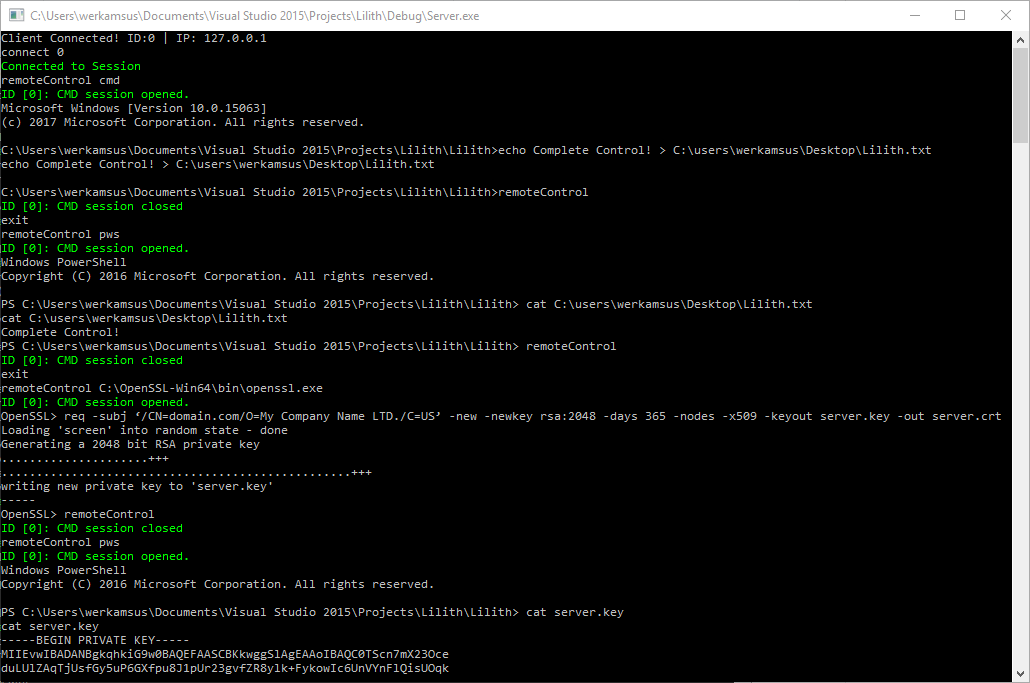 werkamsus/lilith
Lilith - Foundational reverse engineering resource for cybersecurity entrepreneurs in C++
 alphaseclab/awesome-rat
RAT And C&C Resources. 250+ Open Source Projects, 1200+ RAT/C&C blog/video.