
adPEAS
 61106960/adpeas
Powershell tool to automate Active Directory enumeration.
authenticationexploitationinformation-gathering+6
61106960/adpeasPowershell tool to automate Active Directory enumeration.
 mertdas/redpersist
C# tool for establishing Windows persistence via multiple techniques including scheduled tasks, WMI events, startup folders, and registry hijacking,…
 rifting/unrestrictedusercreator
Simple script to add a new, unrestricted user on devices with Family Link by abusing CVE-2025-32324 (pre September patch)
 login-securite/donpapi
Automated remote credential dumper for Windows environments, extracting DPAPI secrets, browser credentials, certificates, and configuration files…
 maldev-academy/maldevacademyldr.2
RunPE implementation with multiple evasive techniques (2)
 harleyqu1nn/aggressorscripts
Collection of Aggressor scripts for Cobalt Strike 3.0+ pulled from multiple sources
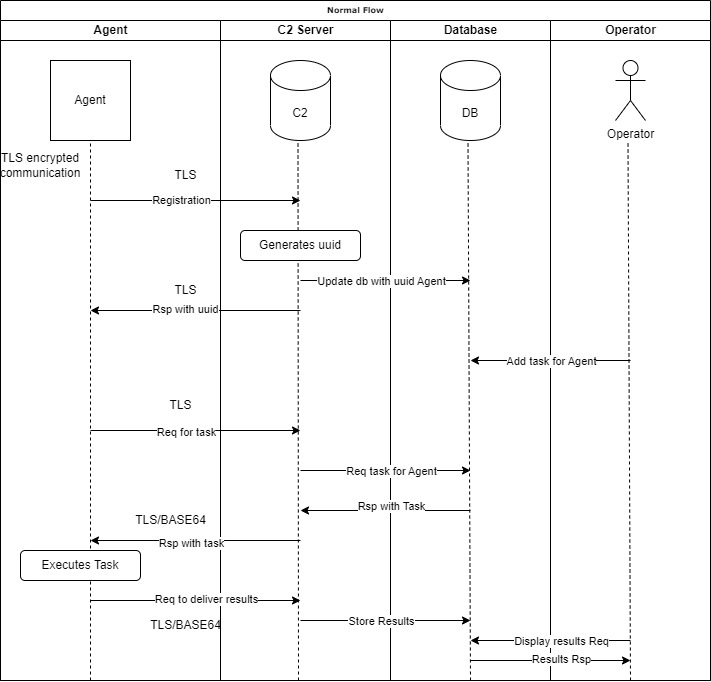 voukatas/commander
Python-based command and control framework with encrypted TLS communication, multiple agent support (Python/C), interactive sessions, file transfer,…
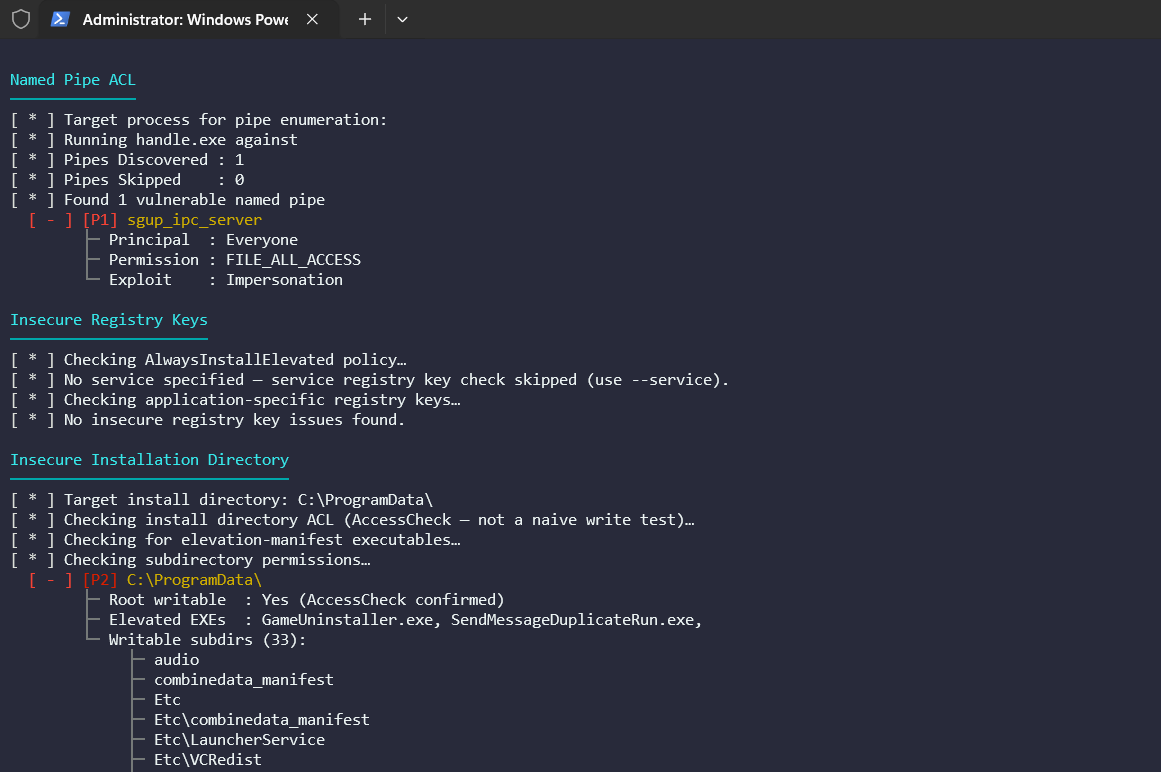 shellkraft/anvil
Anvil is a runtime-first attack surface assessment tool for Windows thick client applications, built for penetration testers and security researchers…
 ricardojoserf/samdump
Extract the SAM and SYSTEM hives using the Volume Shadow Copy (VSS) API. With exfiltration and XOR obfuscation options. In C#, C++, Crystal, Python,…
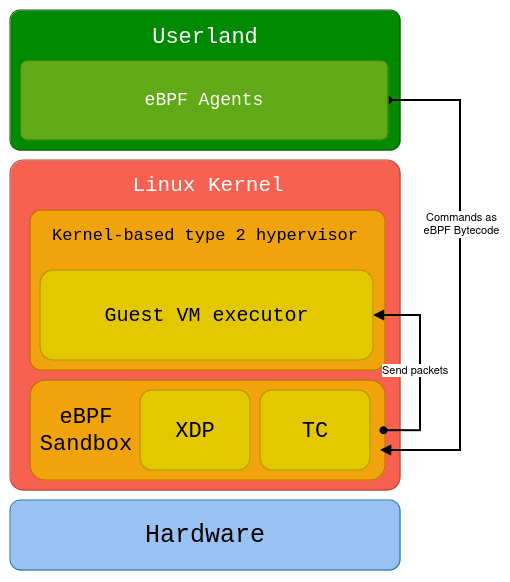 shard77/blackpill
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
 esskumar/phantomevasion
Python-based antivirus evasion tool generating undetectable executables from msfvenom payloads with advanced techniques like junkcode injection,…
 ntdallas/bof_runpe
BOF to run PE in Cobalt Strike Beacon without console creation
 mbadanoiu/cve-2024-37081
CVE-2024-37081: Multiple Local Privilege Escalation in VMware vCenter Server
 thecybergeek/cve-2019-19268
New Found 0-days!