
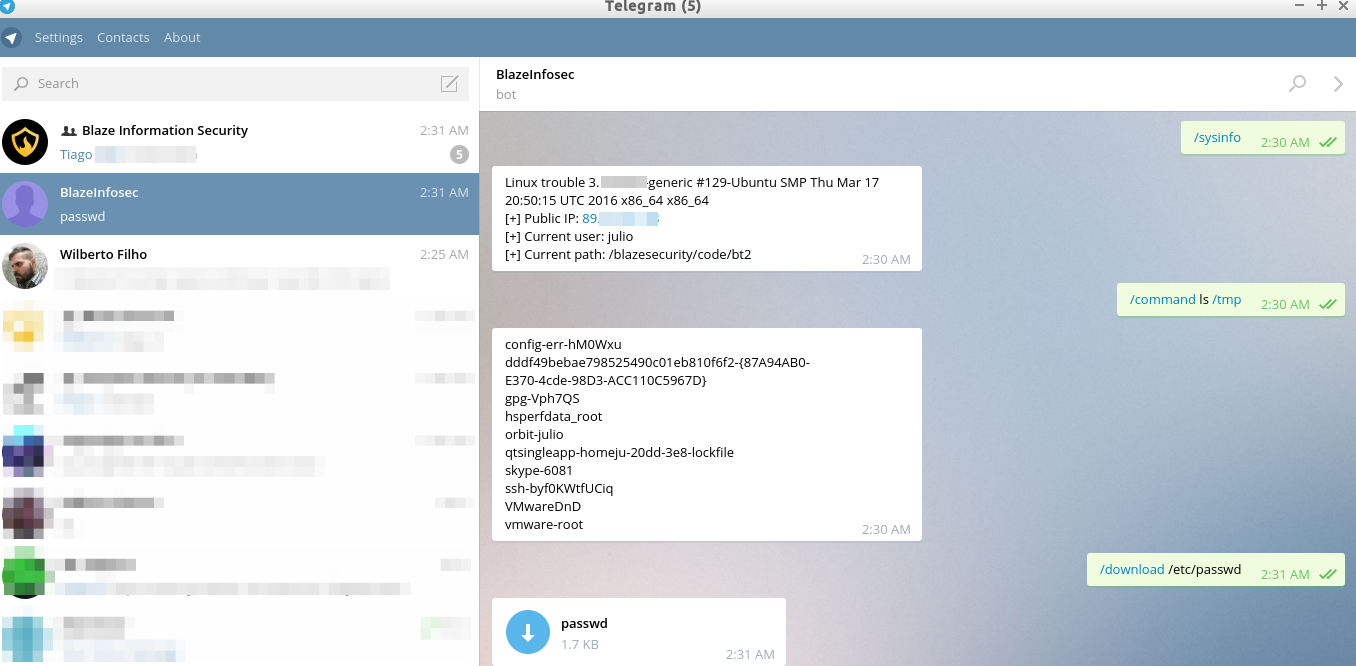
bt2
 blazeinfosec/bt2
Blaze Telegram Backdoor Toolkit is a post-exploitation tool that leverages the infrastructure of Telegram as a C&C
command-and-controlpayload-developmentpenetration-testing+3
207
blazeinfosec/bt2Blaze Telegram Backdoor Toolkit is a post-exploitation tool that leverages the infrastructure of Telegram as a C&C
 cyberstruggle/chalumeau
Chalumeau is automated,extendable and customizable credential dumping tool based on powershell and python.
 byt3bl33d3r/gcat
A PoC backdoor that uses Gmail as a C&C server
 cr4sh/smmbackdoor
First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
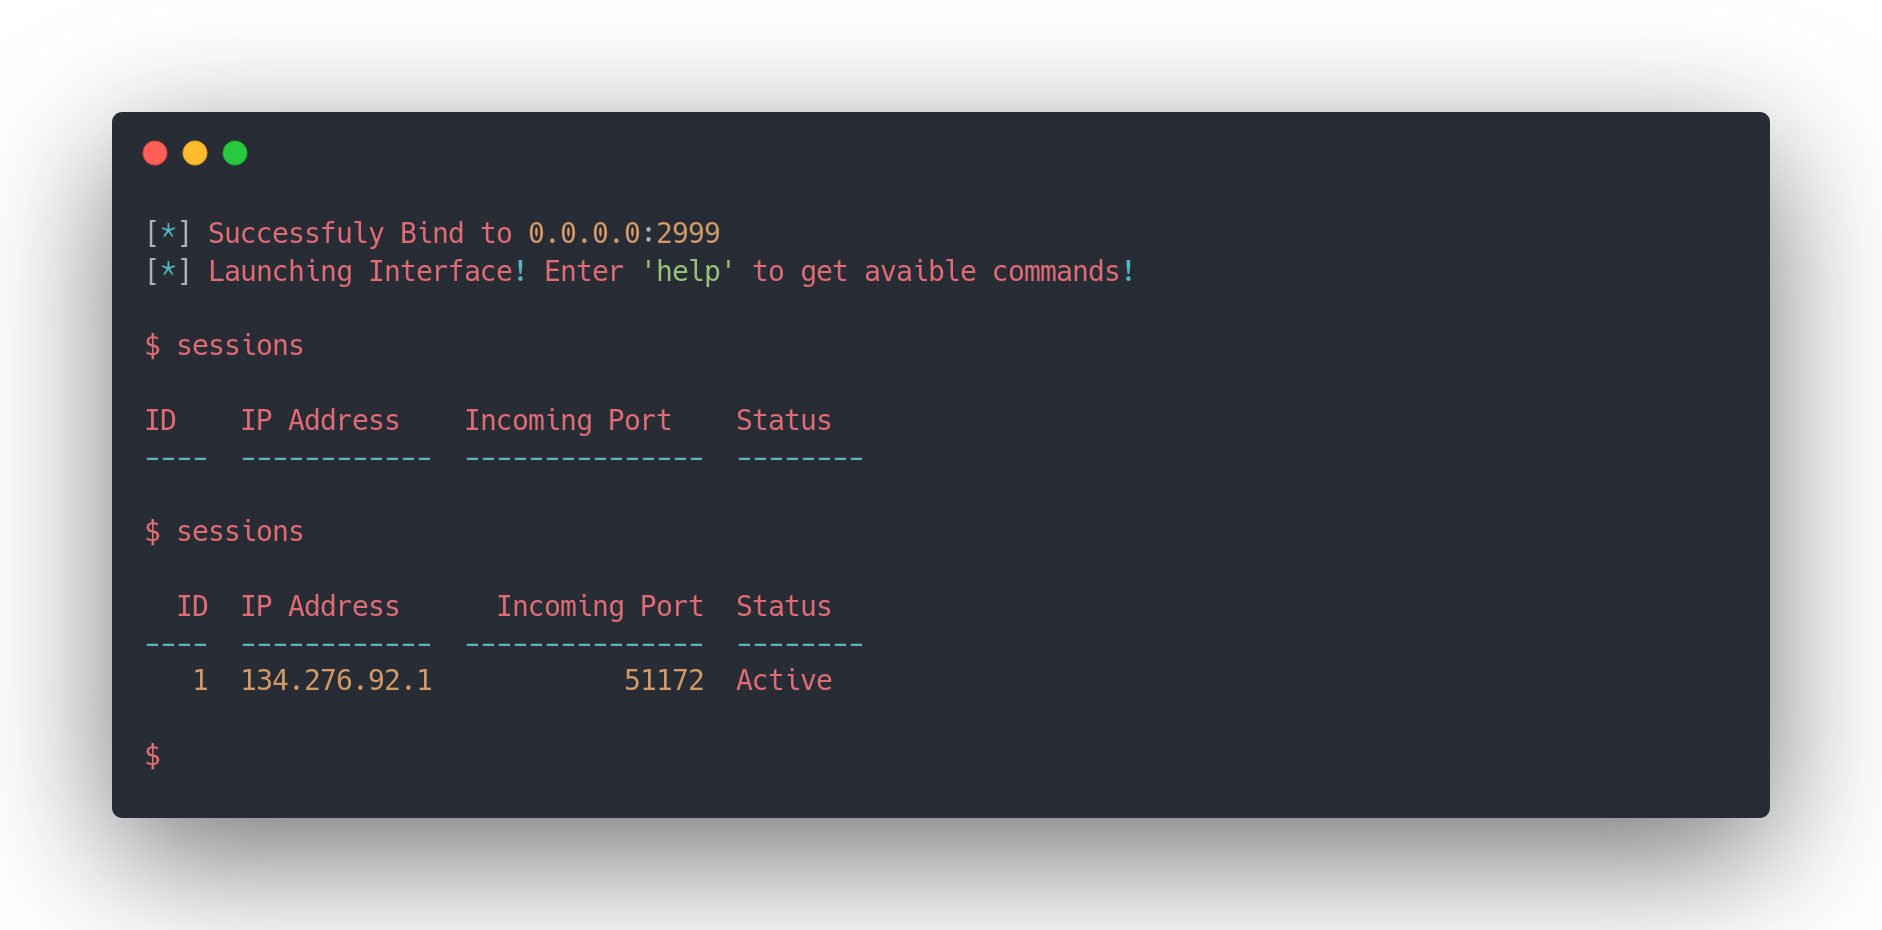 hash3lizer/sillyrat
A Python based RAT 🐀 (Remote Access Trojan) for getting reverse shell 🖥️
 paulsec/twittor
A fully featured backdoor that uses Twitter as a C&C server
 ahhh/reverse_https_bot
A python based https remote access trojan for penetration testing
 maldevel/gdog
A fully featured Windows backdoor that uses Gmail as a C&C server
 maldevel/canisrufus
A stealthy Python based Windows backdoor that uses Github as a command and control server
 panagiks/rspet
RSPET (Reverse Shell and Post Exploitation Tool) is a Python based reverse shell equipped with functionalities that assist in a post exploitation…
 noname-elv/cve-2026-48907
Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…