
CyberStrikeAI
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
ai-securitybinary-analysiscloud-security+9
5.7k
ed1s0nz/cyberstrikeaiThe system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 joshuagodwin7929/purple-team-automation
Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.
 ahmyth/ahmyth-android-rat
Android Remote Administration Tool
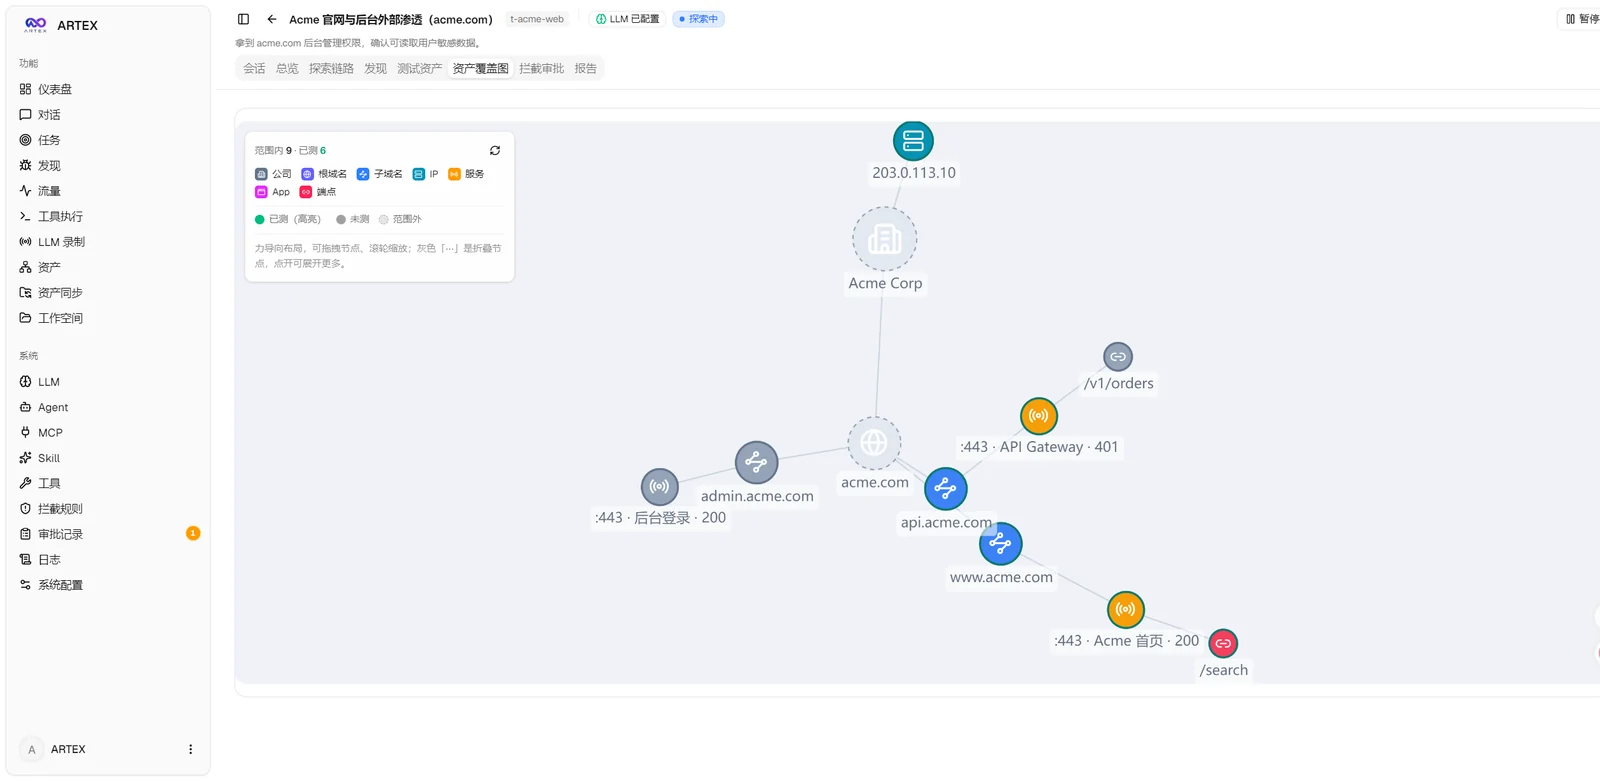 trhhubsd/artex
Multi-agent LLM system for autonomous penetration testing in isolated labs: planner/worker agents share asset and exploration graphs, with MITM…
 omar-tamerr/horuseye
AI-Powered Active Directory Attack Platform
 a2333c/dfroot
Android root tool for Samsung Galaxy S25 Ultra (SM-S938B) that chains DirtyFrag CVE-2026-43284 and CVE-2026-43499 to gain root automatically at boot…
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 1ndevelopment/ghostlock-s26
GhostLock (CVE-2026-43499) app for the Galaxy S26 series
 ccp-p/ghostlock-cve-2026-43499-4.19-k40
Android kernel LPE PoC for CVE-2026-43499, an rtmutex use-after-free in 4.19 Qualcomm kernels, adapted for Redmi K40 with LD_PRELOAD root payload.
 itm4n/pentest-windows
Collection of Windows internals research and exploitation techniques covering privilege escalation, token abuse, and post-exploitation tricks for red…
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
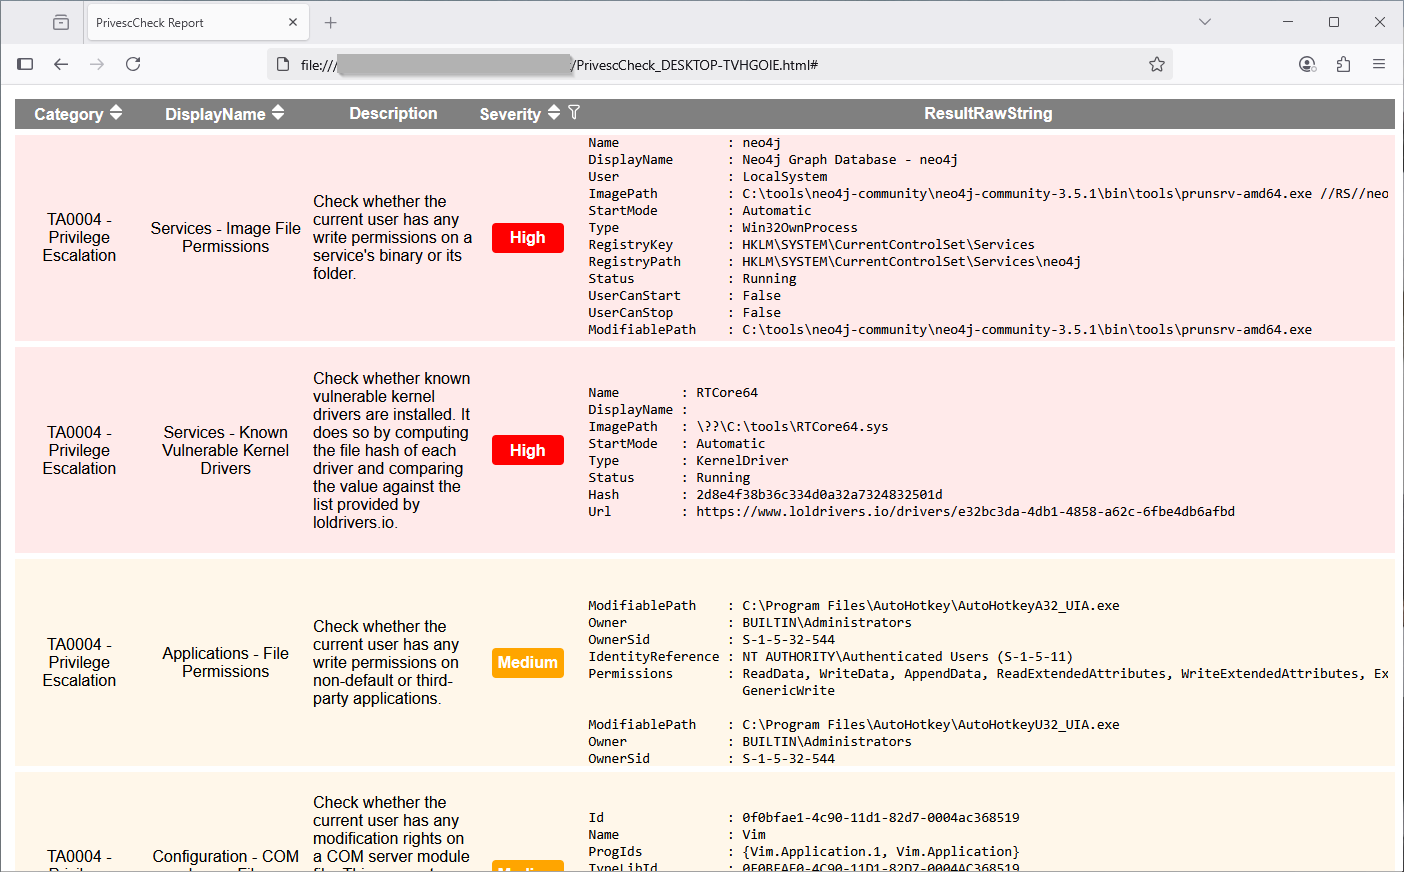 itm4n/privesccheck
Privilege Escalation Enumeration Script for Windows
 threekiii/awesome-redteam
一个攻防知识库。A knowledge base for red teaming and offensive security.
 bishopfox/sliver
Adversary Emulation Framework
 peass-ng/peass-ng
PEASS - Privilege Escalation Awesome Scripts SUITE (with colors)
 purpleailab/decepticon
Autonomous Hacking Agent for Red Team
 r0rt1z2/ghostlock
Kernel root exploit (CVE-2026-43499) for some Amazon devices