

custom-oscp-tooling
 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
database-securitydns-analysishash-analysis+9
wattocyber/custom-oscp-toolingOSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 mwr-cybersec/pxethief
PXEThief is a set of tooling that can extract passwords from the Operating System Deployment functionality in Microsoft Endpoint Configuration Manager
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
 s1ckb0y1337/cobalt-strike-cheatsheet
Some notes and examples for cobalt strike's functionality
 login-securite/lsassy
Extract credentials from lsass remotely
 safebreach-labs/poolparty
A set of fully-undetectable process injection techniques abusing Windows Thread Pools
 matthieu-hackwitharts/win32_offensive_cheatsheet
Win32 and Kernel abusing techniques for pentesters
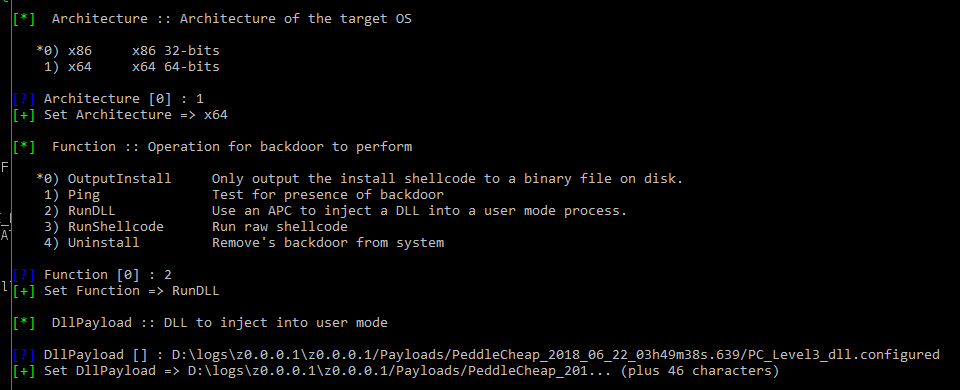 francisck/danderspritz_lab
A fully functional DanderSpritz lab in 2 commands
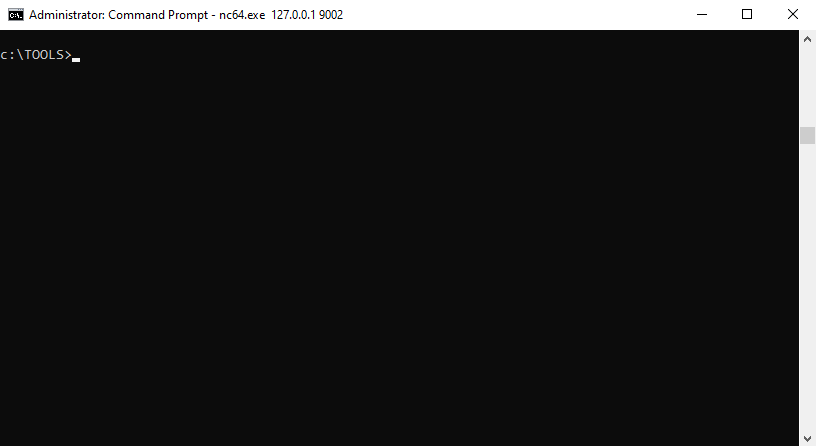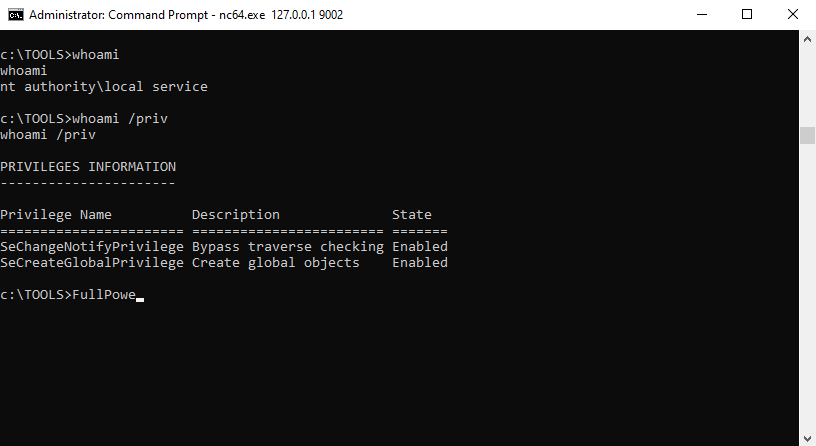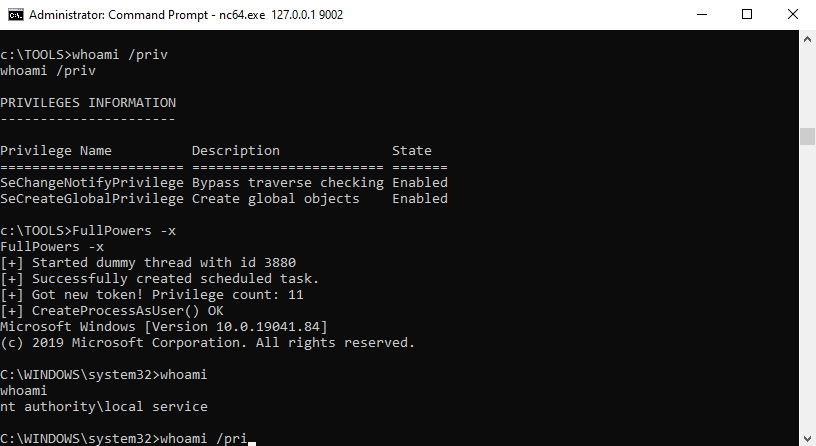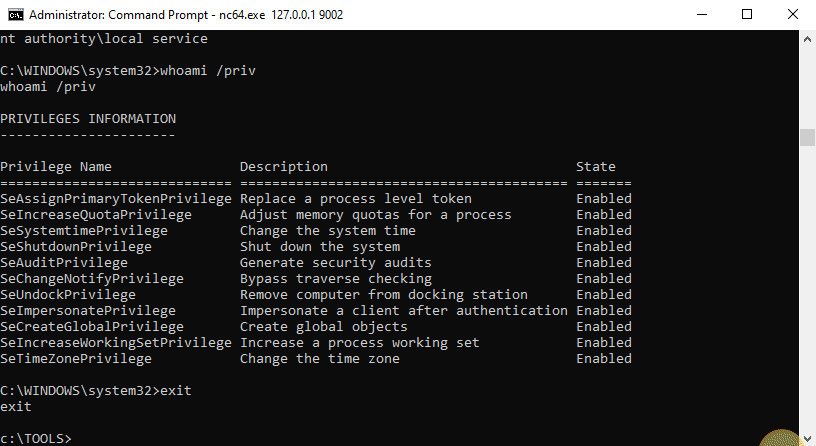 itm4n/fullpowers
Recover the default privilege set of a LOCAL/NETWORK SERVICE account
 thomasareed/pict
Modular incident response toolkit for collecting forensic data from potentially infected macOS endpoints, capturing browser artifacts, persistence…
 rad9800/tamperingsyscalls
C++ library that retrieves and spoofs Windows syscall arguments using hardware breakpoints and exception handlers to subvert EDR telemetry.
 t43wiu6/cve-2019-0887
exp for CVE-2019-0887
 twosevenonet/edrchoker
A tool uses the QoS Policy (Pacer.sys) to throttle Endpoint Detection and Response (EDR) agents from connecting to the server.
 dr4g0n23/cve-2020-1472
Exploit script for CVE-2020-1472 (ZeroLogon) with automated privilege escalation, credential dumping via secretsdump, and lateral movement using…