metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…

Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…

Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…

A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.

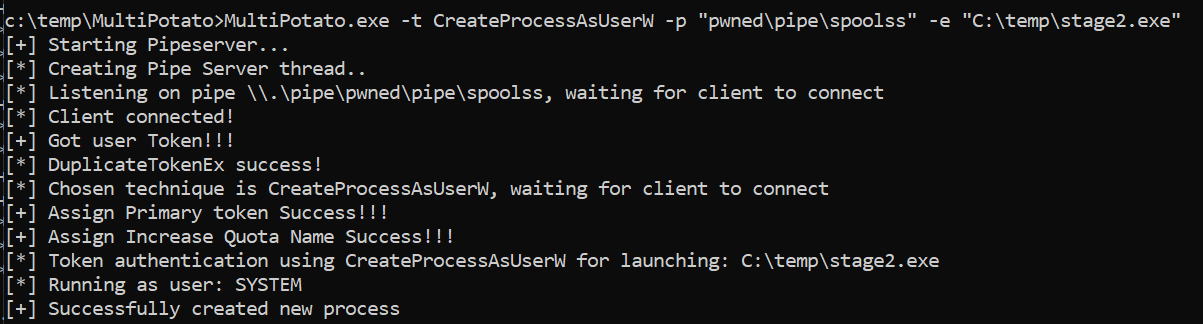
Windows privilege escalation tool exploiting SeImpersonate privileges via Named Pipe impersonation, supporting multiple execution methods…

CVE-2026-63030

A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself

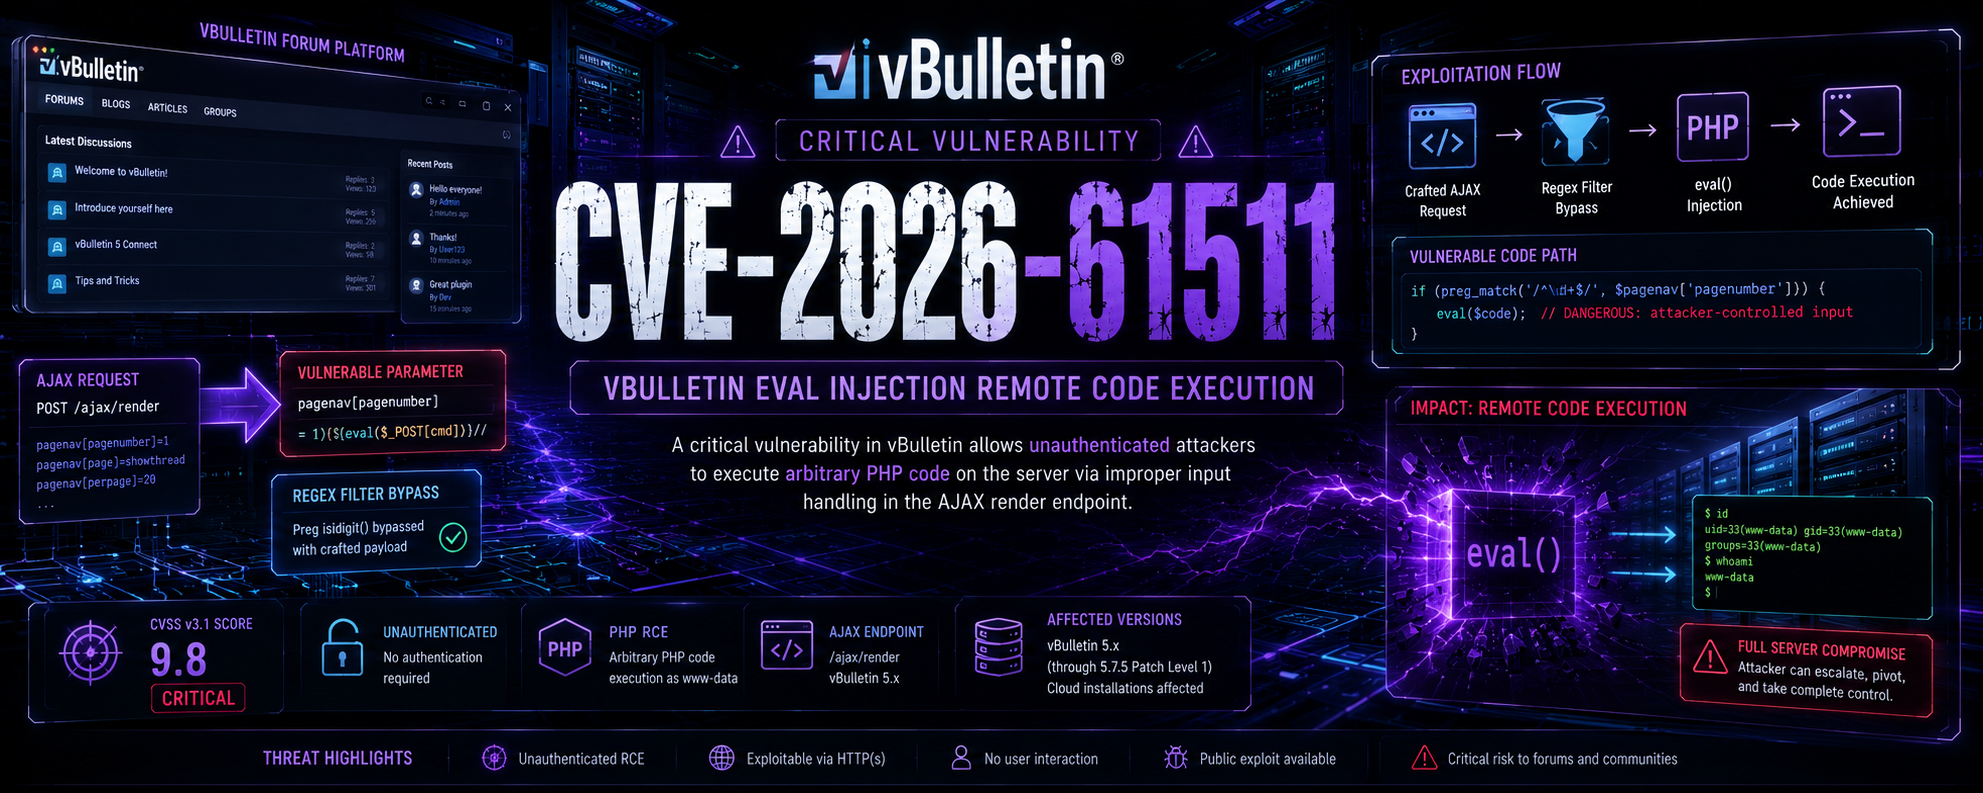
CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…

POCs to demonstrate CVE-2026-42167 in ProFTPD

Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…

mssql 终端连接工具|命令执行

MSSQL client for SCCM environments, enabling reconnaissance, remote PowerShell execution on managed clients, and extraction of sensitive secrets such…

Proof-of-concept exploit for CVE-2026-6471, demonstrating privilege escalation in PostgreSQL via logical decoding dlopen to achieve arbitrary code…

mssqlproxy is a toolkit aimed to perform lateral movement in restricted environments through a compromised Microsoft SQL Server via socket reuse

Practical MSSQL penetration testing cheat sheet covering enumeration, linked-server pivoting, privilege escalation, persistence, and command…

Offensive MSSQL toolkit written in Python, based off SQLRecon

An implementation of F5's `mcp` protocol, including MitM tooling to sniff traffic while vuln hunting