Purple-Team-Automation

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

Offset Independent Credential Extraction Tool

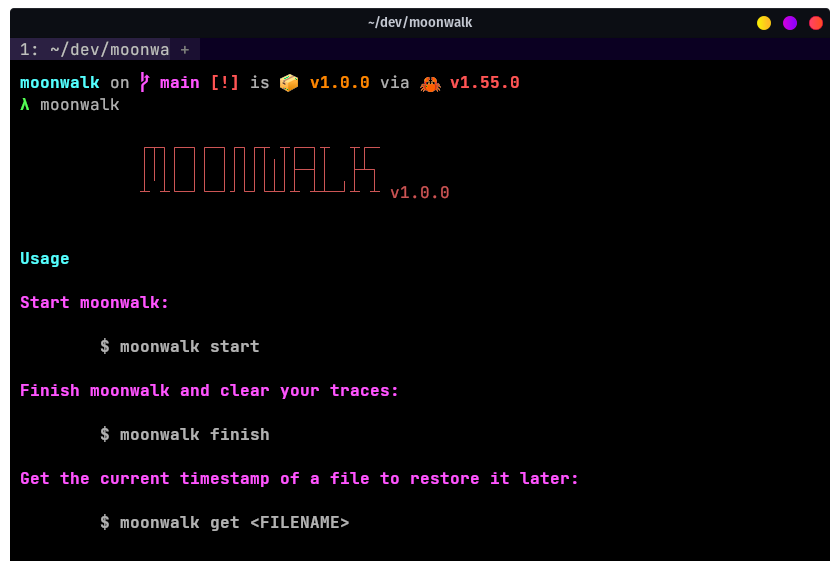
PowerShell tool for red teamers that clears execution evidence by stopping event logging, removing file and registry artifacts, and saving timestamps…

PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.

An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…

Anti Forensics Tool For Red Teamers, Used For Erasing Footprints In The Post Exploitation Phase.

CredsHunter - Credential Hunting scripts for Windows and Linux OS

A command-line utility for Windows written in C that creates and configures persistent Event Tracing for Windows (ETW) AutoLogger sessions.

Extract Windows credentials directly from VM memory snapshots and virtual disks

Post-Exploitation EVTX Analyzer for BloodHound Mapping

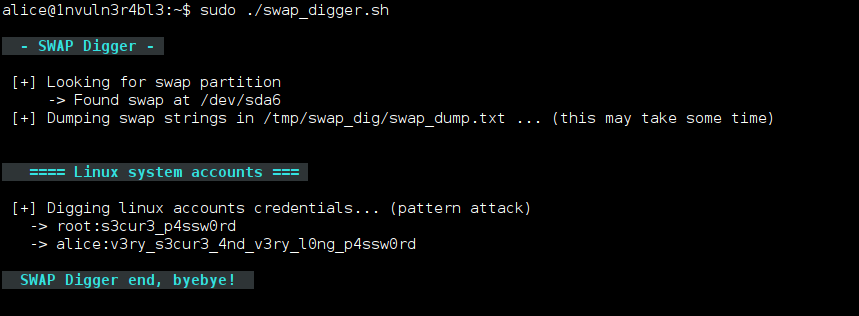
Automates Linux swap analysis to extract user credentials, web form data, WiFi keys, and HTTP authentication during post-exploitation or forensic…

A comprehensive educational repository demonstrating the evolution of a Windows reverse shell implant, from a simple proof‑of‑concept (v1.0) to a…

Cover your tracks during Linux Exploitation by leaving zero traces on system logs and filesystem timestamps.

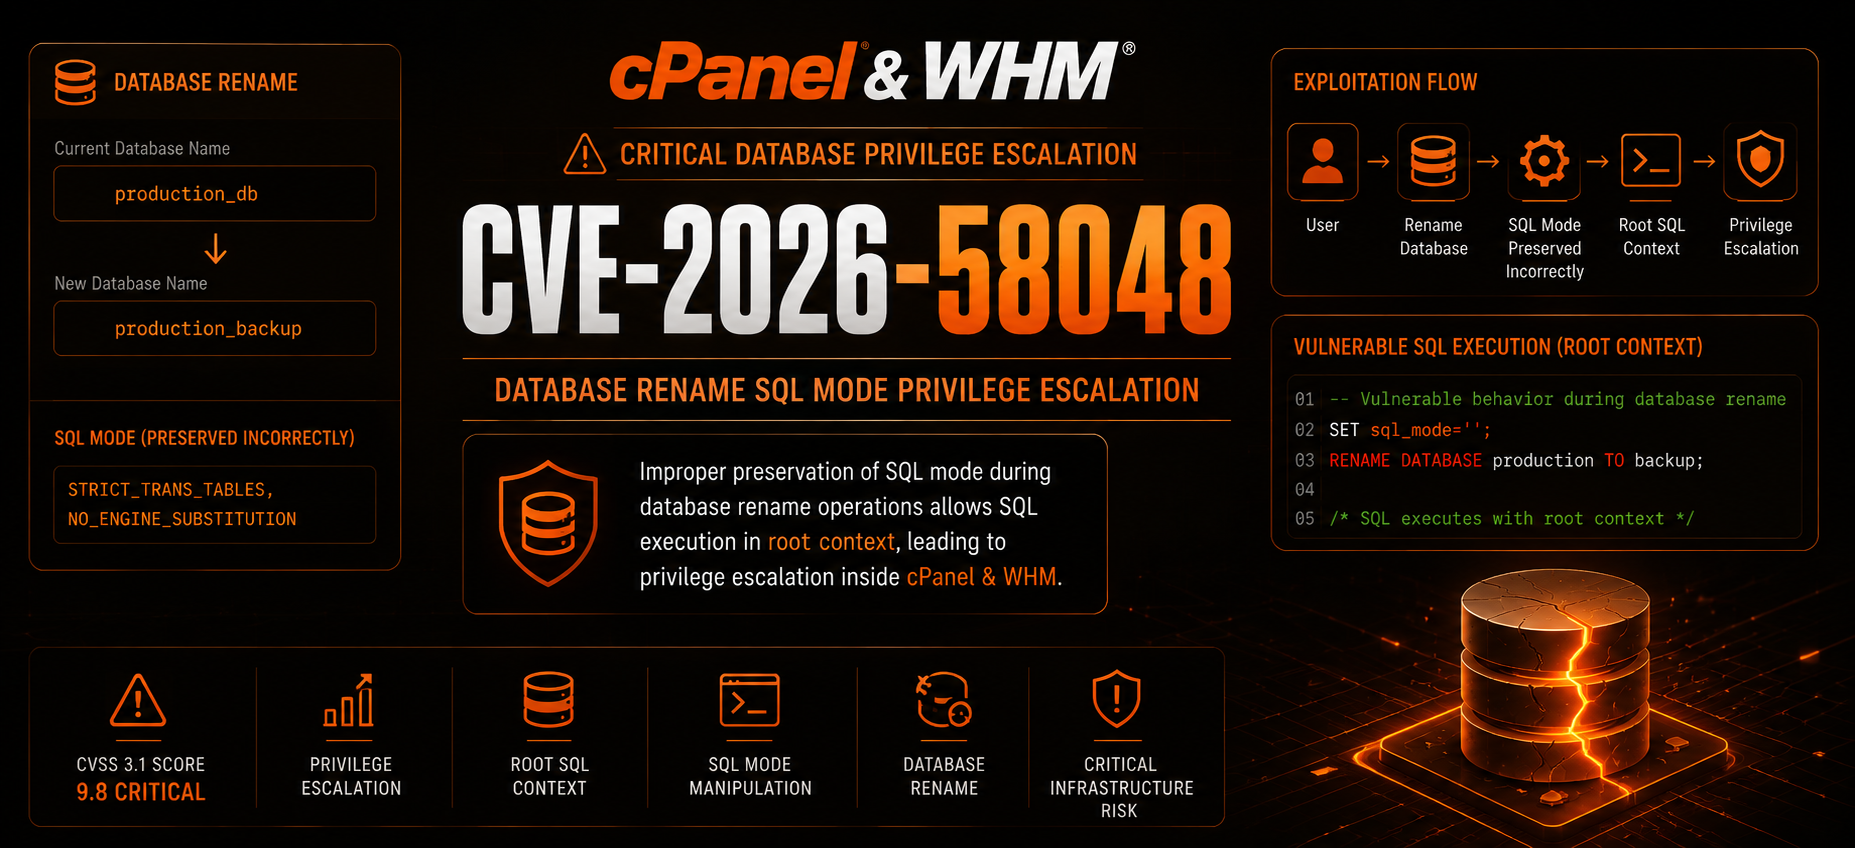
👾 CVE-2026-58048 – cPanel Root SQL Execution Toolkit (CVSS 9.4) | Full Red/Blue Team Toolkit suite for unpatched cPanel & WHM 11.x. 2 tools: Safe…

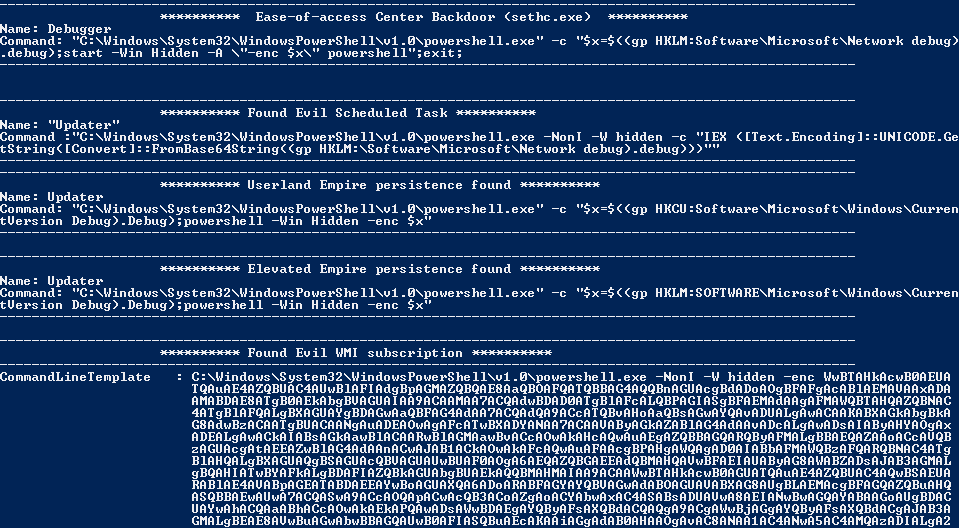
Powershell Empire Persistence finder

Create and enumerate hidden desktops.

Offline AI Security Assistant for Air-Gapped Pentesting