

BEAR-C2
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
adversarial-attackcommand-and-controldata-exfiltration+8
687
s3n4t0r-0x0/bear-c2The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 bishopfox/sliver
Adversary Emulation Framework
 ivancabrera02/hashsiphon
Extracts the current user's NetNTLMv2 hash via HTTP authentication proxying, avoiding direct SSPI calls; v2 delegates auth to the BITS service to…
 3v4si0n/http-revshell
Powershell reverse shell using HTTP/S protocol with AMSI bypass and Proxy Aware
 synacktiv/prox-ez
HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…
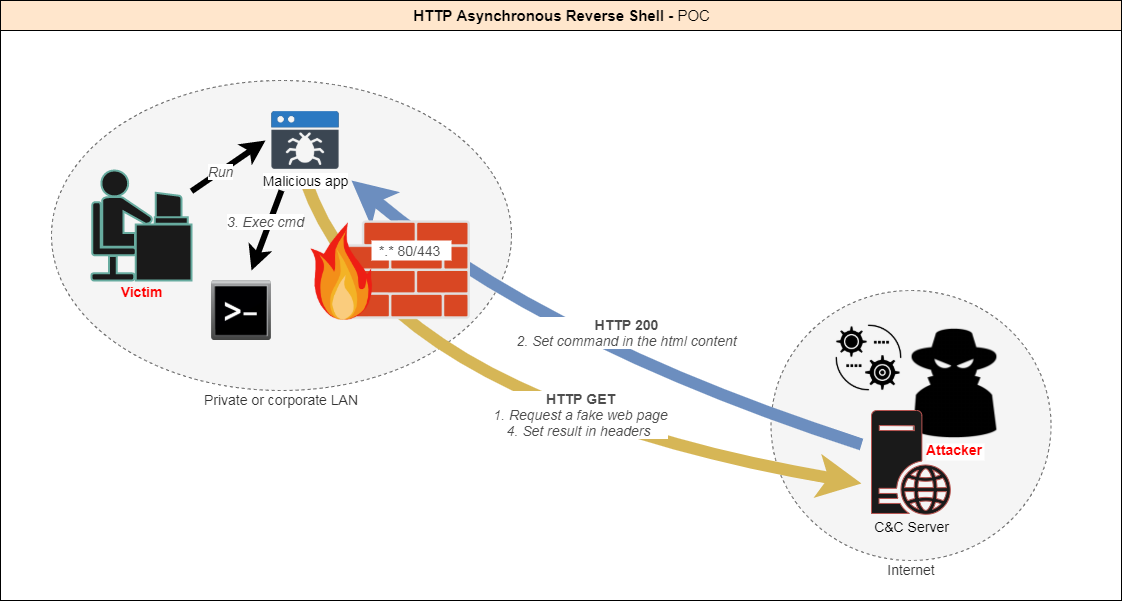 onsec-fr/http-asynchronous-reverse-shell
[POC] Asynchronous reverse shell using the HTTP protocol.
 nccgroup/fenrir
PoC to tunnel the Meterpreter reverse HTTP shell over RDP Virtual Channels
 lexfo/sshimpanzee
SSHD Based implant supporting tunneling mecanisms to reach the C2 (DNS, ICMP, HTTP Encapsulation, HTTP/Socks Proxies, UDP...)

 jephthai/evilvm
Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
 davidtavarez/pinky
pinky - The PHP mini RAT (Remote Administration Tool)
 e4zyy/project-cve-2026-33017
CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
 mr-un1k0d3r/thundershell
Python / C# Unmanaged PowerShell based RAT
 abdurahmon3236/cve-2024-38472
Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
 synacktiv/sccm_sql_backdoor
Exploit CVE-2024-43468 and CVE-2025-59213 to implant a controlled backdoor into SCCM Management Point's SQL stored procedure, enabling remote SQL…
 sensepost/regeorg
The successor to reDuh, pwn a bastion webserver and create SOCKS proxies through the DMZ. Pivot and pwn.
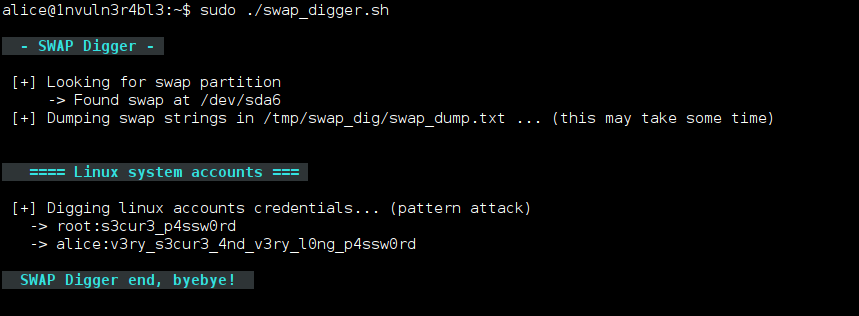 sevagas/swap_digger
Automates Linux swap analysis to extract user credentials, web form data, WiFi keys, and HTTP authentication during post-exploitation or forensic…
 gr1mmie/atlasc2
C# C2 Framework centered around Stage 1 operations