

Blackbone
 darthton/blackbone
Windows memory hacking library
binary-analysisdebuggersdynamic-analysis-sandboxing+9
darthton/blackboneWindows memory hacking library
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 oddcod3/phantom-evasion
Python antivirus evasion tool
 nccgroup/mnemosyne
A Generic Windows Memory Scraping Tool
 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
 gmh5225/driver-kaldereta
Unsigned Kernel Mode Driver that does memory modifications
 gmh5225/driver-pidqserializationwrite-example
How to use PiDqSerializationWrite. Introduces how to safely read and write from mapped driver
 q1f3/triple_fetch
This is an exploit for CVE-2017-7047, Works on 10.3.2 and below.
 gmh5225/kernelmode-driver
Kernel Driver for x64 Window System which allows you to read/write Virtual/Physical Memory hooking Win32k
 fuzzysecurity/powershell-suite
My musings with PowerShell
 illegal-instruction-co/processhacker-mcp
Runtime process analysis and memory hacking MCP server for AI agents. Supports dynamic extension loading, read-only mode, audit logging, and…
 ivancabrera02/whfb-pincapture
Captures Windows Hello PINs at entry by injecting a DLL into LogonUI.exe that sets a CPU hardware breakpoint on NgcSerializeConvenienceCredential,…
 rad9800/hwbp4mw
Hardware breakpoint hooking engine for Windows that uses debug registers to hook functions, bypass ETW/AMSI, and evade user-land EDR monitoring.
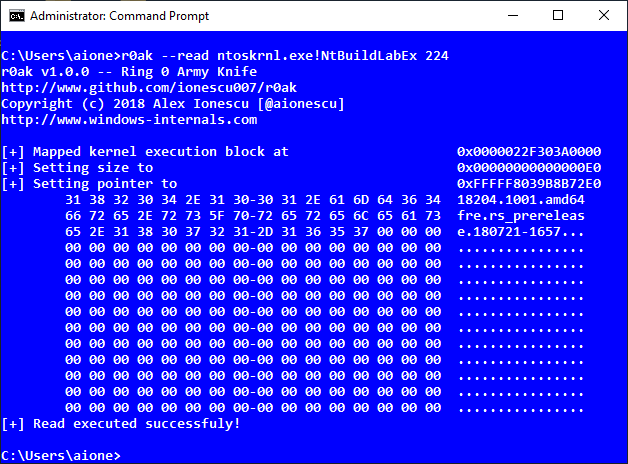 harryanon/r0ak
Windows command-line utility for reading, writing, and executing kernel-mode code from Administrator context using a font validation execution…
 whokilleddb/psi_bof
A BOF designed to inspect processes memory and addresses