

RustScan
 bee-san/rustscan
🤖 The Modern Port Scanner 🤖
network-mappingpenetration-testingport-scanning+3
bee-san/rustscan🤖 The Modern Port Scanner 🤖
 dmontgomery40/pentest-mcp
NOT for educational purposes: An MCP server for professional penetration testers including STDIO/HTTP/SSE support, nmap, go/dirbuster, nikto, JtR,…
 enenumxela/ps.sh
A bash script that automates port scanning on specified target host(s). The aim of the scripts is reducing scan time, increasing scan efficiency and…
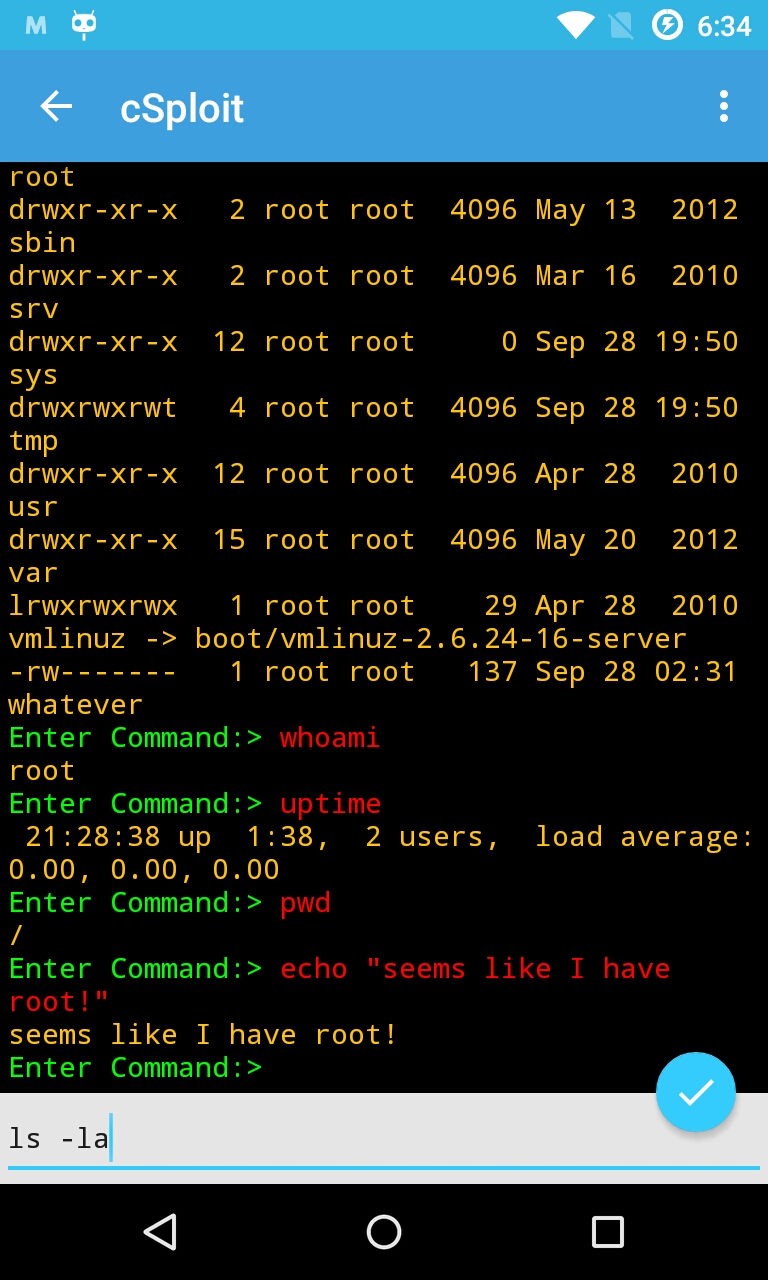 csploit/android
cSploit - The most complete and advanced IT security professional toolkit on Android.
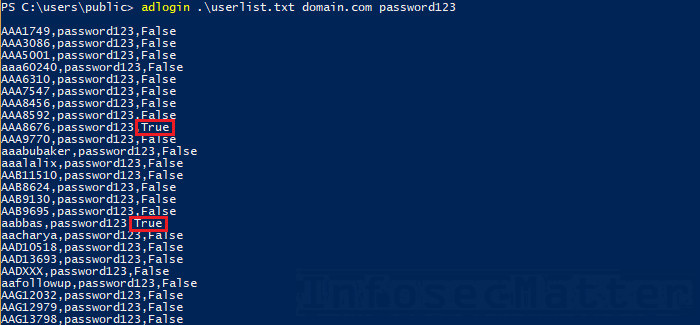 infosecmatter/minimalistic-offensive-security-tools
A repository of tools for pentesting of restricted and isolated environments.
 blindfuzzy/lhf
A modular recon tool for pentesting
 azmisyahrul/prismsec
Secure, modular MCP server wrapping nmap, nuclei, gobuster, subfinder, httpx, nikto, sqlmap for AI-powered pentesting
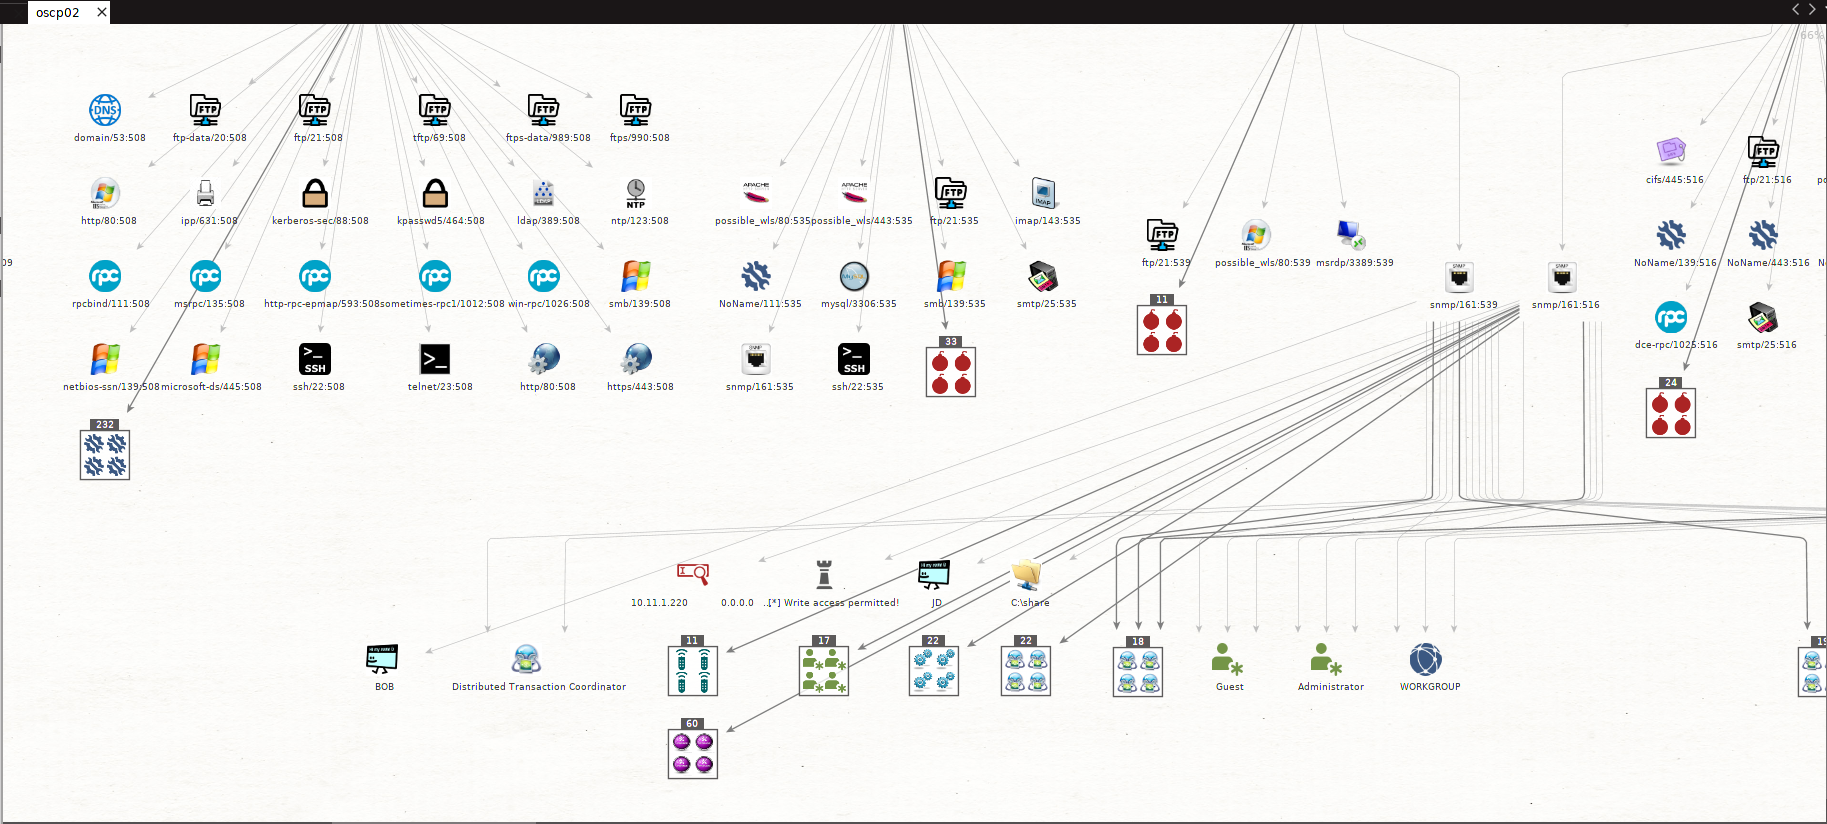 shizzz477/msploitego
Pentesting suite for Maltego based on data in a Metasploit database
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 lazorfuzz/python-hacklib
hacklib - pentesting, port scanning, and logging in anywhere with Python
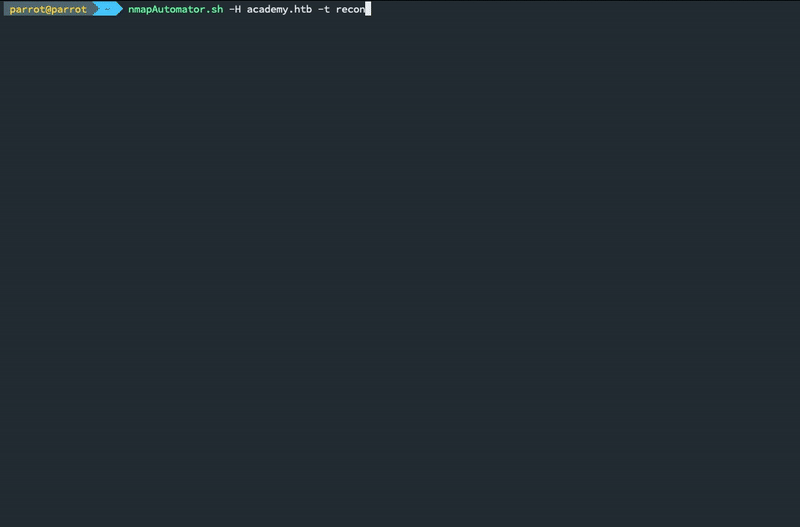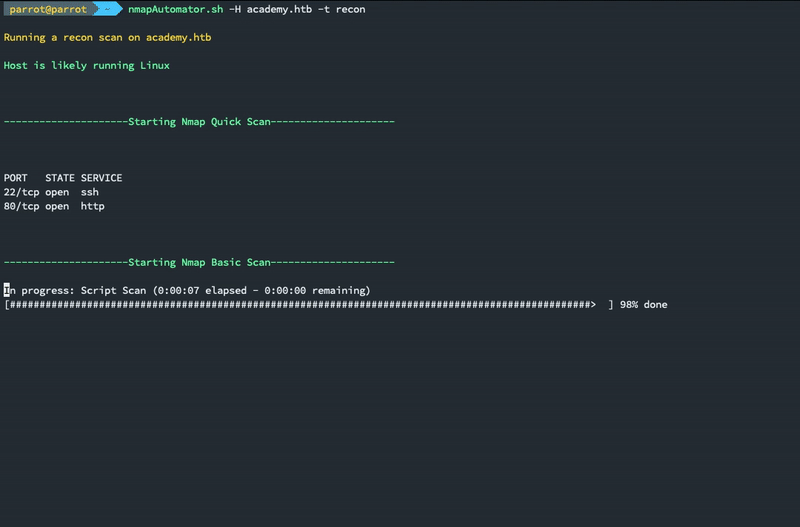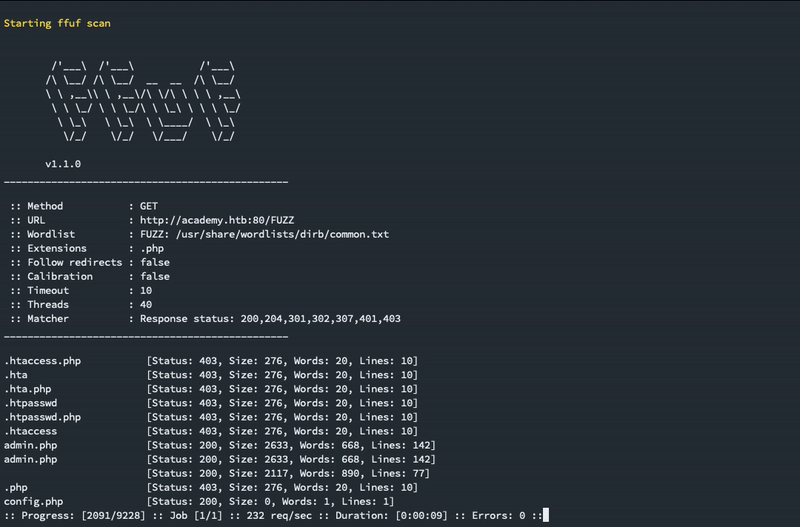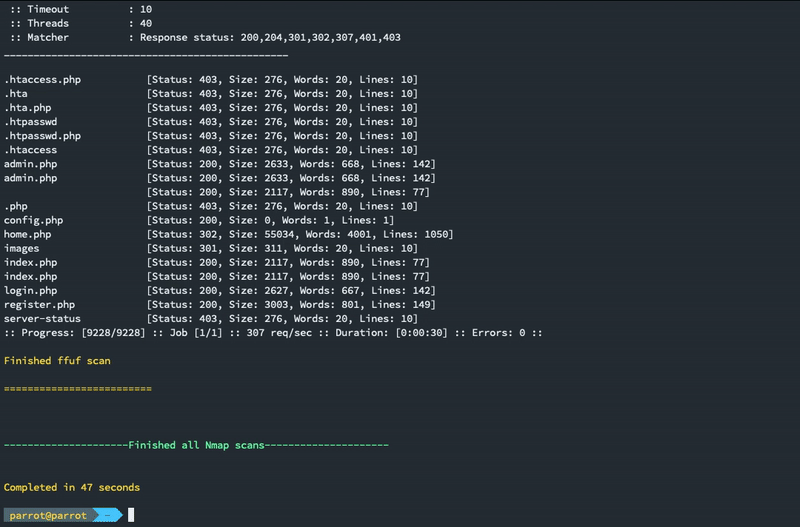 21y4d/nmapautomator
A script that you can run in the background!
 nu11secur1ty/nmap-cheat-sheet
Curated cheat sheet for Nmap, covering target selection, port scanning, service/OS detection, NSE scripts, and output formats for network…
 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
 praetorian-inc/nerva
Fast service fingerprinting CLI for 170+ protocols (TCP/UDP/SCTP) - built by Praetorian
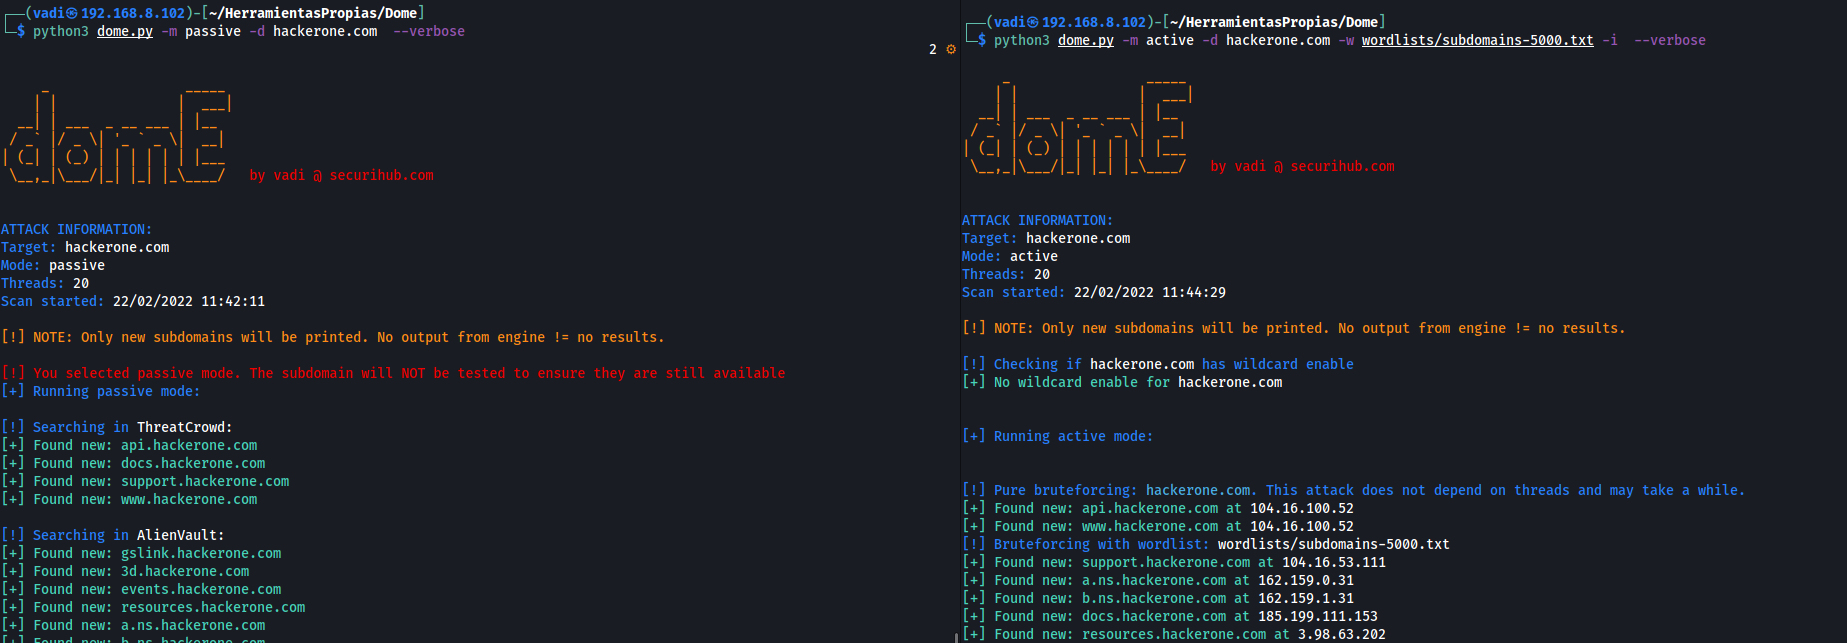 v4d1/dome
Fast Python-based subdomain enumeration tool combining passive OSINT and active brute-force scanning with DNS wildcard detection, port scanning, and…
 ginjachris/pentmenu
A bash script for recon and DOS attacks
 alechilczenko/kimi
Attack Surface Discovery tool built on a microservice approach, utilizing multi-threading for fast, internet-scale asset indexing
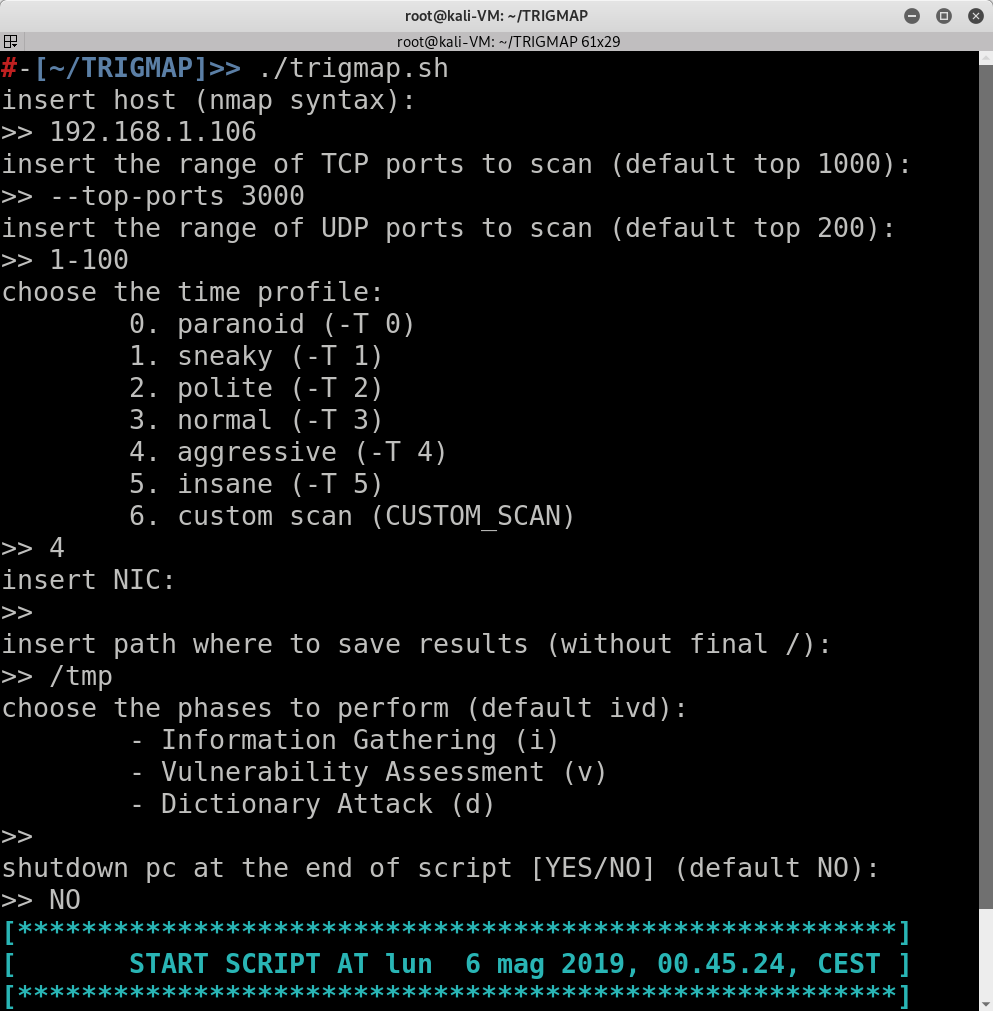 leviathan36/trigmap
A wrapper for Nmap to quickly run network scans