
CVE-2019-5544_CVE-2020-3992
 hynekpetrak/cve-2019-5544_cve-2020-3992
Python / scapy module implementing SRVLOC/SLP protocol and scans for enabled OpenSLP services.
exploitationinformation-gatheringnetwork-mapping+3
50
hynekpetrak/cve-2019-5544_cve-2020-3992Python / scapy module implementing SRVLOC/SLP protocol and scans for enabled OpenSLP services.
 j0ey17/exploit_cve-2023-27163
Proof of Concept exploit for Server Side Request Forgery vulnerability in Requests Basket v1.2.1 and before.
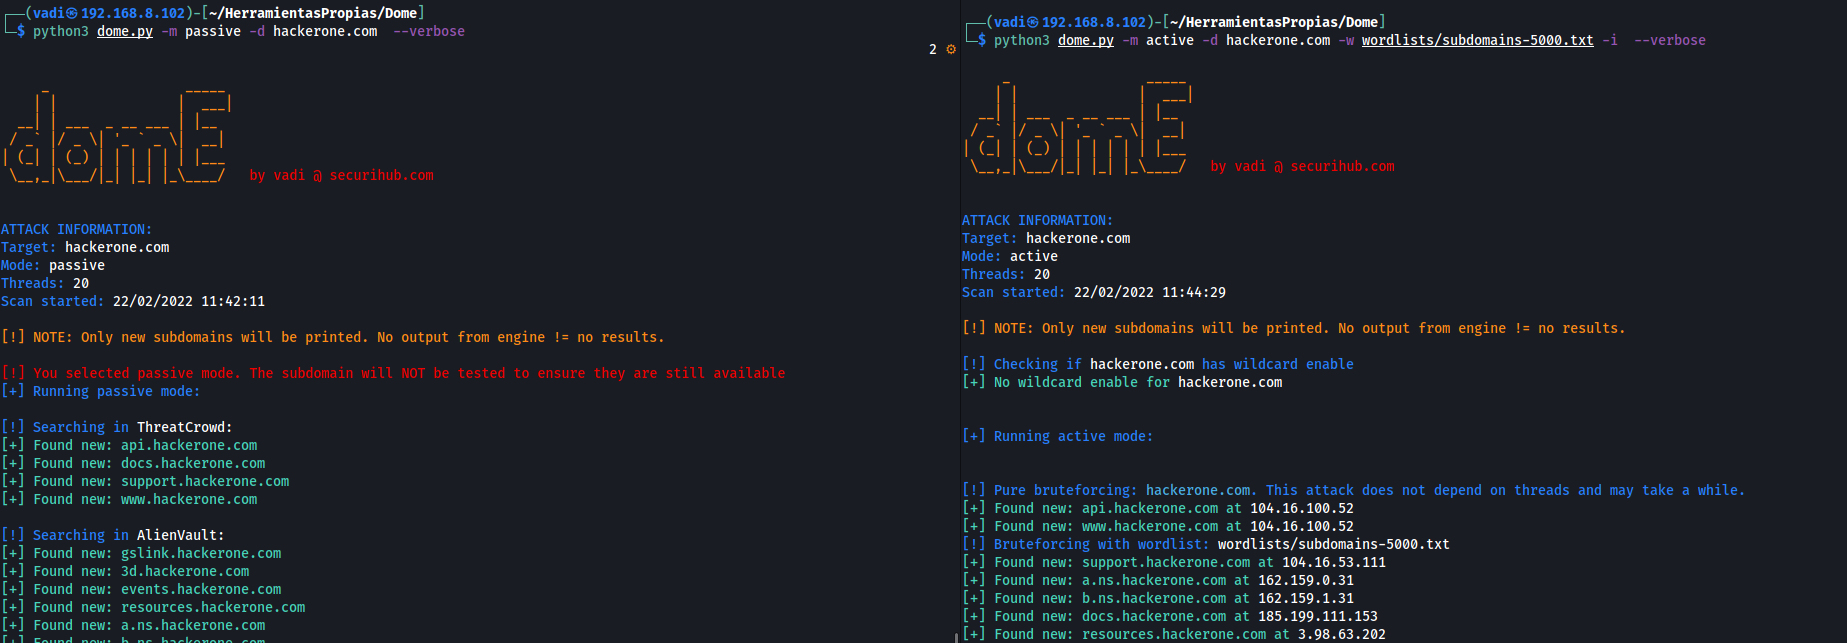 v4d1/dome
Fast Python-based subdomain enumeration tool combining passive OSINT and active brute-force scanning with DNS wildcard detection, port scanning, and…
 thegenetic/cve-2024-6387-exploit
CVE-2024-6387 exploit
 achux21/checker-cve-2024-6387
Python scanner that checks hosts for the OpenSSH regreSSHion vulnerability (CVE-2024-6387)
 shivamrai2003/reconky-automated_bash_script
Reconky is an great Content Discovery bash script for bug bounty hunters which automate lot of task and organized in the well mannered form which…
 m0usem0use/erl_mouse
python script to find vulnerable targets of CVE-2025-32433
 peco602/findwall
Check if your provider is blocking you!
 chrizator/netattack2
An advanced network scan and attack script based on GUI. 2nd version of no-GUI netattack.
 yunuscadirci/callstranger
Vulnerability checker for Callstranger (CVE-2020-12695)
 exfil0/cve-2024-55591-poc
A comprehensive all-in-one Python-based Proof of Concept script to discover and exploit a critical authentication bypass vulnerability…
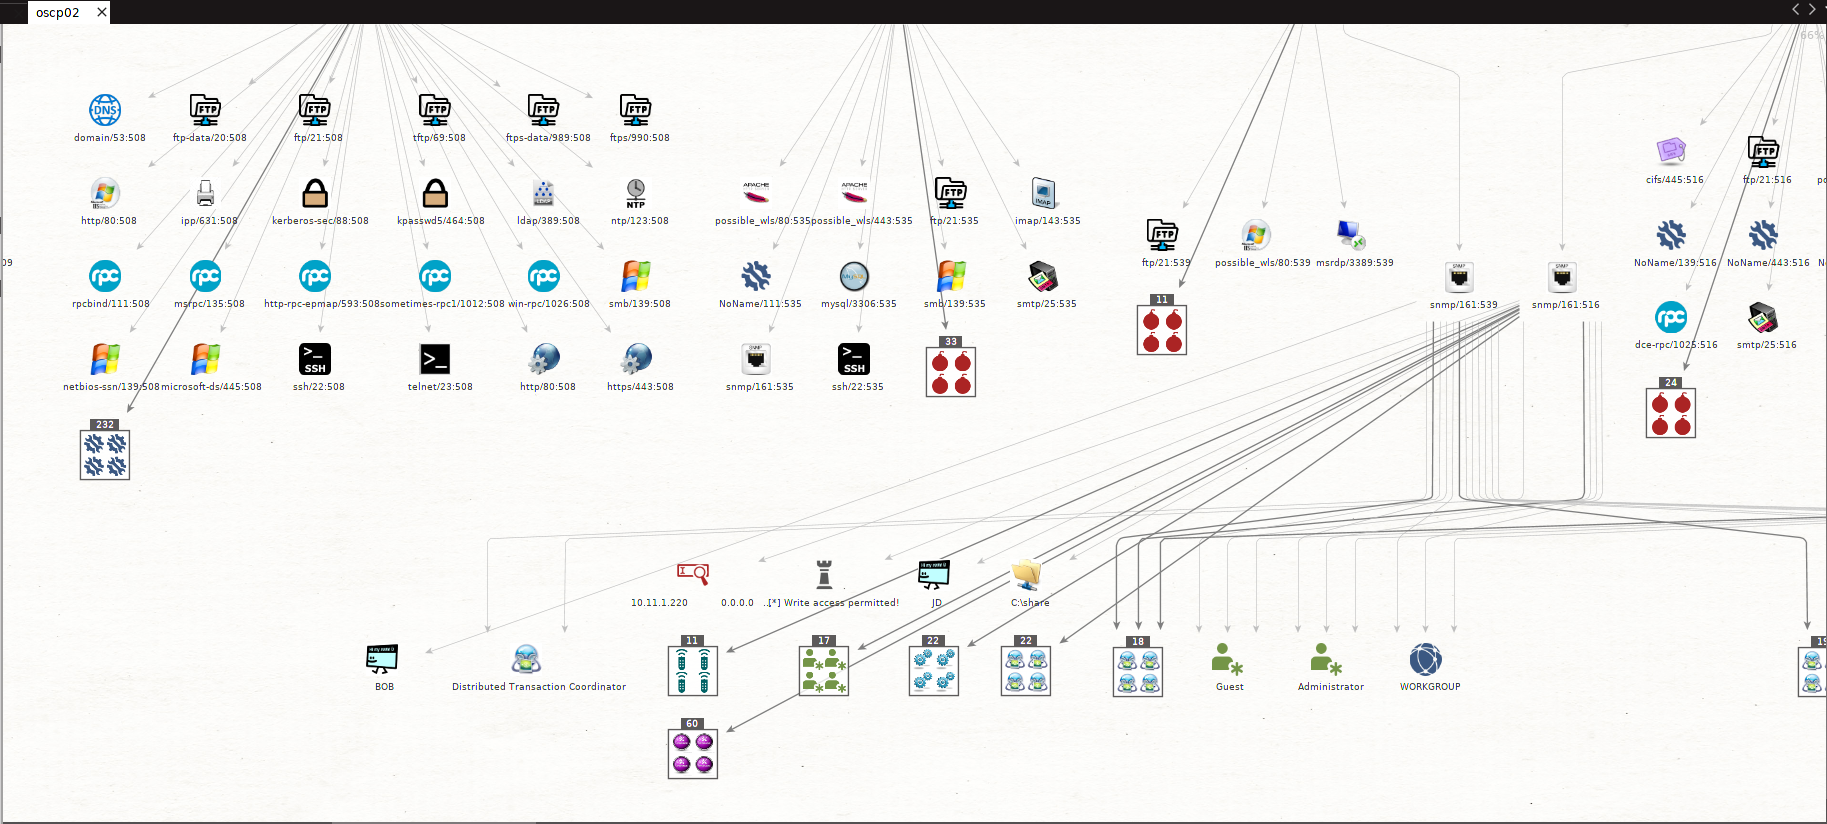 shizzz477/msploitego
Pentesting suite for Maltego based on data in a Metasploit database
 manisso/fsociety
fsociety Hacking Tools Pack – A Penetration Testing Framework
 rxerium/bug-bounty-tools
A BASH Script to automate the installation of the most popular bug bounty tools
 enenumxela/ps.sh
A bash script that automates port scanning on specified target host(s). The aim of the scripts is reducing scan time, increasing scan efficiency and…
 r4tw1z/cve-2024-6387
This script, created by R4Tw1z, is designed to scan IP addresses to check if they are running a potentially vulnerable version of OpenSSH. The tool…
 rv4l3r3/log4v-vuln-check
This script is used to perform a fast check if your server is possibly affected by CVE-2021-44228 (the log4j vulnerability).
 nccgroup/port-scan-automation
Automate NMAP Scans and Generate Custom Nessus Policies Automatically