Jozini-network-scanner

Python-based network scanner with port scanning, banner grabbing, and RouterOS CVE mapping for vulnerability identification and reporting.

Python-based network scanner with port scanning, banner grabbing, and RouterOS CVE mapping for vulnerability identification and reporting.

An autonomous reflective Go agent for full-cycle security auditing, WAF evasion, OOB LDAP verification, self-remediation (auto-patching), and…

A repository of tools for pentesting of restricted and isolated environments.


Check if your provider is blocking you!

Pivot your way deeper into computer networks with SSH compromised machines.

Сollection of TCL scripts for Cisco IOS penetration testing

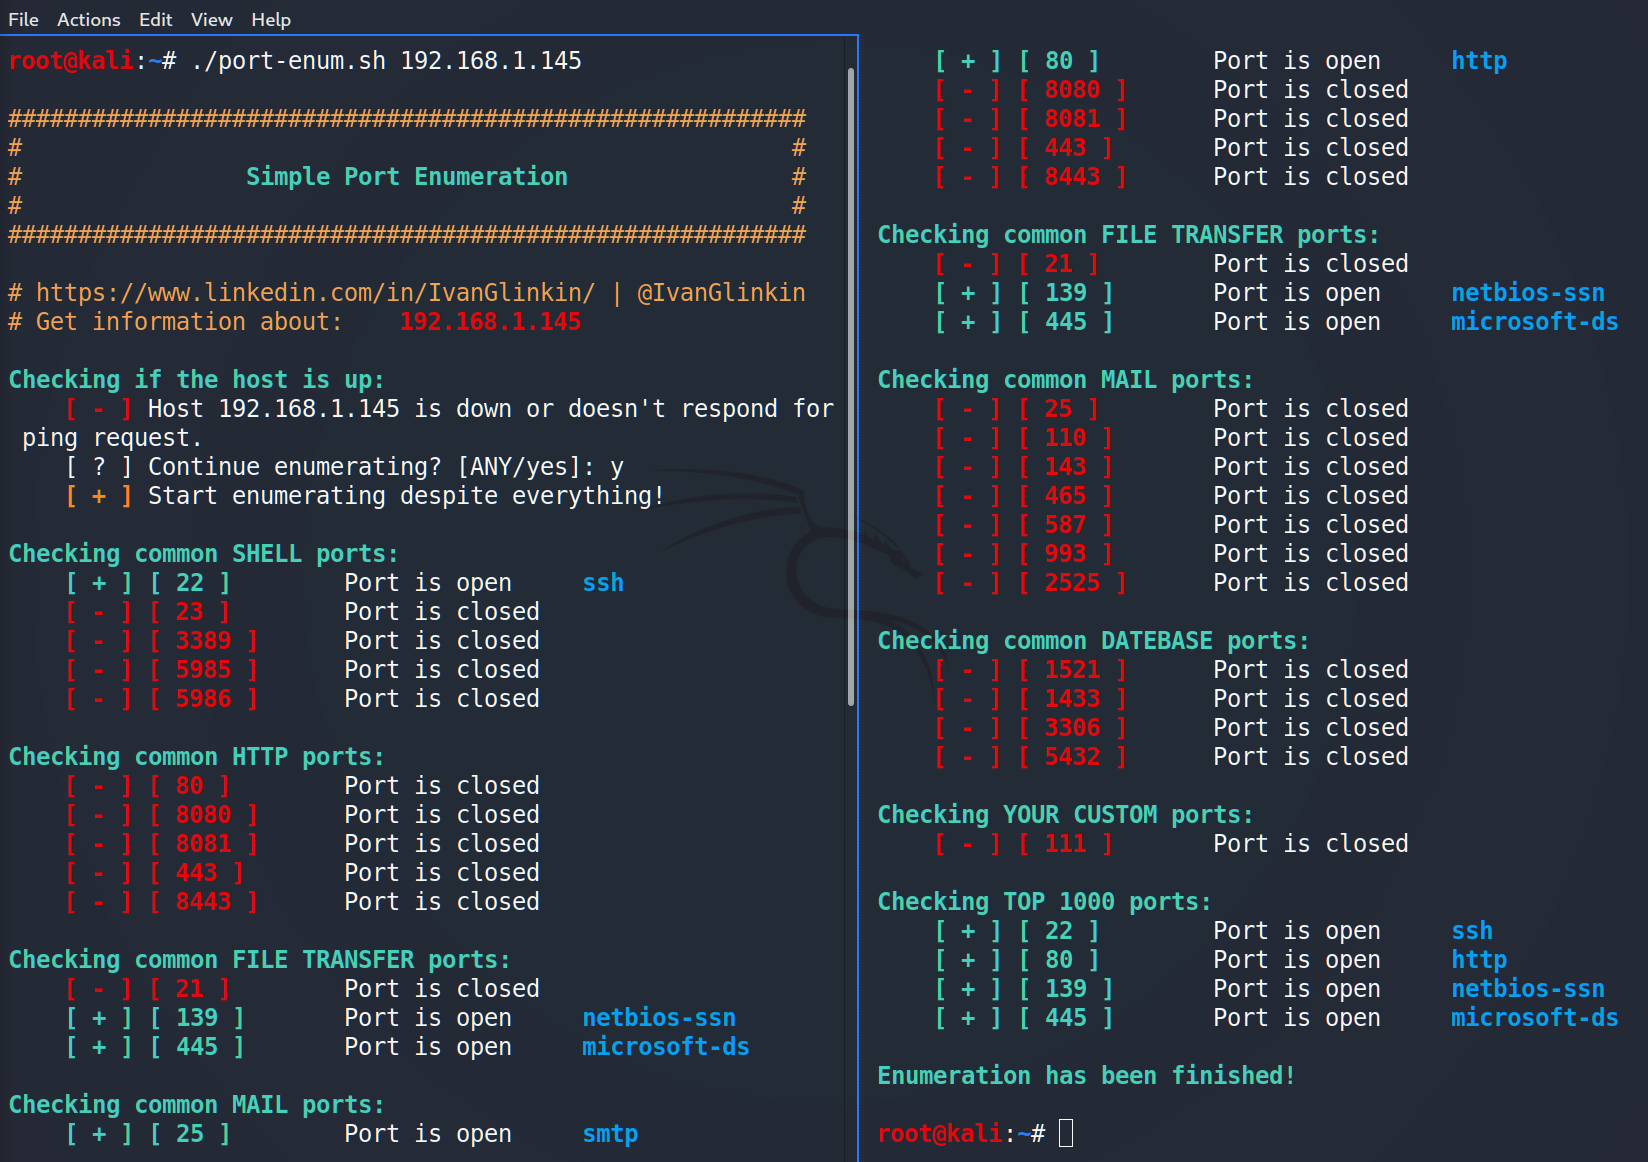
Have you ever faced with the lack of possibility of using NMap? For instance if you have reverse shell as an unprivileged user and there are no…

A fast, customizable service detection tool powered by a flexible fingerprint system. It helps you identify services, APIs, and network…

A third-party Gopher Assassin for the Havoc Framework.

CVE-2024-6387 exploit

A tool to perform port scanning using vulnerable Request-Baskets

Sunflower CVE-2022-10270 vulnerability exploitation tool

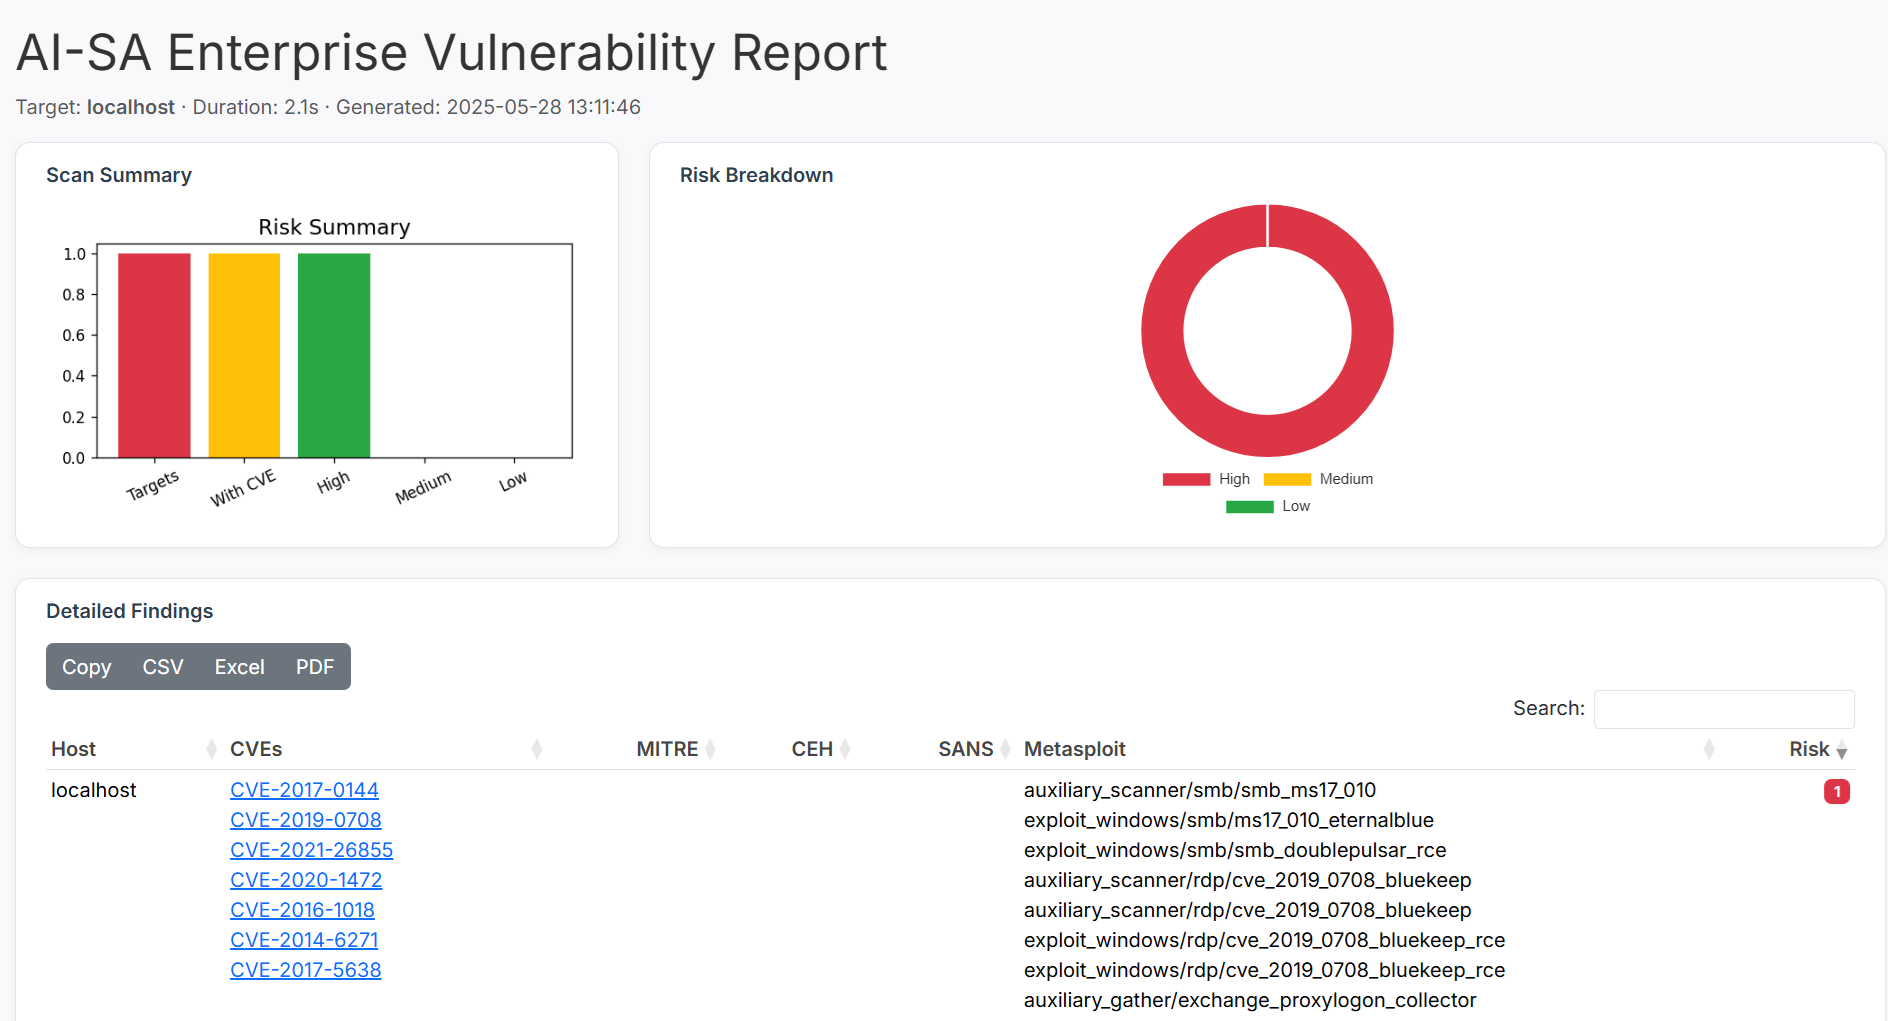
AISA-Scanner is an AI-powered autonomous vulnerability scanner that maps CVEs to metasploit exploits, MITRE, CEH, and SANS, delivering intelligent,…

Python scanner that checks hosts for the OpenSSH regreSSHion vulnerability (CVE-2024-6387)

Script to exploit CVE-2018-1042 in order to do internal port scans.

Authorized high-impact tool from CYBERDUDEBIVASH ECOSYSTEM to detect CVE-2025-64155 (FortiSIEM phMonitor Command Injection). Scans for open ports and…