
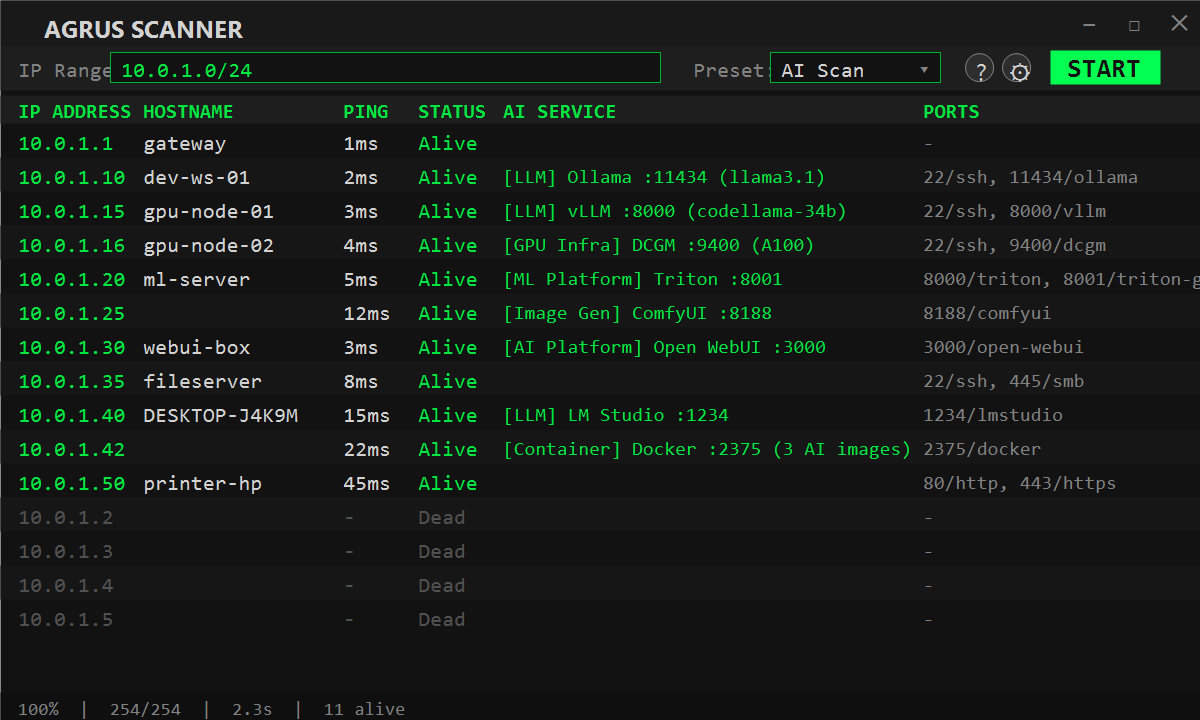
AgrusScanner
 nybaywatch/agrusscanner
Windows network reconnaissance scanner with ping sweeps, TCP port scanning, and deep AI/ML service detection for finding shadow AI, rogue LLM…
ai-securitydefensive-toolsinformation-gathering+6
28
nybaywatch/agrusscannerWindows network reconnaissance scanner with ping sweeps, TCP port scanning, and deep AI/ML service detection for finding shadow AI, rogue LLM…
 darkrx1/rxscan
Rust CLI for bounded network reconnaissance: TCP/UDP port discovery, service identification, DNS/TLS/HTTP evidence collection, and public-source…
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
 mindedsecurity/behave
Behave! A monitoring browser extension for pages acting as "bad boi"
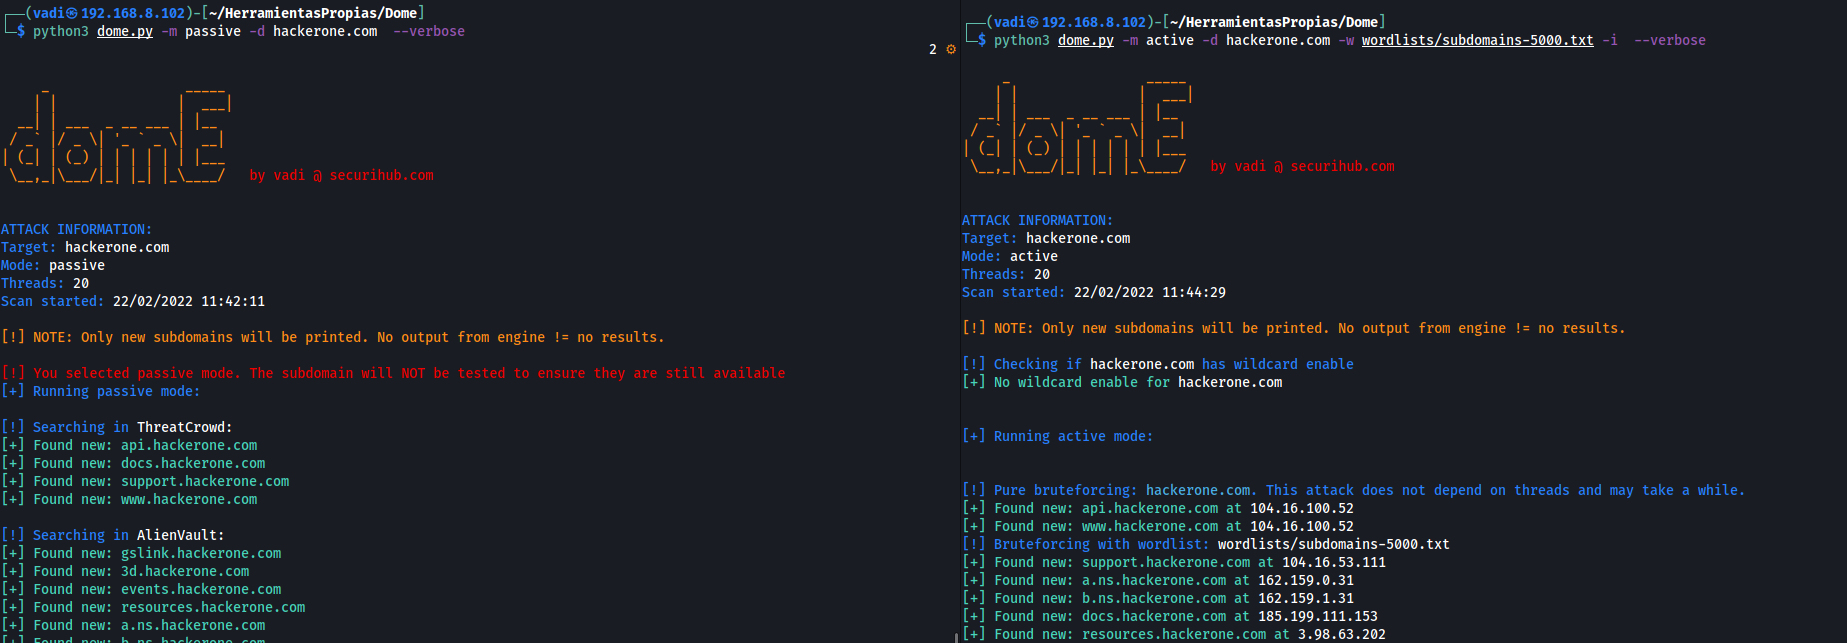 v4d1/dome
Fast Python-based subdomain enumeration tool combining passive OSINT and active brute-force scanning with DNS wildcard detection, port scanning, and…
 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
 praetorian-inc/nerva
Fast service fingerprinting CLI for 170+ protocols (TCP/UDP/SCTP) - built by Praetorian
 yeee3642/edu-recon
Authorized education-sector recon & triage orchestrator (nmap/dirsearch/sqlmap/hydra + CVE-2024-4577, secret/API-key leak, XSS, wp2shell) with a web…
 k3ystr0k3r/mikrotik-winbox-scanner
Winbox Protocol Scanner (MikroTik RouterOS)

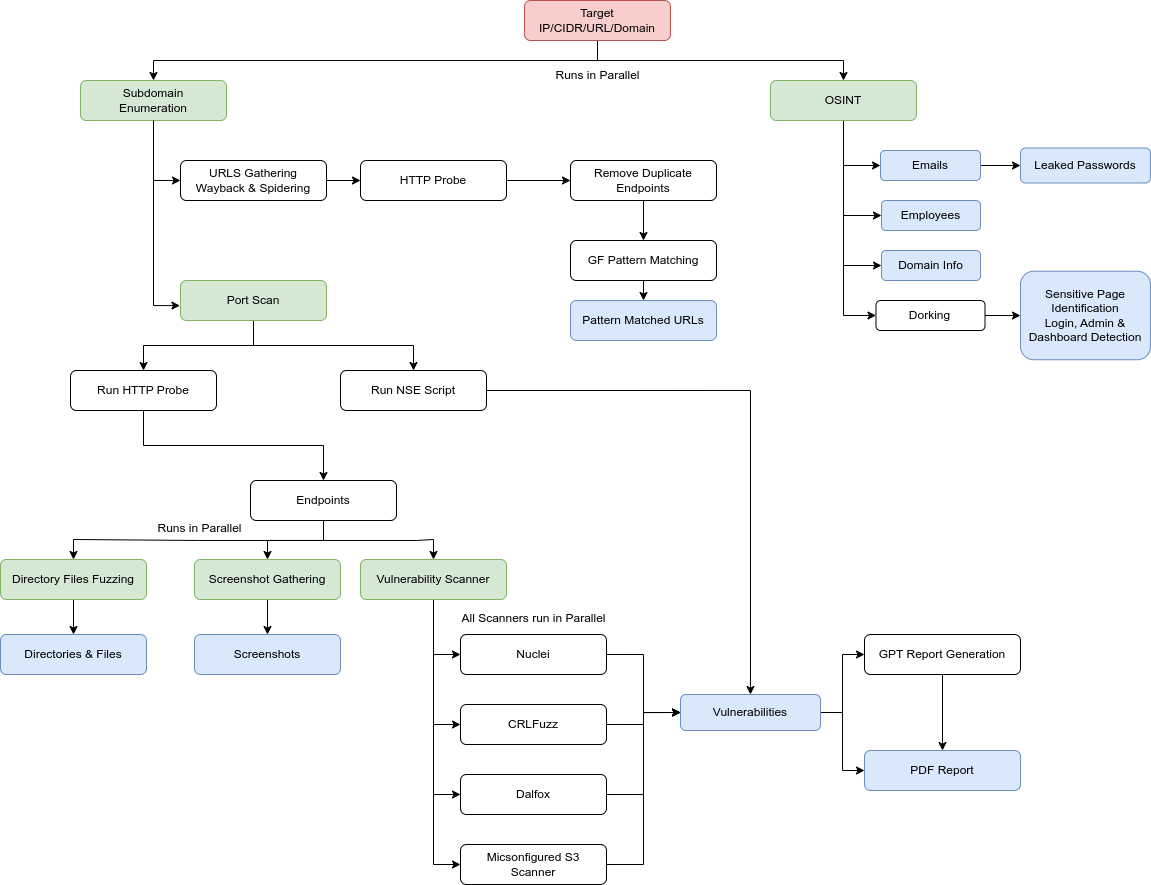 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
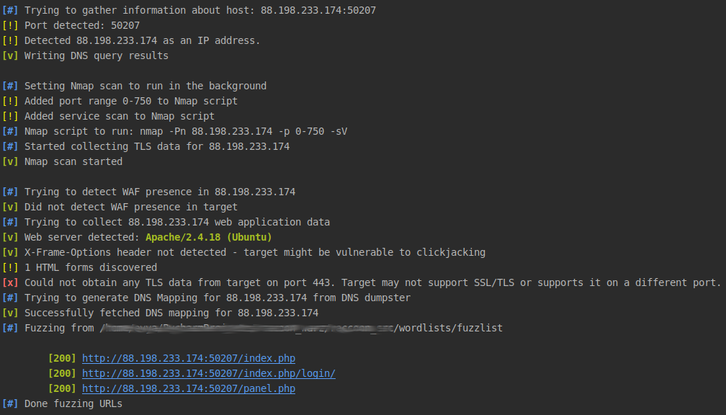 evyatarmeged/raccoon
A high performance offensive security tool for reconnaissance and vulnerability scanning
 thewhiteh4t/finalrecon
Automated web reconnaissance tool providing header analysis, DNS enumeration, subdomain discovery, directory scanning, SSL inspection, and port…
 chvancooten/bugbountyscanner
A Bash script and Docker image for Bug Bounty reconnaissance. Intended for headless use.
 r3vn/badkarma
network reconnaissance toolkit
 maldevel/intelspy
Perform automated network reconnaissance scans
 mr-rizwan-syed/chomtesh
CHOMTE.SH is a powerful shell script designed to automate reconnaissance tasks during penetration testing. It utilizes various Go-based tools to…
 six2dez/reconftw
reconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…