
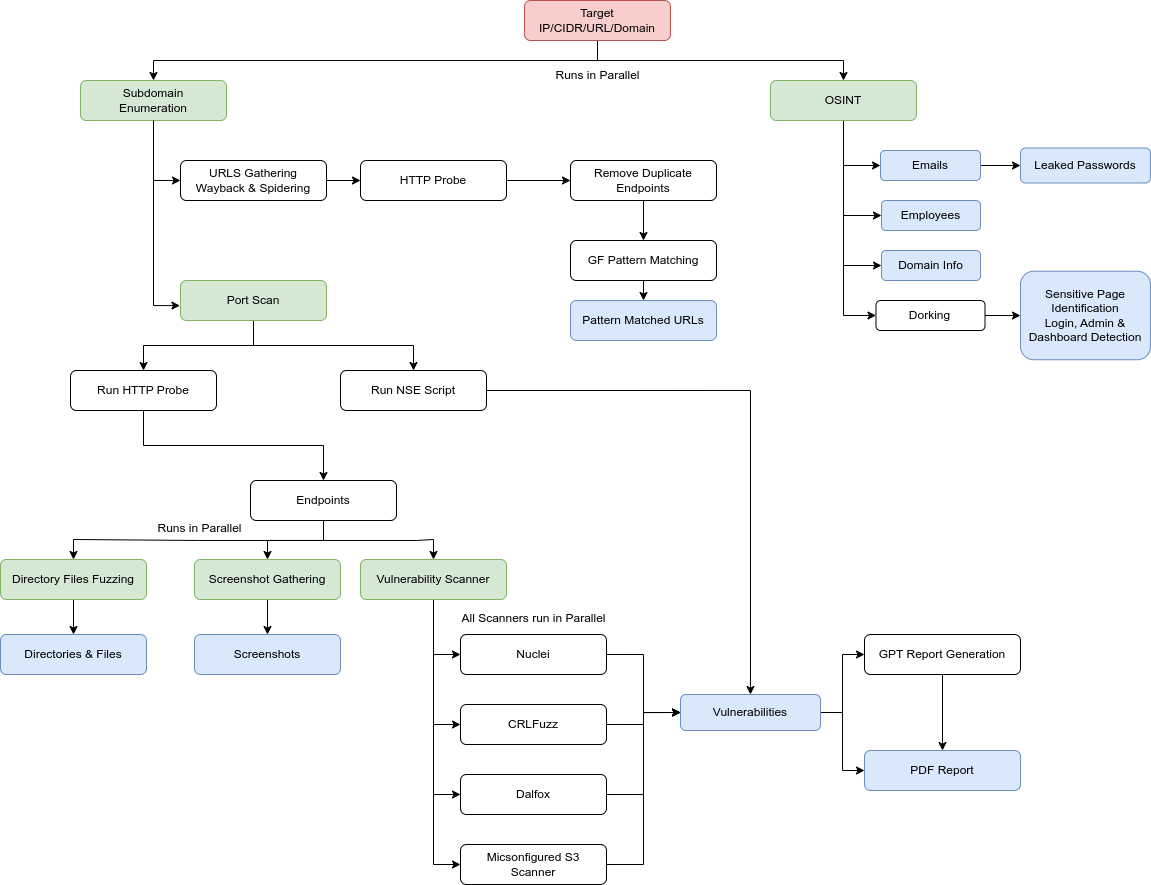
rengine
 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
crawlerdns-subdomain-enumerationinformation-gathering+9
8.9k
yogeshojha/renginereNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 robotshell/magicrecon
MagicRecon is a powerful shell script to maximize the recon and data collection process of an objective and finding common vulnerabilities, all this…
 netbox-community/netbox
Open-source IPAM and DCIM platform providing a centralized source of truth for modeling, documenting, and automating network infrastructure with…
 netalertx/netalertx
Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.
 irsaattiquecyber/systemvulnerabilitychecklist_project4_decodelabs
System Vulnerability Checklist & Network Security Hardening project featuring reconnaissance, vsFTPd backdoor analysis (CVE-2011-2523), and active…
 isnic/prober
Automated, reproducible network security testing framework using Ansible and BATS to verify DNS, host availability, open ports, and TLS configuration…
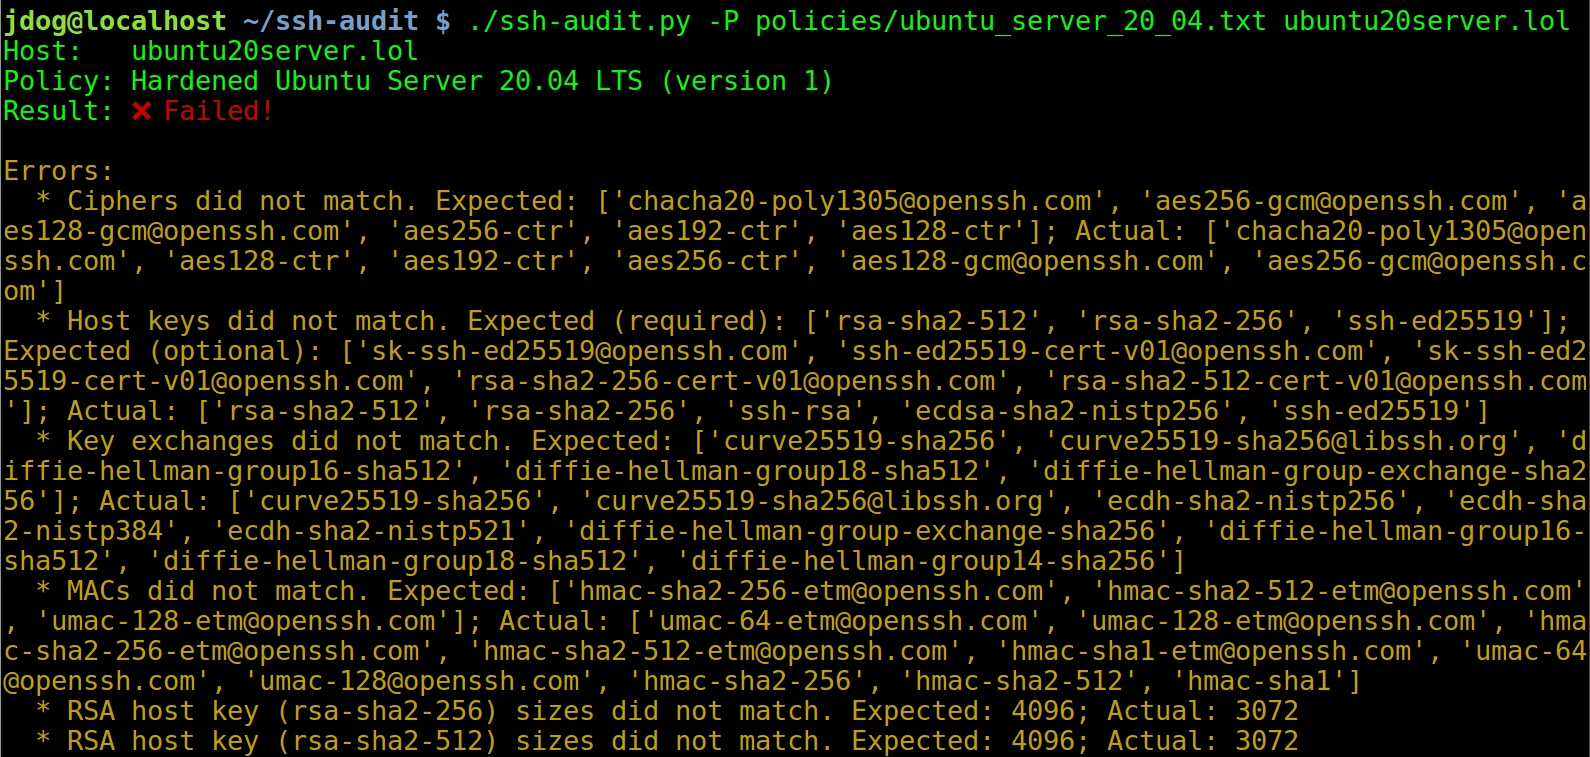 jtesta/ssh-audit
SSH server & client security auditing (banner, key exchange, encryption, mac, compression, compatibility, security, etc)
 zales2004/sunset-noontide-pentesting
Description Professional penetration testing assessment of the Sunset: Noontide VulnHub machine, covering reconnaissance, service enumeration,…
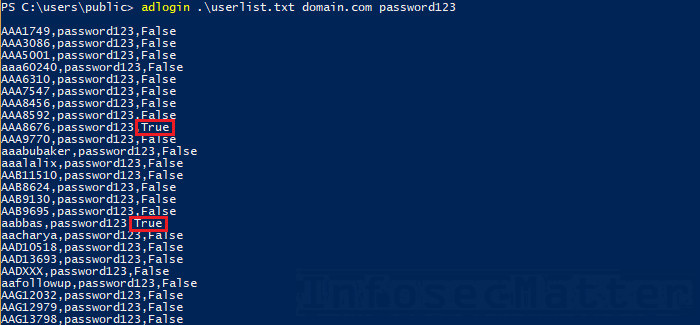 infosecmatter/minimalistic-offensive-security-tools
A repository of tools for pentesting of restricted and isolated environments.
 anouarbensaad/vulnx
vulnx 🕷️ an intelligent Bot, Shell can achieve automatic injection, and help researchers detect security vulnerabilities CMS system. It can perform…
 zcyberseclab/zscan
A fast, customizable service detection tool powered by a flexible fingerprint system. It helps you identify services, APIs, and network…
 sinfulz/justtryharder
Comprehensive penetration testing cheat sheet for PWK/OSCP exam preparation, covering privilege escalation, password cracking, payload generation,…
 ritvikb99/dark-fantasy-hack-tool
DDOS Tool: To take down small websites with HTTP FLOOD. Port scanner: To know the open ports of a site. FTP Password Cracker: To hack file system of…
 alisamtechnology/atscan
Advanced dork Search & Mass Exploit Scanner
 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
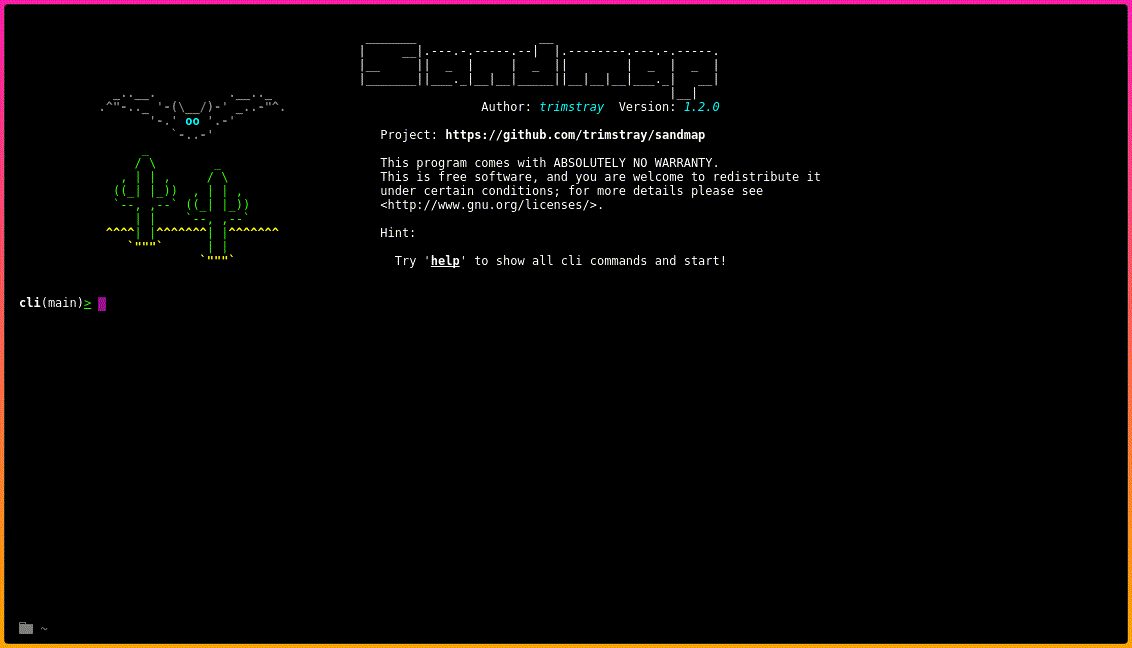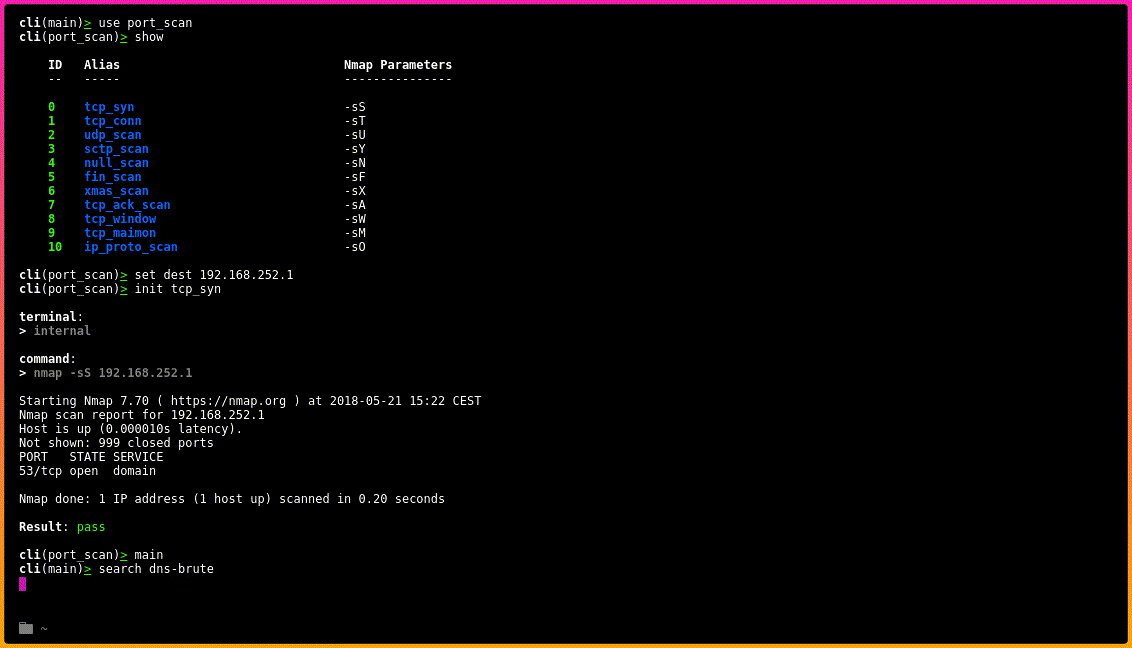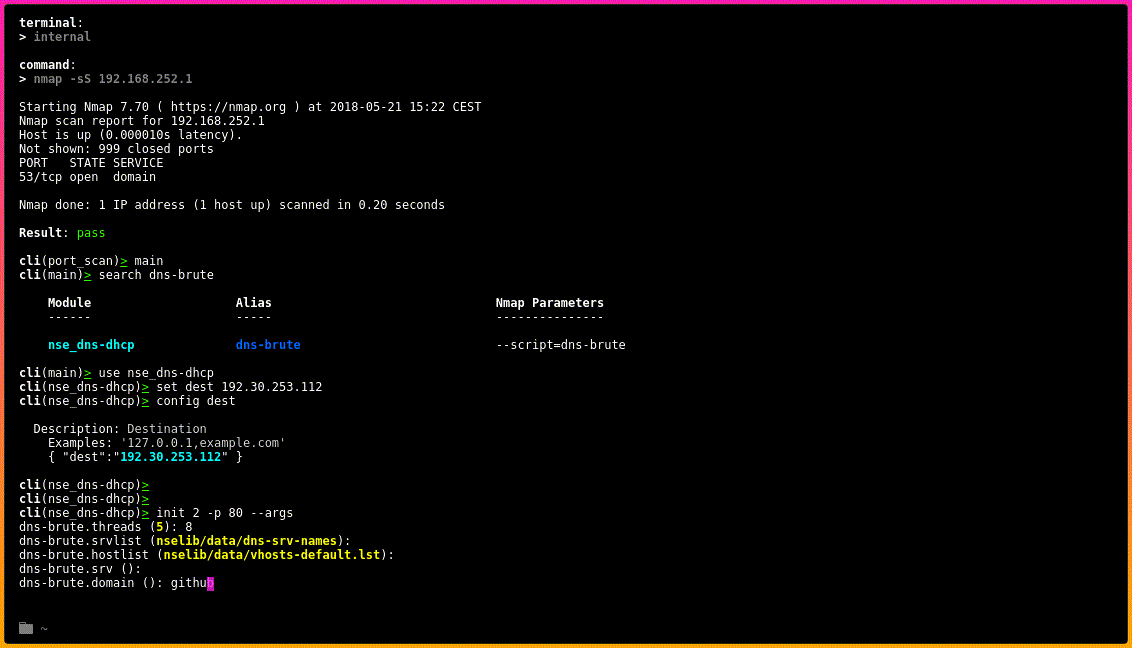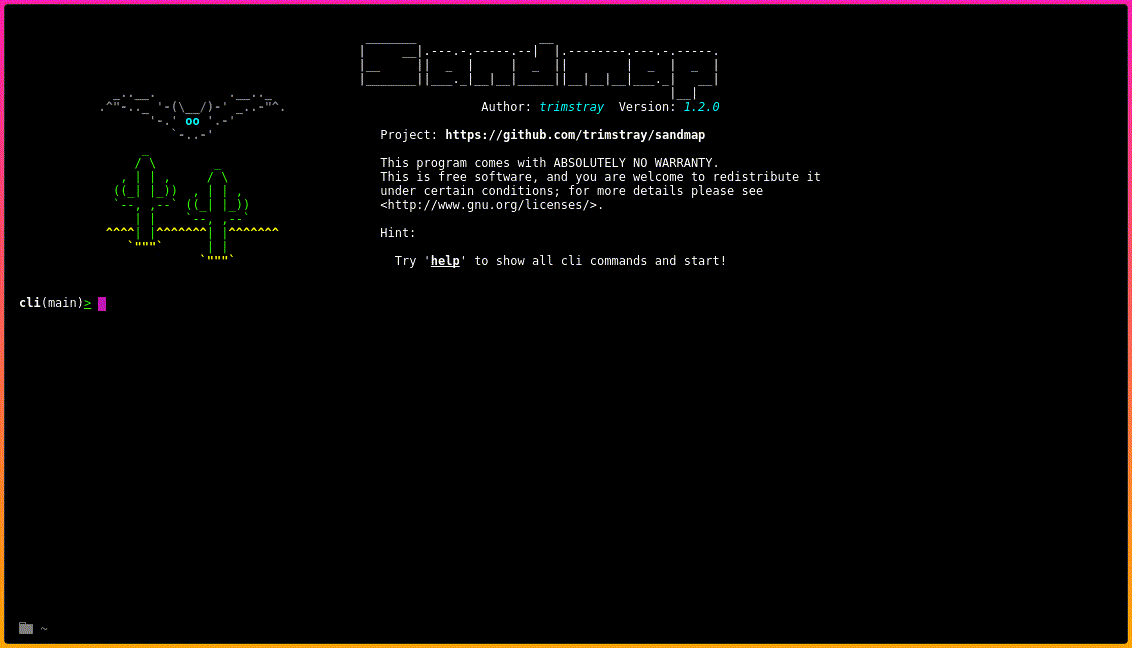 trimstray/sandmap
Nmap on steroids. Simple CLI with the ability to run pure Nmap engine, 31 modules with 459 scan profiles.
 cytopia/pwncat
pwncat - netcat on steroids with Firewall, IDS/IPS evasion, bind and reverse shell, self-injecting shell and port forwarding magic - and its fully…