
lazyrecon
 jhaddix/lazyrecon
This script is intended to automate your reconnaissance process in an organized fashion
information-gatheringnetwork-mappingpenetration-testing+4
488 years ago
jhaddix/lazyreconThis script is intended to automate your reconnaissance process in an organized fashion
 alisamtechnology/atscan
Advanced dork Search & Mass Exploit Scanner
 m0usem0use/erl_mouse
python script to find vulnerable targets of CVE-2025-32433
 s0md3v/smap
a drop-in replacement for Nmap powered by shodan.io
 eldraco/domain_analyzer
Analyze the security of any domain by finding all the information possible. Made in python.
 praetorian-inc/nerva
Fast service fingerprinting CLI for 170+ protocols (TCP/UDP/SCTP) - built by Praetorian
 edu4rdshl/unimap
Scan only once by IP address and reduce scan times with Nmap for large amounts of data.
 yukselberkay/asnap
Automates reconnaissance by mapping IPv4/IPv6 addresses to organizations using GeoLite2 databases, with integrated nmap port scanning and batch…
 l33tdawg/phantomrecon
PhantomRecon is a CLI-based, modular, agent-driven red team automation tool designed to demonstrate autonomous offensive security workflows powered…
 r4tw1z/cve-2024-6387
This script, created by R4Tw1z, is designed to scan IP addresses to check if they are running a potentially vulnerable version of OpenSSH. The tool…
 rv4l3r3/log4v-vuln-check
This script is used to perform a fast check if your server is possibly affected by CVE-2021-44228 (the log4j vulnerability).
 pownjs/recon
A powerful target reconnaissance framework powered by graph theory.
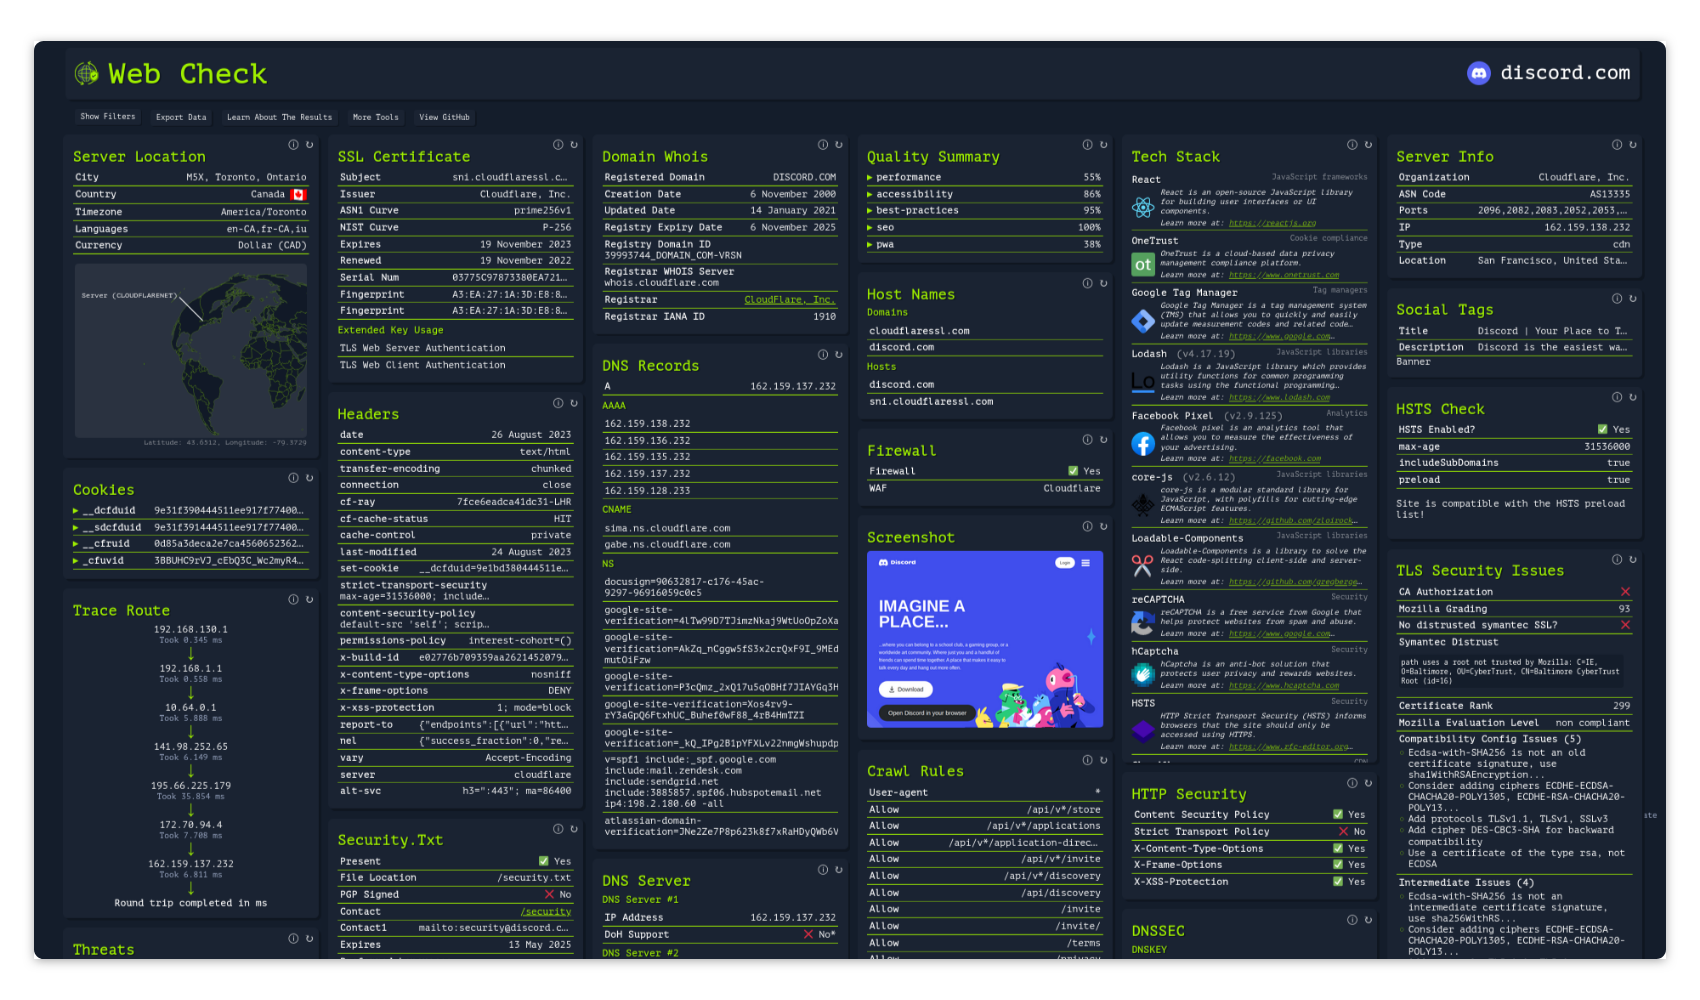 lissy93/web-check
🕵️♂️ All-in-one OSINT tool for analysing any website
 autorecon/autorecon
Multi-threaded network reconnaissance tool that automates service enumeration, port scanning, and information gathering for penetration testing and…
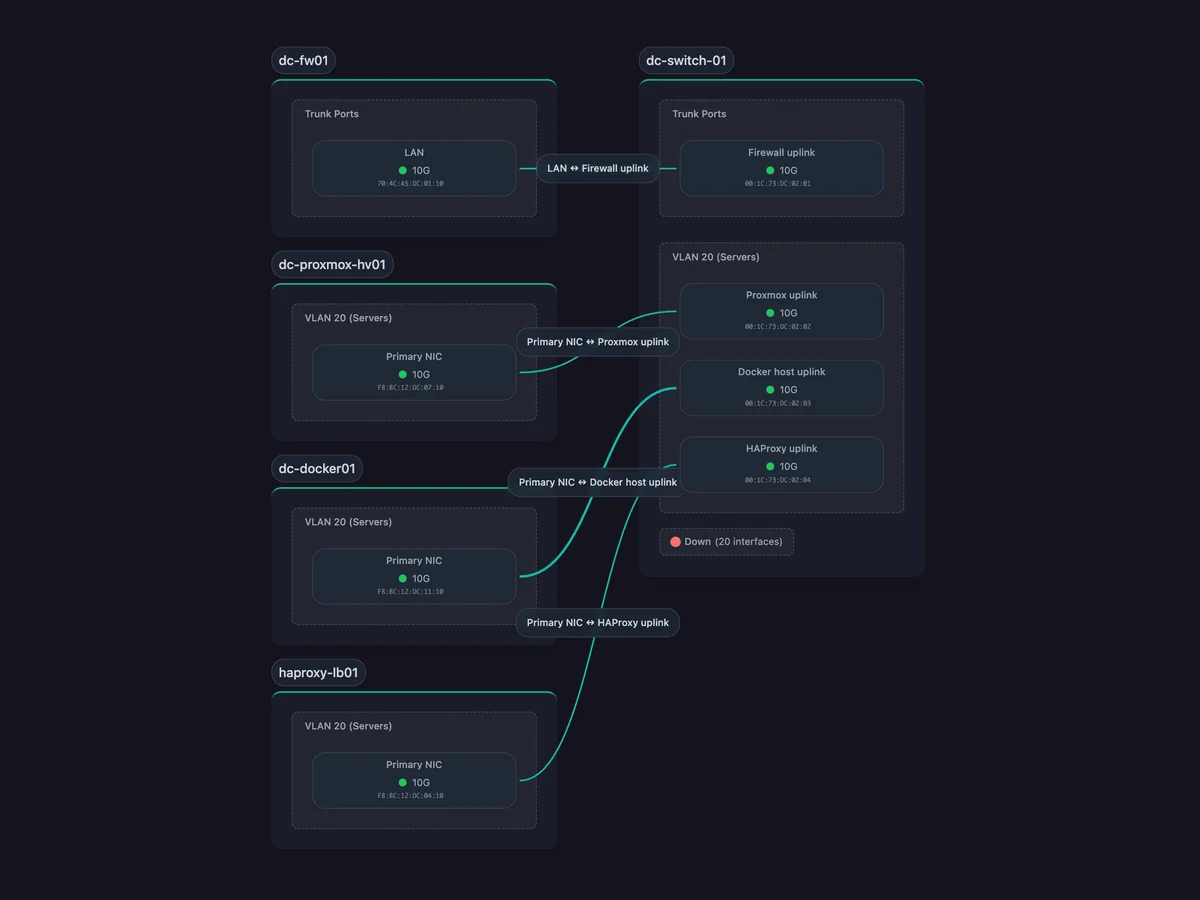 scanopy/scanopy
Network diagrams that update themselves
 s0md3v/striker
Striker is an offensive information and vulnerability scanner.
 ullaakut/nmap
Idiomatic Go library for invoking a network scanner binary, enabling host discovery, port scanning, service/OS detection, and scripted vulnerability…
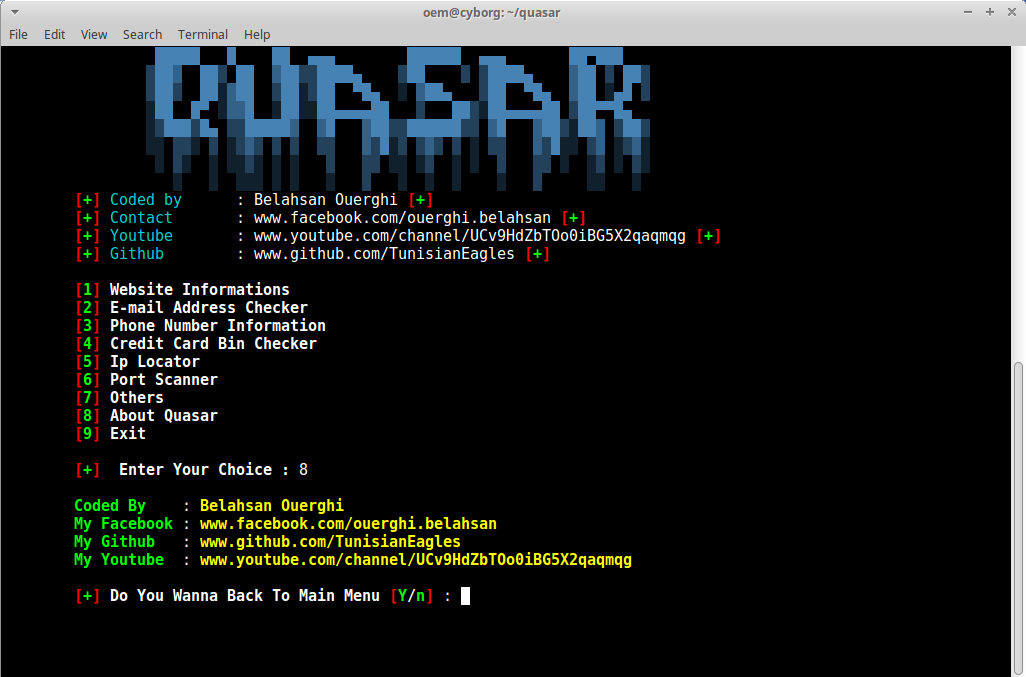 cyb0r9/quasar
Modular information gathering framework for penetration testers, featuring website analysis, email/phone lookup, credit card BIN checking, IP…