
phantomrecon
 l33tdawg/phantomrecon
PhantomRecon is a CLI-based, modular, agent-driven red team automation tool designed to demonstrate autonomous offensive security workflows powered…
dns-analysisexploitationinformation-gathering+6
3
l33tdawg/phantomreconPhantomRecon is a CLI-based, modular, agent-driven red team automation tool designed to demonstrate autonomous offensive security workflows powered…
 dewolfrobin/last
Linux Automated Security scanning Tool
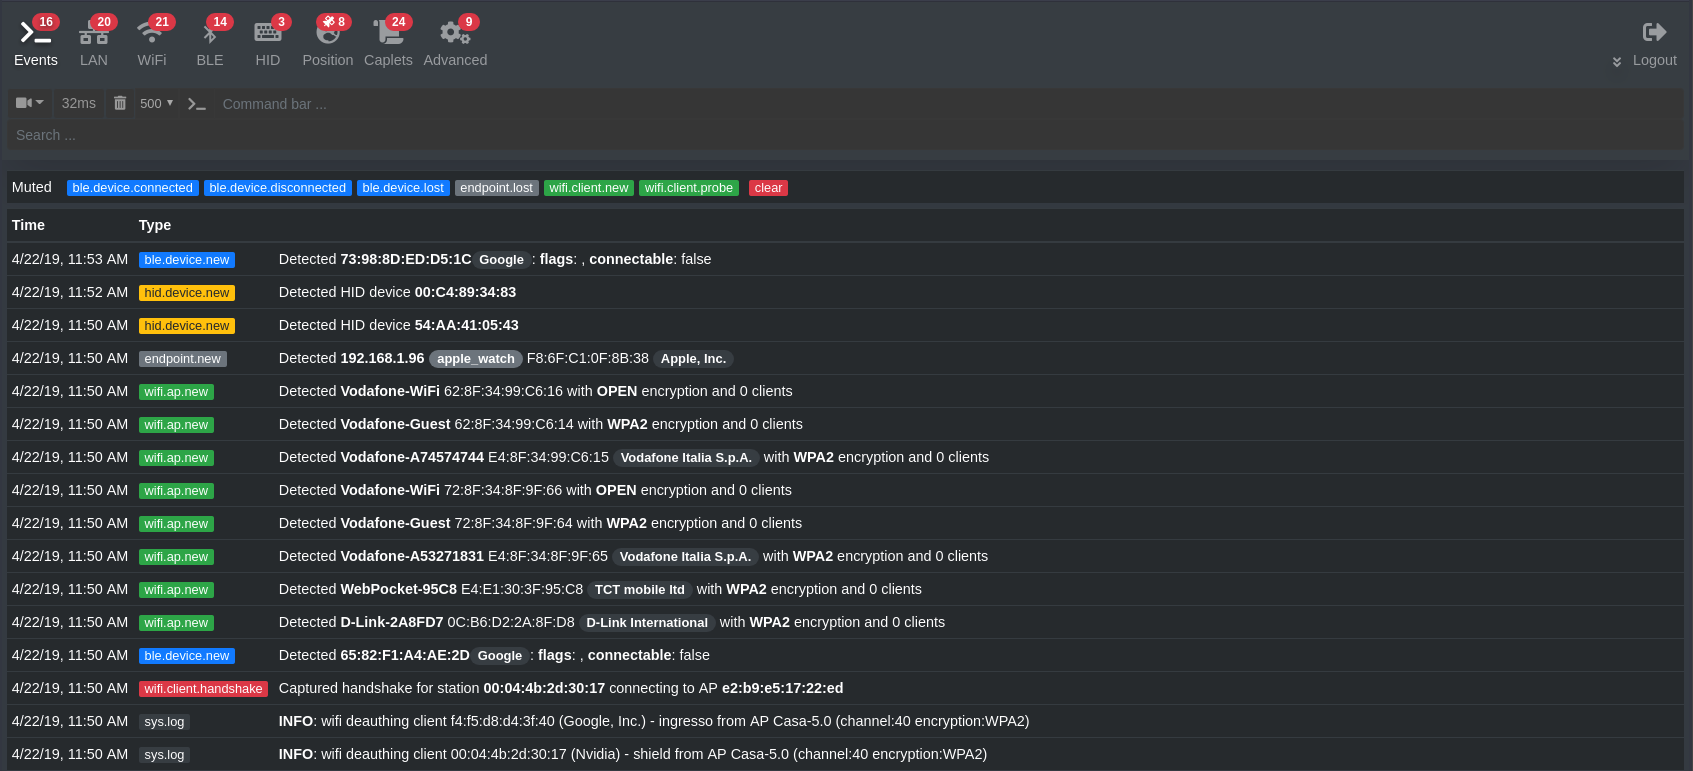 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
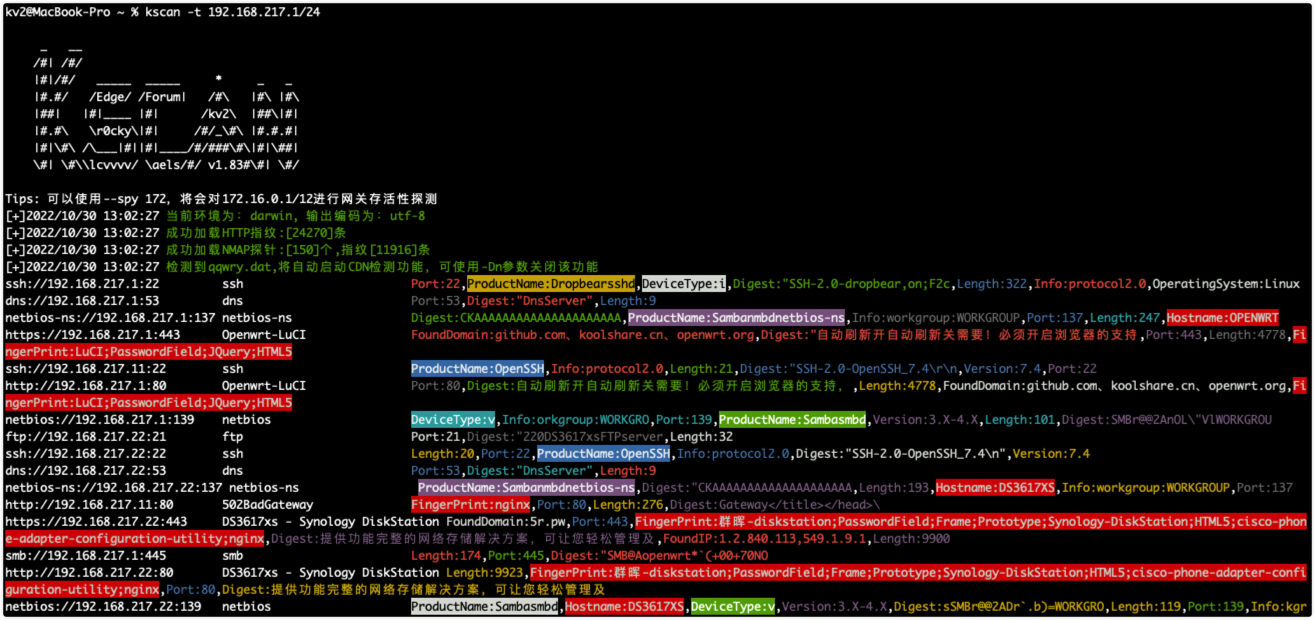 lcvvvv/kscan
Multi-protocol port scanner with fingerprint recognition, service detection, and brute-force authentication testing. Supports 1200+ protocols, 10000+…
 esc4icescesc/skanuvaty
Dangerously fast DNS/network/port scanner
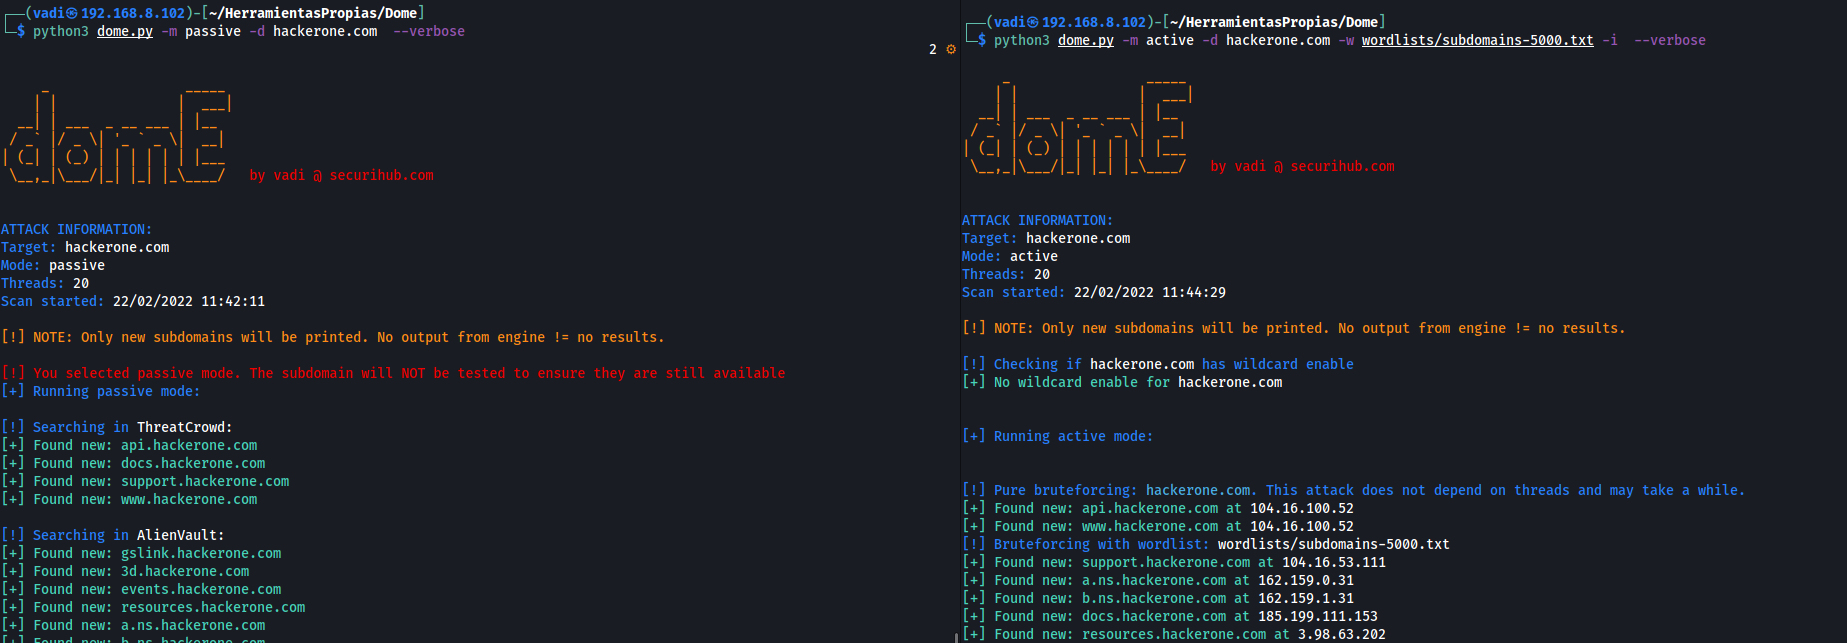 v4d1/dome
Fast Python-based subdomain enumeration tool combining passive OSINT and active brute-force scanning with DNS wildcard detection, port scanning, and…
 ginjachris/pentmenu
A bash script for recon and DOS attacks
 serain/netmap.js
Fast browser-based network discovery module
 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.
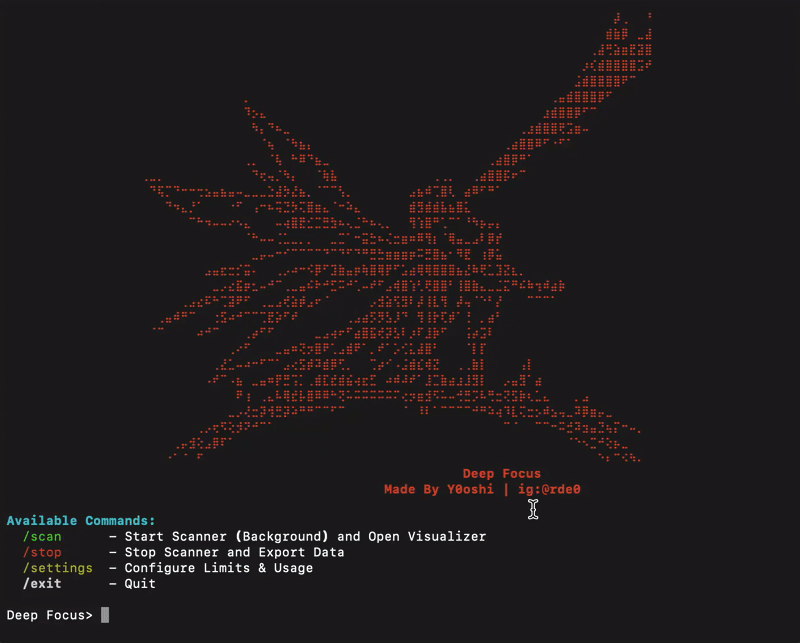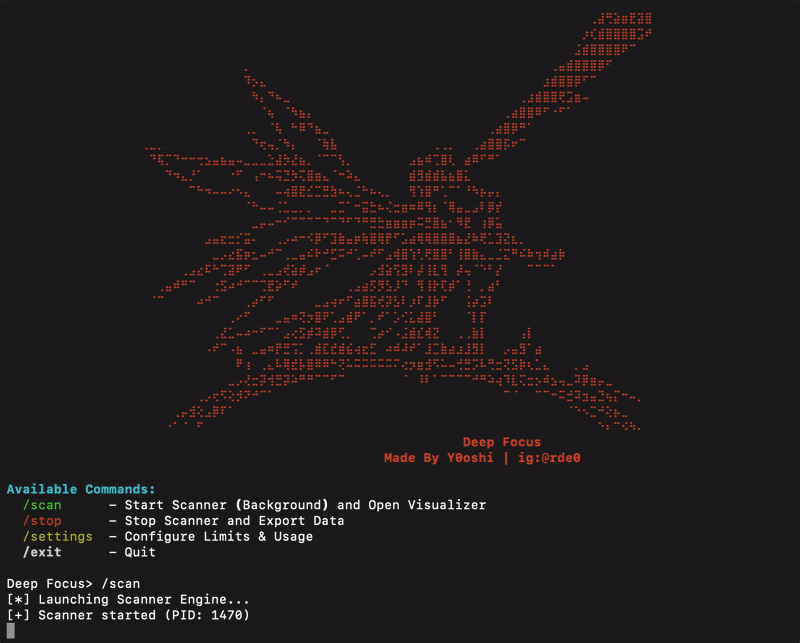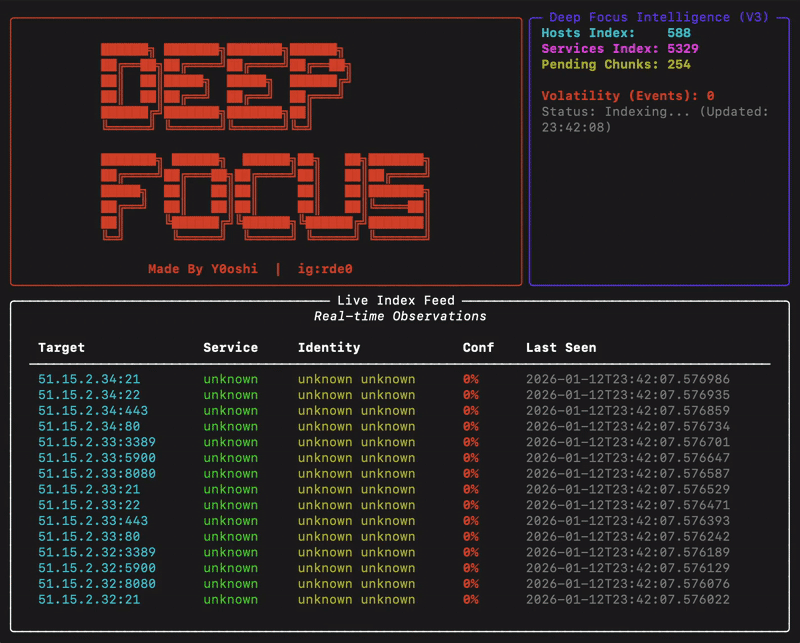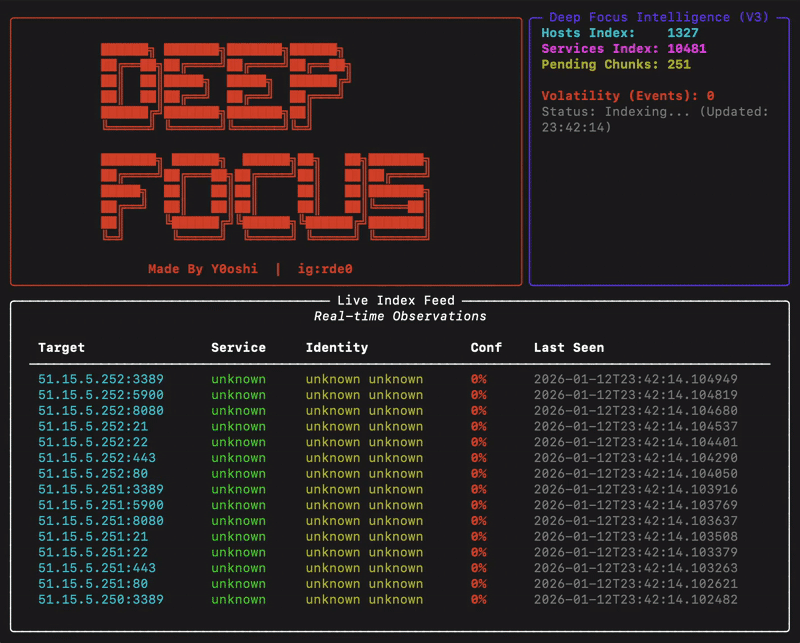 y0oshi/project-deep-focus
Asynchronous network reconnaissance engine for large-scale service discovery and fingerprinting. Identifies unsecured services (RTSP cameras, VNC,…
 dmontgomery40/pentest-mcp
NOT for educational purposes: An MCP server for professional penetration testers including STDIO/HTTP/SSE support, nmap, go/dirbuster, nikto, JtR,…
 knowledge-wisdom-understanding/recon
Enumerate a target Based off of Nmap Results
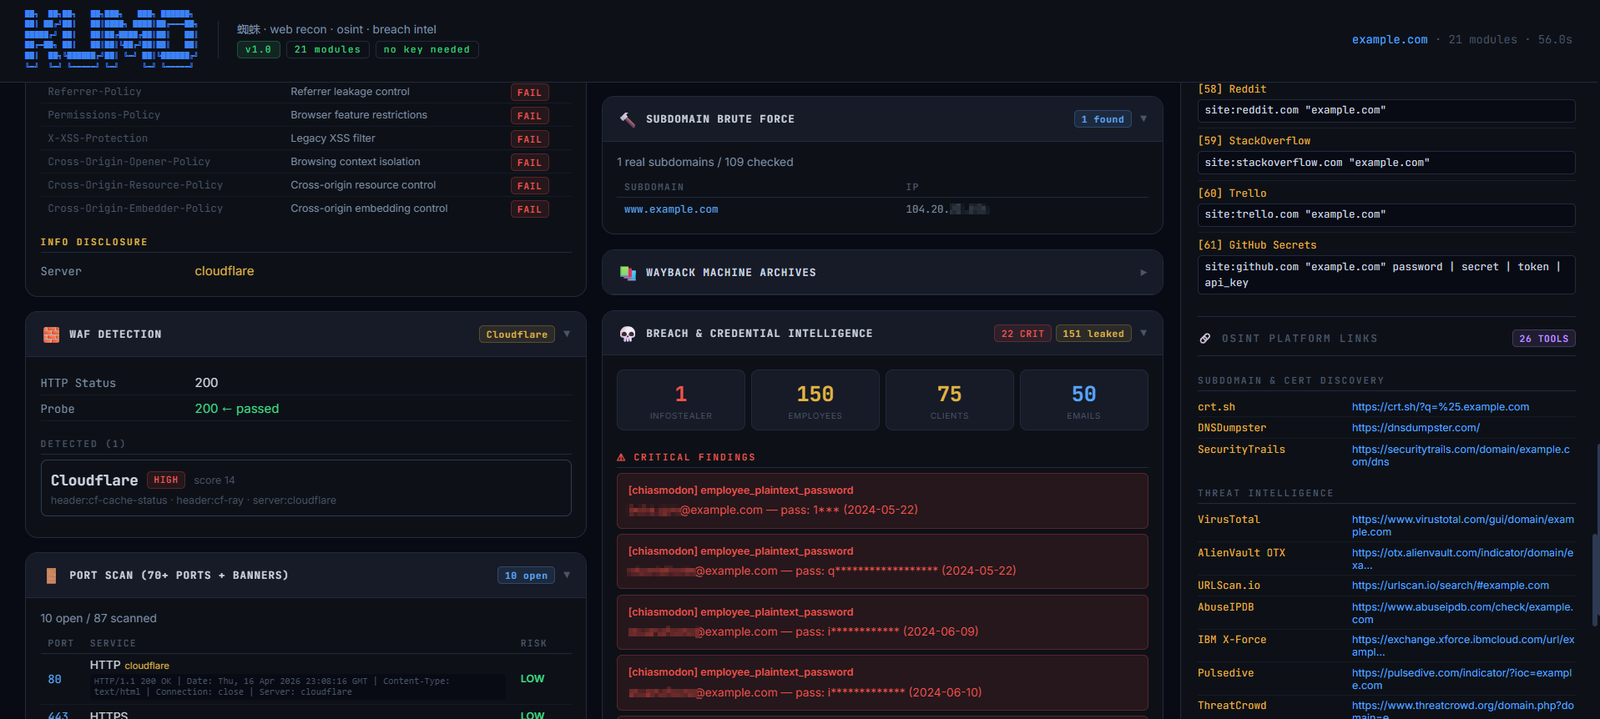 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 hcbaker/puwr
Pivot your way deeper into computer networks with SSH compromised machines.
 zcyberseclab/zscan
A fast, customizable service detection tool powered by a flexible fingerprint system. It helps you identify services, APIs, and network…