
CVE-2024-6387-exploit
 thegenetic/cve-2024-6387-exploit
CVE-2024-6387 exploit
exploitationnetwork-securitypenetration-testing+3
13
thegenetic/cve-2024-6387-exploitCVE-2024-6387 exploit
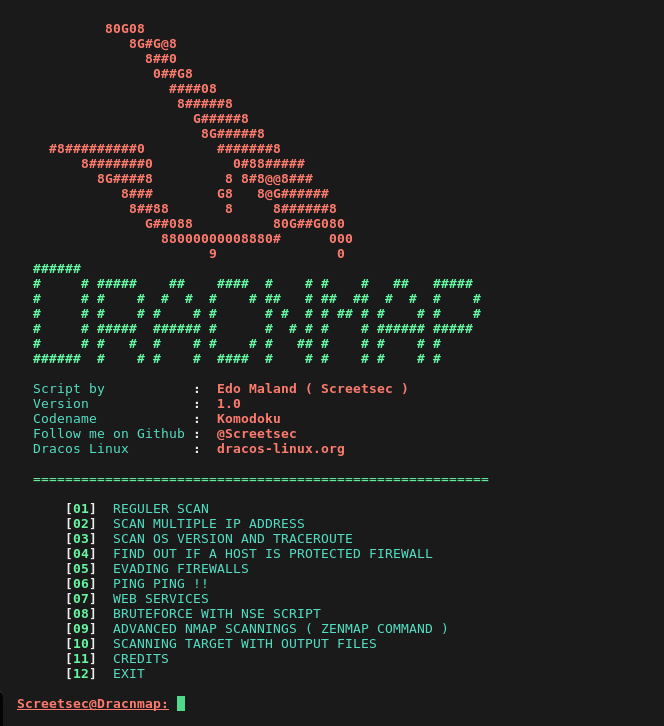 screetsec/dracnmap
Dracnmap is an open source program which is using to exploit the network and gathering information with nmap help. Nmap command comes with lots of…
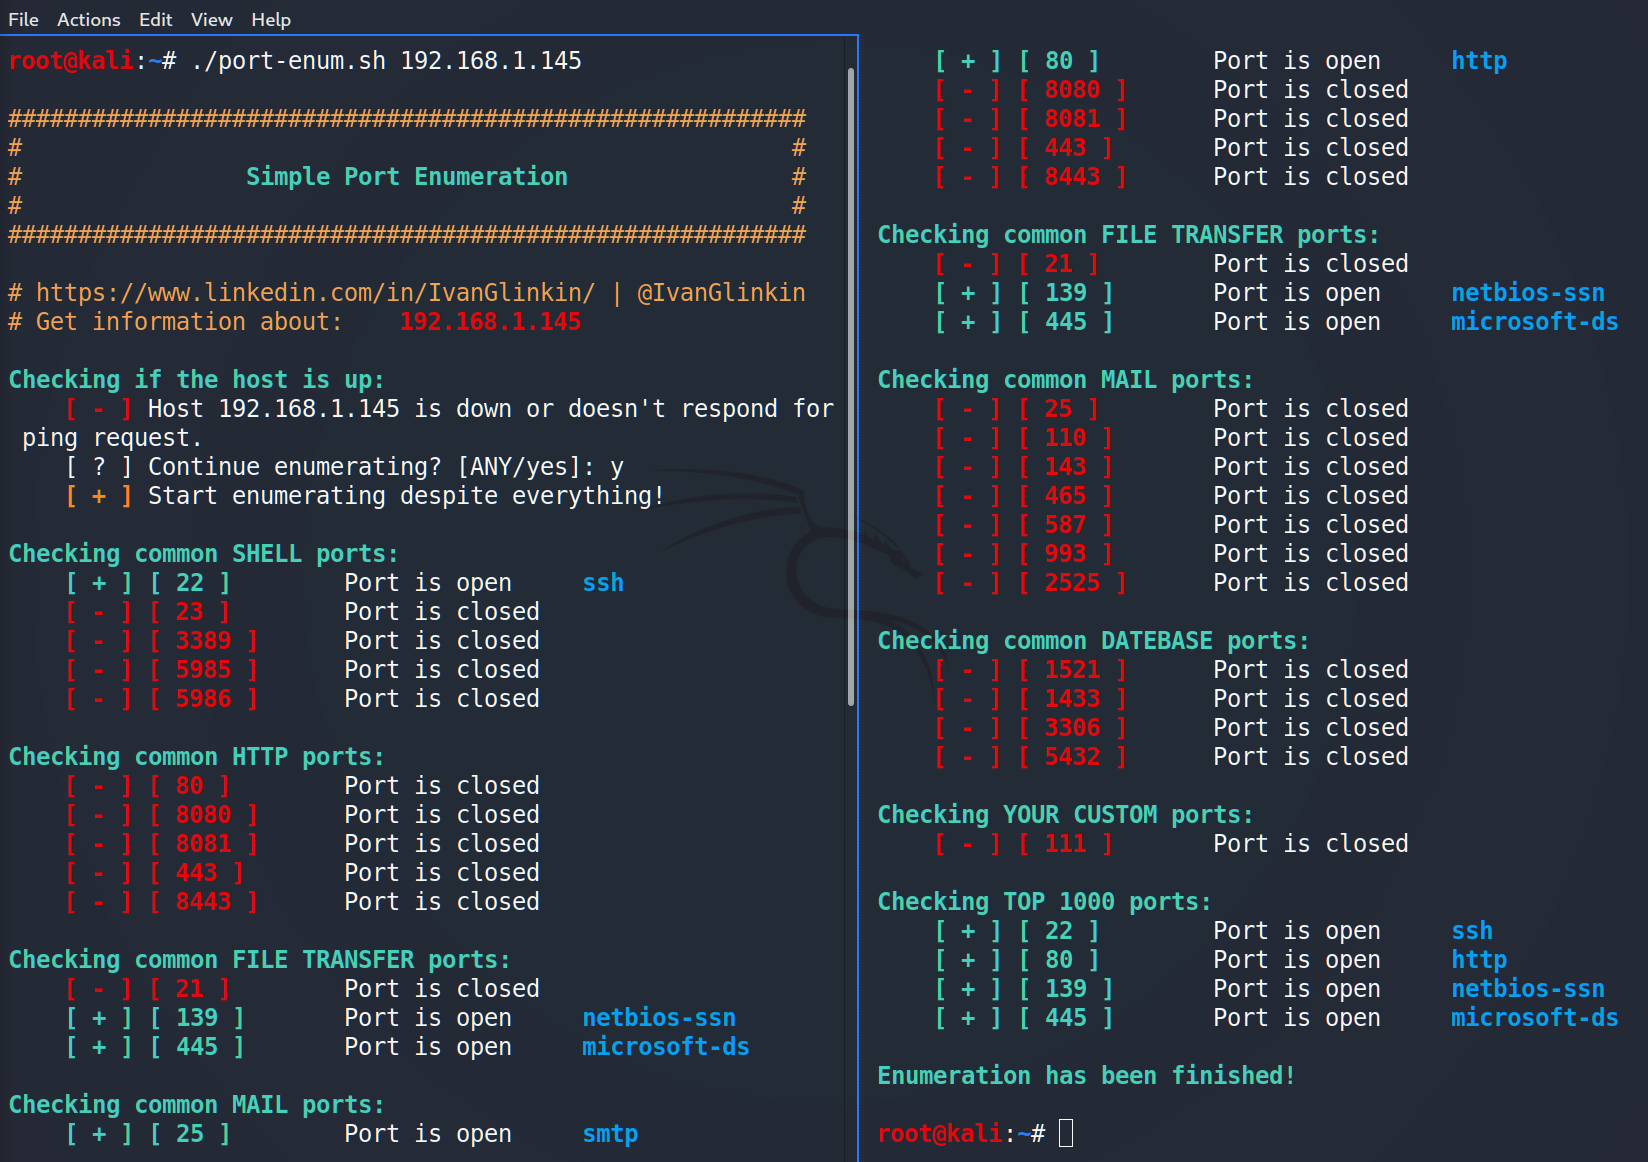 ivanglinkin/port-enumeration
Have you ever faced with the lack of possibility of using NMap? For instance if you have reverse shell as an unprivileged user and there are no…
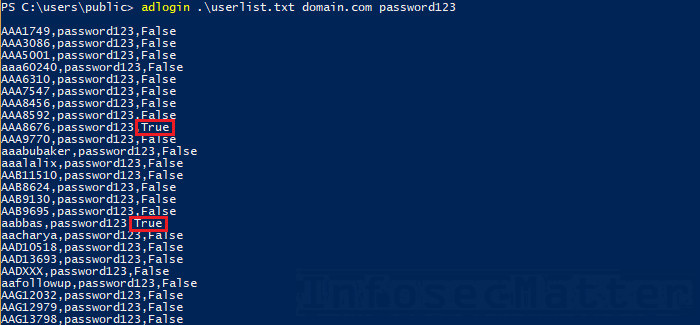 infosecmatter/minimalistic-offensive-security-tools
A repository of tools for pentesting of restricted and isolated environments.
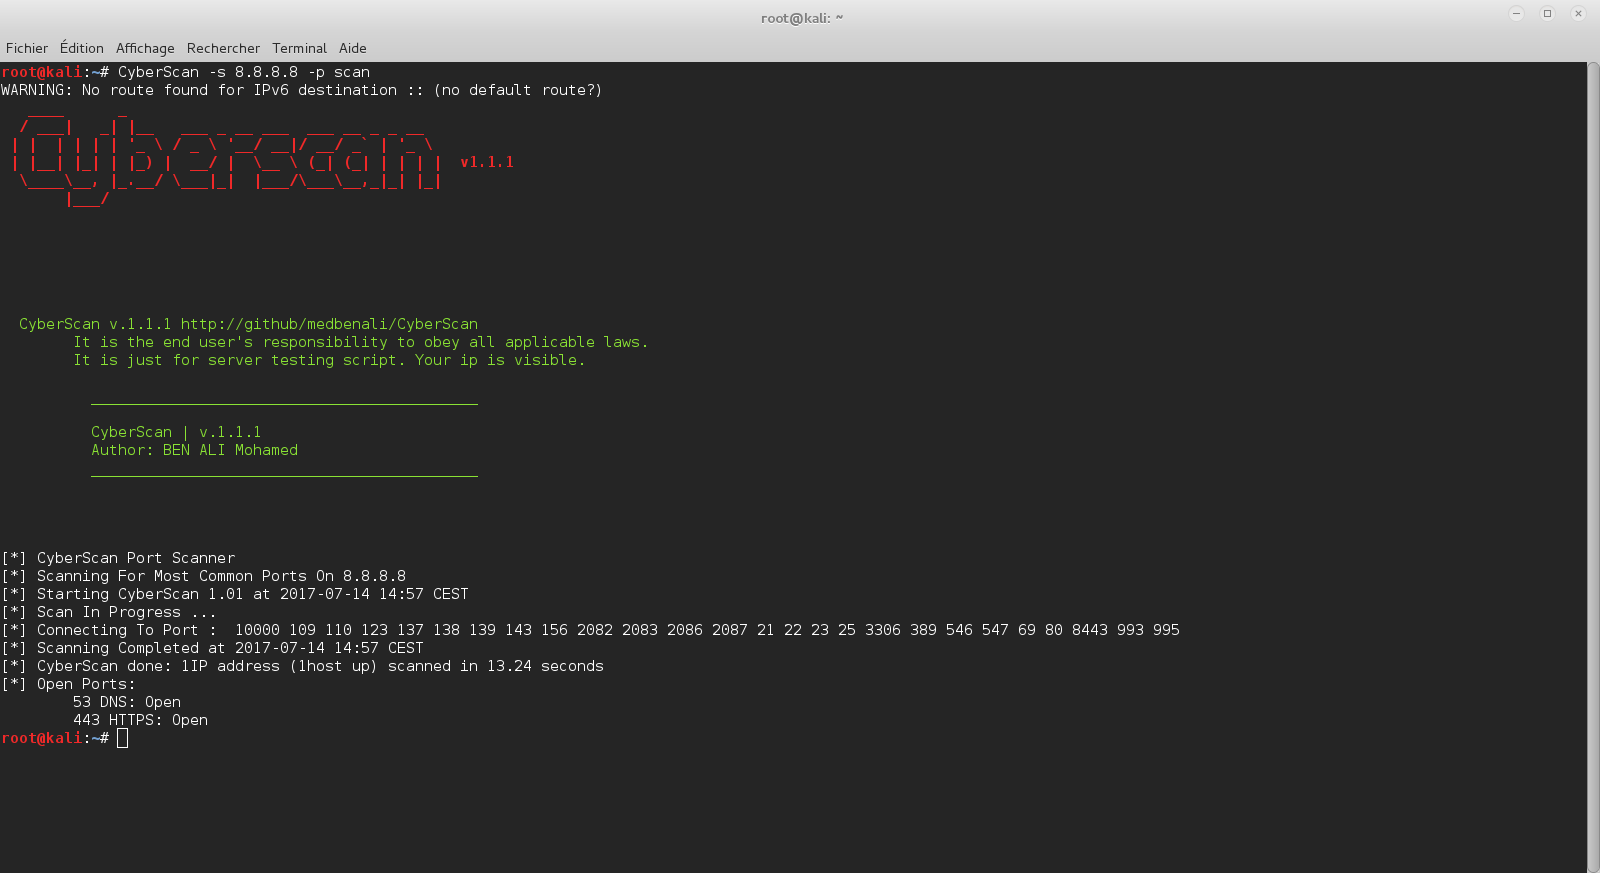 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
 reddyyz/astsu
A network scanner tool, developed in Python 3 using scapy.
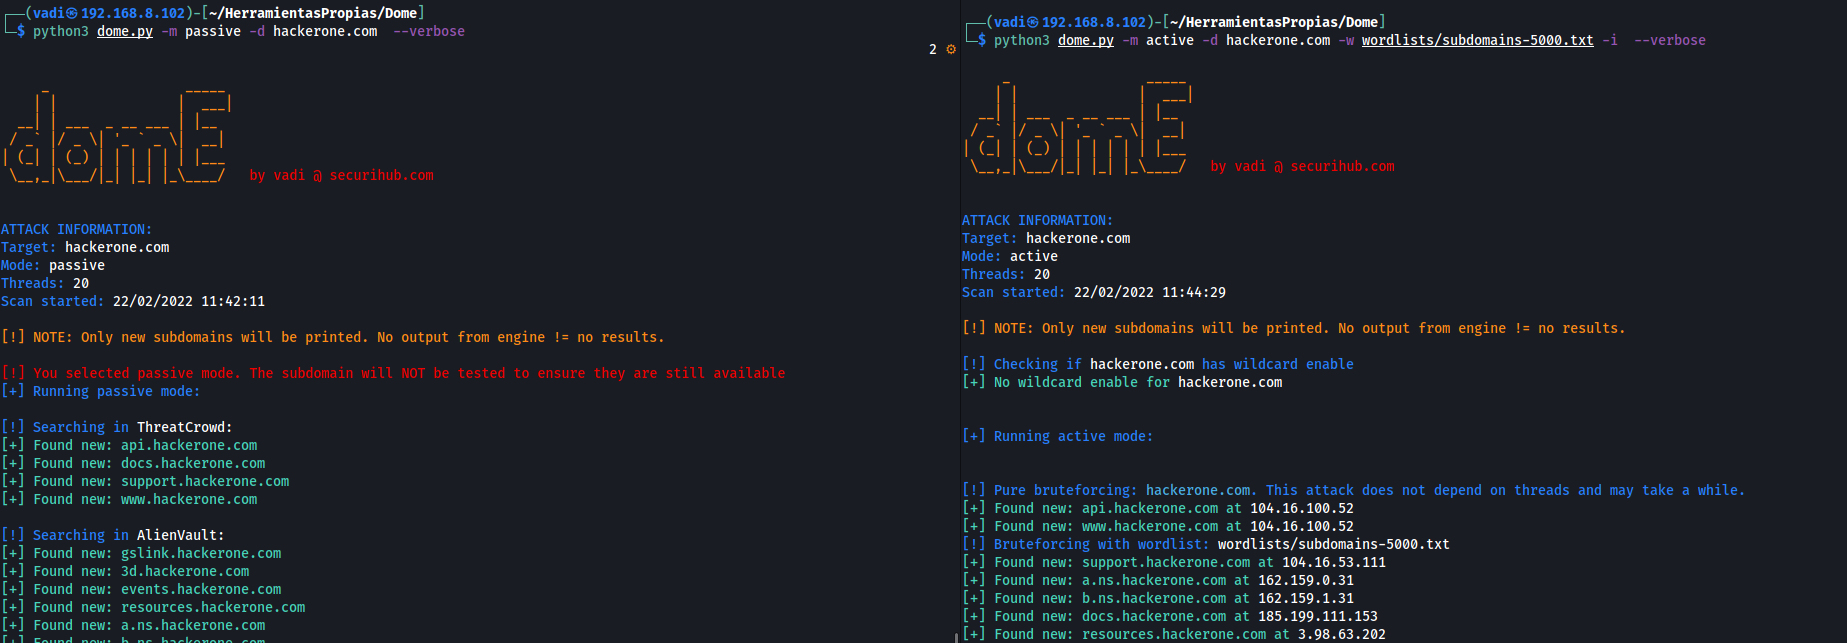 v4d1/dome
Fast Python-based subdomain enumeration tool combining passive OSINT and active brute-force scanning with DNS wildcard detection, port scanning, and…
 neutralwarrior/c-port-scanner
A port scanner that scans a target IP for open ports and displays the results, built with C
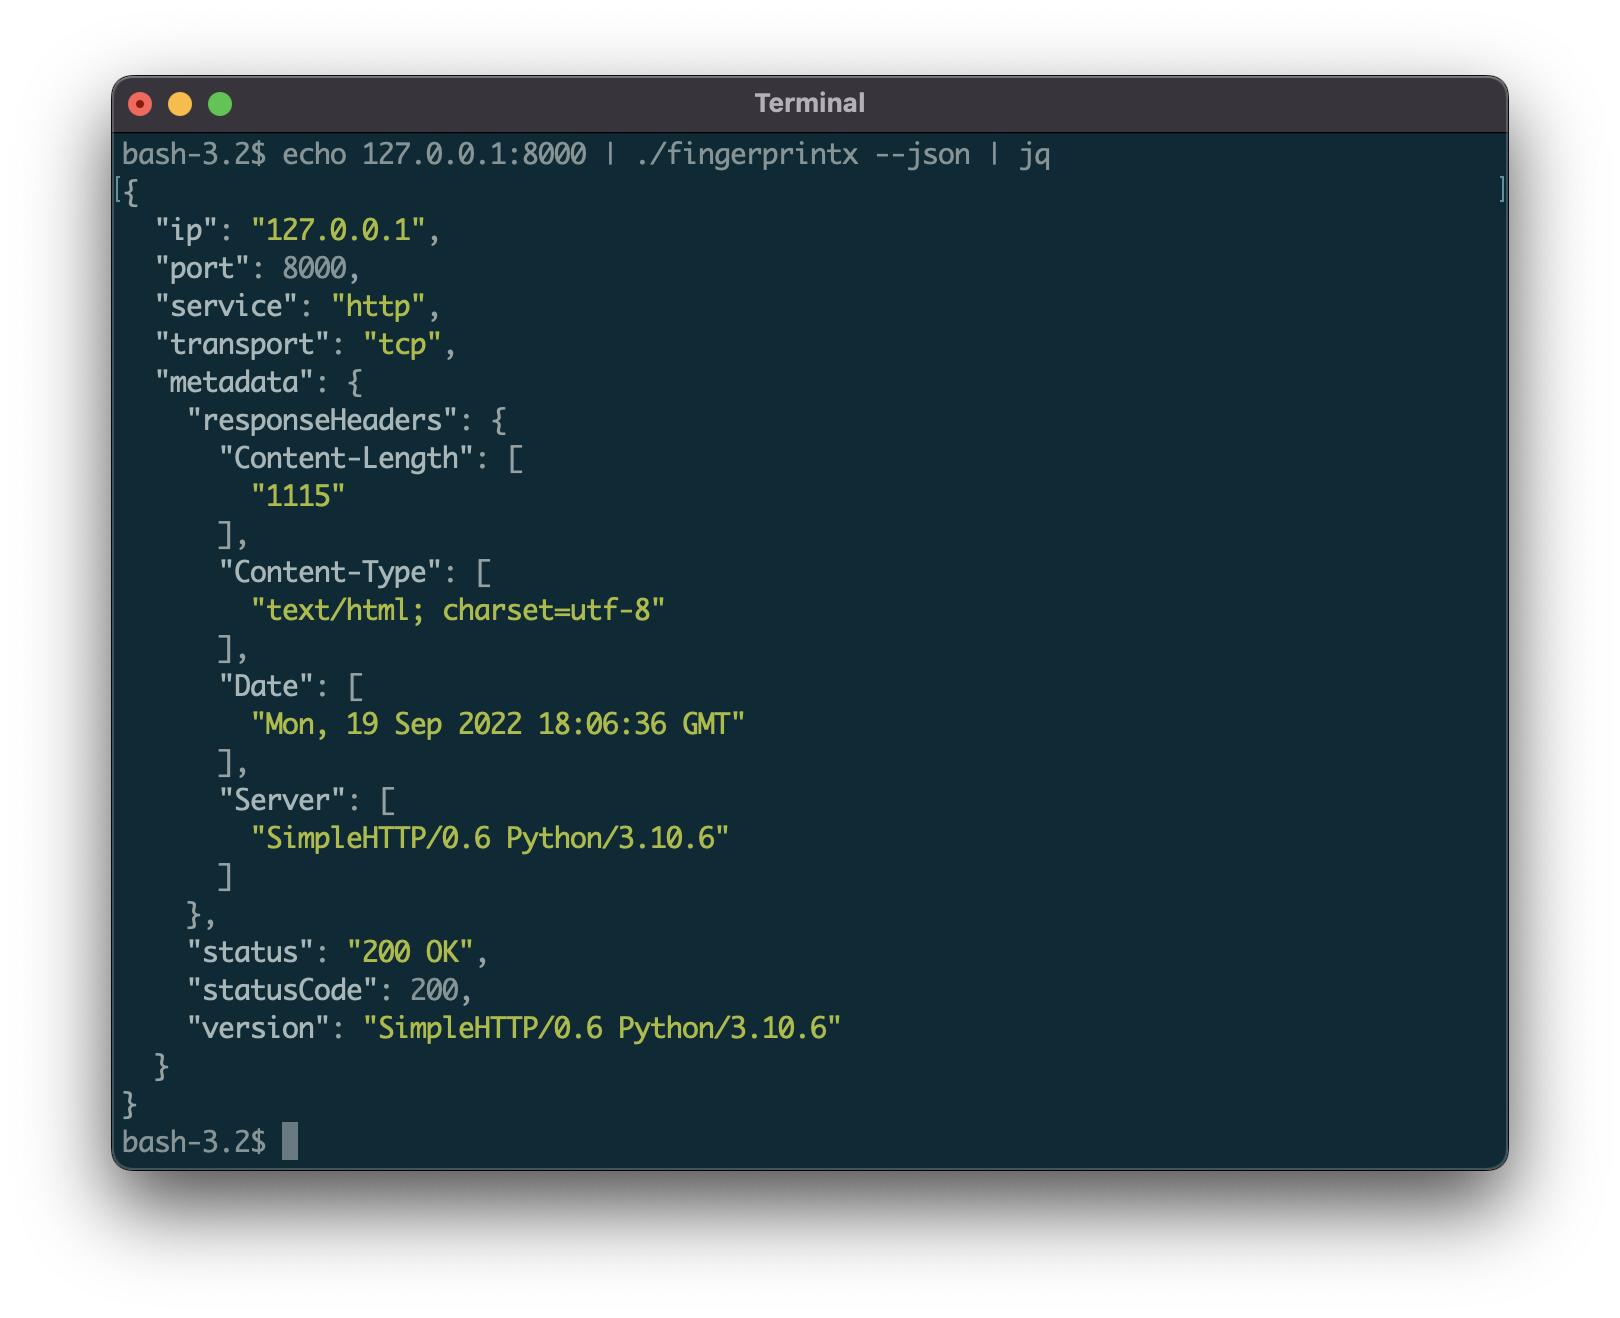 praetorian-inc/fingerprintx
Standalone utility for service discovery on open ports!
 ullaakut/nmap
Idiomatic Go library for invoking a network scanner binary, enabling host discovery, port scanning, service/OS detection, and scripted vulnerability…
 r3vn/badkarma
network reconnaissance toolkit
 tulpar/tulpar
Tulpar - Web Vulnerability Scanner
 aqeisi/cve-2022-36663-poc
Internal network scanner through Gluu IAM blind ssrf
 alientec1908/alientec-recon-tool
AlienTec-Recon-Tool