

Simple Pentesting
 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
educationinformation-gatheringnetwork-mapping+7
sakispat/simple-pentestingAn educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…

 bee-san/rustscan
🤖 The Modern Port Scanner 🤖
 arch3rpro/pentest-windows
⚔️Windows11 Penetration Suite Toolkit 🔰 The First Windows Penetration Testing Environment on Mac M Chips
 marco-lancini/goscan
Interactive Network Scanner
 praetorian-inc/nerva
Fast service fingerprinting CLI for 170+ protocols (TCP/UDP/SCTP) - built by Praetorian
 milesrichardson/docker-onion-nmap
Scan .onion hidden services with nmap using Tor, proxychains and dnsmasq in a minimal alpine Docker container.
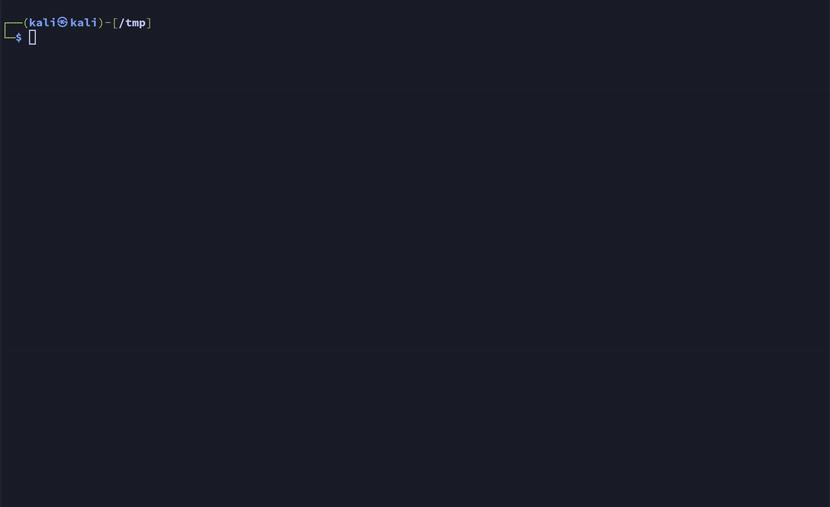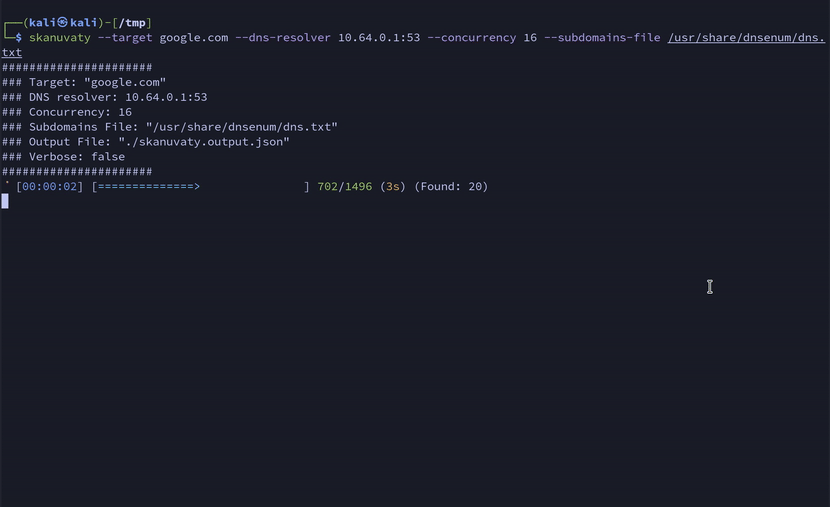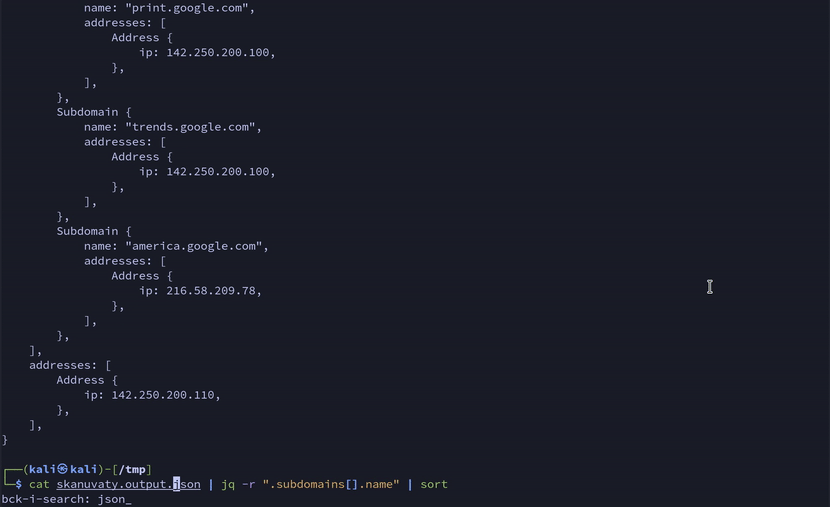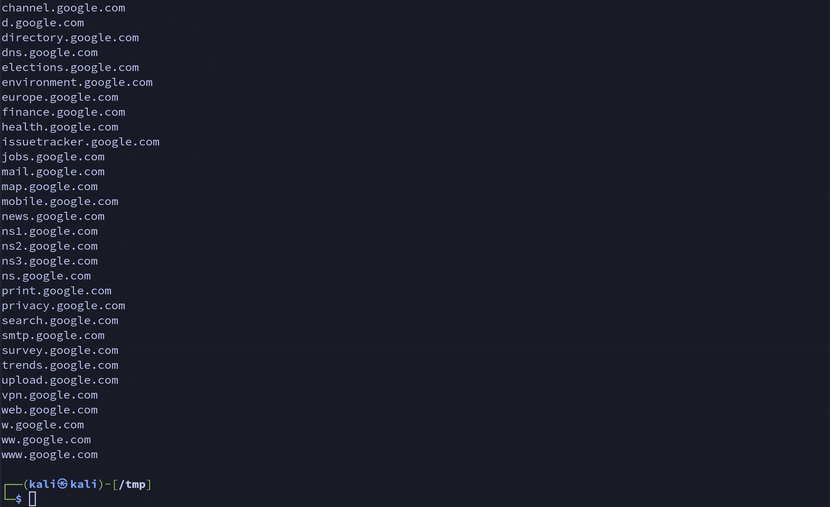 esc4icescesc/skanuvaty
Dangerously fast DNS/network/port scanner
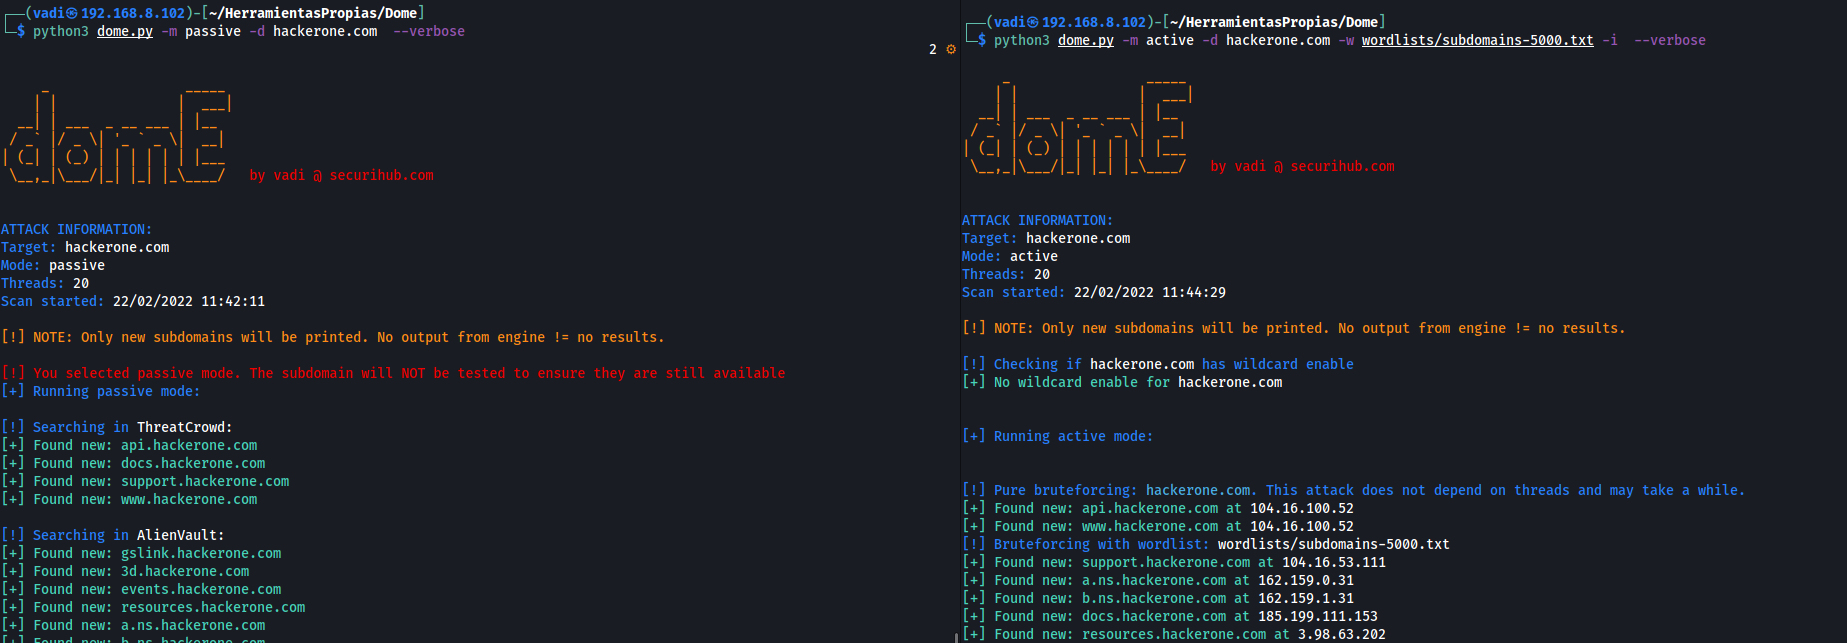 v4d1/dome
Fast Python-based subdomain enumeration tool combining passive OSINT and active brute-force scanning with DNS wildcard detection, port scanning, and…
 ginjachris/pentmenu
A bash script for recon and DOS attacks
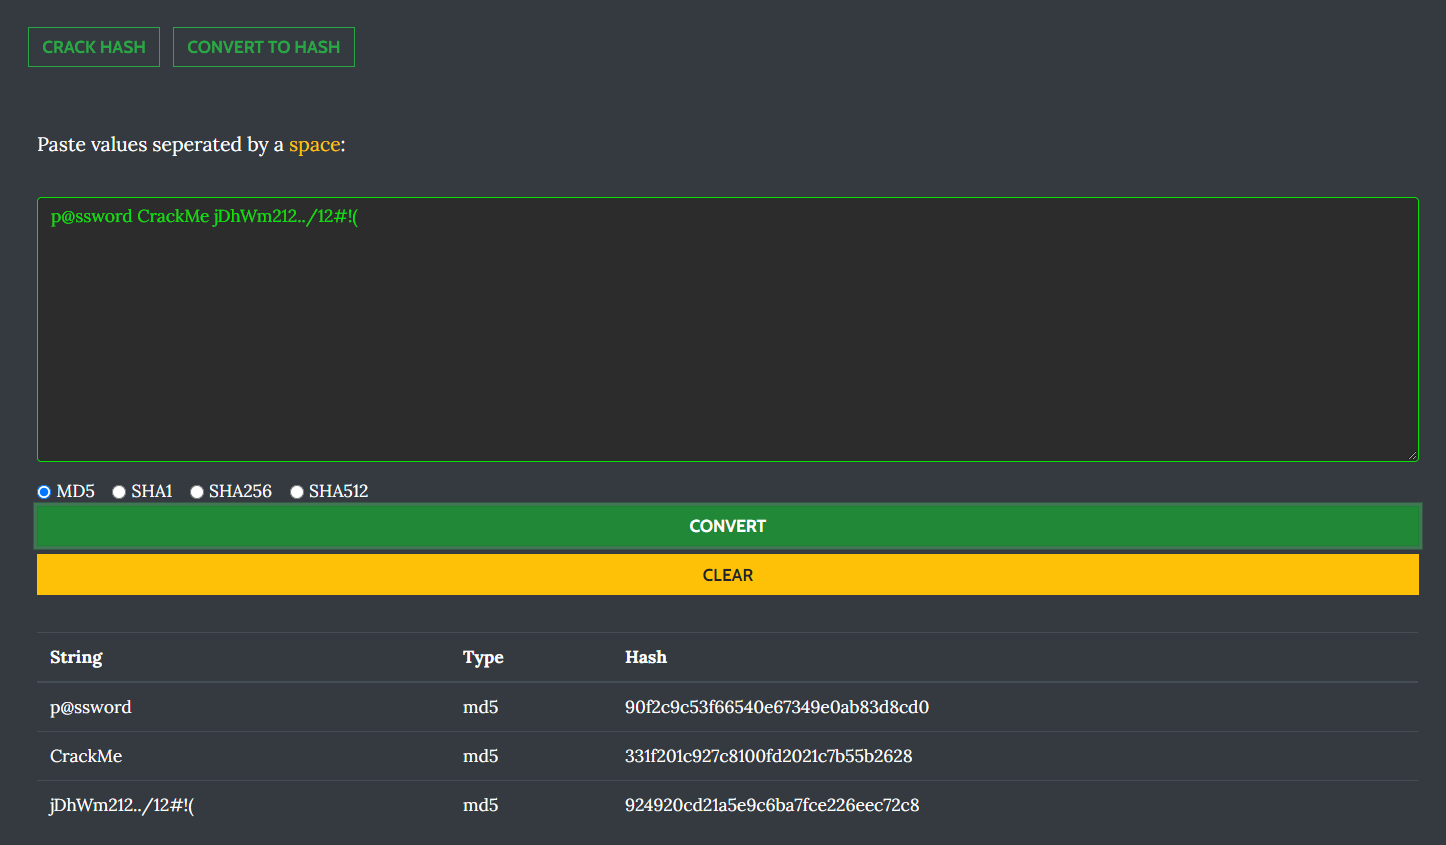 helich0pper/karkinos
Penetration Testing and Hacking CTF's Swiss Army Knife with: Reverse Shell Handling - Encoding/Decoding - Encryption/Decryption - Cracking Hashes /…
 alechilczenko/kimi
Attack Surface Discovery tool built on a microservice approach, utilizing multi-threading for fast, internet-scale asset indexing
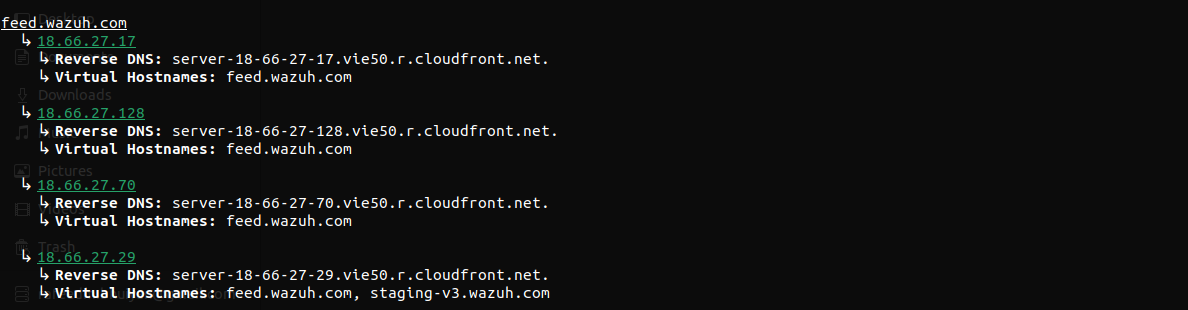 pptx704/domainim
A fast and comprehensive tool for organizational network scanning
 serain/netmap.js
Fast browser-based network discovery module
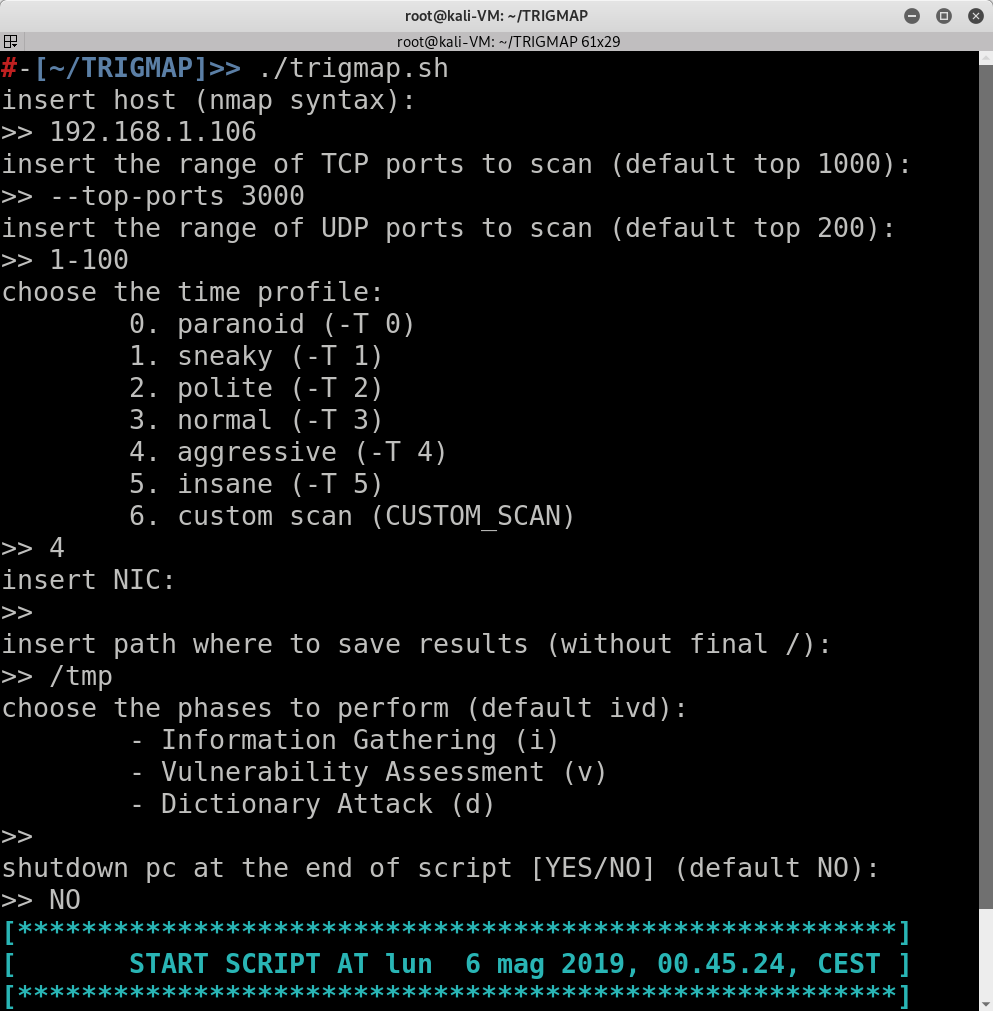 leviathan36/trigmap
A wrapper for Nmap to quickly run network scans
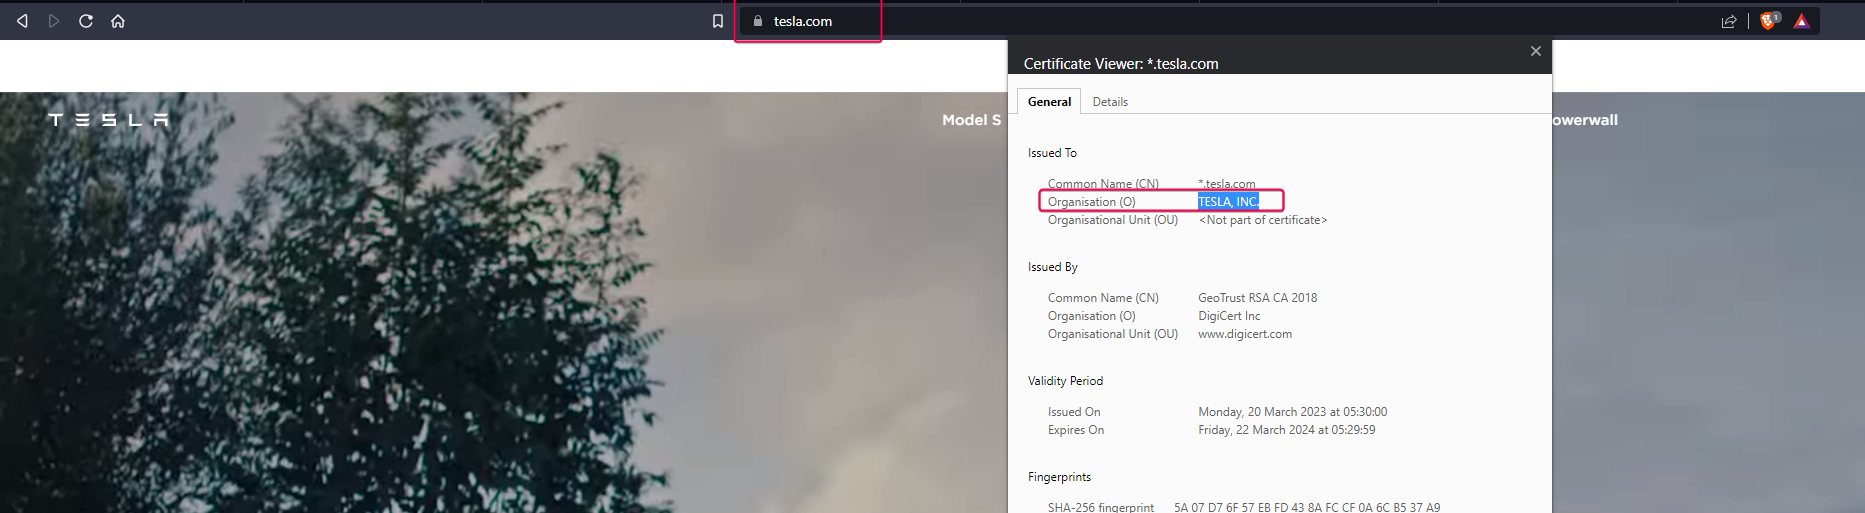 mr-rizwan-syed/chomtesh
CHOMTE.SH is a powerful shell script designed to automate reconnaissance tasks during penetration testing. It utilizes various Go-based tools to…
 luijait/gonet-scanner
Golang network scanner with arp discovery and own parser
 hcbaker/puwr
Pivot your way deeper into computer networks with SSH compromised machines.
 0xor0ne/qscan
Quick network scanner library. https://crates.io/crates/qscan