

KUMO-Domain-Recon-Tool
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
dns-analysisinformation-gatheringosint+8
99
karim852/kumo-domain-recon-toolDomain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 thewhiteh4t/finalrecon
Automated web reconnaissance tool providing header analysis, DNS enumeration, subdomain discovery, directory scanning, SSL inspection, and port…
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 tuhinshubhra/red_hawk
All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
 vqkro/higernes
a passive OSINT toolkit in python and c++ usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 robertdavidgraham/masscan
TCP port scanner, spews SYN packets asynchronously, scanning entire Internet in under 5 minutes.
 projectdiscovery/naabu
A fast port scanner written in go with a focus on reliability and simplicity. Designed to be used in combination with other tools for attack surface…
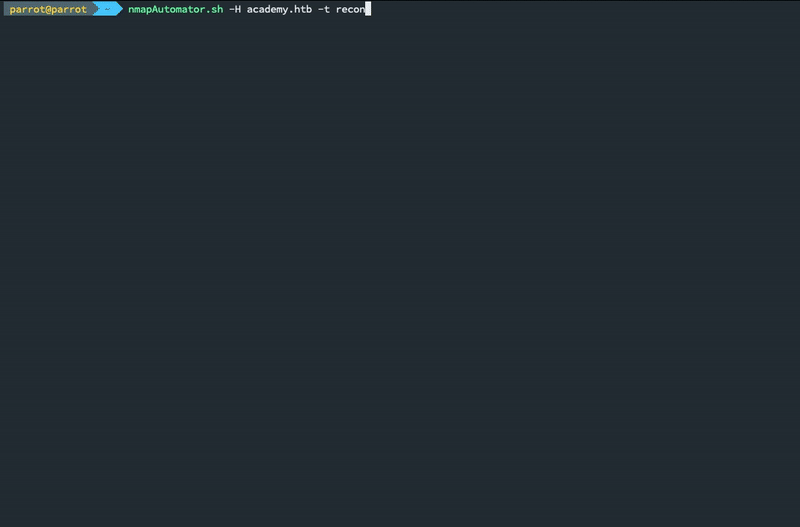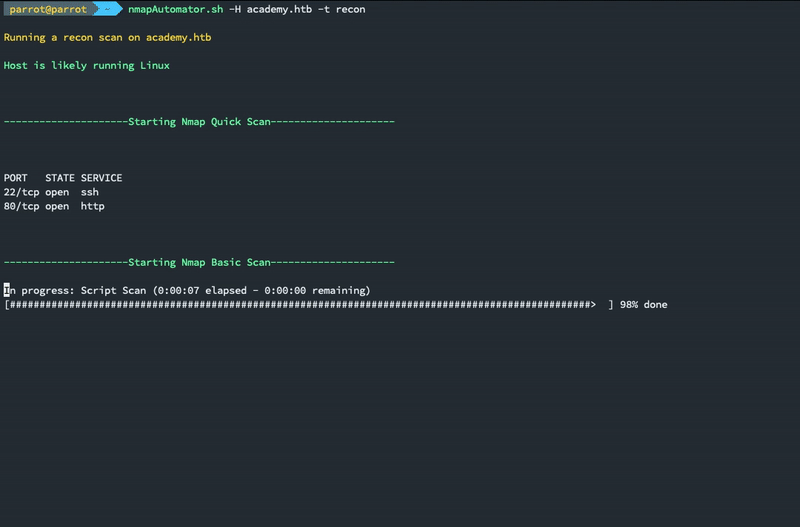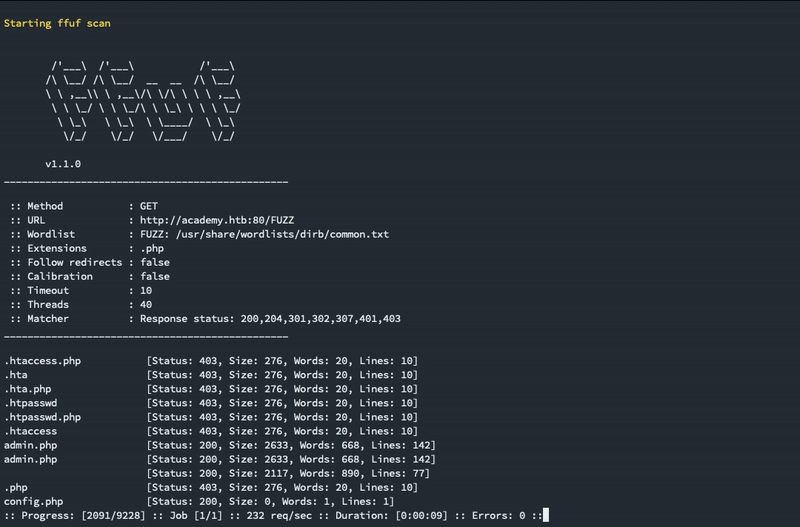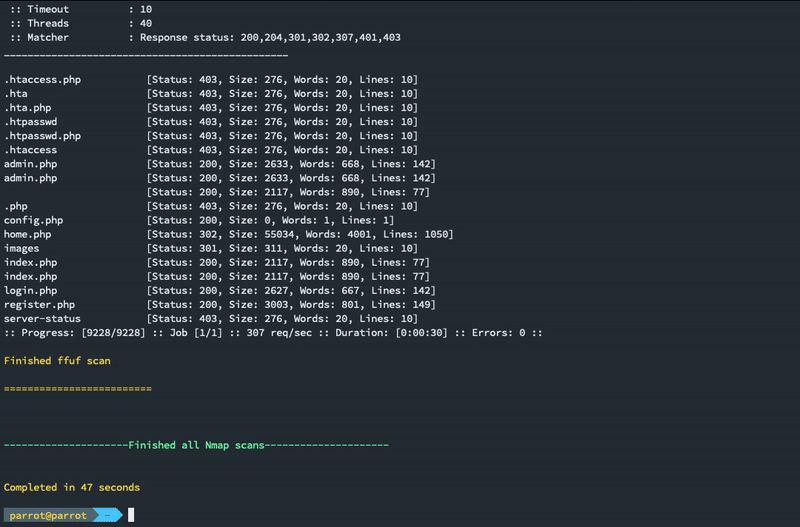 21y4d/nmapautomator
A script that you can run in the background!
 besimorhino/powercat
netshell features all in version 2 powershell
 lionsec/xerosploit
Efficient and advanced man in the middle framework
 eldraco/domain_analyzer
Analyze the security of any domain by finding all the information possible. Made in python.
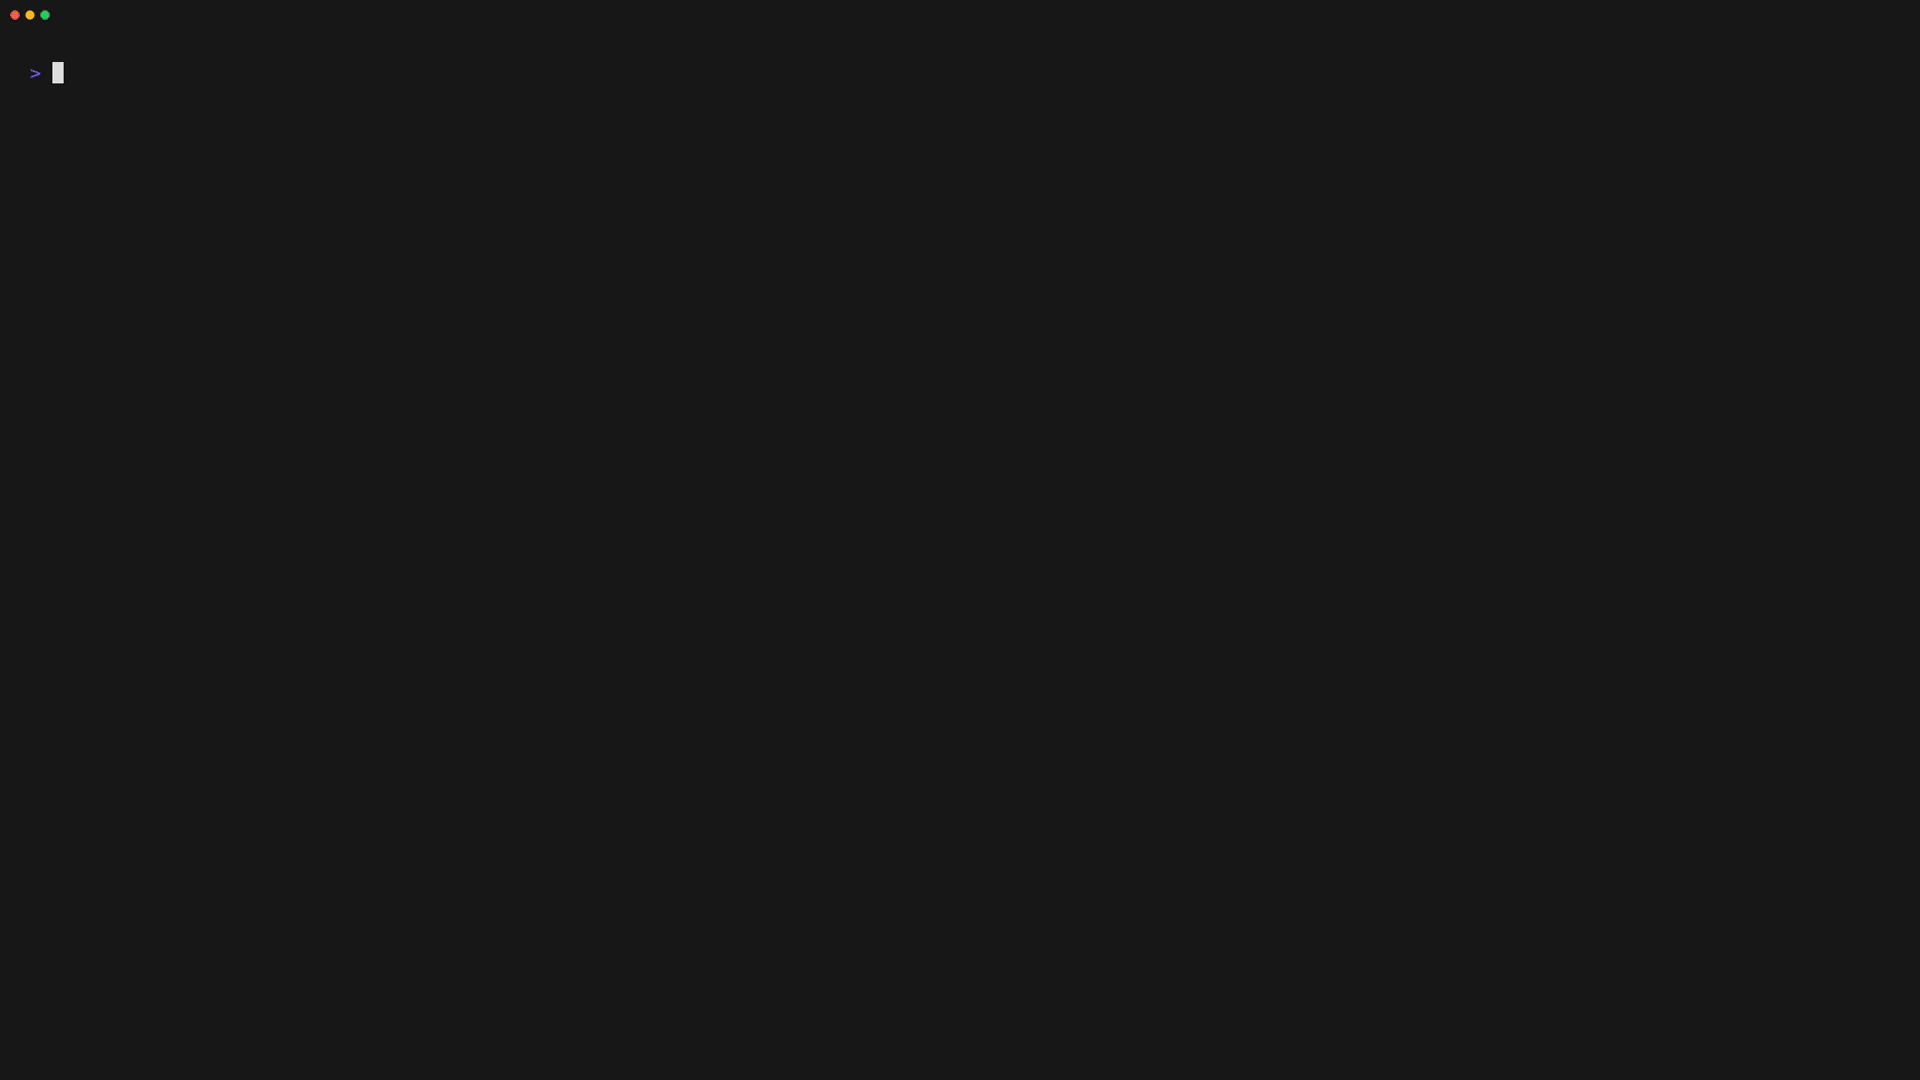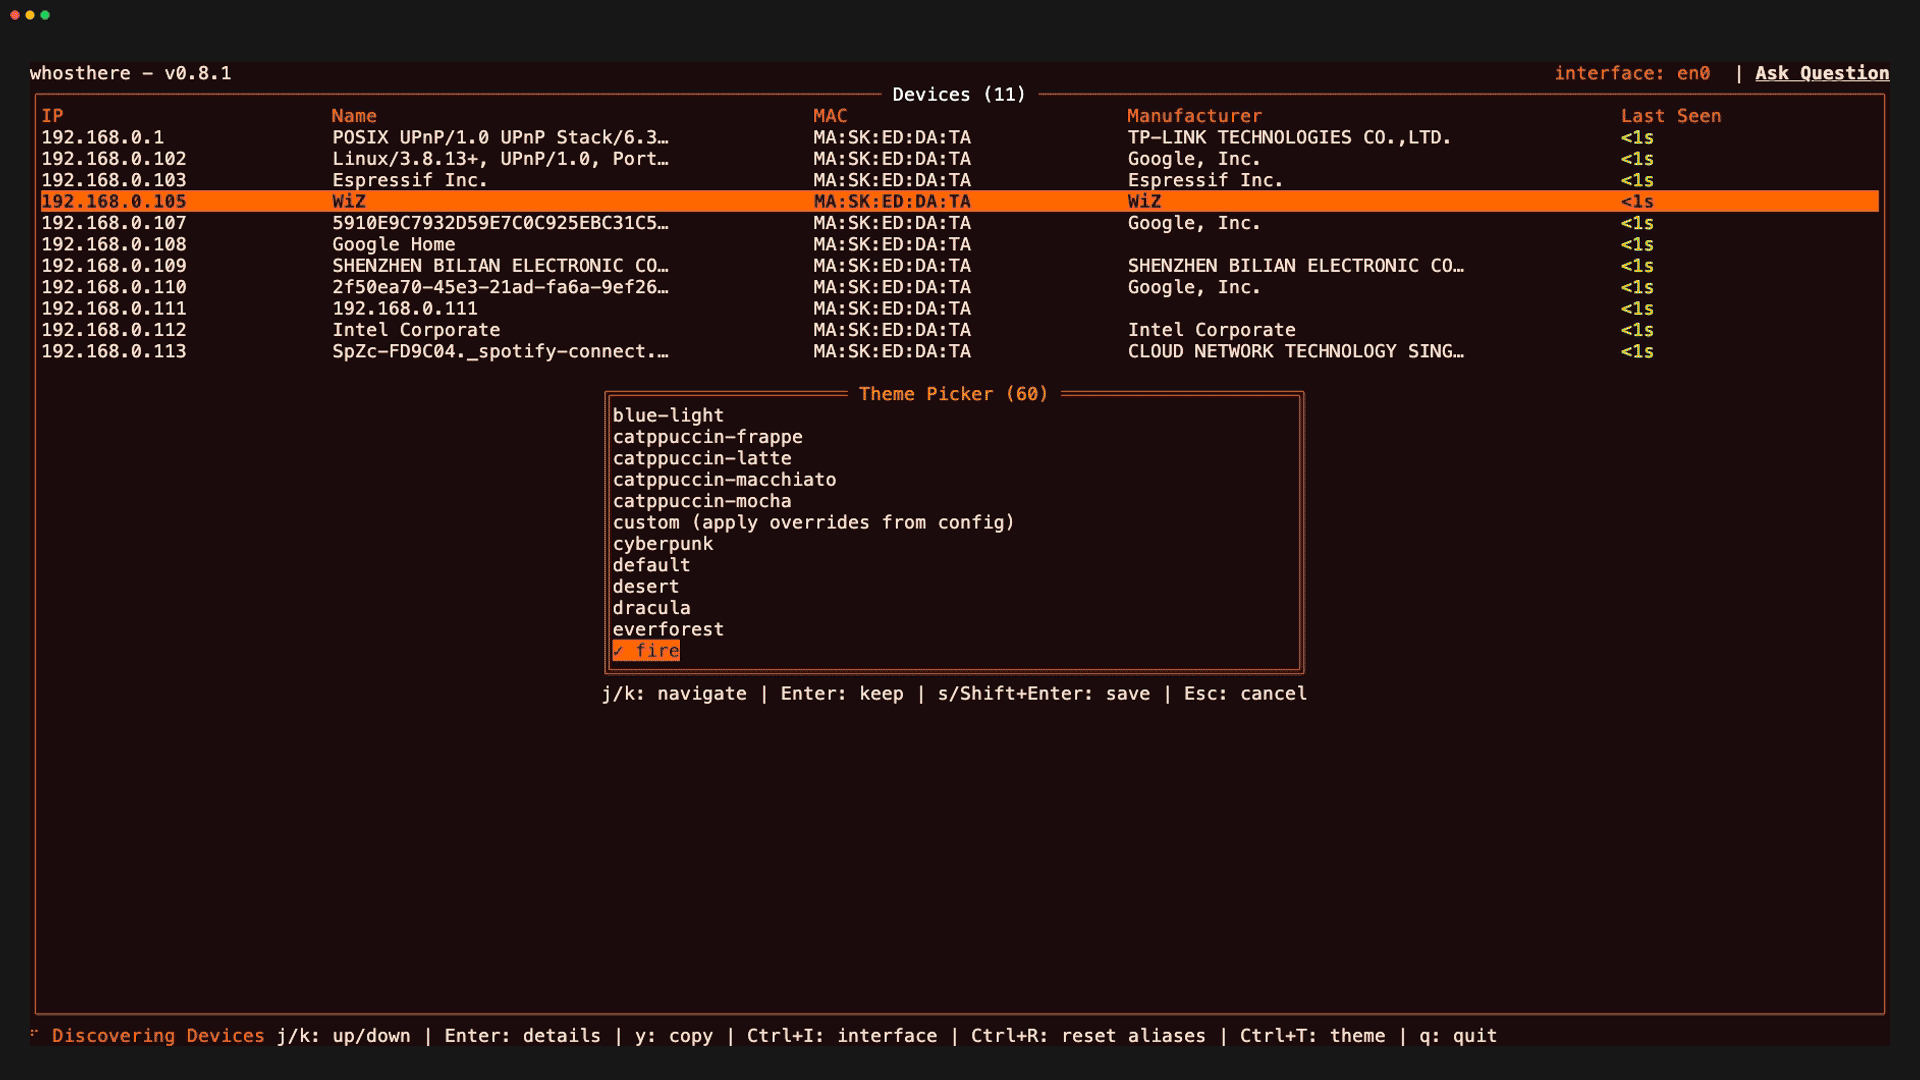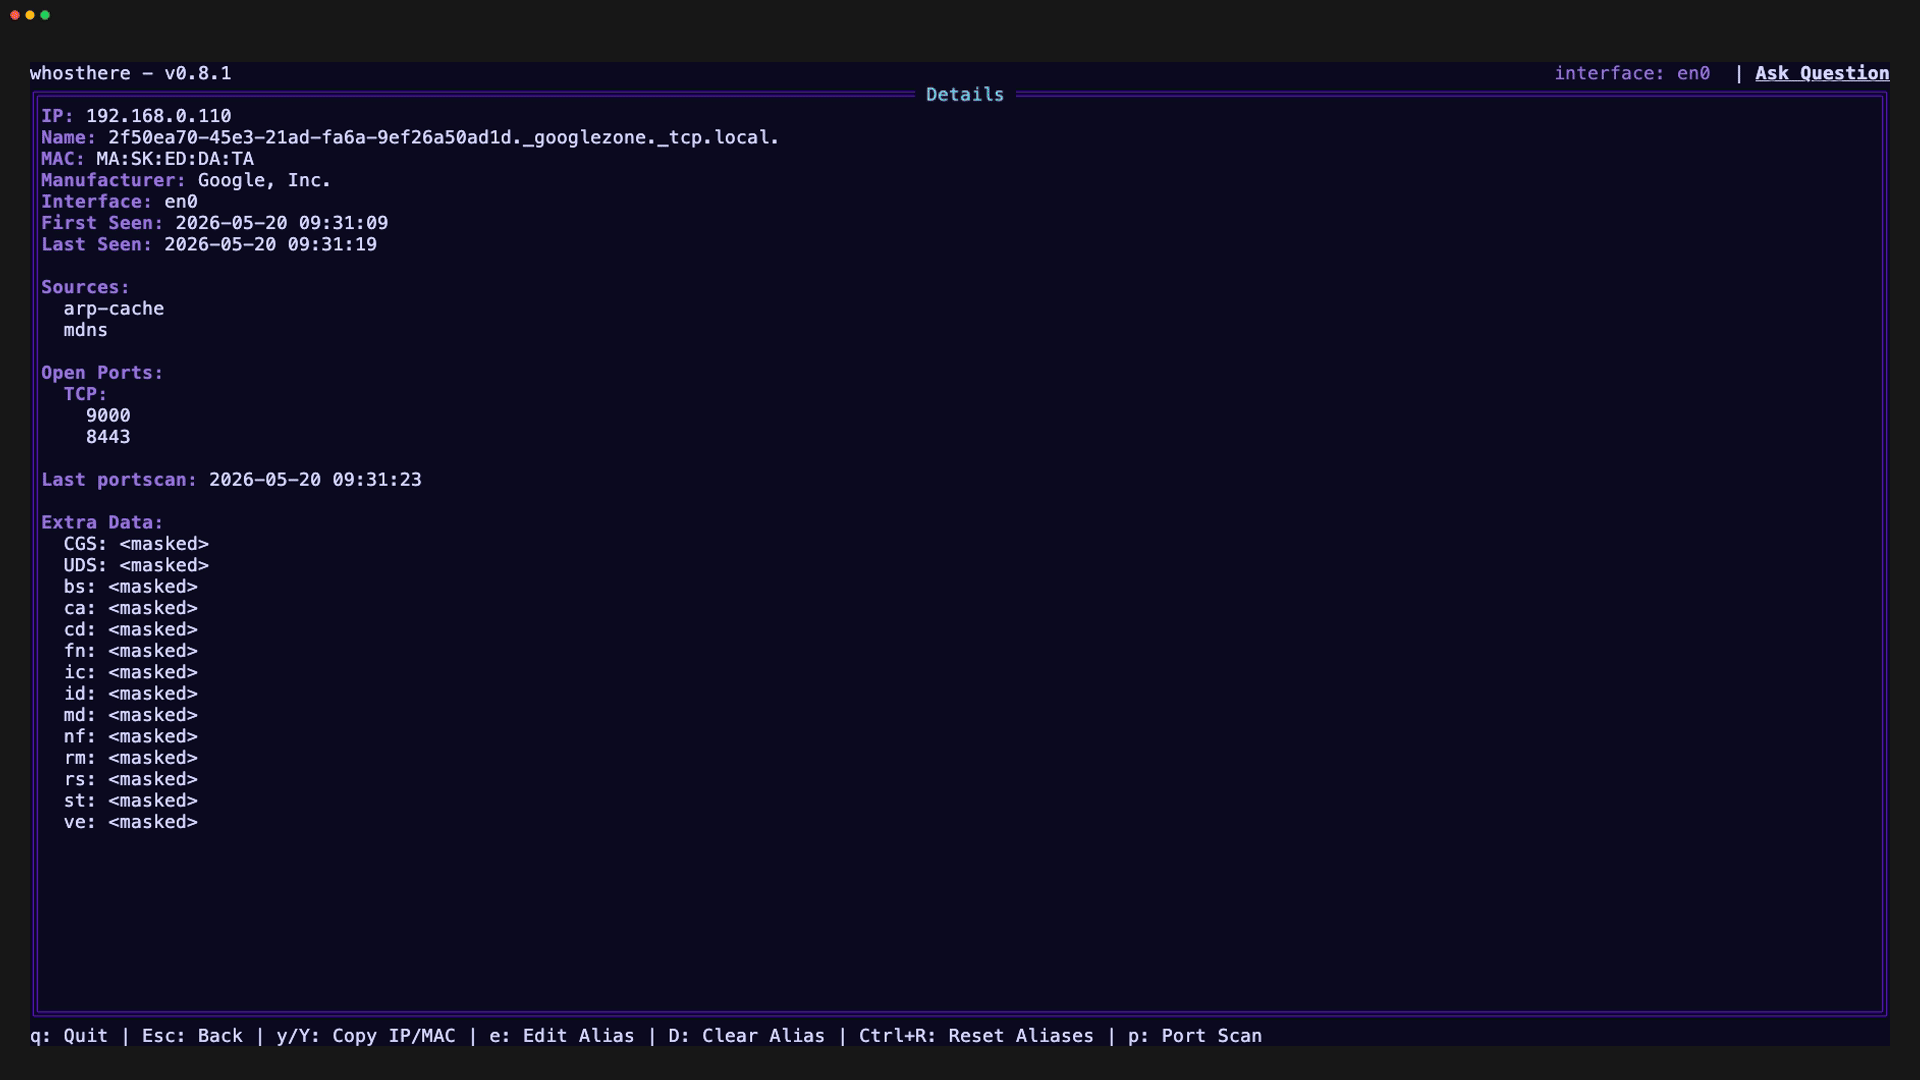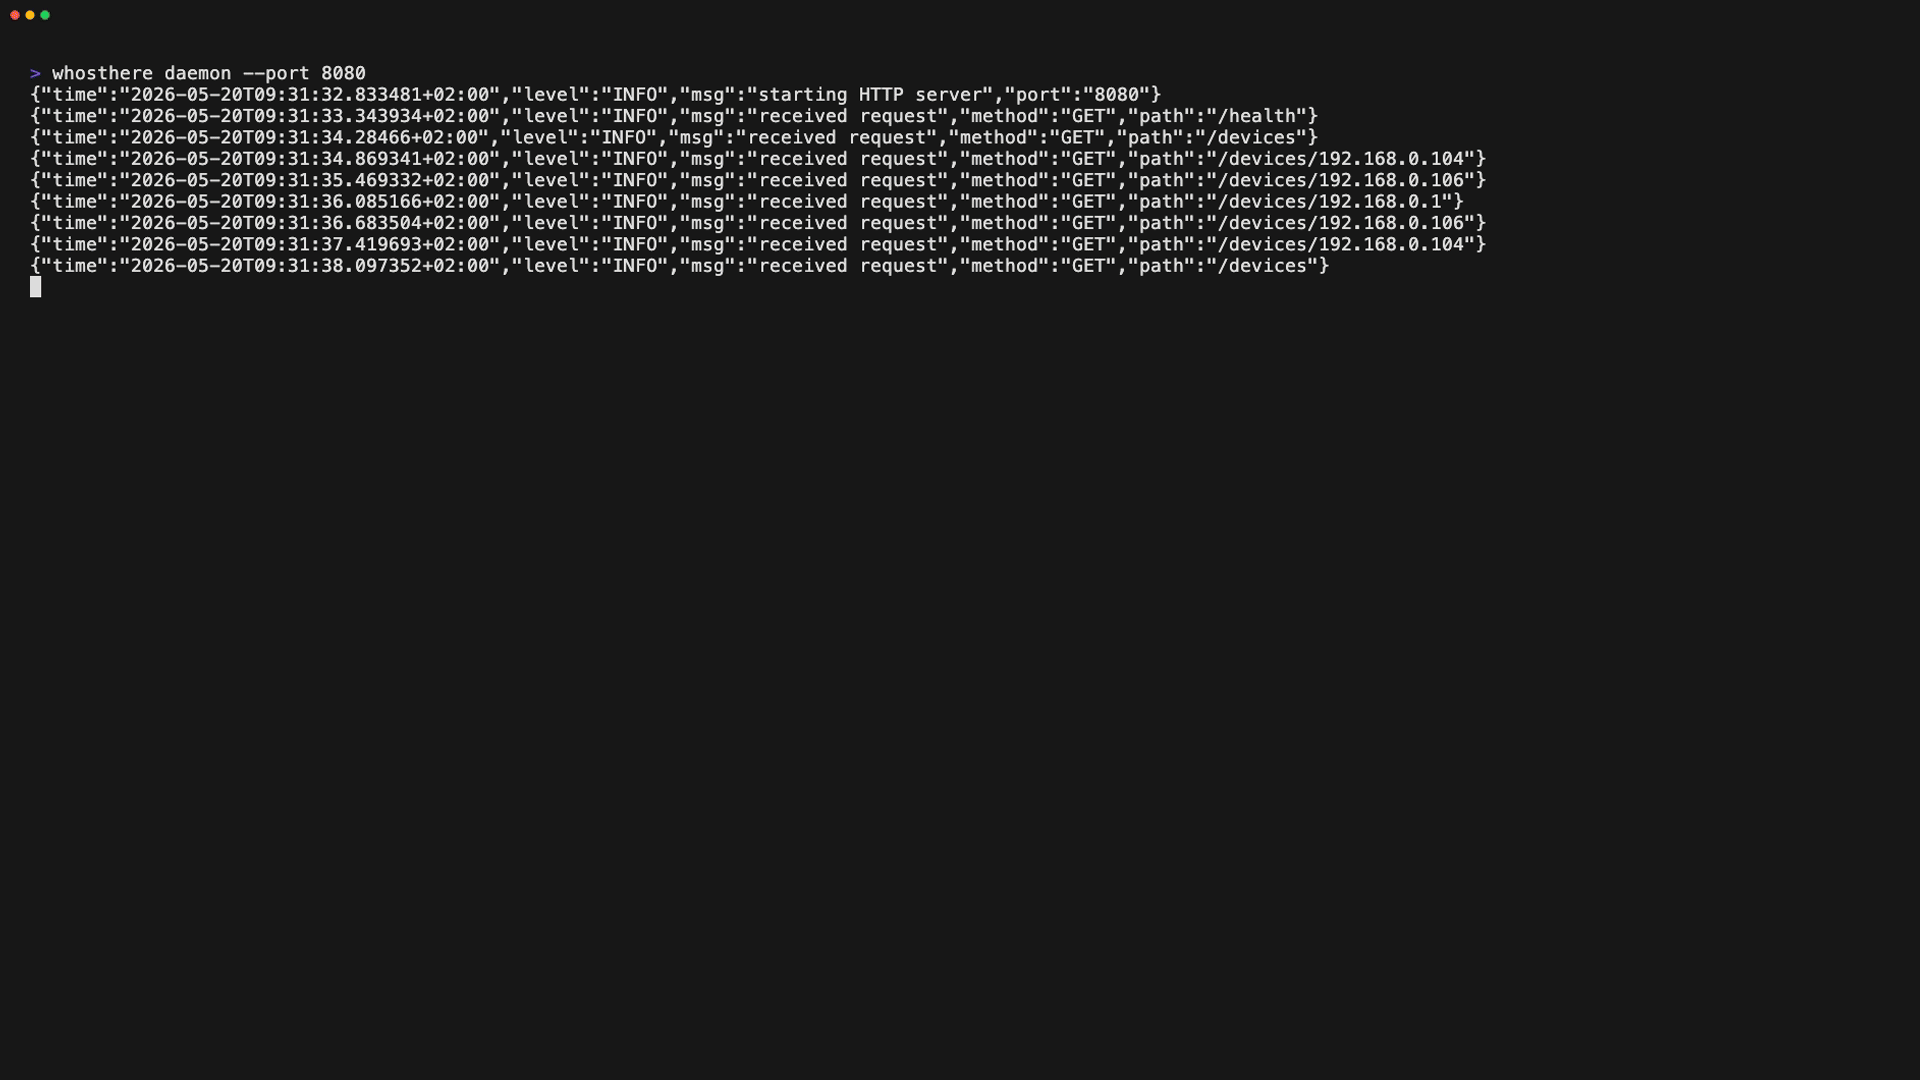 ramonvermeulen/whosthere
Local Area Network discovery tool with an interactive Terminal User Interface (TUI) written in Go. Discover, explore, and understand your LAN in an…
 robotshell/magicrecon
MagicRecon is a powerful shell script to maximize the recon and data collection process of an objective and finding common vulnerabilities, all this…
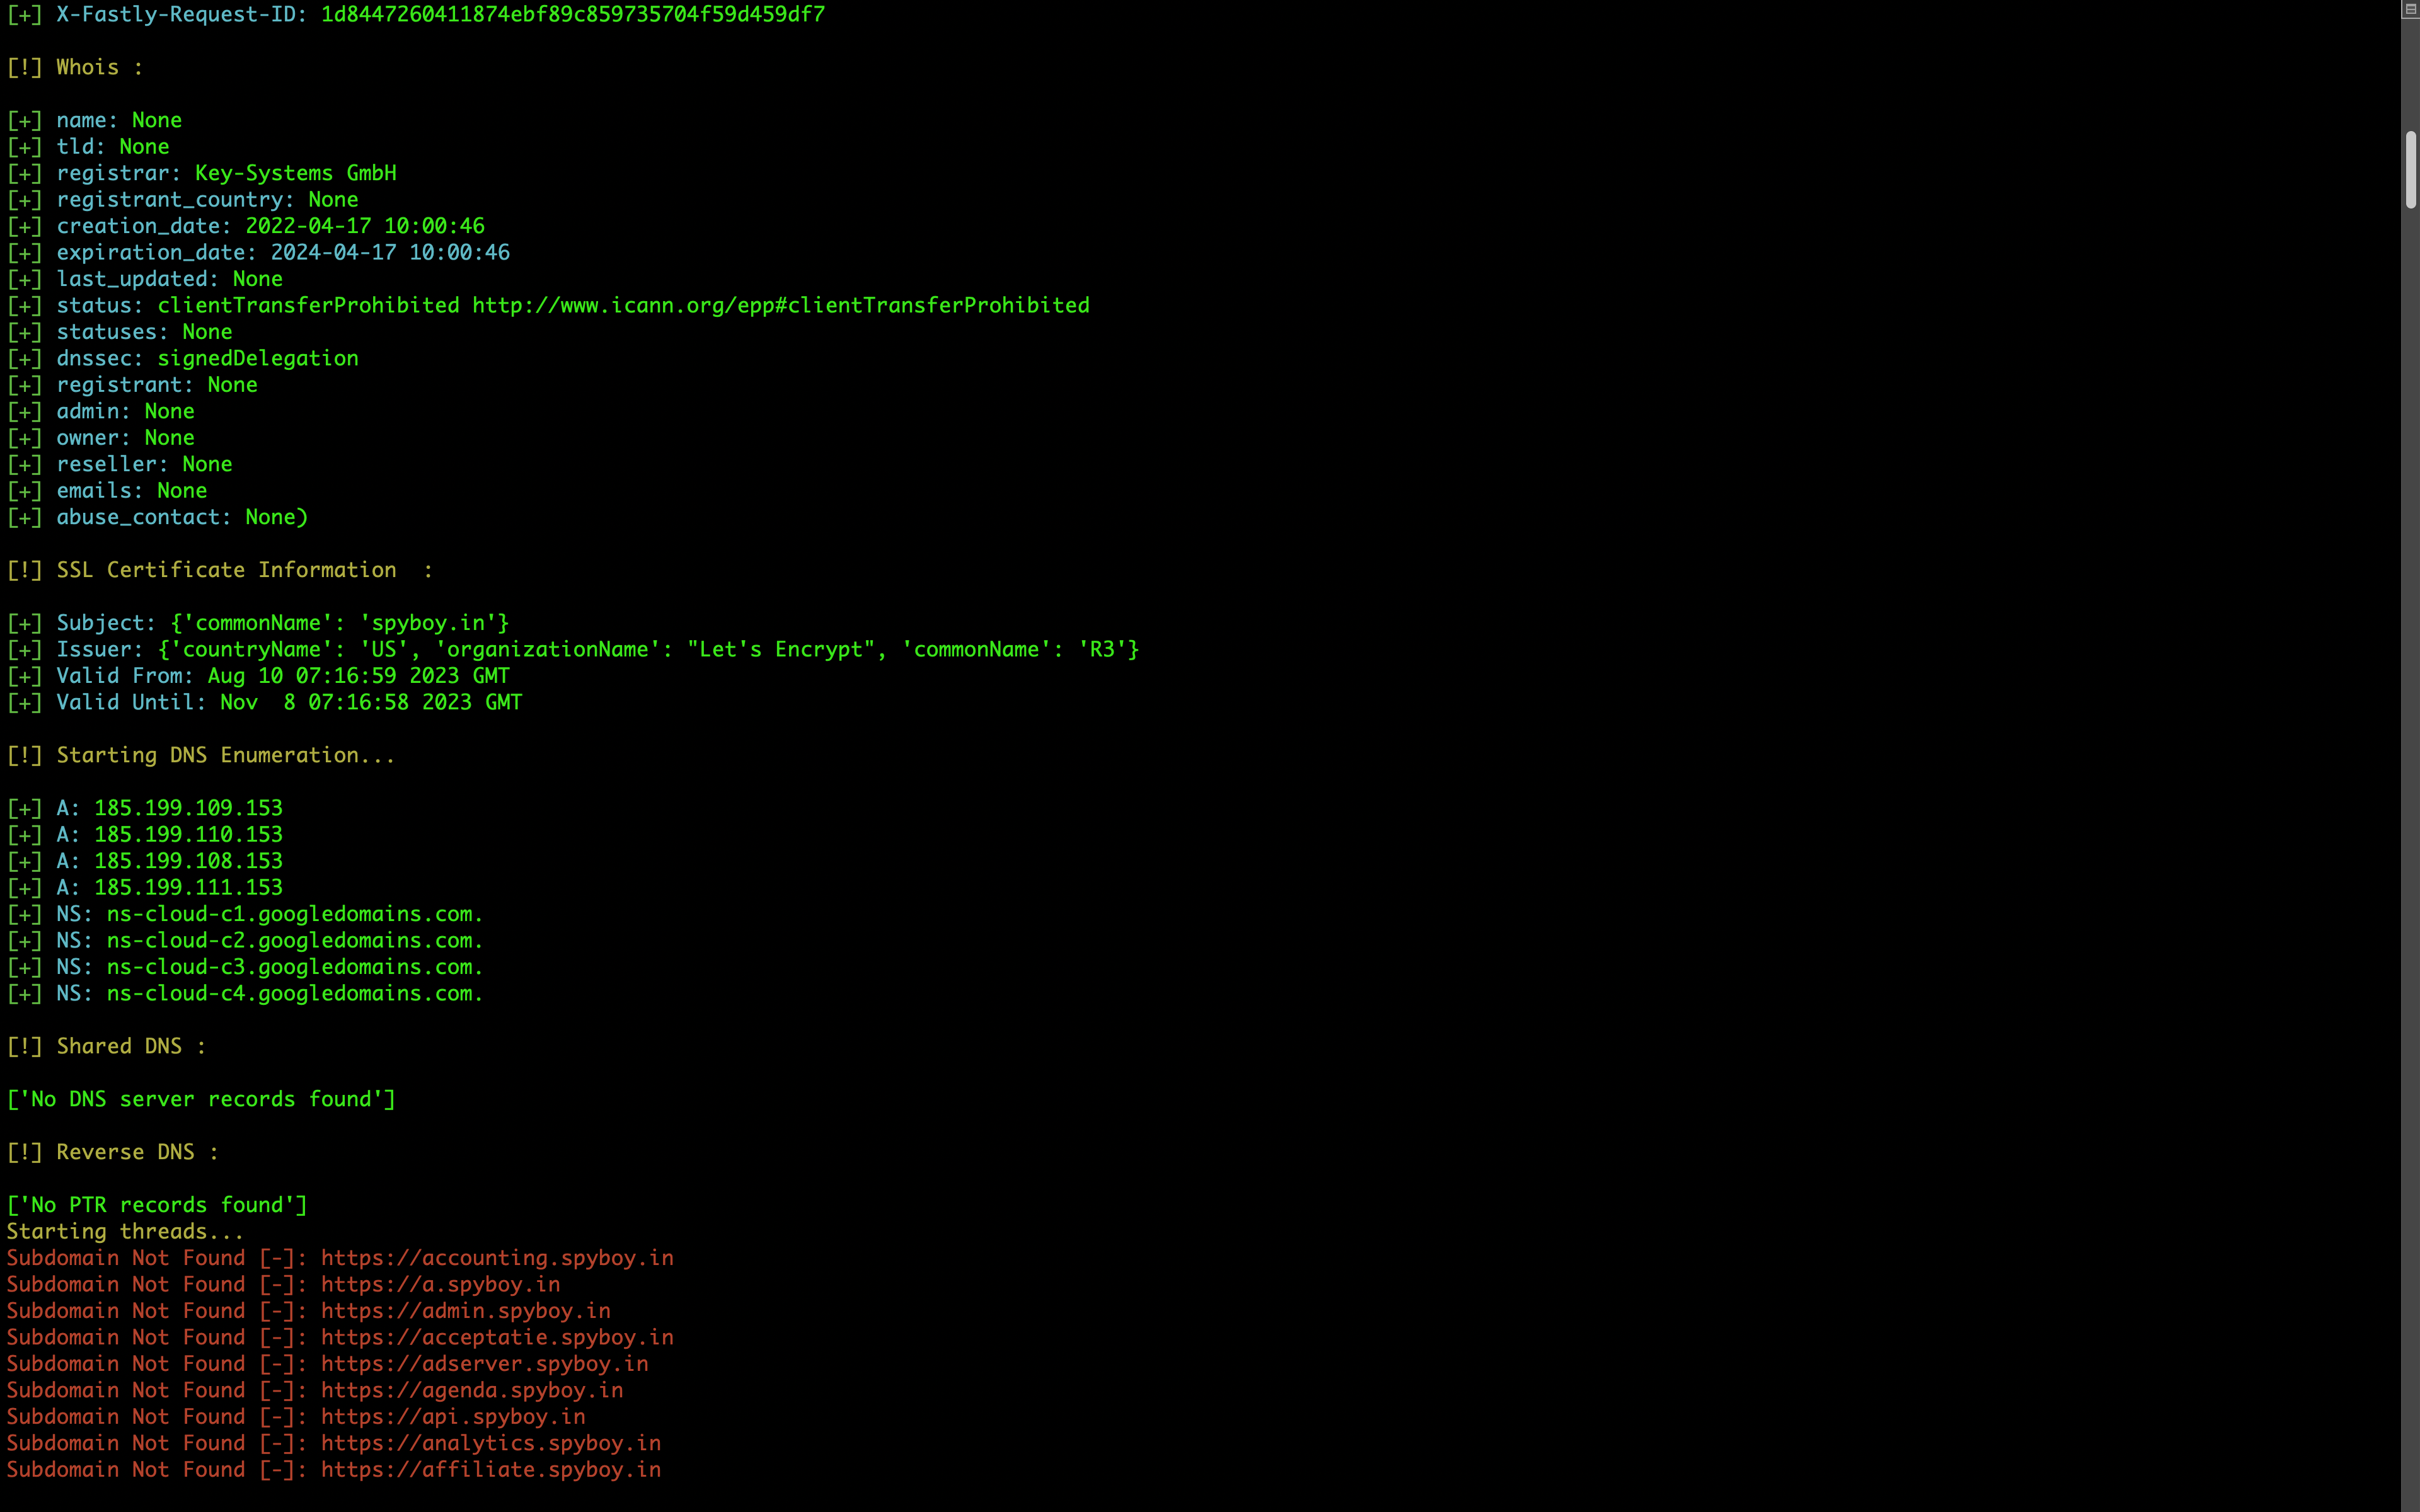 spyboy-productions/omnisci3nt
Omnisci3nt is an open-source web reconnaissance and intelligence tool for extracting deep technical insights from domains, including subdomains, SSL…
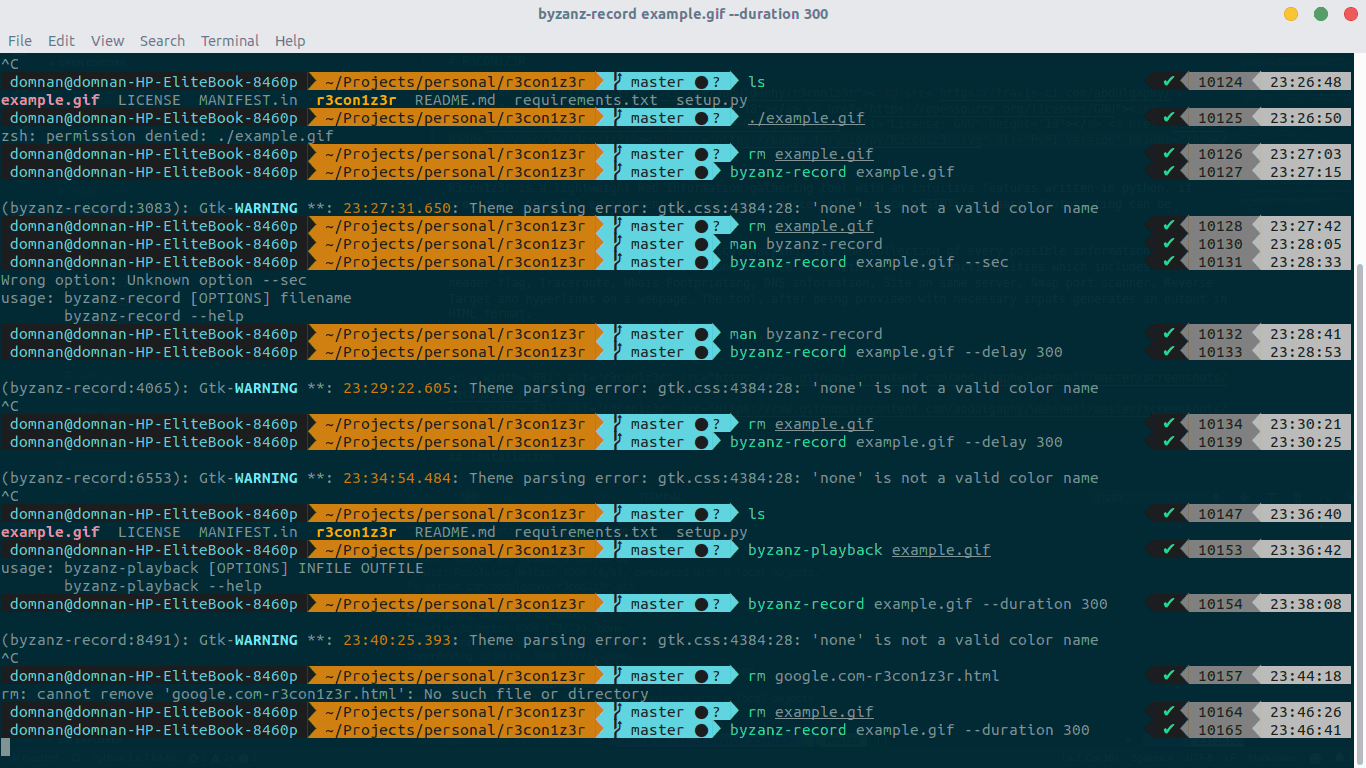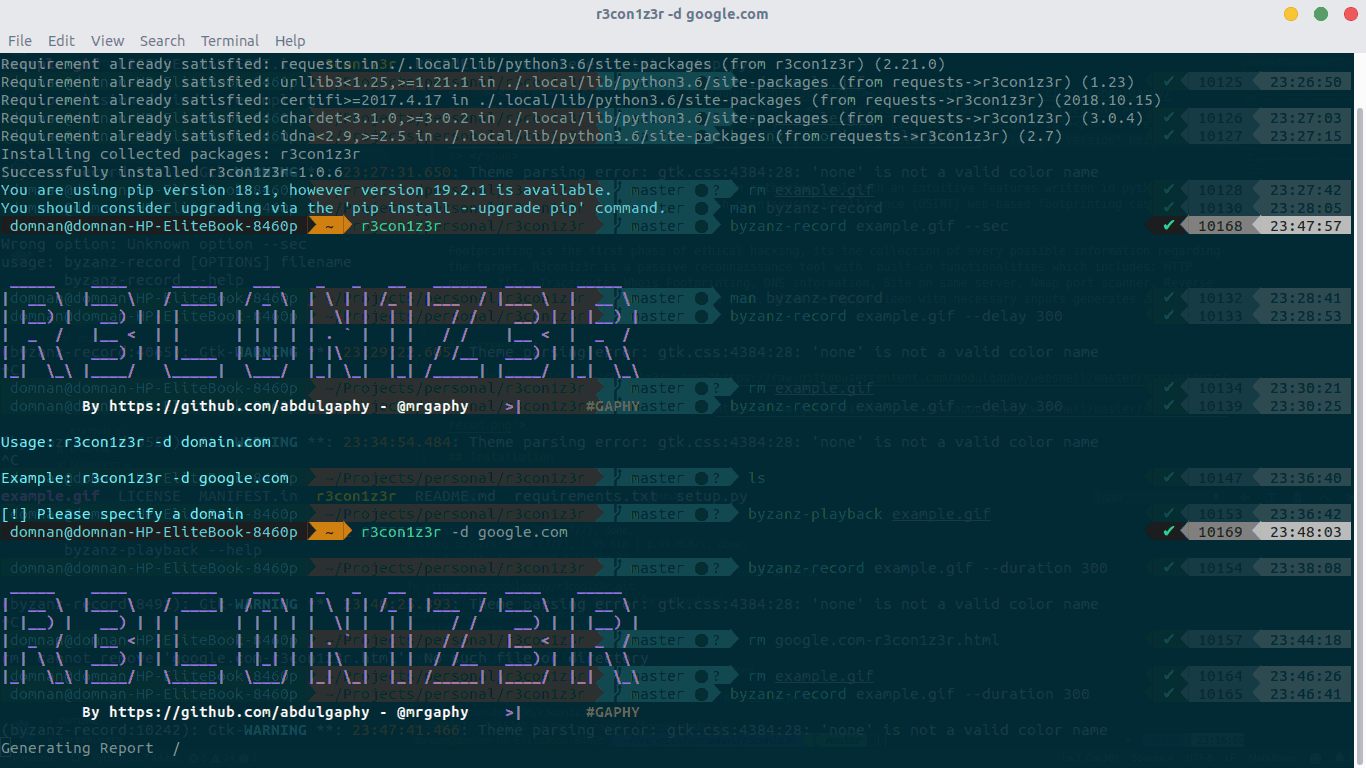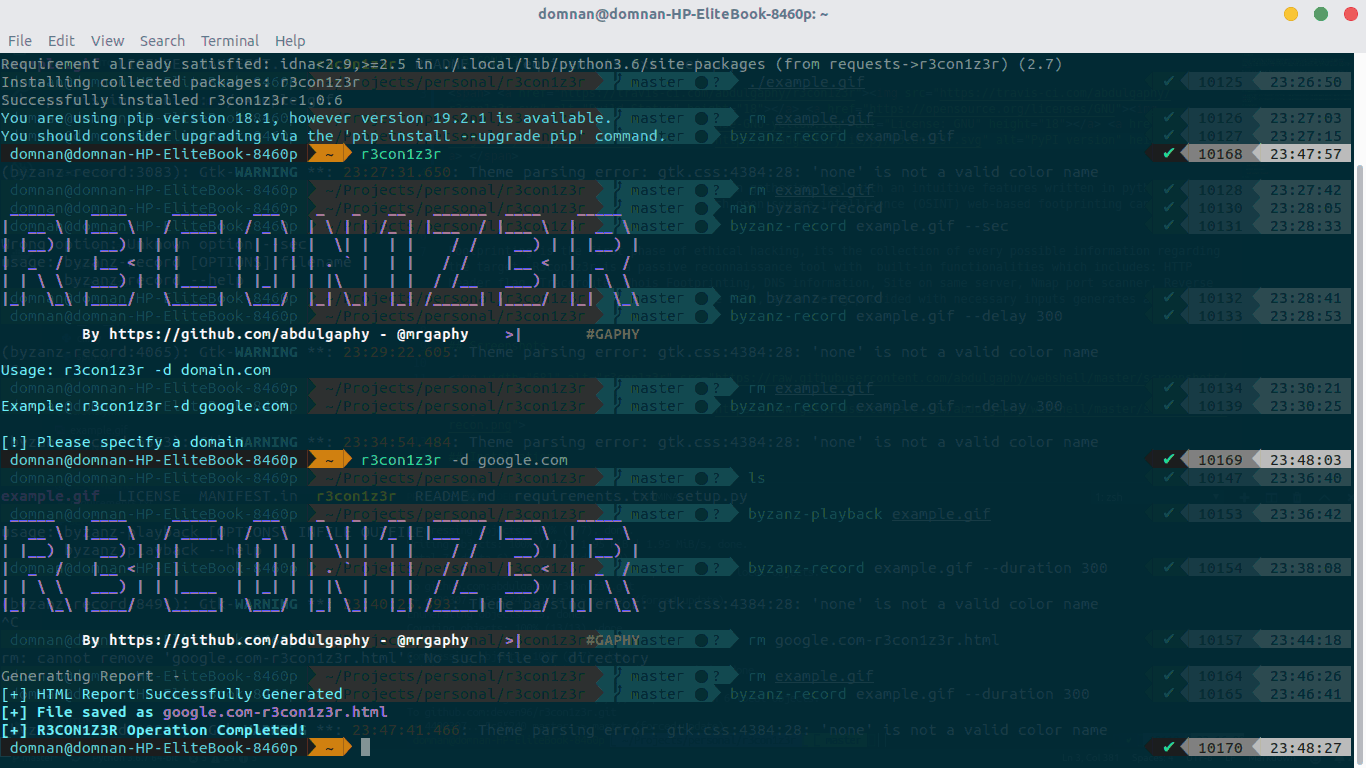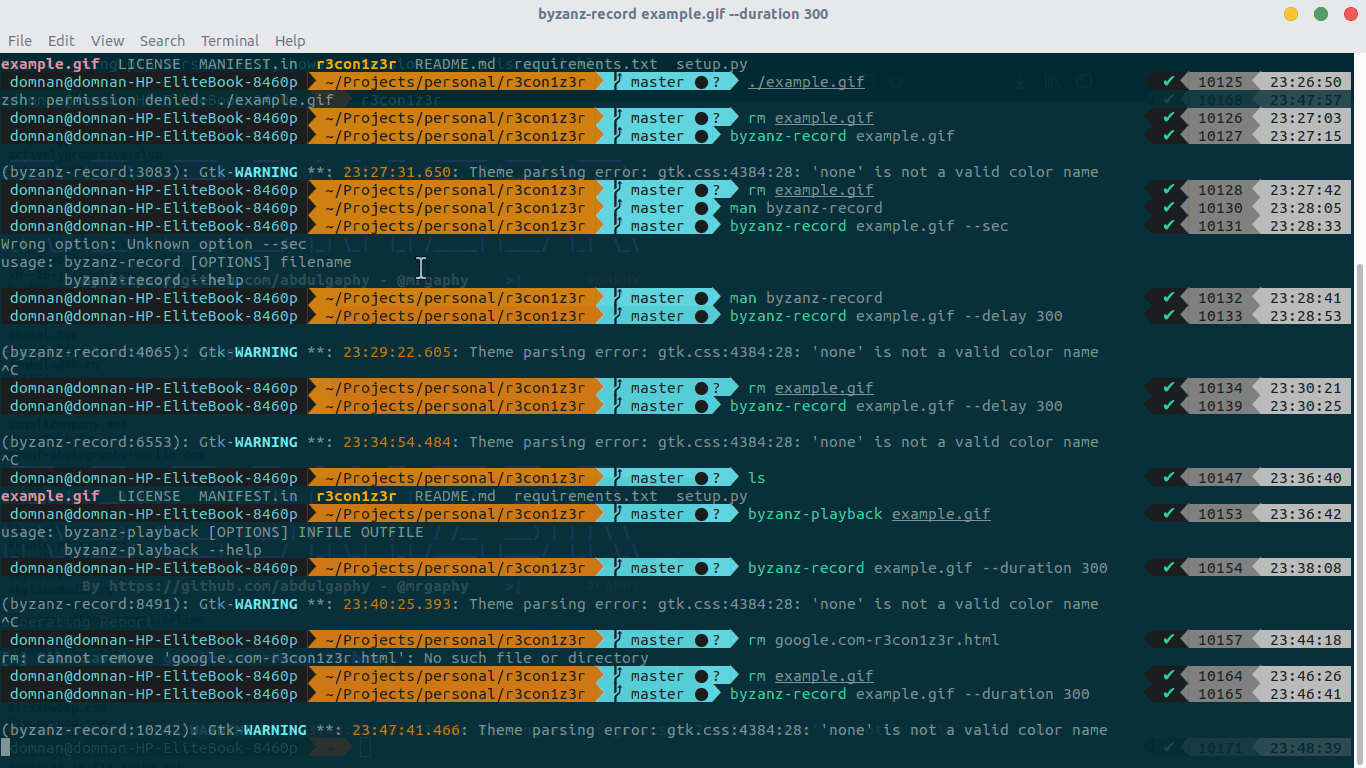 abdulgaphy/r3con1z3r
R3con1z3r is a lightweight Web information gathering tool with an intuitive features written in python. it provides a powerful environment in which…
 flipkart-incubator/rta
Red team Arsenal - An intelligent scanner to detect security vulnerabilities in company's layer 7 assets.
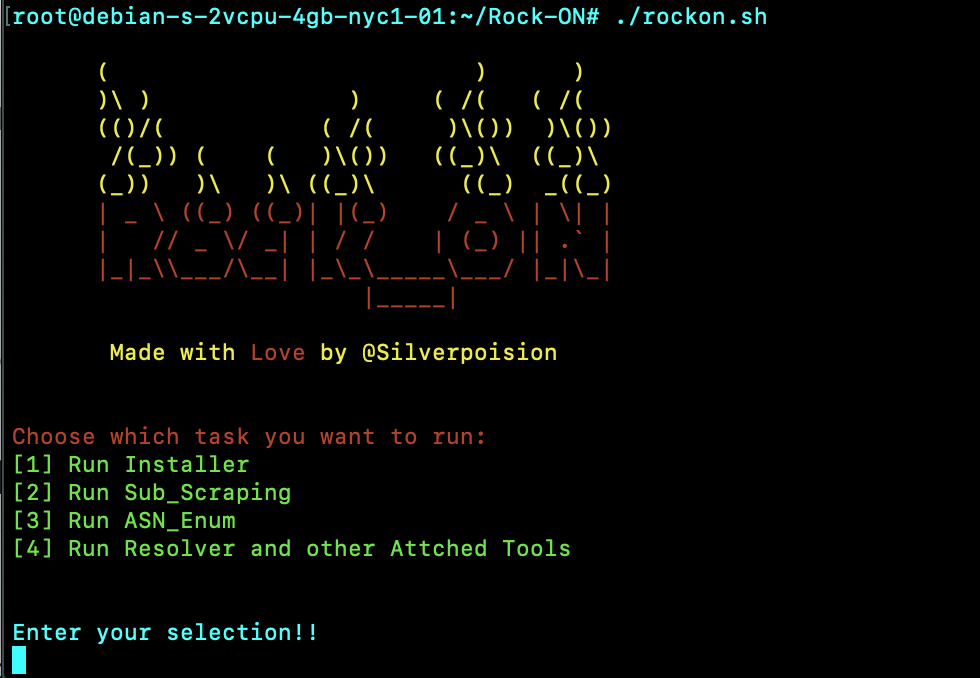 silverpoision/rock-on
Rock-On is a all in one Recon tool that will just get a single entry of the Domain name and do all of the work alone.
 nullt3r/udpx
Single-packet UDP scanner in Go for fast discovery of 45+ services across networks, supporting custom probes, CIDR scanning, and JSONL output.