
docker-onion-nmap
 milesrichardson/docker-onion-nmap
Scan .onion hidden services with nmap using Tor, proxychains and dnsmasq in a minimal alpine Docker container.
container-securitydns-analysisinformation-gathering+8
milesrichardson/docker-onion-nmapScan .onion hidden services with nmap using Tor, proxychains and dnsmasq in a minimal alpine Docker container.
 thewhiteh4t/finalrecon
Automated web reconnaissance tool providing header analysis, DNS enumeration, subdomain discovery, directory scanning, SSL inspection, and port…
 raskrebs/sonar
CLI tool for inspecting and managing services listening on localhost ports
 yakushstanislav/ultraviolet
Self-hosted network discovery and search engine with continuous port scanning, deep protocol probing across ~100 services, local CVE matching, and…
 abacus-group-rto/legion
Legion is an open source, easy-to-use, super-extensible and semi-automated network penetration testing tool that aids in discovery, reconnaissance…
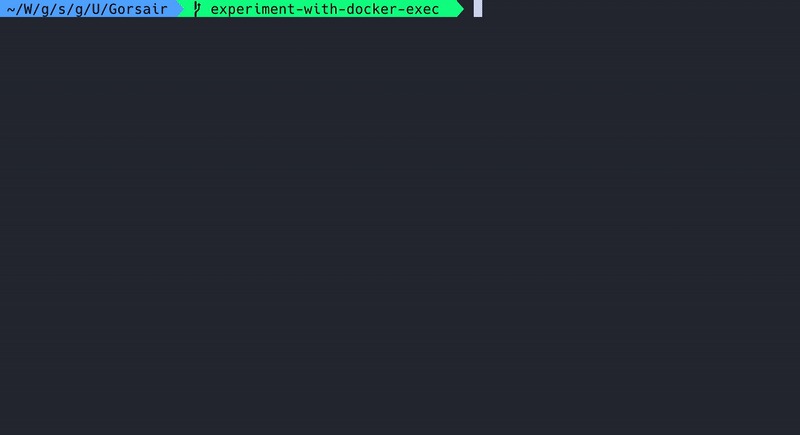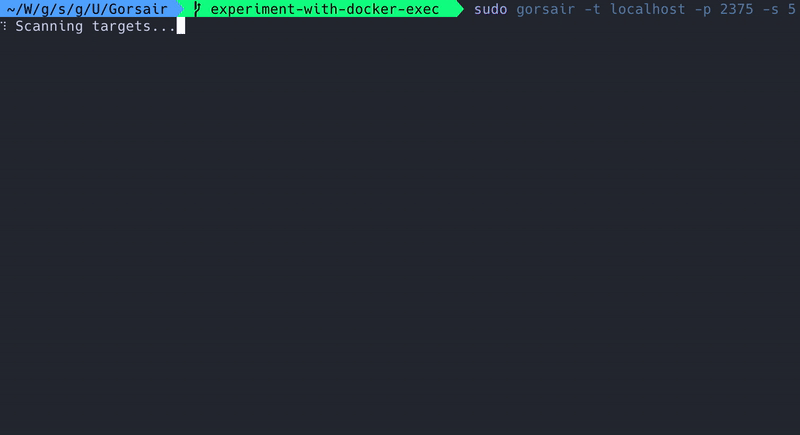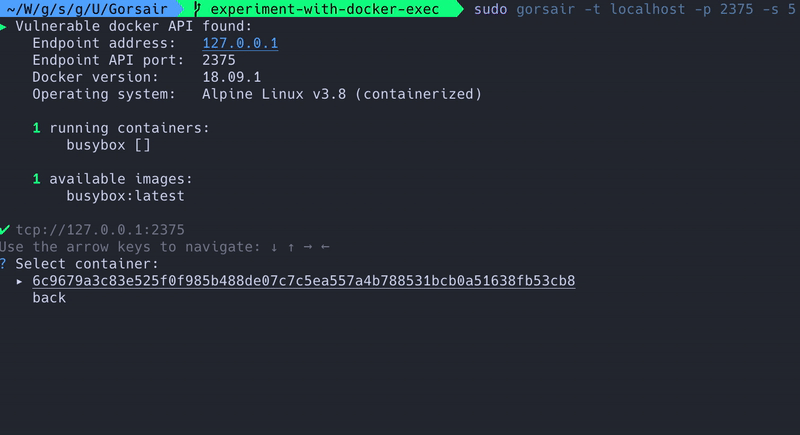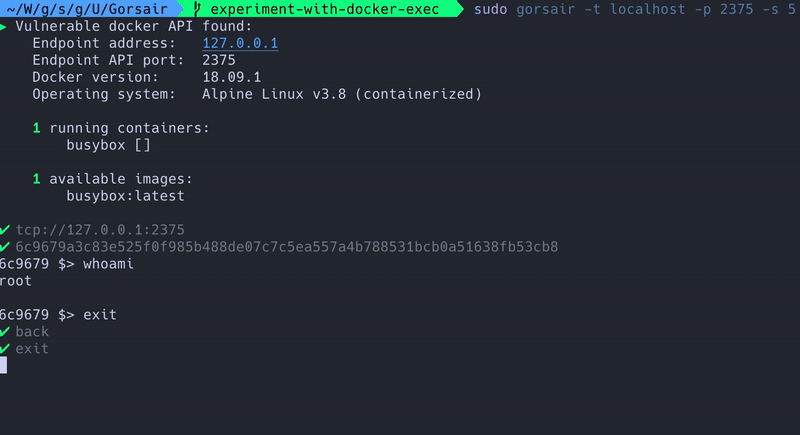 ullaakut/gorsair
Gorsair gives root access on remote docker containers that expose their APIs
 chvancooten/bugbountyscanner
A Bash script and Docker image for Bug Bounty reconnaissance. Intended for headless use.
 znakar/sharktooth
Port Scanner with Docker & Prometheus + Grafana integration. A tool for network auditing with multithreading support and real-time monitoring.
 bee-san/rustscan
🤖 The Modern Port Scanner 🤖
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
 v-byte-cpu/sx
:vulcan_salute: Fast, modern, easy-to-use network scanner
 marco-lancini/goscan
Interactive Network Scanner
 x1mdev/reconpi
ReconPi - A lightweight recon tool that performs extensive scanning with the latest tools.
 0xor0ne/qscan
Quick network scanner library. https://crates.io/crates/qscan
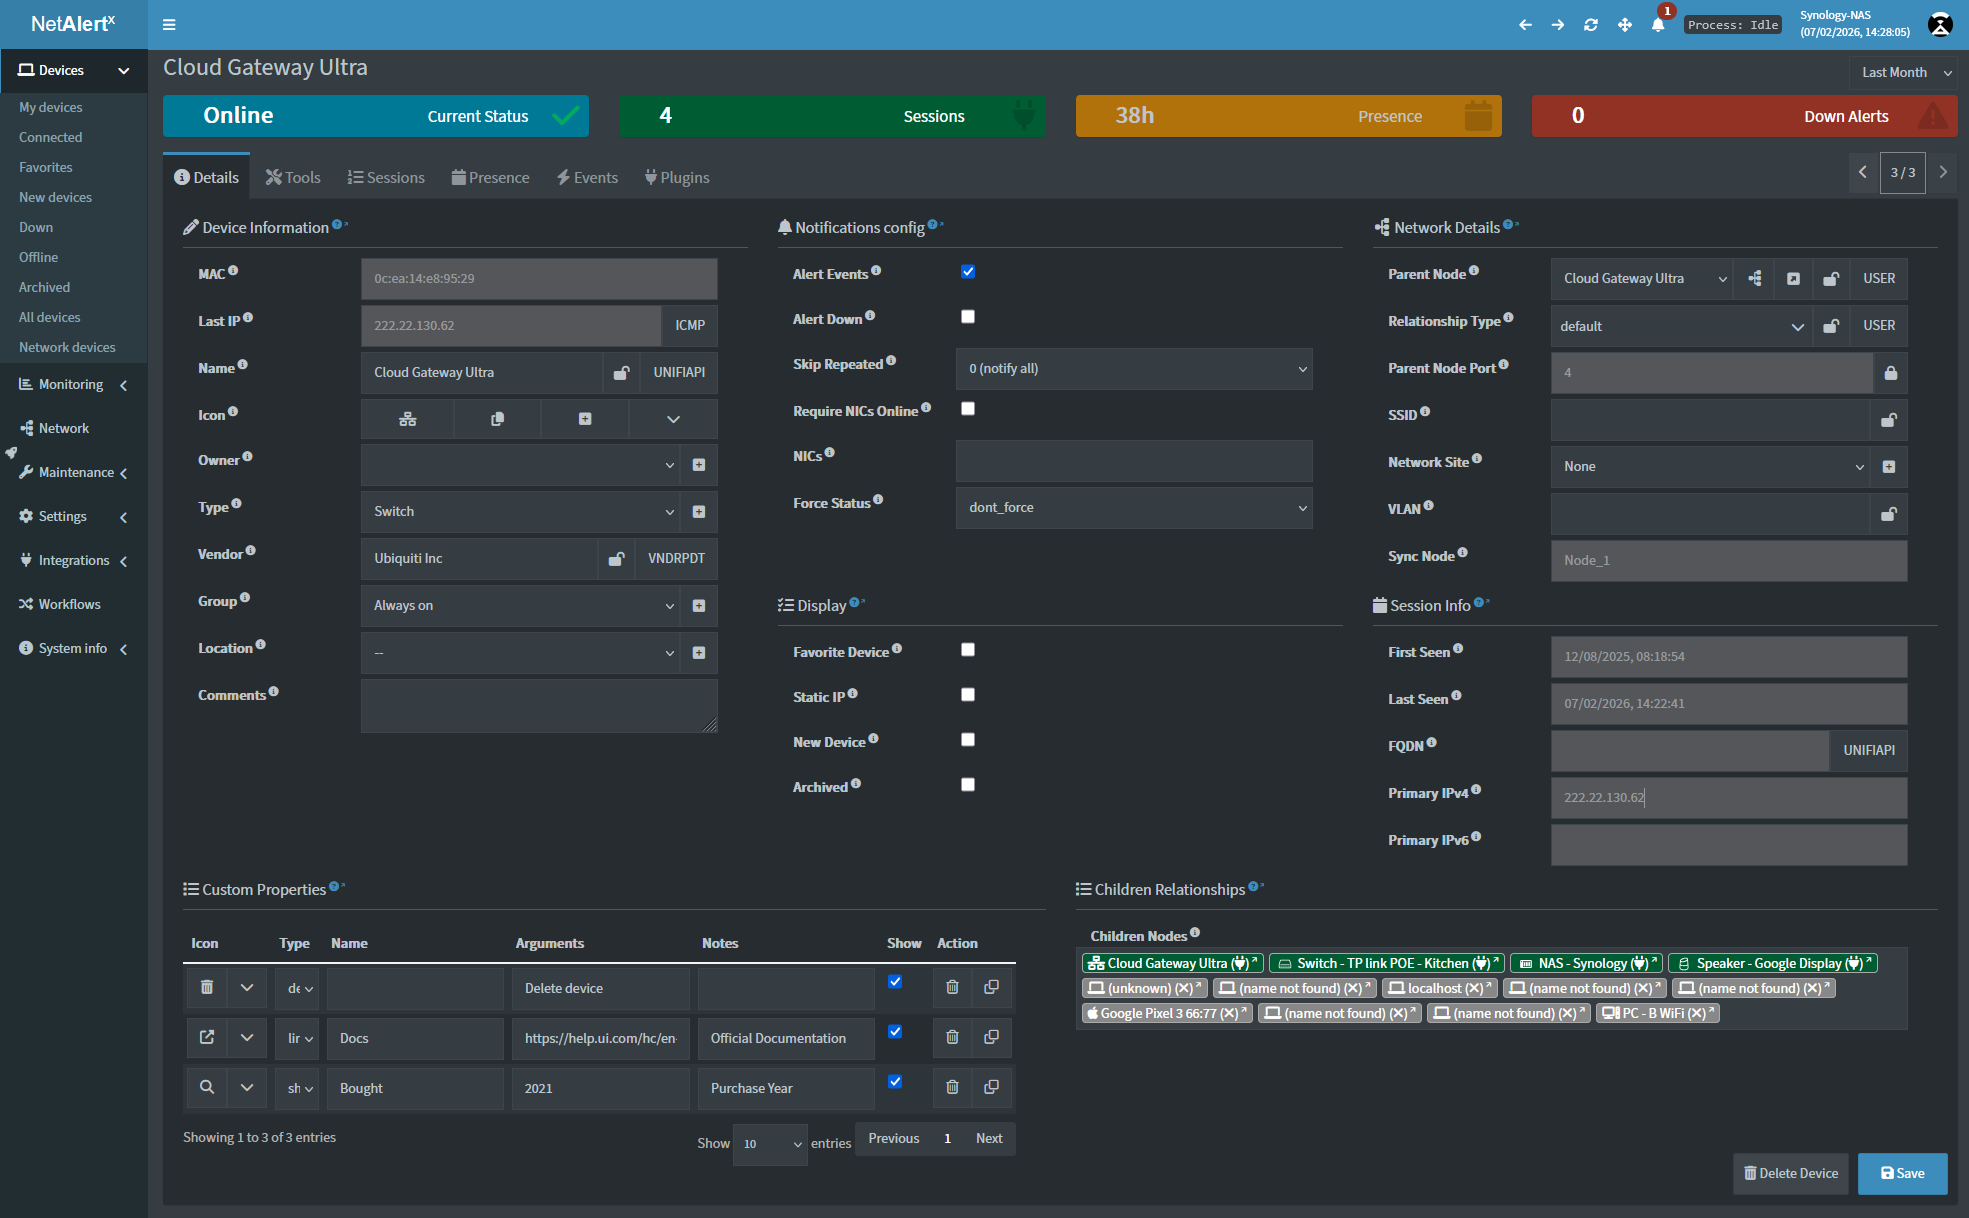 netalertx/netalertx
Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.
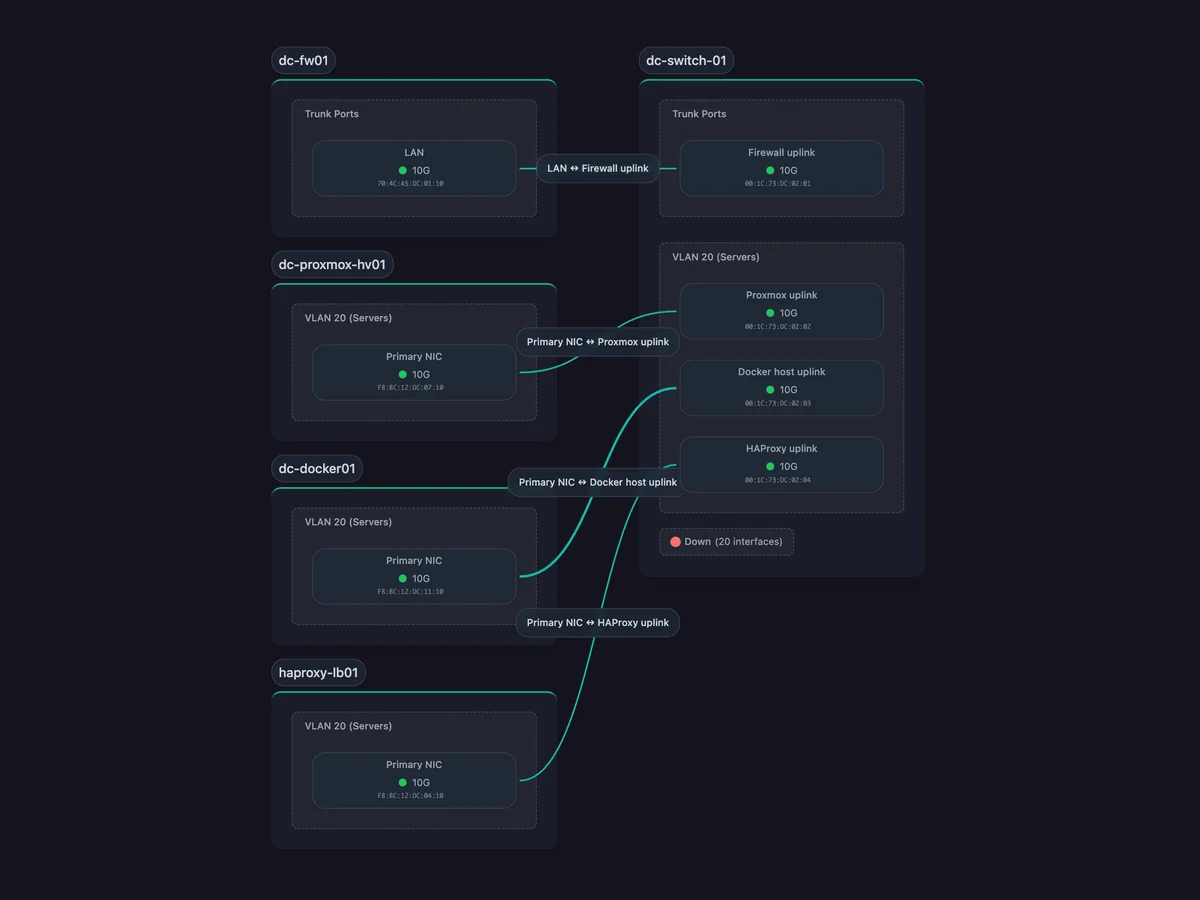 scanopy/scanopy
Network diagrams that update themselves
 cloudflare/flan
A pretty sweet vulnerability scanner
 tomnomnom/httprobe
Take a list of domains and probe for working HTTP and HTTPS servers