
log4shell_scanner
 linkmjb/log4shell_scanner
Quick and dirty scanner, hitting common ports looking for Log4Shell (CVE-2021-44228) vulnerability
exploitationinformation-gatheringnetwork-mapping+3
linkmjb/log4shell_scannerQuick and dirty scanner, hitting common ports looking for Log4Shell (CVE-2021-44228) vulnerability
 rv4l3r3/log4v-vuln-check
This script is used to perform a fast check if your server is possibly affected by CVE-2021-44228 (the log4j vulnerability).
 0xinfection/logmepwn
A fully automated, reliable, super-fast, scanning and validation toolkit for the Log4J RCE CVE-2021-44228 vulnerability.
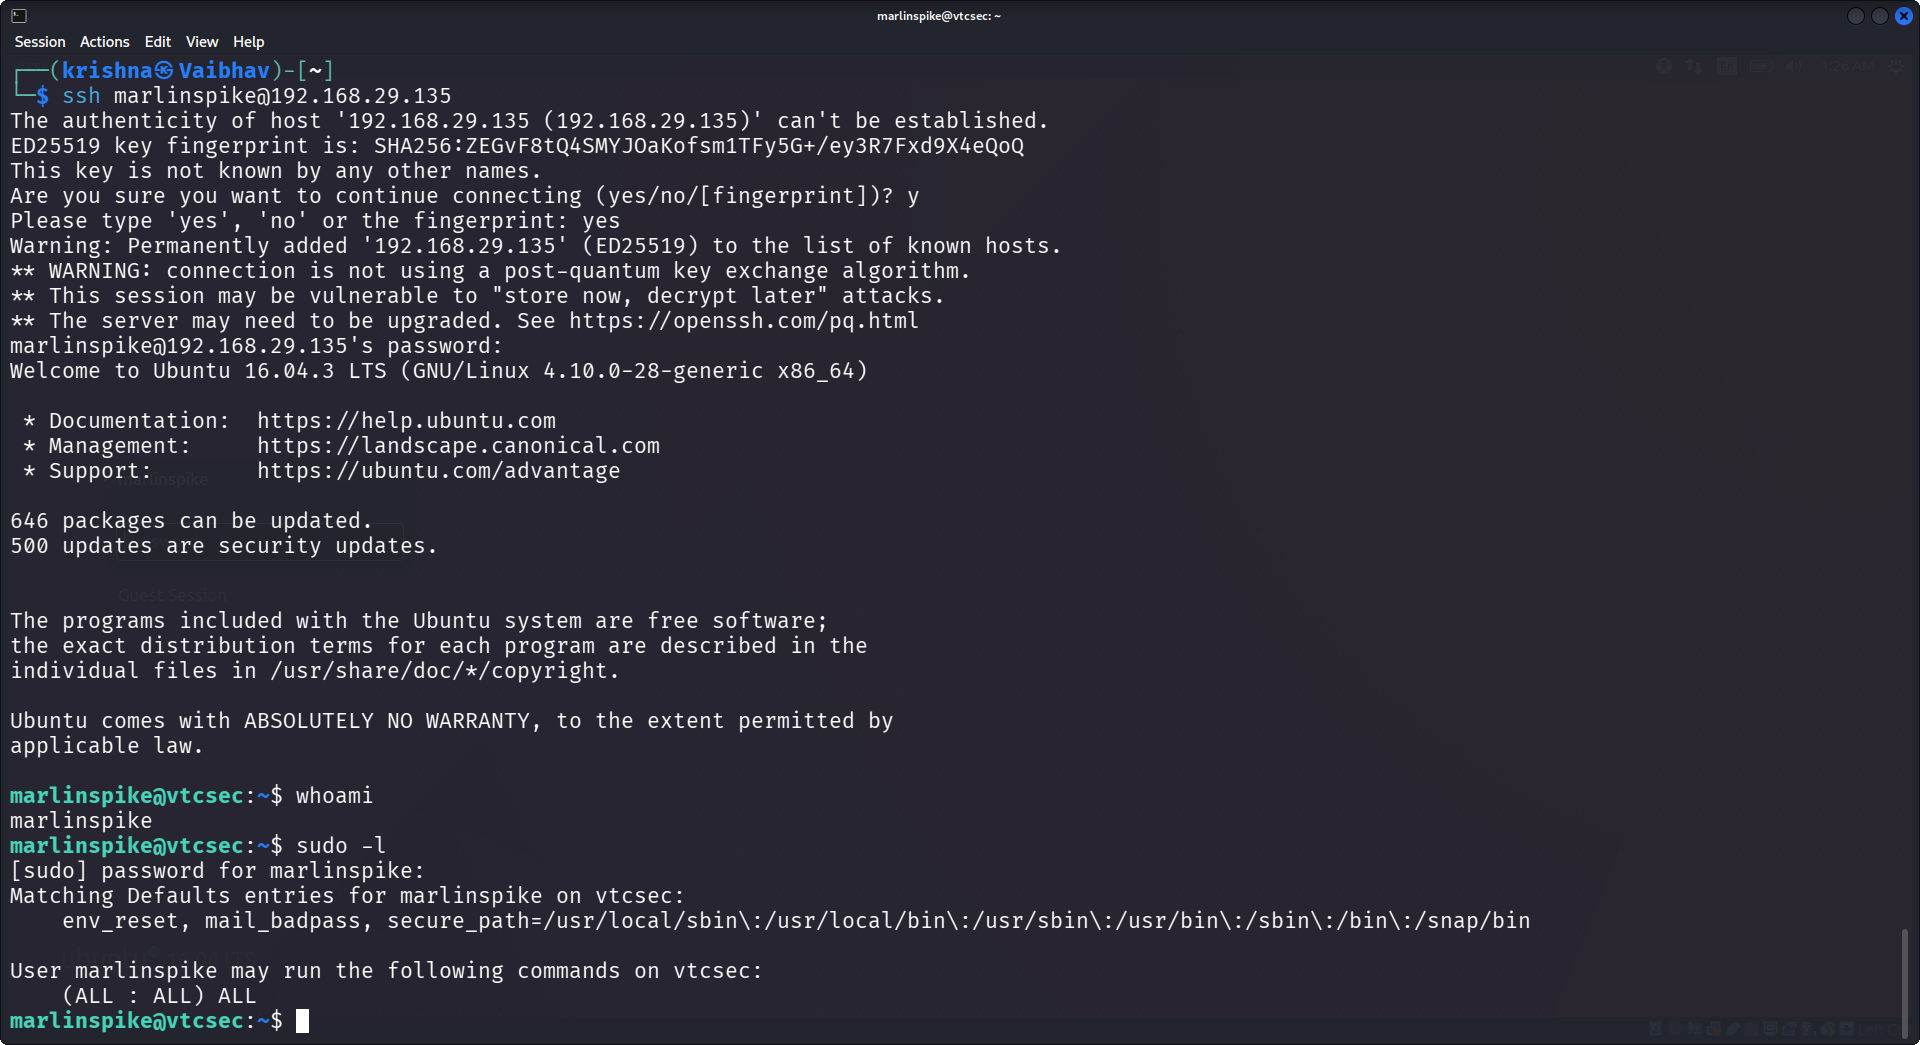 vaibhavkrishna12004/ubuntu-privesc-lab
Full penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)